
Netskope NSK300 Practice Exams
Last updated on Oct 22,2026- Exam Code: NSK300
- Exam Name: Netskope Certified Cloud Security Architect Exam
- Certification Provider: Netskope
- Latest update: Oct 22,2026
You do not want a scheduled Advanced Analytics dashboard to be automatically updated when Netskope makes improvements to that dashboard.
In this scenario, what would you do to retain the original dashboard?
- A . Create a new dashboard from scratch that mimics the Netskope dashboard you want to use.
- B . Copy the dashboard into your Group or Personal folders and schedule from these folders.
- C . Ask Netskope Support to provide the dashboard and import into your Personal folder.
- D . Download the dashboard you want and Import from File into your Group or Personal folder.
D
Explanation:
To retain the original dashboard without automatic updates due to improvements made by Netskope, you can download the desired dashboard and then import it from a file into your Group or Personal folder.
This approach ensures that you have a static version of the dashboard that won’t be affected by future changes or enhancements.
Reference: The answer is based on general knowledge of dashboard management and customization within Netskope.
What is the role of machine learning in Netskope Security Cloud?
- A . To predict future data usage patterns
- B . To automate the scaling of resources
- C . To detect anomalies and potential threats
- D . To facilitate user access management
What is the role of machine learning in Netskope Security Cloud?
- A . To predict future data usage patterns
- B . To automate the scaling of resources
- C . To detect anomalies and potential threats
- D . To facilitate user access management
You are attempting to merge two Advanced Analytics reports with DLP incidents: Report A with 3000 rows and Report B with 6000 rows. Once merged, you notice that the merged report is missing a significant number of rows.
What is causing this behavior?
- A . Netskope automatically deduplicates data in merged reports.
- B . Missing data is due to viewing limits.
- C . Filters are applied differently to dimensions and measures
- D . Visualizations have a system limit of 5000 rows.
B
Explanation:
When merging two Advanced Analytics reports in Netskope, if the merged report is missing rows, it is likely due to viewing limits within the system. Netskope’s Advanced Analytics platform has limitations on the number of rows that can be viewed at once, which can result in missing data when dealing with large reports. This viewing limit ensures performance and manageability of the data within the system.
Reference: The behavior of data viewing limits in Netskope Advanced Analytics is discussed in the Netskope Knowledge Portal, which provides insights into how data is explored and managed within the platform1
Your organization’s software deployment team did the initial install of the Netskope Client with SCCM. As the Netskope administrator, you will be responsible for all up-to-date upgrades of the client.
Which two actions would be required to accomplish this task9 (Choose two.)
- A . In the Client Configuration, set Upgrade Client Automatically to Latest Release.
- B . Set the installmode-IDP flag during the original Install.
- C . Set the autoupdate-on flag during the original Install.
- D . In the Client Configuration, set Upgrade Client Automatically to Specific Golden Release.
AC
Explanation:
To ensure that the Netskope Client is always up-to-date with the latest upgrades, two actions are required. First, in the Client Configuration, the administrator should set the option to Upgrade Client Automatically to Latest Release. This setting ensures that the client will automatically update to the most recent version available. Second, during the original installation of the Netskope Client, the autoupdate-on flag should be set. This flag enables the auto-update feature, allowing the client to receive and apply updates as they are released.
Reference: The information is based on the Netskope Client deployment options and upgrade process as detailed in the Netskope Knowledge Portal
You recently began deploying Netskope at your company. You are steering all traffic, but you discover that the Real-time Protection policies you created to protect Microsoft OneDrive are not being enforced.
Which default setting in the Ul would you change to solve this problem?
- A . Disable the default Microsoft appsuite SSL rule.
- B . Disable the default certificate-pinned application
- C . Remove the default steering exception for domains.
- D . Remove the default steering exception for Cloud Storage.
C
Explanation:
When deploying Netskope and steering all traffic, if you find that the Real-time Protection policies for Microsoft OneDrive are not being enforced, the likely issue is with the default steering exceptions. To resolve this, you should remove the default steering exception for domains ©. This is because the default exceptions may include domains related to Microsoft services, which could prevent the Real-time Protection policies from being applied to traffic directed towards OneDrive. By removing these exceptions, you ensure that all traffic, including that to OneDrive, is subject to the policies you have set up.
Reference: This recommendation is based on best practices for configuring Real-time Protection policies in Netskope, as outlined in their documentation, which suggests that exceptions should be carefully managed to ensure that security policies are enforced as intended
Given the following:
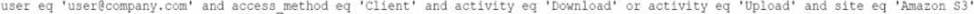
Which result does this Skope IT query provide?
- A . The query returns all events of [email protected] downloading or uploading to or from the site ‘Amazon S3" using the Netskope Client.
- B . The query returns all events of an IP address downloading or uploading to or from Amazon S3 using the Netskope Client.
- C . The query returns all events of everyone except [email protected] downloading or uploading to or from the site "Amazon S3" using the Netskope Client.
- D . The query returns all events of [email protected] downloading or uploading to or from the application "Amazon S3" using the Netskope Client.
A
Explanation:
The given Skope IT query specifies the following conditions:
User equals ‘[email protected]’
Access method equals ‘Client’
Activity equals ‘Download’ or ‘Upload’
Site equals ‘Amazon S3’
The query combines these conditions using logical operators (AND and OR).
The result of this query will include all events where the specified user (‘[email protected]’) is either downloading or uploading data to or from the site ‘Amazon S3’ using the Netskope Client. It does not include events related to other users or IP addresses.
Reference: Netskope Security Cloud Introductory Online Technical Training
Netskope Security Cloud Operation & Administration (NSCO&A) – Classroom Training
Review the exhibit.
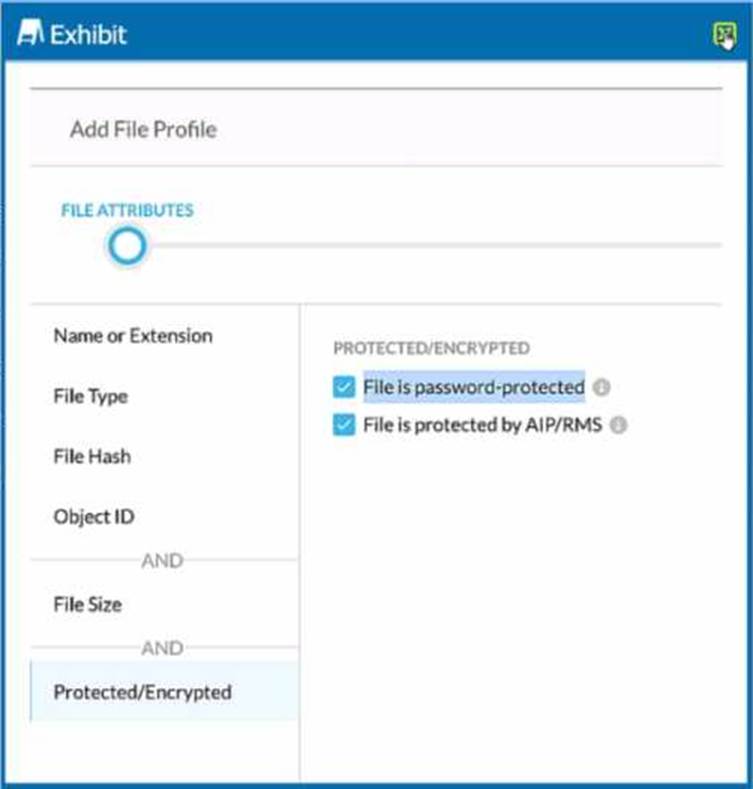
You are attempting to block uploads of password-protected files. You have created the file profile shown in the exhibit.
Where should you add this profile to use in a Real-time Protection policy?
- A . Add the profile to a DLP profile that is used in a Real-time Protection policy.
- B . Add the profile to a Malware Detection profile that is used in a Real-time Protection policy.
- C . Add the profile directly to a Real-time Protection policy as a Constraint.
- D . Add the profile to a Constraint profile that is used in a Real-time Protection policy.
A
Explanation:
In Netskope Cloud Security, to block uploads of password-protected files, you should add the file profile to a DLP (Data Loss Prevention) profile that is used in a Real-time Protection policy. The DLP profiles in Netskope are designed to detect and protect sensitive data in real-time and at rest across the cloud environment. This approach ensures that any file matching the criteria set in the file profile, such as being password-protected, will trigger the DLP rules and prevent the upload action in real-time.
Reference: The information aligns with the best practices for setting up DLP profiles in Netskope as described in their documentation and resources
You are consuming Audit Reports as part of a Salesforce API integration. Someone has made a change to a Salesforce account record field that should not have been made and you are asked to venfy the previous value of the structured data field. You have the approximate date and time of the change, user information, and the new field value.
How would you accomplish this task?
- A . Create a classic report and apply a query that filters on the changed field value.
- B . Use the Application Events Data Collection within Advanced Analytics and filter on the changed field value.
- C . Query Skope IT Page Events and look for the specific Page URL that was called under the Application section.
- D . Query Skope IT for an Access Method of API Connector and search Application Event Details for the Old Value field using the User details and Edit Activity.
D
Explanation:
To verify the previous value of a structured data field in Salesforce after an unauthorized change, you would use Skope IT with an Access Method of API Connector. This method allows you to search the Application Event Details for the ‘Old Value’ field. By filtering with the user details and the edit activity, you can pinpoint the exact change and retrieve the original value of the field.
Reference: The approach is consistent with the Netskope Cloud Security Architect’s guidelines for using API Data Protection with Salesforce. The documentation provides a detailed procedure for configuring Salesforce for API Data Protection, which includes the use of Netskope Audit Reports and the ability to track changes through the ‘Old Value’ field
A hospital has a patient form that they share with their patients over Gmail. The blank form can be freely shared among anyone. However, if the form has any information filled out. the document is considered confidential.
Which rule type should be used in the DLP profile to match such a document?
- A . Use fingerprint classification.
- B . Use a dictionary rule for all your patient names.
- C . Use Exact Match with patient names
- D . Use predefined DLP Rule(s) that match the patient name.
A
Explanation:
The appropriate rule type to use in the DLP profile for a document that is considered confidential when filled out is fingerprint classification. Fingerprinting is a method used to identify and protect sensitive data within documents. It works by creating a digital fingerprint of a file, which can then be used to detect any copies or derivatives of that file. In this case, fingerprinting would allow the hospital to differentiate between the blank patient form, which can be freely shared, and the same form with patient information filled out, which is confidential1.
Reference: Netskope’s DLP rules can contain elements such as predefined data identifiers, custom data identifiers, keyword identifiers from a dictionary file, RegEx expressions, and exact match criteria1. For this specific use case, fingerprint classification is the most effective method as it can accurately detect the presence of filled-out information in the forms, which is crucial for maintaining patient confidentiality as per HIPAA regulations1.