Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
DRAG DROP
You have a Microsoft Sentinel workspace named SW1.
In SW1. you enable User and Entity Behavior Analytics (UEBA).
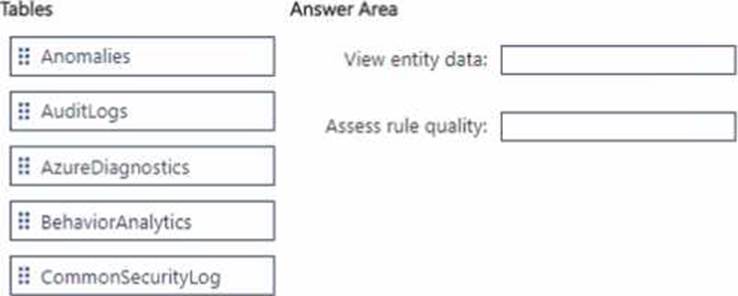
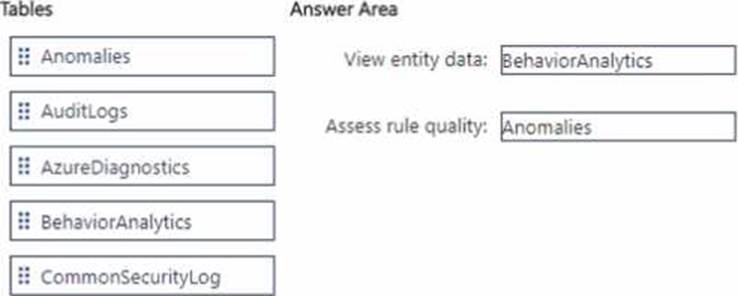
You need to use KQL to perform the following tasks:
• View the entity data that has fields for each type of entity.
• Assess the quality of rules by analyzing how well a rule performs.
Which table should you use in KQL for each task? To answer, drag the appropriate tables to the correct tasks. Each table may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.
You need to modify the anomaly detection policy settings to meet the Cloud App Security requirements.
Which policy should you modify?
- A . Activity from suspicious IP addresses
- B . Activity from anonymous IP addresses
- C . Impossible travel
- D . Risky sign-in
You are investigating a potential attack that deploys a new ransomware strain.
You plan to perform automated actions on a group of highly valuable machines that contain sensitive information.
You have three custom device groups.
You need to be able to temporarily group the machines to perform actions on the devices.
Which three actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . Add a tag to the device group.
- B . Add the device users to the admin role.
- C . Add a tag to the machines.
- D . Create a new device group that has a rank of 1.
- E . Create a new admin role.
- F . Create a new device group that has a rank of 4.
You provision Azure Sentinel for a new Azure subscription. You are configuring the Security Events connector.
While creating a new rule from a template in the connector, you decide to generate a new alert for every event. You create the following rule query.
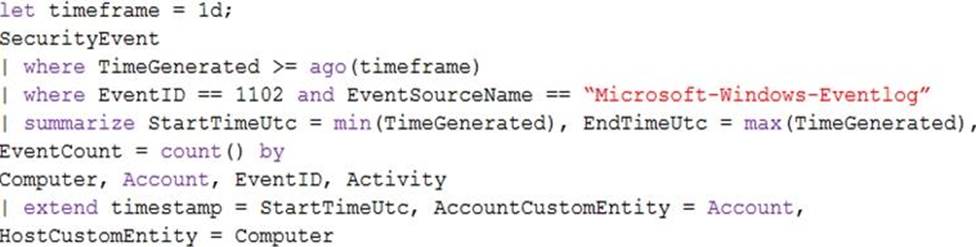
By which two components can you group alerts into incidents? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A . user
- B . resource group
- C . IP address
- D . computer
You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR.
The security team at your company detects command and control (C2) agent traffic on the network.
Agents communicate once every 50 hours.
You need to create a Microsoft Defender XDR custom detection rule that will identify compromised devices and establish a pattern of communication.
The solution must meet the following requirements:
• Identify all the devices that have communicated during the past 14 days.
• Minimize how long it takes to identify the devices.
To what should you set the detection frequency for the rule?
- A . Every three hours
- B . Every 24 hours
- C . Every hour
- D . Every 12 hours
You need to minimize the effort required to investigate the Microsoft Defender for Identity false positive alerts.
What should you review?
- A . the status update time
- B . the alert status
- C . the certainty of the source computer
- D . the resolution method of the source computer
HOTSPOT
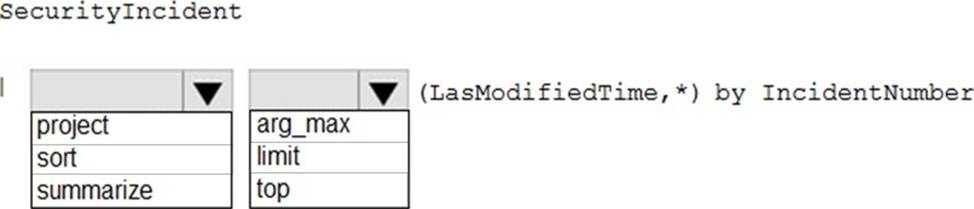
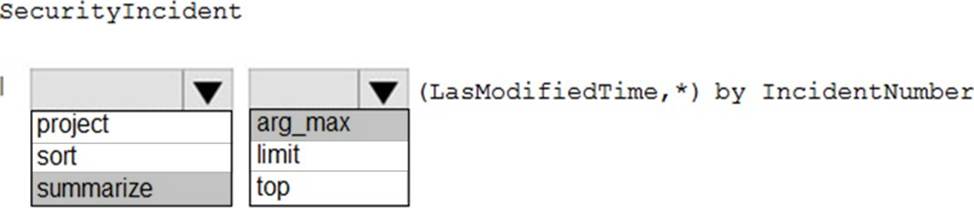
You need to create a query for a workbook.
The query must meet the following requirements:
✑ List all incidents by incident number.
✑ Only include the most recent log for each incident.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
You have a Microsoft Sentinel workspace that has a default data retention period of 30 days.
The workspace contains two custom tables as shown in the following table.
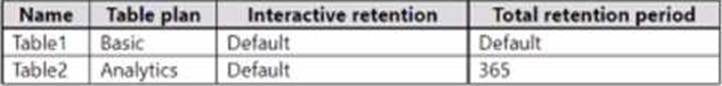
Each table ingested two records per day during the past 365 days.
You build KQL statements for use in analytic rules as shown in the following table.
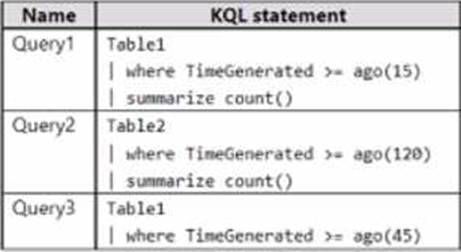
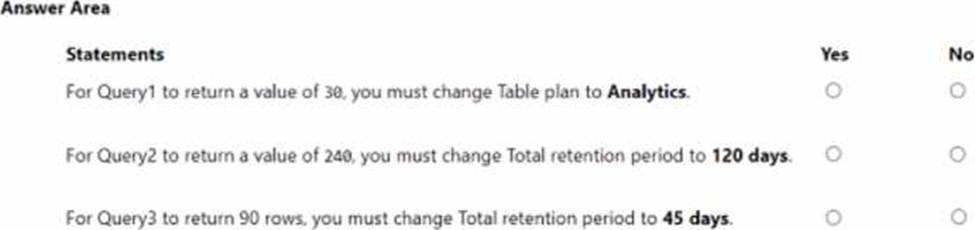
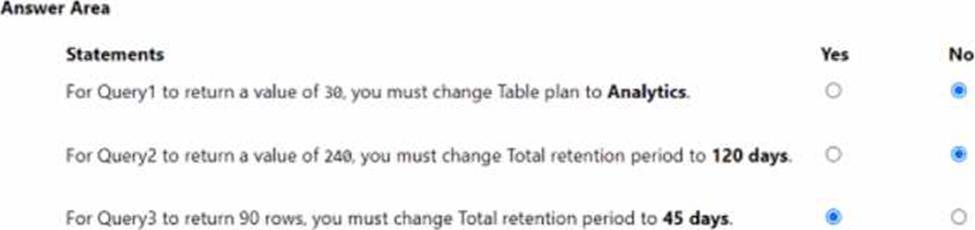
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
DRAG DROP
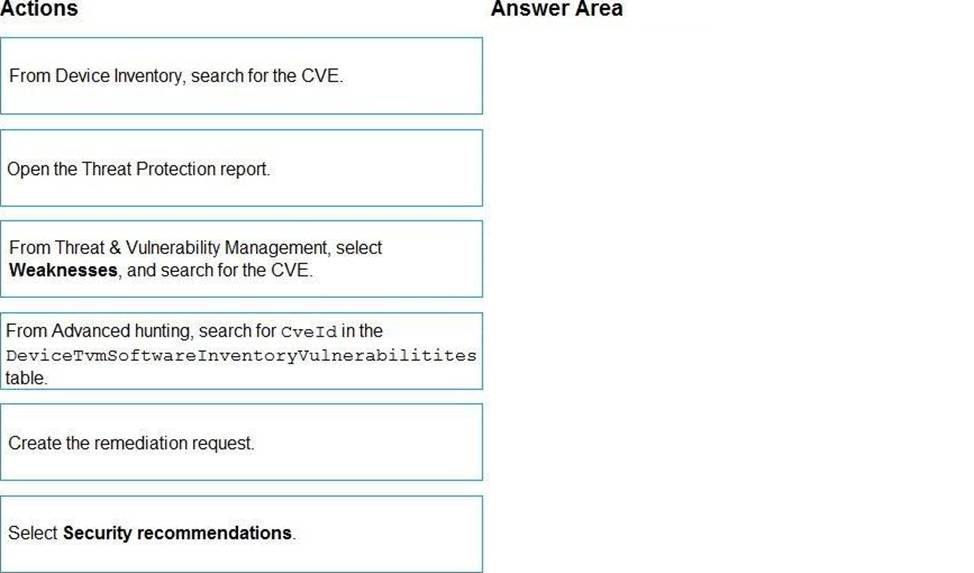
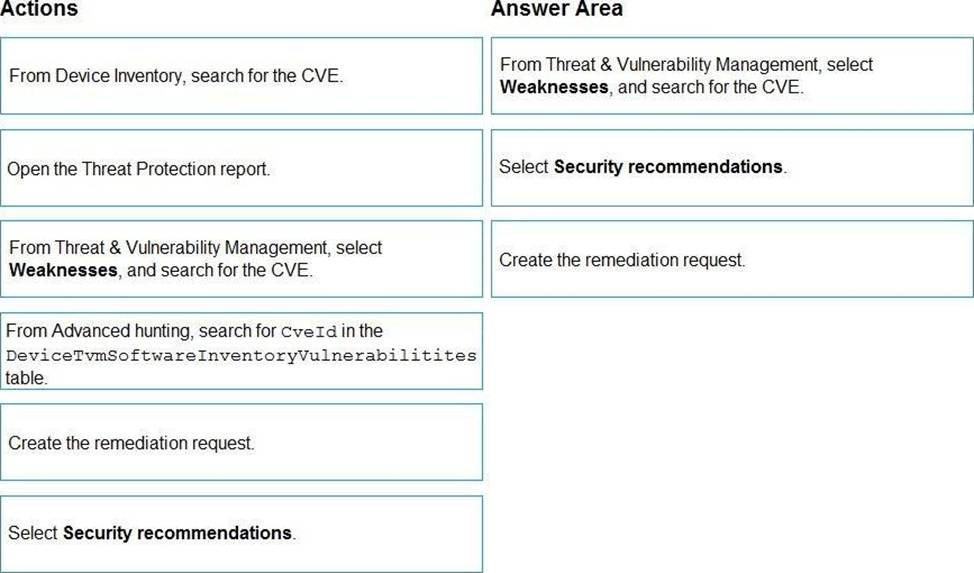
You are informed of a new common vulnerabilities and exposures (CVE) vulnerability that affects your environment.
You need to use Microsoft Defender Security Center to request remediation from the team responsible for the affected systems if there is a documented active exploit available.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
HOTSPOT
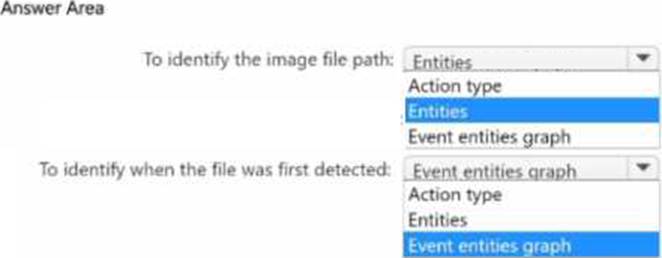
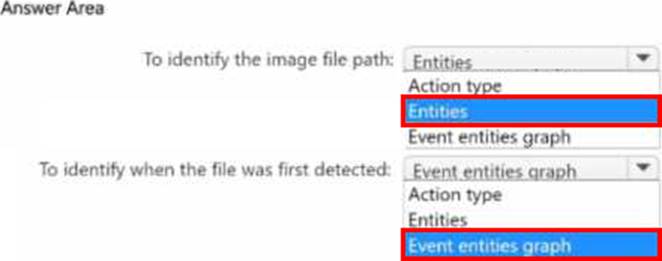
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint and contains a Windows device named Device1. You need to investigate a suspicious executable file detected on Device1.
The solution must meet the following requirements:
• Identify the image file path of the file.
• Identify when the file was first detected on Device1.
What should you review from the timeline of the detection event? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.