Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
HOTSPOT
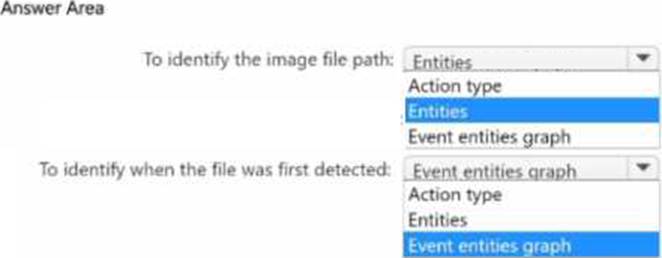
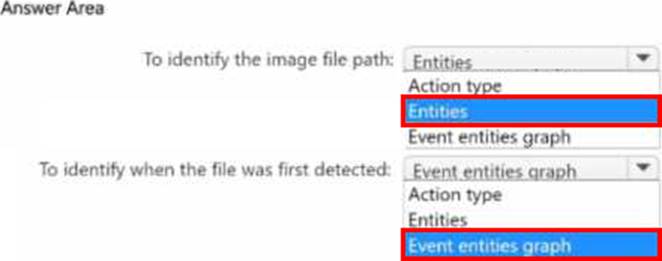
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint and contains a Windows device named Device1. You need to investigate a suspicious executable file detected on Device1.
The solution must meet the following requirements:
• Identify the image file path of the file.
• Identify when the file was first detected on Device1.
What should you review from the timeline of the detection event? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a playbook in Azure Sentinel.
When you trigger the playbook, it sends an email to a distribution group.
You need to modify the playbook to send the email to the owner of the resource instead of the distribution group.
What should you do?
- A . Add a parameter and modify the trigger.
- B . Add a custom data connector and modify the trigger.
- C . Add a condition and modify the action.
- D . Add a parameter and modify the action.
HOTSPOT
You have an Azure subscription named Sub1 and an Azure DevOps organization named AzDO1.
AzDO1 uses Defender for Cloud and contains a project that has a YAML pipeline named Pipeline1.
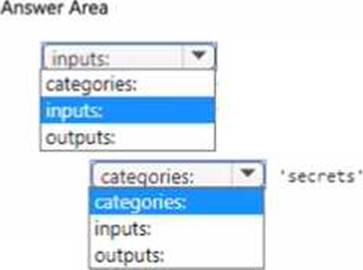
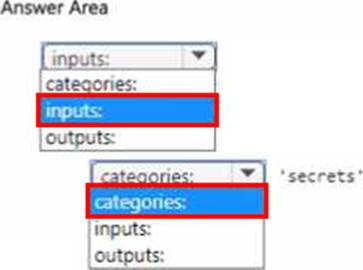
Pipeline1 outputs the details of discovered open source software vulnerabilities to Defender for Cloud.
You need to configure Pipeline1 to output the results of secret scanning to Defender for Cloud.
What should you add to Pipeline1? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint.
You need to add threat indicators for all the IP addresses in a range of 171.23.3432-171.2334.63. The solution must minimize administrative effort.
What should you do in the Microsoft 365 Defender portal?
- A . Create an import file that contains the IP address of 171.23.34.32/27. Select Import and import the file.
- B . Select Add indicator and set the IP address to 171.2334.32-171.23.34.63.
- C . Select Add indicator and set the IP address to 171.23.34.32/27
- D . Create an import file that contains the individual IP addresses in the range. Select Import and
import the file.
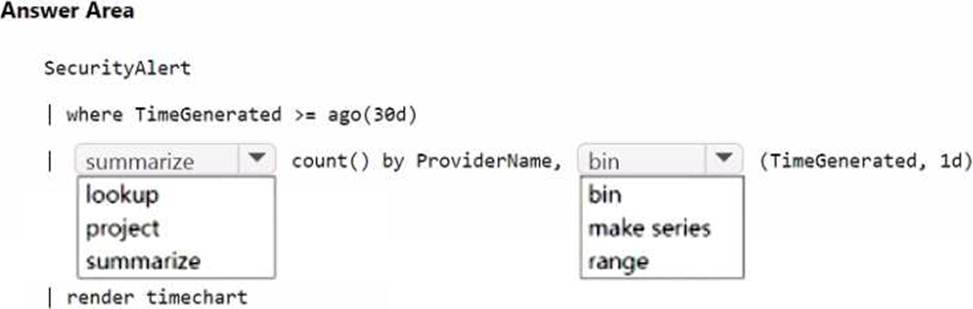
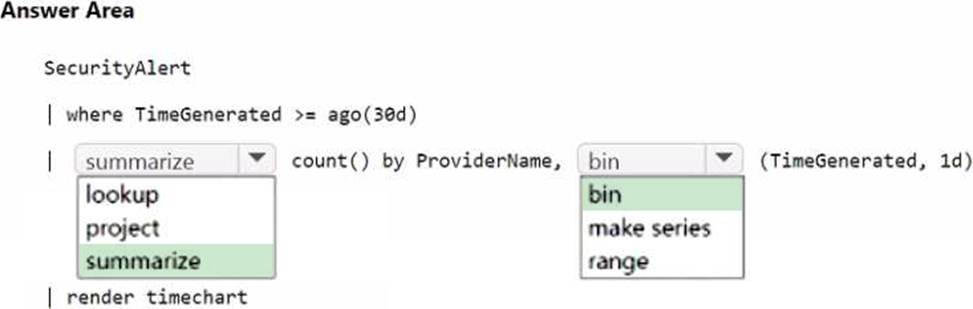
HOTSPOT
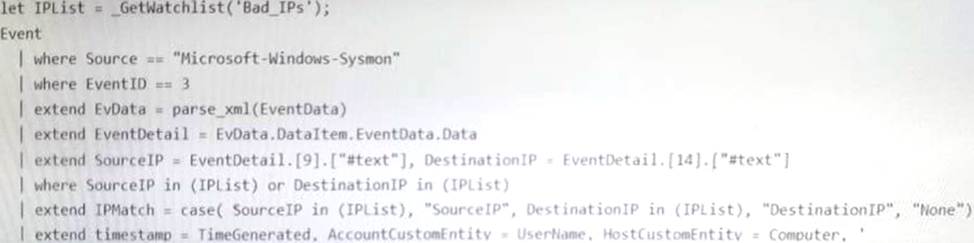
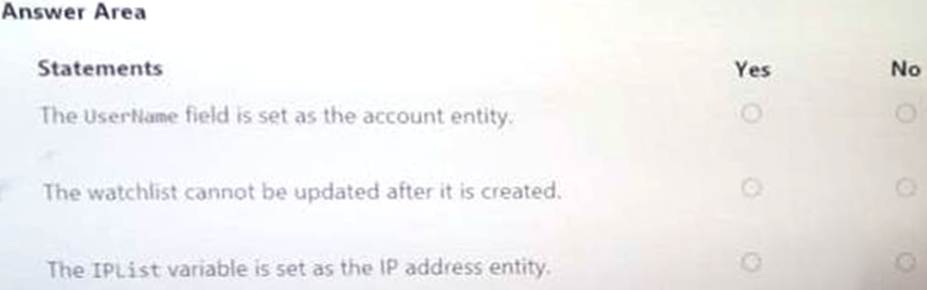
You have a Microsoft Sentinel workspace that contains a custom workbook.
You need to query the number of daily security alerts.
The solution must meet the following requirements:
• Identify alerts that occurred during the last 30 days.
• Display the results in a timechart.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You need to correlate data from the SecurityEvent Log Anarytks table to meet the Microsoft Sentinel
requirements for using UEBA.
Which Log Analytics table should you use?
- A . SentwlAuoNt
- B . AADRiskyUsers
- C . IdentityOirectoryEvents
- D . Identityinfo
Your company uses Microsoft Sentinel
A new security analyst reports that she cannot assign and resolve incidents in Microsoft Sentinel.
You need to ensure that the analyst can assign and resolve incidents. The solution must use the principle of least privilege.
Which role should you assign to the analyst?
- A . Microsoft Sentinel Responder
- B . Logic App Contributor
- C . Microsoft Sentinel Reader
- D . Microsoft Sentinel Contributor
You have a Microsoft Sentinel workspace named workspace1 that contains custom Kusto queries.
You need to create a Python-based Jupyter notebook that will create visuals. The visuals will display the results of the queries and be pinned to a dashboard. The solution must minimize development effort.
What should you use to create the visuals?
- A . plotly
- B . TensorFlow
- C . msticpy
- D . matplotlib
HOTSPOT
You have a Microsoft 365 E5 subscription that uses Microsoft 365 Defender for Endpoint.
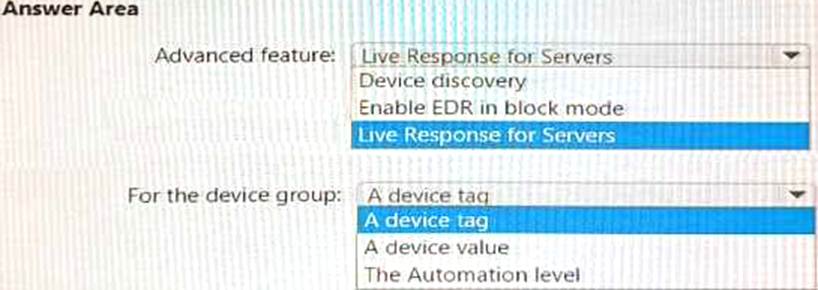
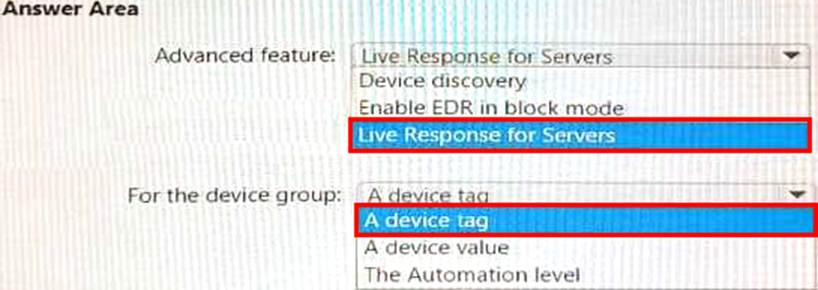
You need to ensure that you can initiate remote shell connections to Windows servers by using the Microsoft 365 Defender portal.
What should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.