Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
You have an Azure subscription that contains a Microsoft Sentinel workspace. The workspace contains a Microsoft Defender for Cloud data connector. You need to customize which details will be included when an alert is created for a specific event.
What should you do?
- A . Modify the properties of the connector.
- B . Create a Data Collection Rule (DCR).
- C . Create a scheduled query rule.
- D . Enable User and Entity Behavior Analytics (UEBA)
Your company deploys the following services:
✑ Microsoft Defender for Identity
✑ Microsoft Defender for Endpoint
✑ Microsoft Defender for Office 365
You need to provide a security analyst with the ability to use the Microsoft 365 security center. The analyst must be able to approve and reject pending actions generated by Microsoft Defender for Endpoint. The solution must use the principle of least privilege.
Which two roles should assign to the analyst? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . the Compliance Data Administrator in Azure Active Directory (Azure AD)
- B . the Active remediation actions role in Microsoft Defender for Endpoint
- C . the Security Administrator role in Azure Active Directory (Azure AD)
- D . the Security Reader role in Azure Active Directory (Azure AD)
You have a Microsoft 365 subscription.
You have 1,000 Windows devices that have a third-party antivirus product installed and Microsoft Defender Antivirus in passive mode.
You need to ensure that the devices are protected from malicious artifacts that were undetected by the third -party antivirus product.
Solution: You configure endpoint detection and response (EDR) in block mode.
Does this meet the goal?
- A . Yes
- B . No
You have an Azure subscription that contains a Microsoft Sentinel workspace named WS1.
You create a hunting query that detects a new attack vector. The attack vector maps to a tactic listed in the MITRE ATT&CK database.
You need to ensure that an incident is created in WS1 when the new attack vector is detected.
What should you configure?
- A . a Fusion rule
- B . a query bookmark
- C . a scheduled query rule
- D . a hunting livestream session
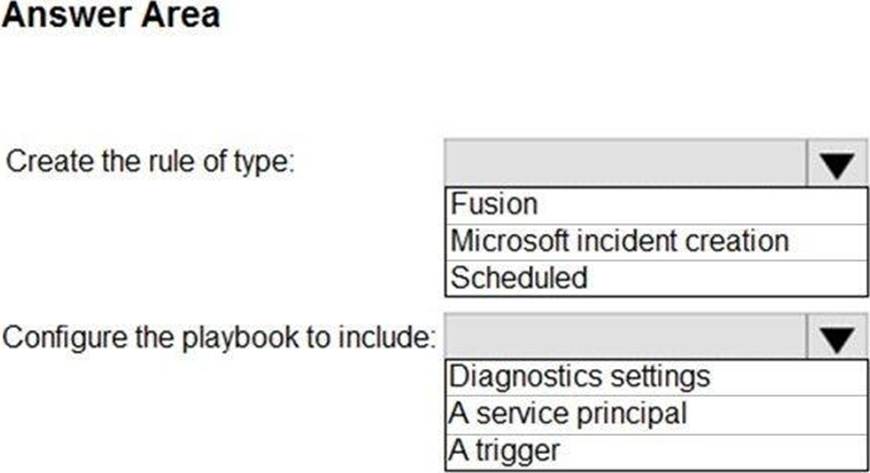
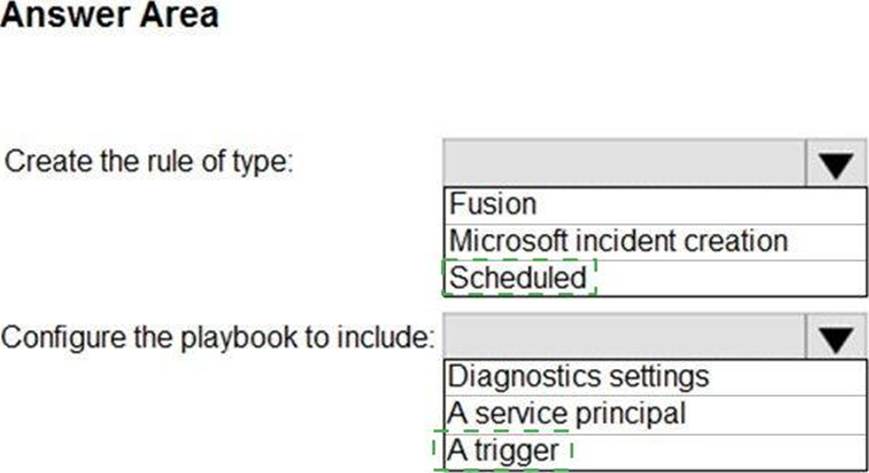
HOTSPOT
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an on-premises network.
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Identity.
From the Microsoft Defender portal, you investigate an incident on a device named Device1 of a user named User1. The incident contains the following Defender for Identity alert.
Suspected identity theft (pass-the-ticket) (external ID 2018)
You need to contain the incident without affecting users and devices. The solution must minimize administrative effort.
What should you do?
- A . Disable User 1 only.
- B . Quarantine Device1 only.
- C . Reset the password for all the accounts that previously signed in to Device1.
- D . DisableUser1 and quarantine Device1.
- E . Disable User1, quarantine Device1, and reset the password for all the accounts that previously signed in to Device1.
You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You need to configure the continuous export of high-severity alerts to enable their retrieval from a third-party security information and event management (SIEM) solution.
To which service should you export the alerts?
- A . Azure Cosmos DB
- B . Azure Event Grid
- C . Azure Event Hubs
- D . Azure Data Lake
You need to restrict cloud apps running on CUENT1 to meet the Microsoft Defender for Endpoint requirements.
Which two configurations should you modify? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . the Cloud Discovery settings in Microsoft Defender for Cloud Apps
- B . the Onboarding settings from Device management in Settings in Microsoft 365 Defender portal
- C . Microsoft Defender for Cloud Apps anomaly detection policies
- D . Advanced features from the Endpoints Settings in the Microsoft 365 Defender portal
HOTSPOT
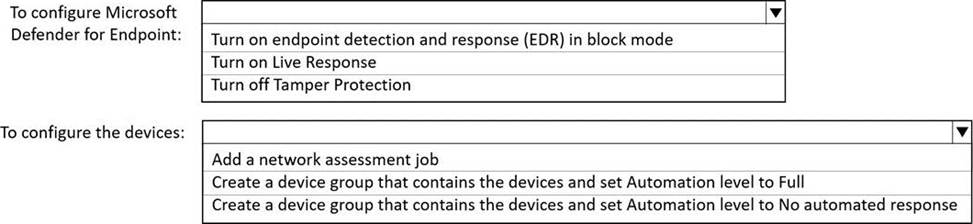
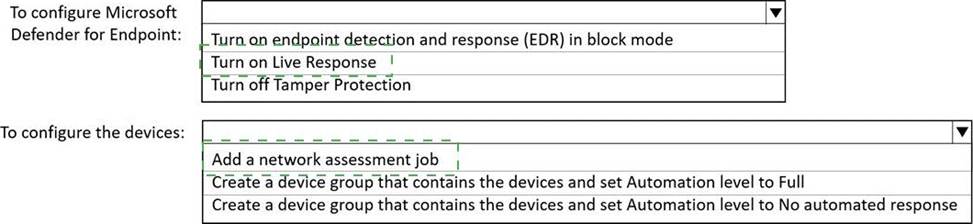
You have a Microsoft 365 E5 subscription that contains 200 Windows 10 devices enrolled in Microsoft Defender for Endpoint.
You need to ensure that users can access the devices by using a remote shell connection directly from the Microsoft 365 Defender portal. The solution must use the principle of least privilege.
What should you do in the Microsoft 365 Defender portal? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
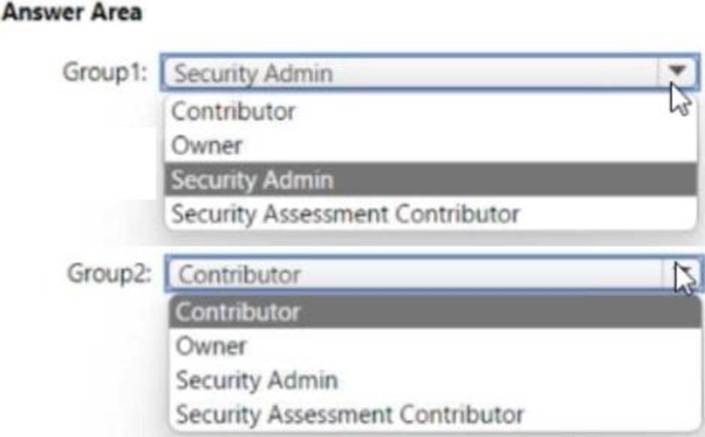
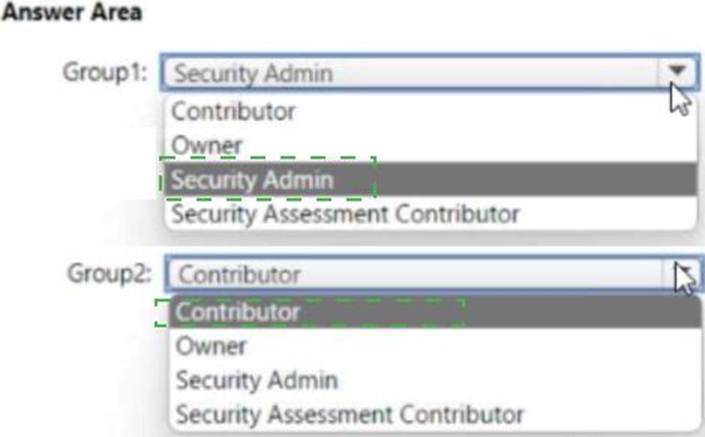
You need to assign role-based access control (RBAQ roles to Group1 and Group2 to meet. The Microsoft Defender for Cloud requirements and the business requirements.
Which role should you assign to each group? To answer, select the appropriate options in the answer area NOTE Each
correct selection is worth one point.