Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have Linux virtual machines on Amazon Web Services (AWS).
You deploy Azure Defender and enable auto-provisioning.
You need to monitor the virtual machines by using Azure Defender.
Solution: You enable Azure Arc and onboard the virtual machines to Azure Arc.
Does this meet the goal?
- A . Yes
- B . No
HOTSPOT
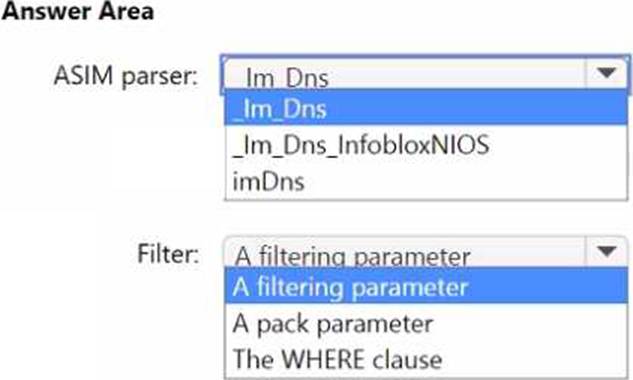
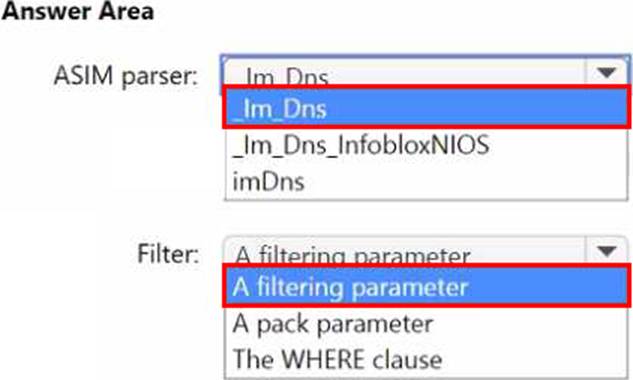
You need to implement the ASIM query for DNS requests. The solution must meet the Microsoft Sentinel requirements.
How should you configure the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You create a custom analytics rule to detect threats in Azure Sentinel.
You discover that the rule fails intermittently.
What are two possible causes of the failures? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . The rule query takes too long to run and times out.
- B . The target workspace was deleted.
- C . Permissions to the data sources of the rule query were modified.
- D . There are connectivity issues between the data sources and Log Analytics
You plan to create a custom Azure Sentinel query that will provide a visual representation of the security alerts generated by Azure Security Center.
You need to create a query that will be used to display a bar graph.
What should you include in the query?
- A . extend
- B . bin
- C . count
- D . workspace
You have a custom Microsoft Sentinel workbook named Workbooks.
You need to add a grid to Workbook1. The solution must ensure that the grid contains a maximum of 100 rows.
What should you do?
- A . In the query editor interface, configure Settings.
- B . In the query editor interface, select Advanced Editor
- C . In the grid query, include the project operator.
- D . In the grid query, include the take operator.
You have an Azure subscription that uses Microsoft Defender for Cloud and contains a resource group named RG1. RG1. You need to configure just in time (JIT) VM access for the virtual machines in RG1.
The solution must meet the following
• Limit the maximum request time to two hours.
• Limit protocol access to Remote Desktop Protocol (RDP) only.
• Minimize administrative effort.
What should you use?
- A . Azure AD Privileged Identity Management (PIM)
- B . Azure Policy
- C . Azure Front Door
- D . Azure Bastion
HOTSPOT
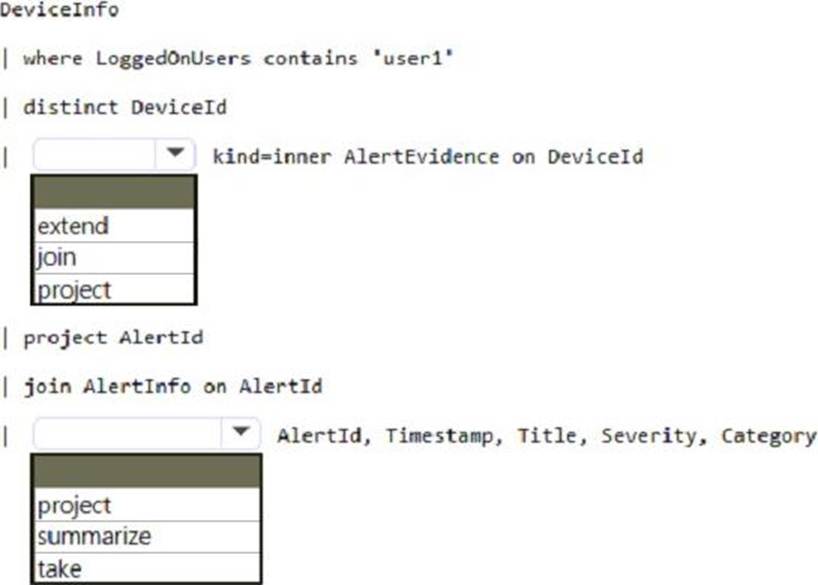
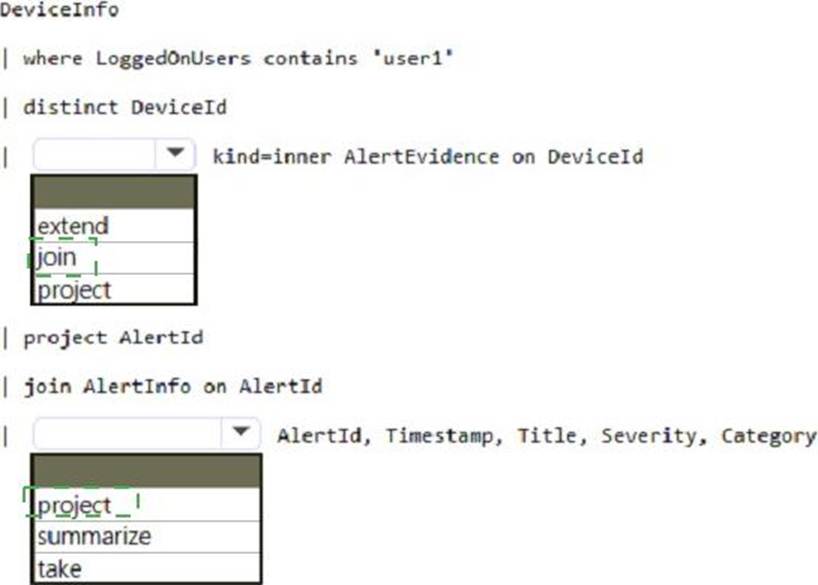
You have a Microsoft 365 subscription that uses Microsoft 365 Defender and contains a user named User1.
You are notified that the account of User1 is compromised.
You need to review the alerts triggered on the devices to which User1 signed in.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users.
The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel.
What should you do first?
- A . And a new scheduled query rule.
- B . Add a data connector to Azure Sentinel.
- C . Configure a custom Threat Intelligence connector in Azure Sentinel.
- D . Modify the trigger in the logic app.
HOTSPOT
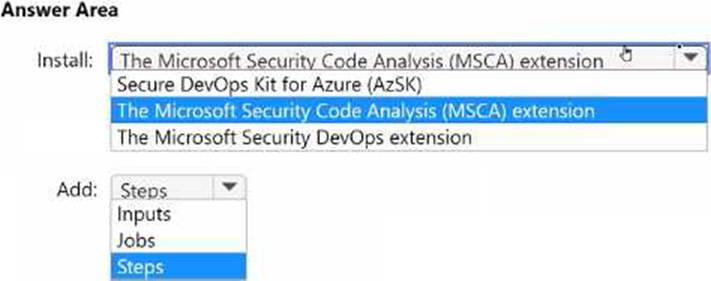
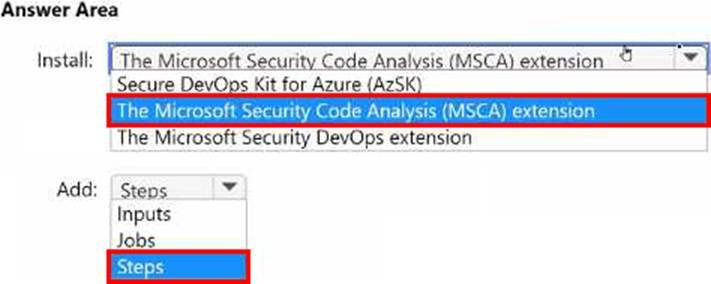
You have an Azure DevOps organization that uses Microsoft Defender for DevOps. The organization contains an Azure DevOps repository named Repo1 and an Azure Pipelines pipeline named Pipeline1. Pipeline1 is used to build and deploy code stored in Repo1.
You need to ensure that when Pipeline1 runs, Microsoft Defender for Cloud can perform secret scanning of the code in Repo1.
What should you install in the organization, and what should you add to the YAML file of Pipeline"!? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
DRAG DROP
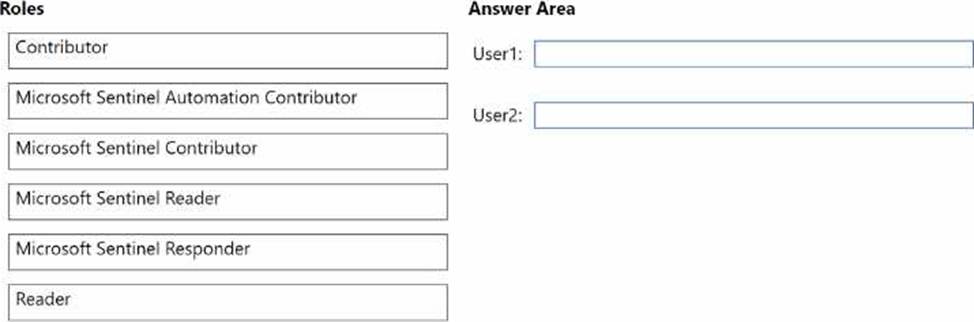
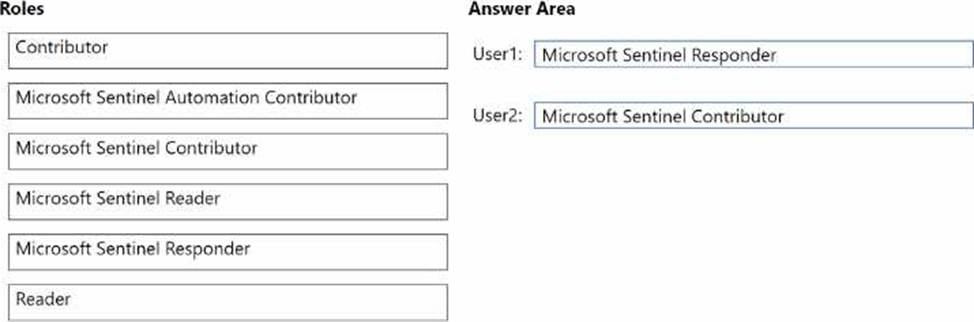
You have an Azure subscription that contains two users named User1 and User2 and a Microsoft Sentinel workspace named workspace1.
You need to ensure that the users can perform the following tasks in workspace1:
• User1 must be able to dismiss incidents and assign incidents to users.
• User2 must be able to modify analytics rules.
The solution must use the principle of least privilege.
Which role should you assign to each user? To answer, drag the appropriate roles to the correct users. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point.