
Microsoft SC-200 Practice Exams
Last updated on Oct 21,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 21,2026
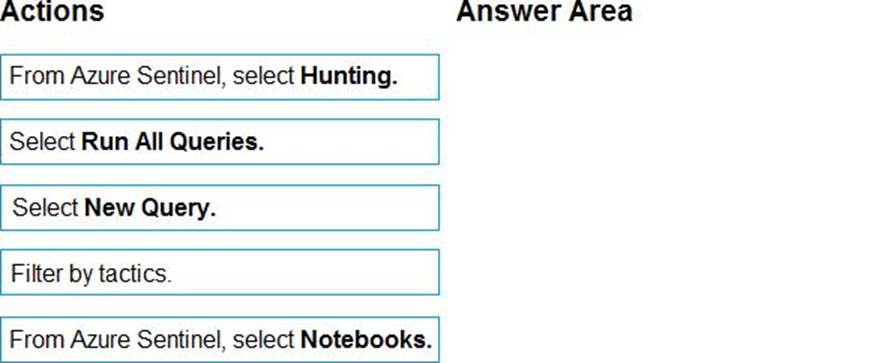
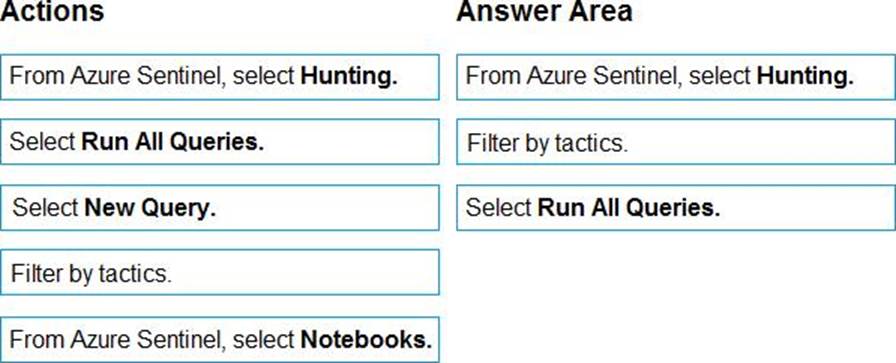
DRAG DROP
You have an Azure Sentinel deployment.
You need to query for all suspicious credential access activities.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
HOTSPOT
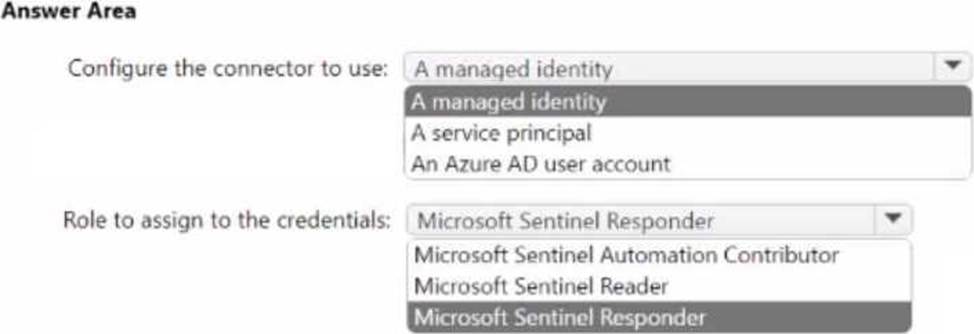
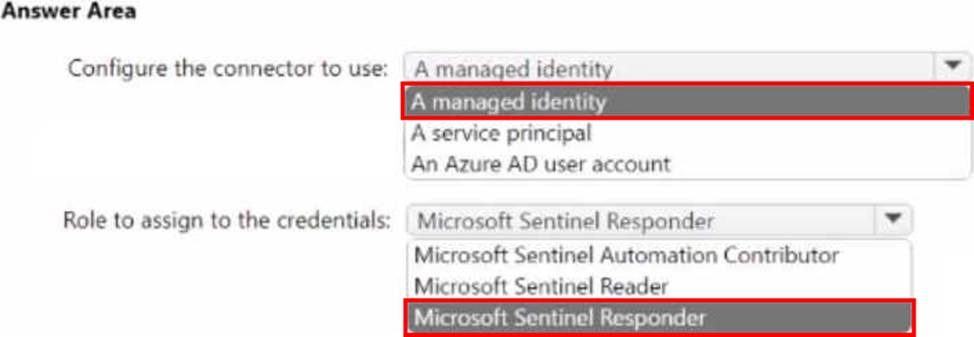
You have a Microsoft Sentinel workspace named sws1.
You plan to create an Azure logic app that will raise an incident in an on-premises IT service management system when an incident is generated in sws1.
You need to configure the Microsoft Sentinel connector credentials for the logic app.
The solution must meet the following requirements:
• Minimize administrative effort.
• Use the principle of least privilege.
How should you configure the credentials? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
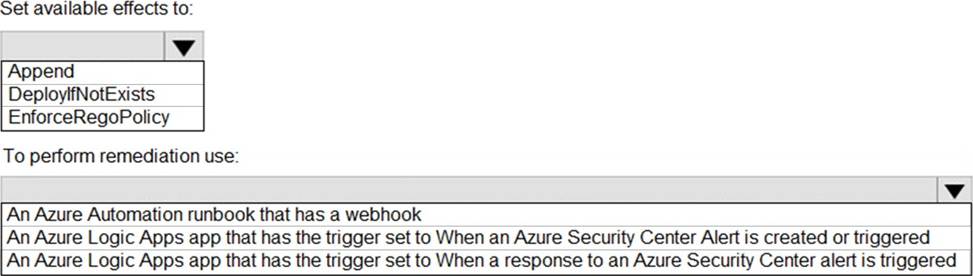
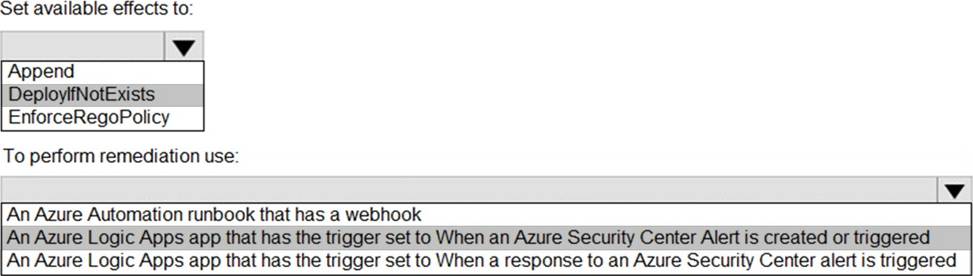
You have an Azure subscription that uses Azure Defender.
You plan to use Azure Security Center workflow automation to respond to Azure Defender threat alerts.
You need to create an Azure policy that will perform threat remediation automatically.
What should you include in the solution? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains a user named User1.
User1 is assigned an Azure Active Directory Premium Plan 2 license
You need to identify whether the identity of User1 was compromised during the last 90 days.
What should you use?
- A . the risk detections report
- B . the risky users report
- C . Identity Secure Score recommendations
- D . the risky sign-ins report
You have a Microsoft Sentinel workspace.
You need to prevent a built-in Advance Security information Model (ASIM) parse from being updated automatically.
What are two ways to achieve this goal? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A . Redeploy the built-in parse and specify a CallerContext parameter of any and a SourceSpecificParse parameter of any.
- B . Create a hunting query that references the built-in parse.
- C . Redeploy the built-in parse and specify a CallerContext parameter of built-in.
- D . Build a custom unify parse and include the build- parse version
- E . Create an analytics rule that includes the built-in parse
DRAG DROP
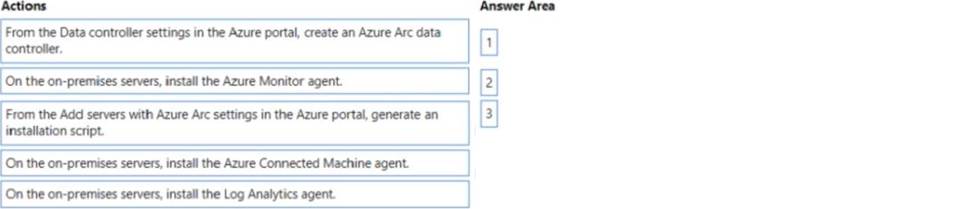
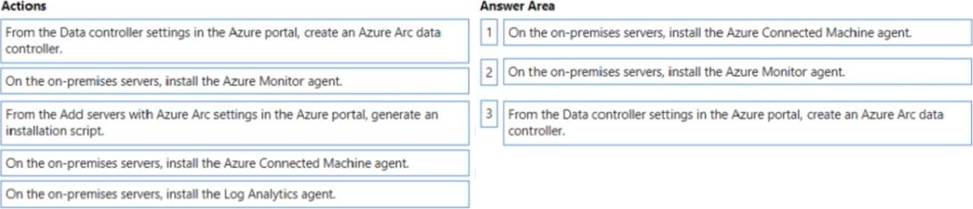
You have 50 on-premises servers.
You have an Azure subscription that uses Microsoft Defender for Cloud. The Defender for Cloud deployment has Microsoft Defender for Servers and automatic provisioning enabled.
You need to configure Defender for Cloud to support the on-premises servers.
The solution must meet the following requirements:
• Provide threat and vulnerability management.
• Support data collection rules.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
You have a Microsoft Sentinel workspace named SW1.
In SW1, you investigate an incident that is associated with the following entities:
• Host
• IP address
• User account
• Malware name
Which entity can be labeled as an indicator of compromise (loC) directly from the incident s page?
- A . malware name
- B . host
- C . user account
- D . IP address
HOTSPOT
You have a Microsoft 365 E5 subscription.
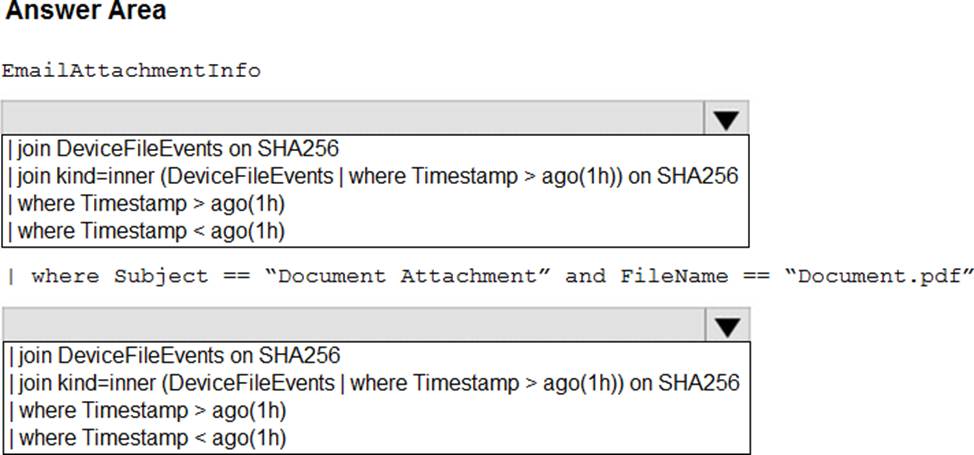
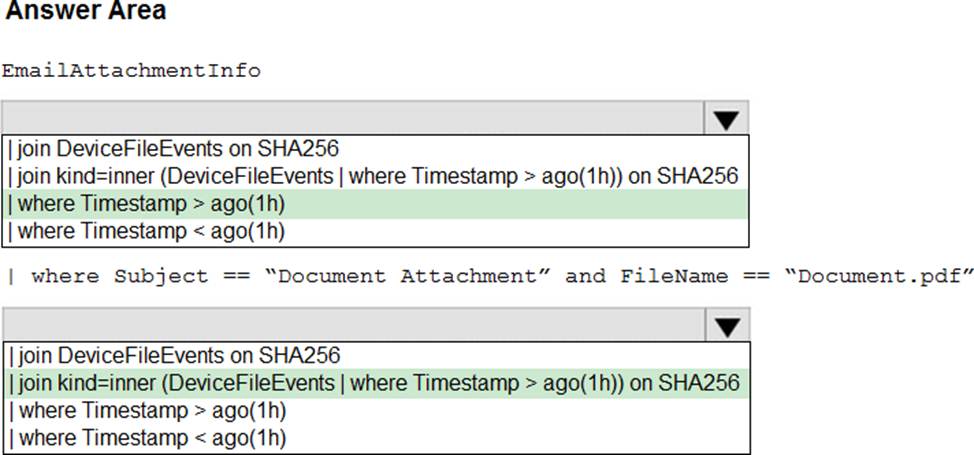
You need to create a hunting query that will return every email that contains an attachment named Document.pdf.
The query must meet the following requirements:
• Only show emails sent during the last hour.
• Optimize query performance.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
You have a Microsoft 365 E5 subscription.
You need to create a hunting query that will return every email that contains an attachment named Document.pdf.
The query must meet the following requirements:
• Only show emails sent during the last hour.
• Optimize query performance.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that uses Microsoft Defender for Office 365.
You have Microsoft SharePoint Online sites that contain sensitive documents. The documents contain customer account numbers that each consists of 32 alphanumeric characters.
You need to create a data loss prevention (DLP) policy to protect the sensitive documents.
What should you use to detect which documents are sensitive?
- A . SharePoint search
- B . a hunting query in Microsoft 365 Defender
- C . Azure Information Protection
- D . RegEx pattern matching