Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
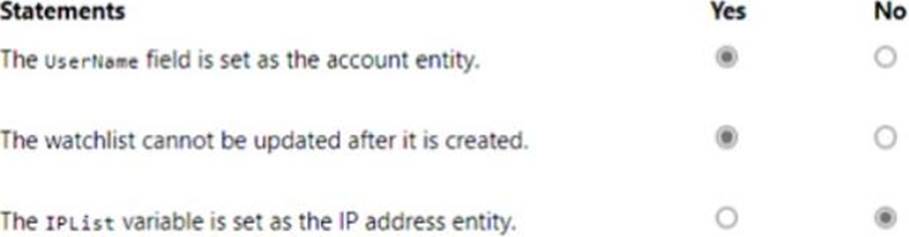
Topic 3, Adatum Corporation
Overview
Adatum Corporation is a United States-based financial services company that has regional offices in New York, Chicago, and San Francisco.
The on-premises network contains an Active Directory Domain Services (AD DS) forest named corp.adatum.com that syncs with an Azure AD tenant named adatum.com. All user and group management tasks are performed in corp.adatum.com. The corp.adatum.com domain contains a group named Group! that syncs with adatum.com.
All the users at Adatum are assigned a Microsoft 365 E5 license and an Azure Active Directory Perineum 92 license.
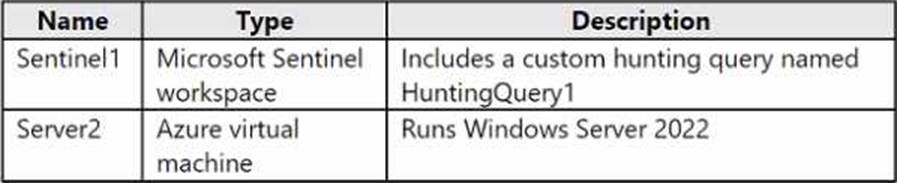
The cloud environment contains a Microsoft 365 subscription, an Azure subscription linked to the adatum.com tenant, and the resources shown in the following table.
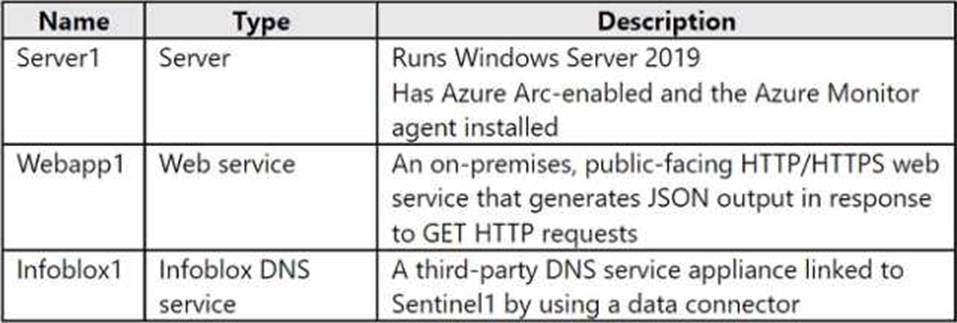
The on-premises network contains the resources shown in the following table.
Adatum plans to perform the following changes;
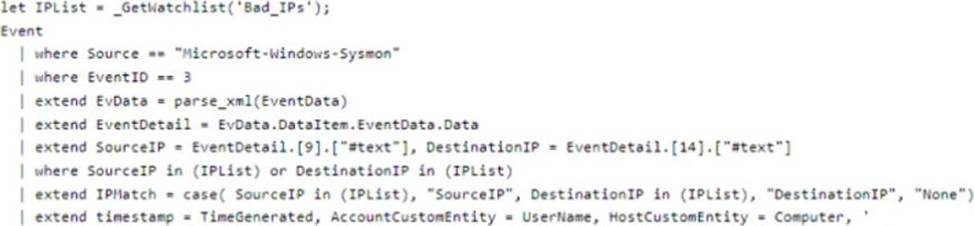
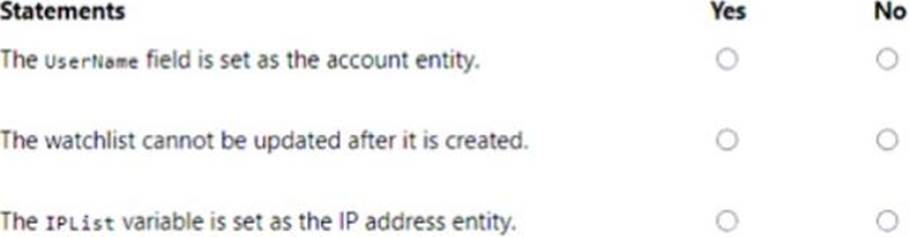
• Implement a query named rulequery1 that will include the following KQL query.
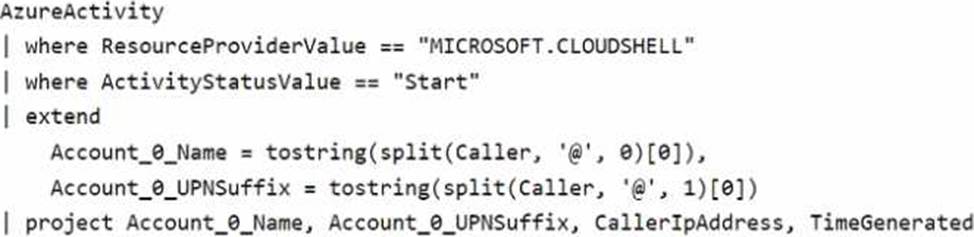
• Implement a Microsoft Sentinel scheduled rule that generates incidents based on rulequery1. Adatum identifies the following Microsoft Defender for Cloud requirements:
• The members of Group1 must be able to enable Defender for Cloud plans and apply regulatory compliance initiatives.
• Microsoft Defender for Servers Plan 2 must be enabled on all the Azure virtual machines.
• Server2 must be excluded from agentless scanning.
Adatum identifies the following Microsoft Sentinel requirements:
• Implement an Advanced Security Information Model (ASIM) query that will return a count of DNS requests that results in an NXDOMAIN response from Infoblox1.
• Ensure that multiple alerts generated by rulequery1 in response to a single user launching Azure Cloud Shell multiple times are consolidated as a single incident.
• Implement the Windows Security Events via AMA connector for Microsoft Sentinel and configure it to monitor the Security event log of Server1.
• Ensure that incidents generated by rulequery1 are closed automatically if Azure Cloud Shell is launched by the company’s SecOps team.
• Implement a custom Microsoft Sentinel workbook named Workbook1 that will include a query to dynamically retrieve data from Webapp1.
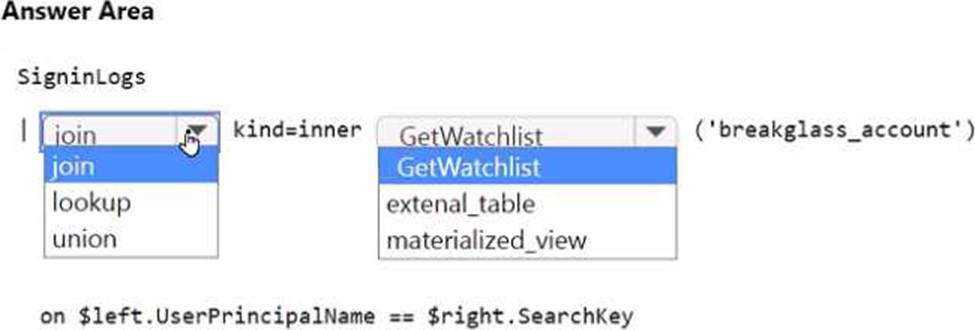
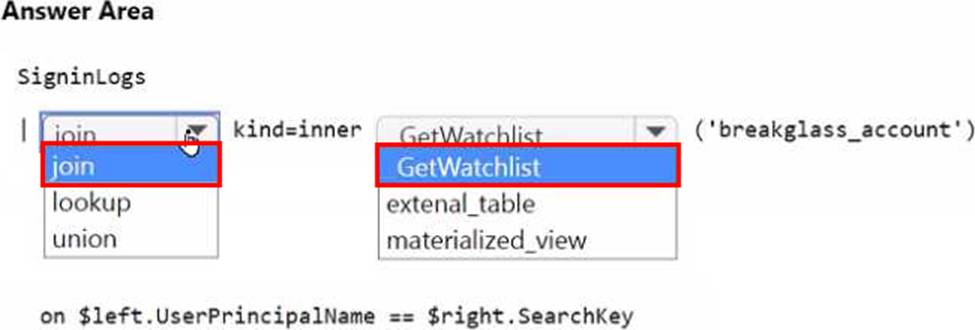
• Implement a Microsoft Sentinel near-real-time (NRT) analytics rule that detects sign-ins to a designated break glass account
• Ensure that HuntingQuery1 runs automatically when the Hunting page of Microsoft Sentinel in the Azure portal is accessed.
• Ensure that higher than normal volumes of password resets for corp.adatum.com user accounts are detected.
• Minimize the overhead associated with queries that use ASIM parsers.
• Ensure that the Group1 members can create and edit playbooks.
• Use built-in ASIM parsers whenever possible.
Adatum identifies the following business requirements:
• Follow the principle of least privilege whenever possible.
• Minimize administrative effort whenever possible. Directory Perineum 92 license.
You need to configure event monitoring for Server1. The solution must meet the Microsoft Sentinel requirements.
What should you create first?
- A . a Microsoft Sentinel automation rule
- B . a Microsoft Sentinel scheduled query rule
- C . a Data Collection Rule (DCR)
- D . an Azure Event Grid topic
HOTSPOT
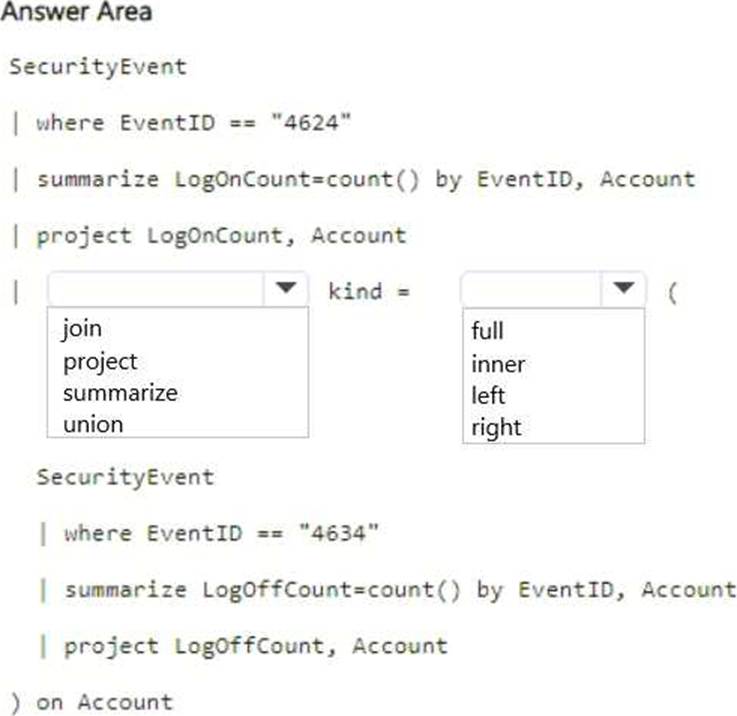
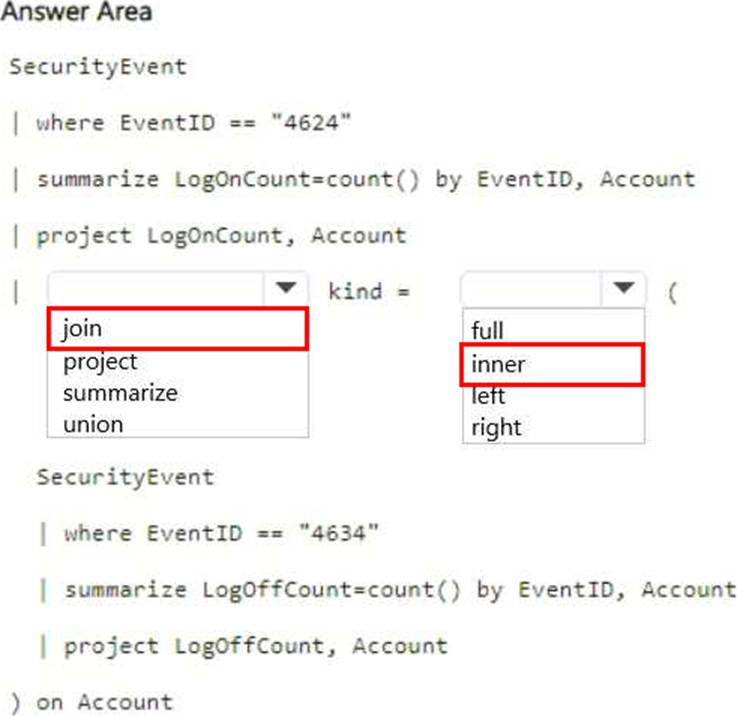
You have a Microsoft Sentine1 workspace that contains a custom workbook named Workbook1.
You need to create a visual in Workbook1 that will display the logon count for accounts that have logon event IDs of 4624 and 4634.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.
DRAG DROP
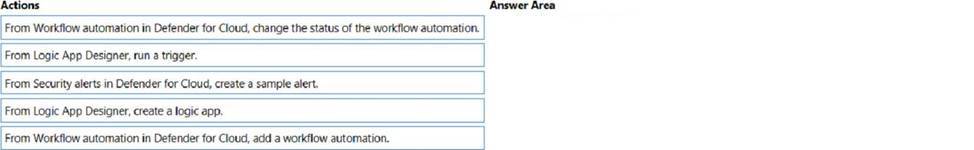
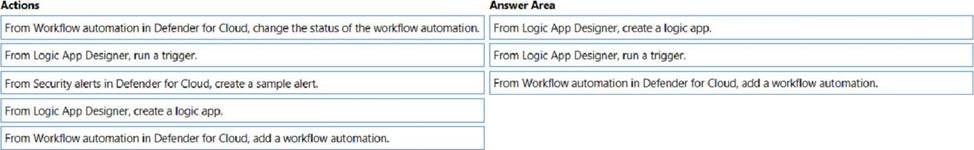
You have an Azure subscription. The subscription contains 10 virtual machines that are onboarded to Microsoft Defender for Cloud.
You need to ensure that when Defender for Cloud detects digital currency mining behavior on a virtual machine, you receive an email notification. The solution must generate a test email.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
You have an Azure subscription that uses Microsoft Defender XDR.
From the Microsoft Defender portal, you perform an audit search and export the results as a file named Filel.csv that contains 10,000 rows.
You use Microsoft Excel to perform Get & Transform Data operations to parse the AuditData column from Filel.csv. The operations fail to generate columns for specific JSON properties.
You need to ensure that Excel generates columns for the specific JSON properties in the audit search results.
Solution: From Excel, you apply filters to the existing columns in Filel.csv to reduce the number of rows, and then you perform the Get & Transform Data operations to parse the AuditData column.
Does this meet the requirement?
- A . Yes
- B . No
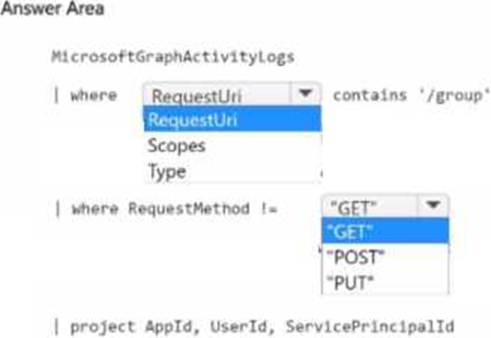
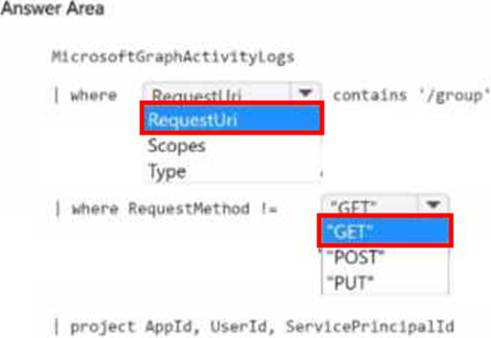
HOTSPOT
You have a Microsoft 365 subscription
You need to identify all the security principals that submitted requests to change or delete groups.
How should you complete the KQL query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains an Microsoft Sentinel workspace.
You need to create a playbook that will run automatically in response to an Microsoft Sentinel alert.
What should you create first?
- A . a trigger in Azure Functions
- B . an Azure logic app
- C . a hunting query in Microsoft Sentinel
- D . an automation rule in Microsoft Sentinel
You have a Microsoft Sentinel workspace named SW1.
You need to identify which anomaly rules are enabled in SW1.
What should you review in Microsoft Sentine1?
- A . Settings
- B . Entity behavior
- C . Analytics
- D . Content hub
HOTSPOT
You need to implement the Microsoft Sentinel NRT rule for monitoring the designated break glass account. The solution must meet the Microsoft Sentinel requirements.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
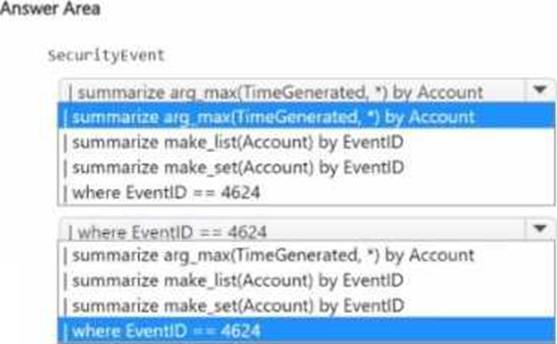
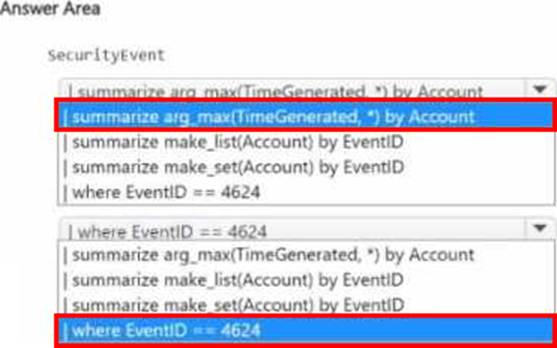
You need to build a KQL query in a Microsoft Sentinel workspace. The query must return the SecurityEvent record for accounts that have the last record with an EventID value of 4624.
How should you complete the query’ To answer, select the appropriate options in the answer area. NOTE: Each coned selection is worth one point