
Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
Your company stores the data for every project in a different Azure subscription. All the subscriptions use the same Azure Active Directory (Azure AD) tenant.
Every project consists of multiple Azure virtual machines that run Windows Server. The Windows events of the virtual machines are stored in a Log Analytics workspace in each machine’s respective subscription.
You deploy Azure Sentinel to a new Azure subscription.
You need to perform hunting queries in Azure Sentinel to search across all the Log Analytics workspaces of all the subscriptions.
Which two actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . Add the Security Events connector to the Azure Sentinel workspace.
- B . Create a query that uses the workspace expression and the union operator.
- C . Use the alias statement.
- D . Create a query that uses the resource expression and the alias operator.
- E . Add the Azure Sentinel solution to each workspace.
You need to assign a role-based access control (RBAC) role to admin1 to meet the Azure Sentinel requirements and the business requirements.
Which role should you assign?
- A . Automation Operator
- B . Automation Runbook Operator
- C . Azure Sentinel Contributor
- D . Logic App Contributor
DRAG DROP
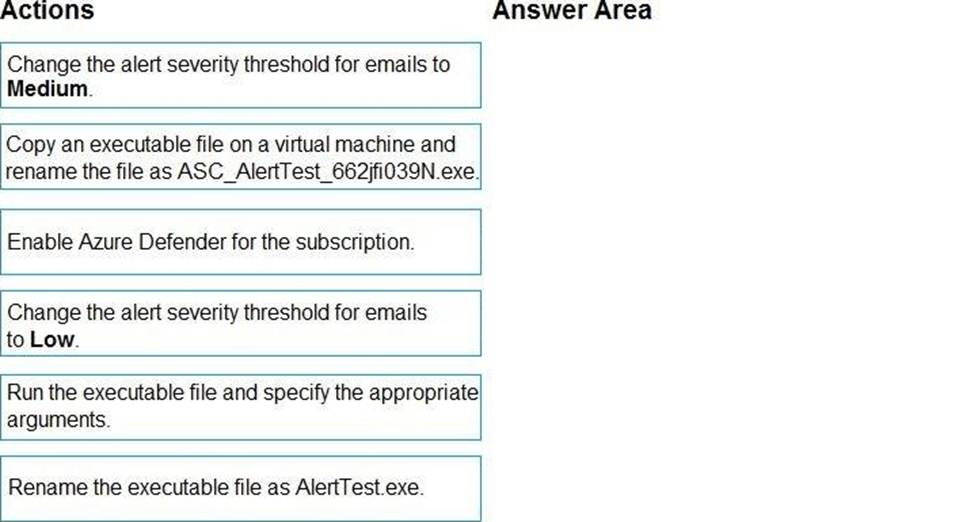
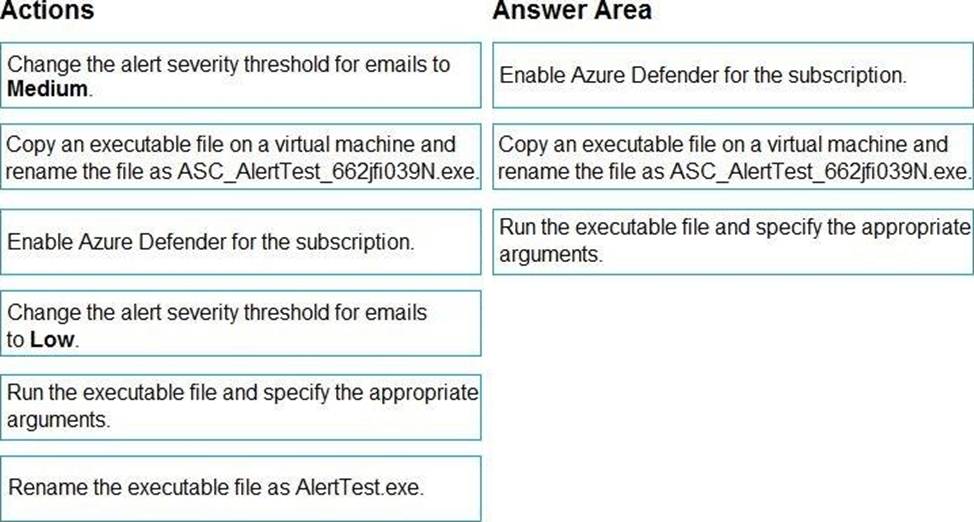
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to configure Azure Security Center to detect possible threats related to sign-ins from suspicious IP addresses to Azure virtual machines. The solution must validate the configuration.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 1 and contains a macOS device named Device1.
You need to investigate a Defender for Endpoint agent alert on Device1.
The solution must meet the following requirements:
• Identify all the active network connections on Device1.
• Identify all the running processes on Device1.
• Retrieve the login history of Device1.
• Minimize administrative effort.
What should you do first from the Microsoft Defender portal?
- A . From Advanced features in Endpoints, disable Authenticated telemetry.
- B . From Advanced features in Endpoints, enable Live Response unsigned script execution.
- C . From Devices, click Collect investigation package for Device 1.
- D . From Devices, initiate a live response session on Device1.
HOTSPOT
You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain that syncs with a Microsoft Entra tenant.
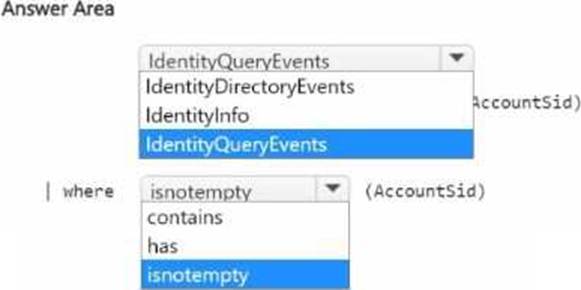
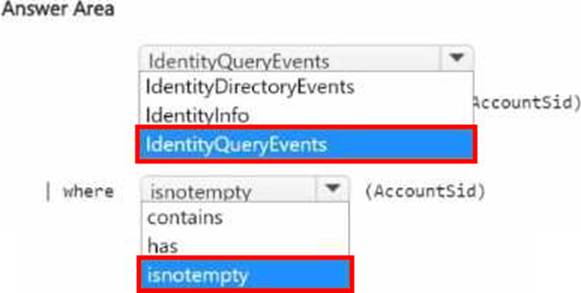
You need to identify LDAP requests by AD DS users to enumerate AD DS objects.
How should you complete the KQL query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You use Azure Defender.
You have an Azure Storage account that contains sensitive information.
You need to run a PowerShell script if someone accesses the storage account from a suspicious IP address.
Which two actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . From Azure Security Center, enable workflow automation.
- B . Create an Azure logic appthat has a manual trigger
- C . Create an Azure logic app that has an Azure Security Center alert trigger.
- D . Create an Azure logic appthat has an HTTP trigger.
- E . From Azure Active Directory (Azure AD), add an app registration.
You recently deployed Azure Sentinel.
You discover that the default Fusion rule does not generate any alerts. You verify that the rule is enabled.
You need to ensure that the Fusion rule can generate alerts.
What should you do?
- A . Disable, and then enable the rule.
- B . Add data connectors
- C . Create a new machine learning analytics rule.
- D . Add a hunting bookmark.
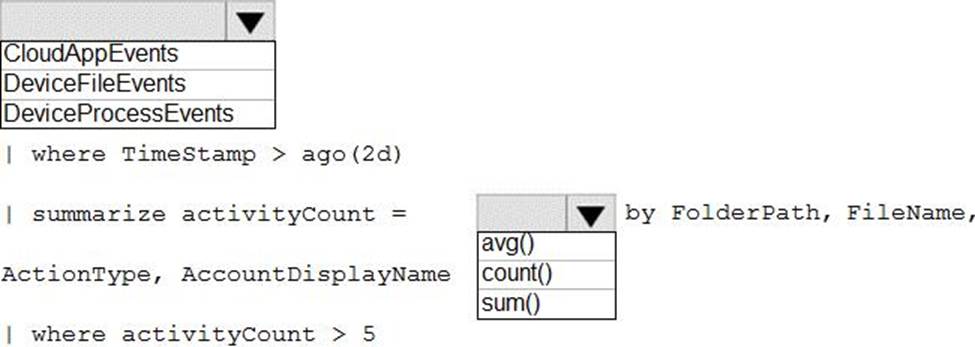
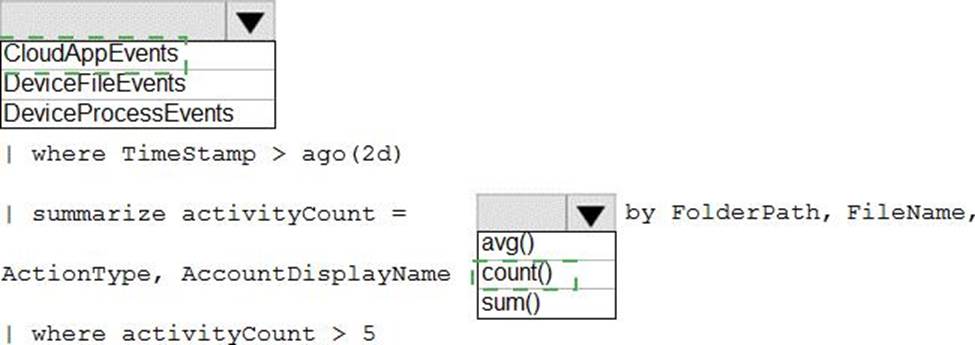
HOTSPOT
You need to create an advanced hunting query to investigate the executive team issue.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
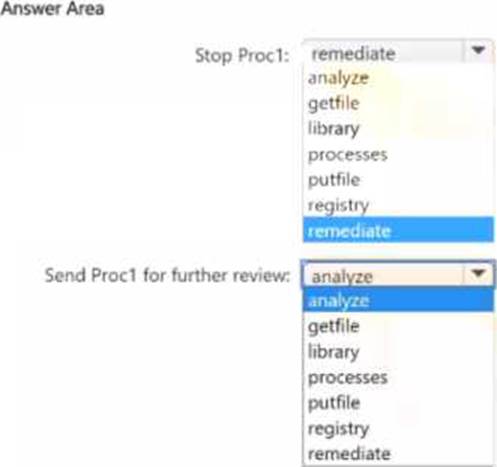
You have a Microsoft 365 subscription that uses Microsoft Defender XOR and contains a Windows device named Oevice1. You investigate a suspicious process named Prod on Device! by using a live response session.
You need to perform the following actions:
• Stop Prod.
• Send Prod for further review.
Which live response command should you run for each action? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
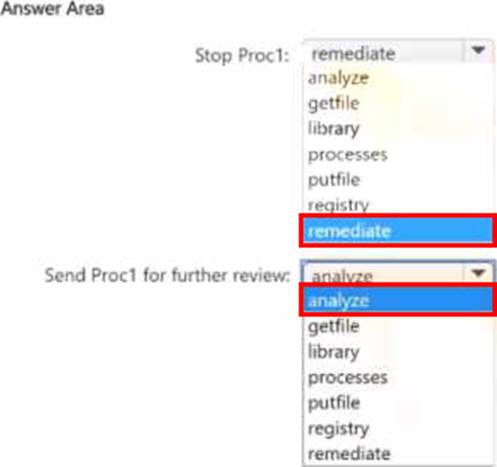
You have a Microsoft 365 subscription that uses Microsoft Defender XOR and contains a Windows device named Oevice1. You investigate a suspicious process named Prod on Device! by using a live response session.
You need to perform the following actions:
• Stop Prod.
• Send Prod for further review.
Which live response command should you run for each action? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.