
Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
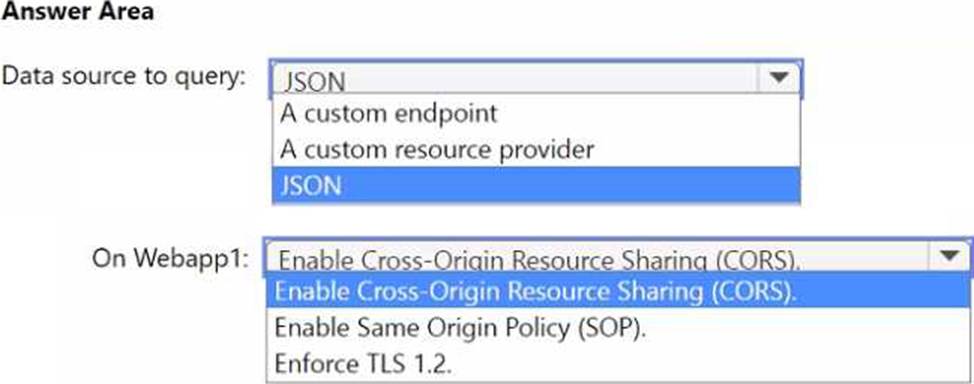
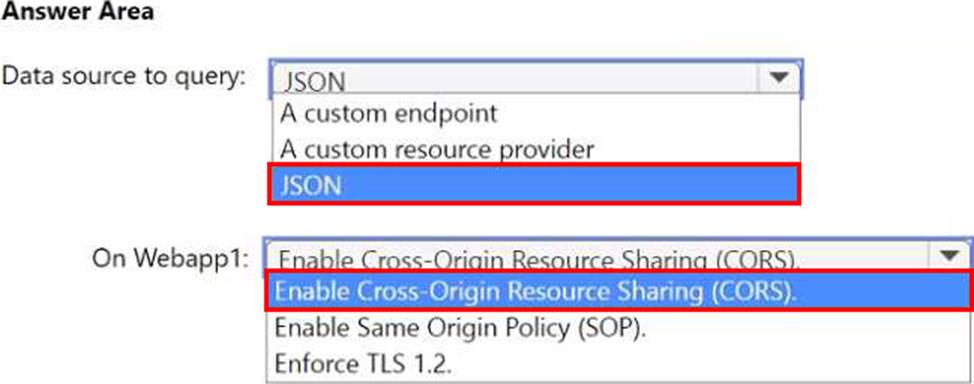
HOTSPOT
You need to implement the query for Workbook1 and Webapp1. The solution must meet the Microsoft Sentinel requirements.
How should you configure the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
DRAG DROP
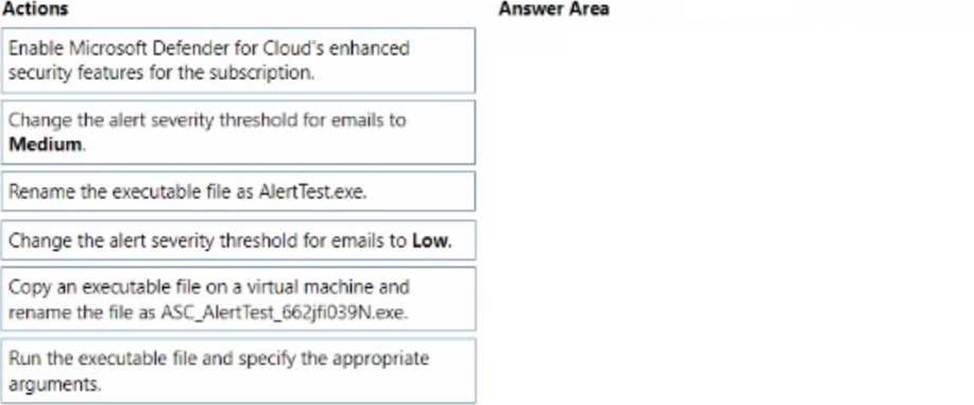
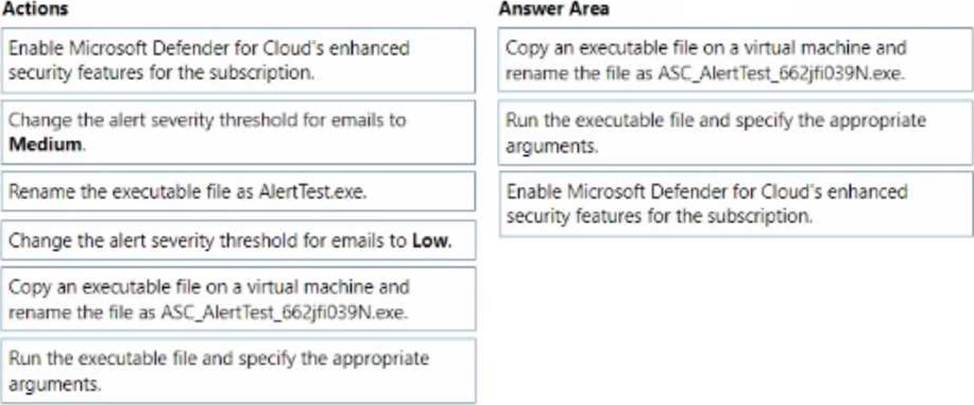
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to validate that Microsoft Defender for Cloud will trigger an alert when a malicious file is present on an Azure virtual machine running Windows Server.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order. NOTE: More than one order of answer choices is correct. You will receive credit for any of the correct orders you select.
HOTSPOT
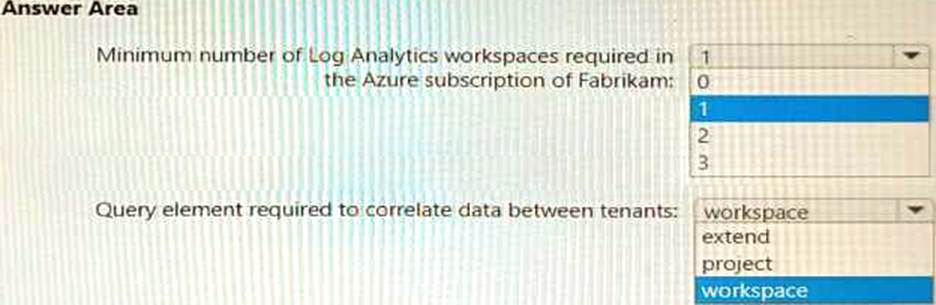
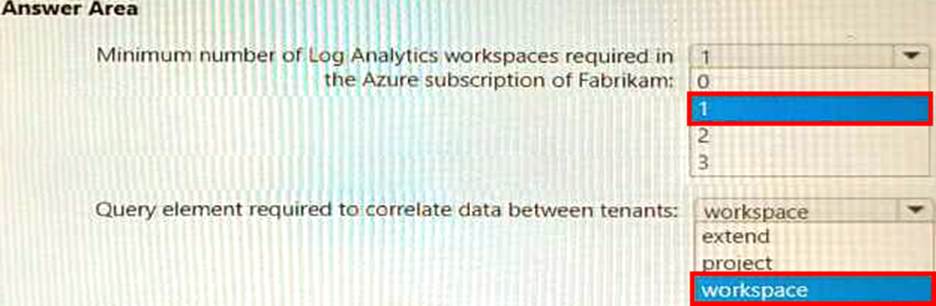
You need to implement Microsoft Sentinel queries for Contoso and Fabrikam to meet the technical requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You need to ensure that the Group1 members can meet the Microsoft Sentinel requirements.
Which role should you assign to Group1?
- A . Microsoft Sentinel Automation Contributor
- B . Logic App Contributor
- C . Automation Operator
- D . Microsoft Sentinel Playbook Operator
You have an Azure subscription that uses Microsoft Sentinel and contains 100 Linux virtual machines.
You need to monitor the virtual machines by using Microsoft Sentinel.
The solution must meet the fallowing requirements:
• Minimize administrative effort
• Minimize the parsing required to read log data What should you configure?
- A . REST API integration
- B . a SysJog connector
- C . a Log Analytics Data Collector API
- D . a Common Event Format (CEF) connector
You have a Microsoft 365 E5 subscription that is linked to a hybrid Azure AD tenant.
You need to identify all the changes made to Domain Admins group during the past 30 days.
What should you use?
- A . the Azure Active Directory Provisioning Analysis workbook
- B . the Overview settings of Insider risk management
- C . the Modifications of sensitive groups report in Microsoft Defender for Identity
- D . the identity security posture assessment in Microsoft Defender for Cloud Apps
You have an Azure subscription that uses resource type for Cloud.
You need to filter the security alerts view to show the following alerts:
• Unusual user accessed a key vault
• Log on from an unusual location
• Impossible travel activity
Which severity should you use?
- A . Informational
- B . Low
- C . Medium
- D . High
You receive a security bulletin about a potential attack that uses an image file.
You need to create an indicator of compromise (IoC) in Microsoft Defender for Endpoint to prevent the attack.
Which indicator type should you use?
- A . a URL/domain indicator that has Action set to Alert only
- B . a URL/domain indicator that has Action set to Alert and block
- C . a file hash indicator that has Action set to Alert and block
- D . a certificate indicator that has Action set to Alert and block
You have an Azure subscription that contains an Azure logic app named app1 and a Microsoft Sentinel workspace that has an Azure AD connector. You need to ensure that app1 launches when Microsoft Sentinel detects an Azure AD-generated alert.
What should you create first?
- A . a repository connection
- B . awatchlist
- C . an analytics rule
- D . an automation rule
You have a Microsoft 365 subscription. The subscription uses Microsoft 365 Defender and has data loss prevention (DLP) policies that have aggregated alerts configured.
You need to identify the impacted entities in an aggregated alert.
What should you review in the DIP alert management dashboard of the Microsoft Purview compliance portal?
- A . the Details tab of the alert
- B . Management log
- C . the Sensitive Info Types tab of the alert
- D . the Events tab of the alert