
Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
You need to ensure that the processing of incidents generated by rulequery1 meets the Microsoft Sentinel requirements.
What should you create first?
- A . a playbook with an incident trigger
- B . a playbook with an entity trigger
- C . an Azure Automation rule
- D . a playbook with an alert trigger
You have a Microsoft 365 subscription that uses Microsoft Purview and Microsoft Teams.
You have a team named Team1 that has a project named Project 1.
You need to identify any Project1 files that were stored on the team site of Team1 between February 1, 2023, and February 10, 2023.
Which KQL query should you run?
A)
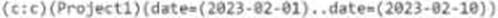
B)
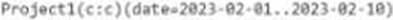
C)
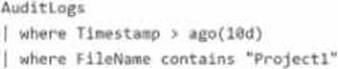
D)
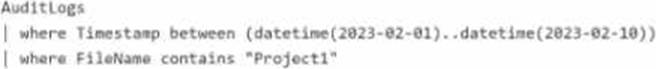
- A . Option A
- B . Option B
- C . Option C
- D . Option D
You receive an alert from Azure Defender for Key Vault.
You discover that the alert is generated from multiple suspicious IP addresses.
You need to reduce the potential of Key Vault secrets being leaked while you investigate the issue. The solution must be implemented as soon as possible and must minimize the impact on legitimate users.
What should you do first?
- A . Modify the access control settings for the key vault.
- B . Enable the Key Vault firewall.
- C . Create an application security group.
- D . Modify the access policy for the key vault.
You are configuring Microsoft Cloud App Security.
You have a custom threat detection policy based on the IP address ranges of your company’s United States-based offices.
You receive many alerts related to impossible travel and sign-ins from risky IP addresses.
You determine that 99% of the alerts are legitimate sign-ins from your corporate offices.
You need to prevent alerts for legitimate sign-ins from known locations.
Which two actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . Override automatic data enrichment.
- B . Add the IP addresses to the corporate address range category.
- C . Increase the sensitivity level of the impossible travel anomaly detection policy.
- D . Add the IP addresses to the other address range category and add a tag.
- E . Create an activity policy that has an exclusion for the IP addresses.
You have an Azure subscription that uses Microsoft Defender for Cloud and contains a storage account named storage1. You receive an alert that there was an unusually high volume of delete operations on the blobs in storage1.
You need to identify which blobs were deleted.
What should you review?
- A . the Azure Storage Analytics logs
- B . the activity logs of storage1
- C . the alert details
- D . the related entities of the alert
HOTSPOT
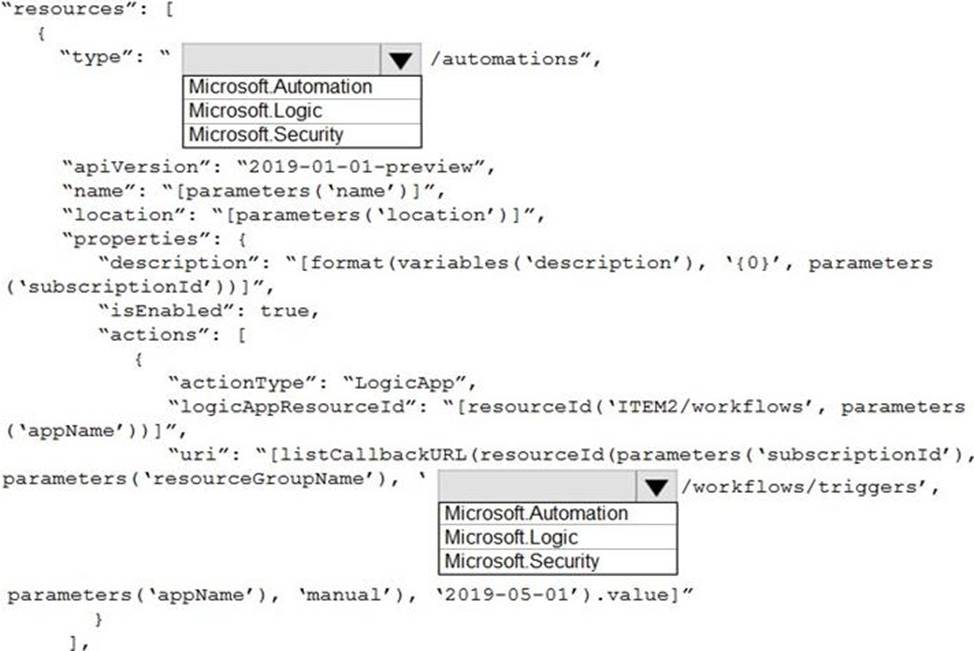
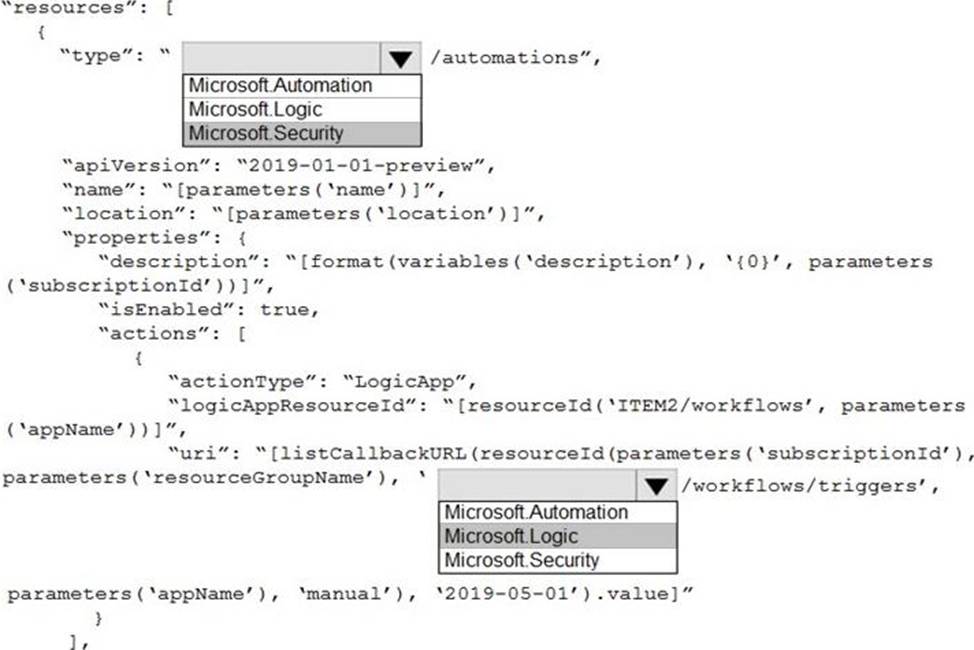
You need to use an Azure Resource Manager template to create a workflow automation that will trigger an automatic remediation when specific security alerts are received by Azure Security Center.
How should you complete the portion of the template that will provision the required Azure resources? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
HOTSPOT
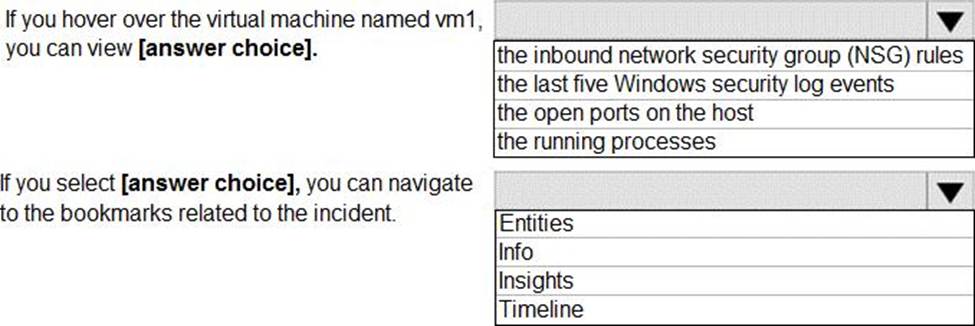
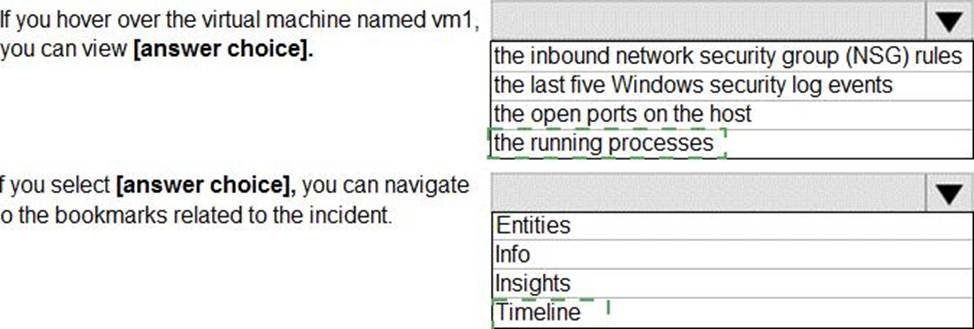
From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.
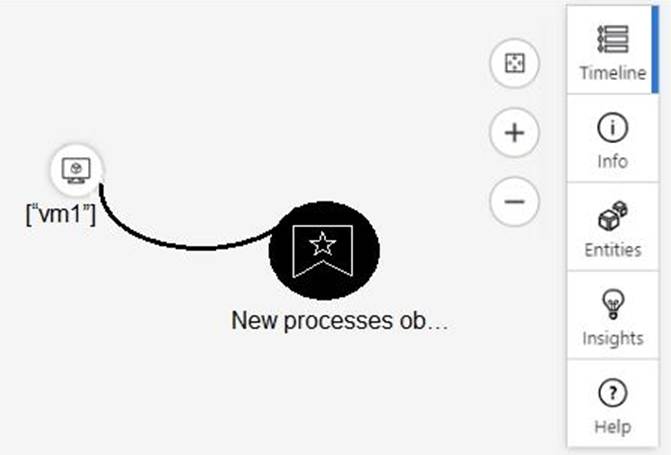
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.
Which rule setting should you configure to meet the Microsoft Sentinel requirements?
- A . From Set rule logic, turn off suppression.
- B . From Analytic rule details, configure the tactics.
- C . From Set rule logic, map the entities.
- D . From Analytic rule details, configure the severity.
You have a Microsoft Sentinel workspace named Workspace1.
You need to exclude a built-in, source-specific Advanced Security information Model (ASIM) parse from a built-in unified ASIM parser.
What should you create in Workspace1?
- A . a watch list
- B . an analytic rule
- C . a hunting query
- D . a workbook
You have a Microsoft Sentinel workspace.
You enable User and Entity Behavior Analytics (UFBA) by using Audit logs and Signin logs.
The following entities are detected in the Azure AD tenant:
• App name: App1
• IP address: 192.168.1.2
• Computer name: Device1
• Used client app: Microsoft Edge
• Email address: [email protected]
• Sign-in URL: https://www.company.com
Which entities can be investigated by using UEBA?
- A . app name, computer name, IP address, email address, and used client app only
- B . IP address and email address only
- C . used client app and app name only
- D . IP address only