
Microsoft SC-200 Practice Exams
Last updated on Oct 22,2026- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Certification Provider: Microsoft
- Latest update: Oct 22,2026
You have an Azure subscription that uses Microsoft Sentinel.
You need to create a custom report that will visualise sign-in information over time.
What should you create first?
- A . a workbook
- B . a hunting query
- C . a notebook
- D . a playbook
DRAG DROP
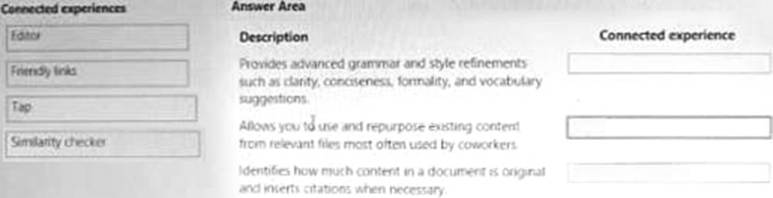
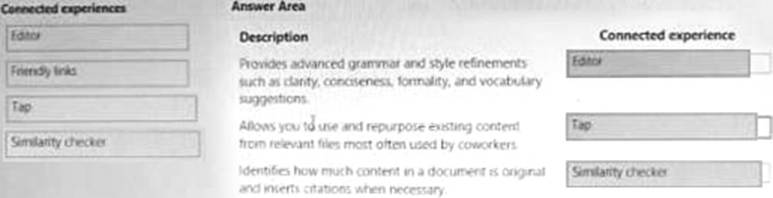
A company wants to analyze by using Microsoft 365 Apps.
You need to describe the connected experiences the company can use.
Which connected experiences should you describe? To answer, drag the appropriate connected experiences to the correct description. Each connected experience may be used once, more than once, or not at all. You may need to drag the split between panes or scroll to view content. NOTE: Each correct selection is worth one point.
HOTSPOT
You have the resources shown in the following table.
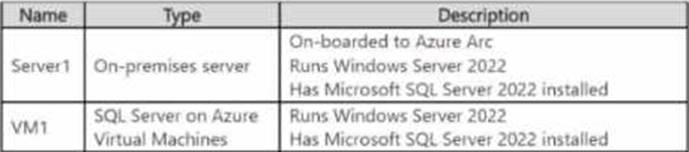
You have an Azure subscription that uses Microsoft Defender for Cloud.
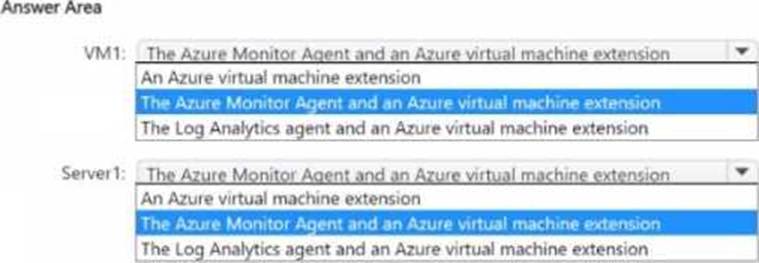
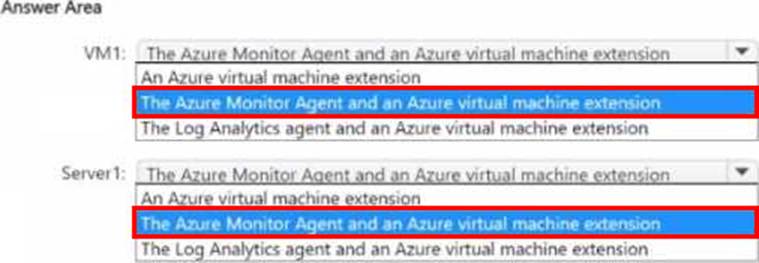
You need to use Defender for Cloud to protect VM1 and Server1.
The solution must meet the following requirements:
• Support Advanced Threat Protection and vulnerability assessment
• Register each SQL Server 2022 instance as a SQL virtual machine.
• Minimize implementation and administrative effort
What should you deploy to each server? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that uses Microsoft Defender XDR.
From the Microsoft Defender portal, you perform an audit search and export the results as a file named Filel.csv that contains 10,000 rows.
You use Microsoft Excel to perform Get & Transform Data operations to parse the AuditData column from Filel.csv. The operations fail to generate columns for specific JSON properties.
You need to ensure that Excel generates columns for the specific JSON properties in the audit search results.
Solution: From Defender, you modify the search criteria of the audit search to reduce the number of returned records, and then you export the results. From Excel, you perform the Get & Transform Data operations by using the new export.
Does this meet the requirement?
- A . Yes
- B . No
You have a Microsoft 365 E5 subscription that uses Microsoft 365 Defender.
You need to review new attack techniques discovered by Microsoft and identify vulnerable resources in the subscription. The solution must minimize administrative effort
Which blade should you use in the Microsoft 365 Defender portal?
- A . Advanced hunting
- B . Threat analytics
- C . Incidents & alerts
- D . Learning hub
You have a Microsoft Sentinel workspace that has user and Entity Behavior Analytics (UEBA) enabled for Signin Logs.
You need to ensure that failed interactive sign-ins are detected.
The solution must minimize administrative effort.
What should you use?
- A . a scheduled alert query
- B . a UEBA activity template
- C . the Activity Log data connector
- D . a hunting query
You need to restrict cloud apps running on CLIENT1 to meet the Microsoft Defender for Endpoint requirements.
Which two configurations should you modify? Each correct answer present part of the solution. NOTE: Each correct selection is worth one point.
- A . the Onboarding settings from Device management in Microsoft Defender Security Center
- B . Cloud App Security anomaly detection policies
- C . Advanced features from Settings in Microsoft Defender Security Center
- D . the Cloud Discovery settings in Cloud App Security
You create an Azure subscription named sub1.
In sub1, you create a Log Analytics workspace named workspace1.
You enable Azure Security Center and configure Security Center to use workspace1.
You need to ensure that Security Center processes events from the Azure virtual machines that report to workspace1.
What should you do?
- A . In workspace1, install a solution.
- B . In sub1, register a provider.
- C . From Security Center, create a Workflow automation.
- D . In workspace1, create a workbook.
You have five on-premises Linux servers.
You have an Azure subscription that uses Microsoft Defender for Cloud.
You need to use Defender for Cloud to protect the Linux servers.
What should you install on the servers first?
- A . the Dependency agent
- B . the Log Analytics agent
- C . the Azure Connected Machine agent
- D . the Guest Configuration extension
You need to complete the query for failed sign-ins to meet the technical requirements.
Where can you find the column name to complete the where clause?
- A . Security alerts in Azure Security Center
- B . Activity log in Azure
- C . Azure Advisor
- D . the query windows of the Log Analytics workspace