Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: User1 [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 7
You need to collect all the audit failure data from the security log of a virtual machine named VM1 to an Azure Storage account. To complete this task, sign in to the Azure portal.
Note: This question is part of a series of questions that present the same scenario. Each question in
the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription named Sub1.
You have an Azure Storage account named sa1 in a resource group named RG1.
Users and applications access the blob service and the file service in sa1 by using several shared access signatures (SASs) and stored access policies.
You discover that unauthorized users accessed both the file service and the blob service.
You need to revoke all access to sa1.
Solution: You regenerate the Azure storage account access keys.
Does this meet the goal?
- A . Yes
- B . No
To configure role-based access control, what should you primarily use in Azure?
- A . Azure Policies
- B . Access Control (IAM)
- C . Azure Blueprints
- D . Azure Management Groups
To configure role-based access control, what should you primarily use in Azure?
- A . Azure Policies
- B . Access Control (IAM)
- C . Azure Blueprints
- D . Azure Management Groups
You are troubleshooting a security issue for an Azure Storage account You enable Azure Storage Analytics logs and archive It to a storage account.
What should you use to retrieve the diagnostics logs?
- A . Azure Storage Explorer
- B . SQL query editor in Azure
- C . Azure Monitor
- D . Azure Cosmos DB explorer
HOTSPOT
You have a Microsoft Entra tenant that contains the users shown in the following table.
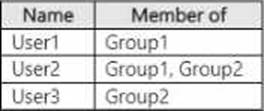
You configure a Conditional Access policy that has the following settings:
• Name: CAPolicy1
• Assignments
o Users or workload identities: Group1
o Target resources: All cloud apps
• Access controls
o Grant access: Require multifactor authentication
From Microsoft Authenticator settings for the tenant, the Enable and Target settings are configured as shown in the Enable and Target exhibit. (Click the Enable and Target tab.)
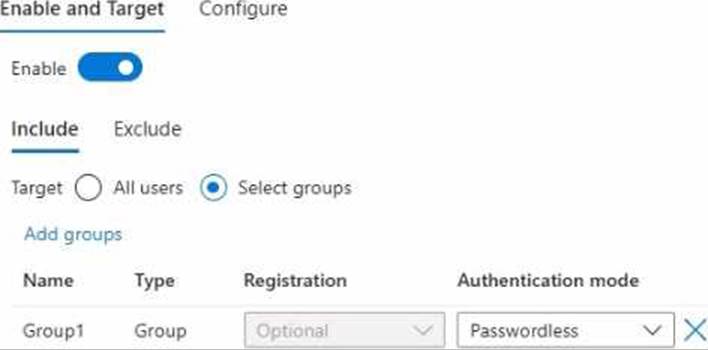
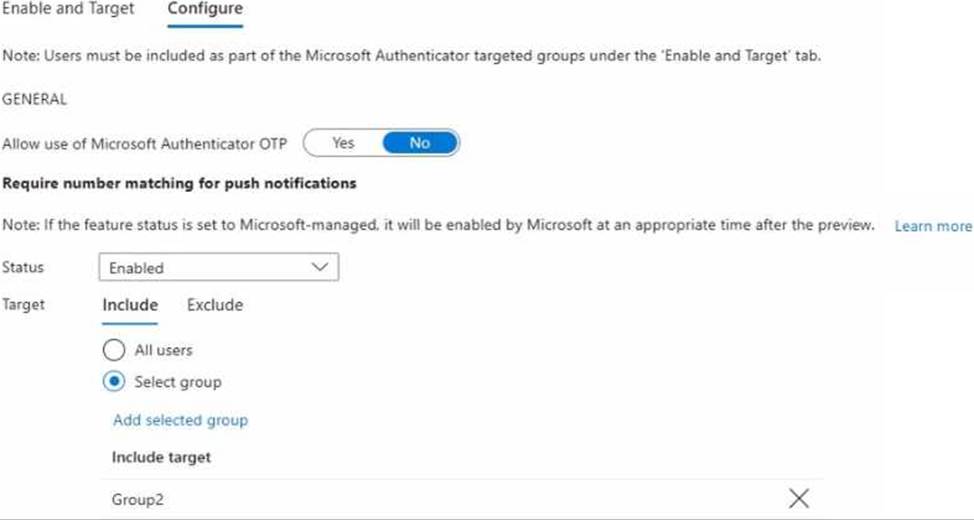
From Microsoft Authenticator settings for the tenant, the Configure settings are configured as shown in the Configure exhibit. (Click the Configure tab.)
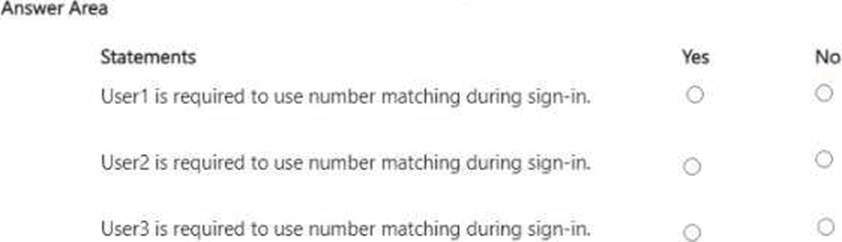
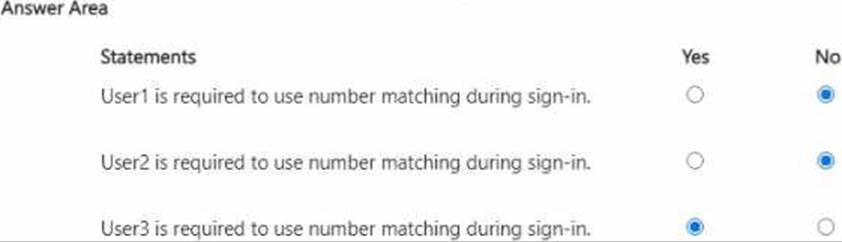
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
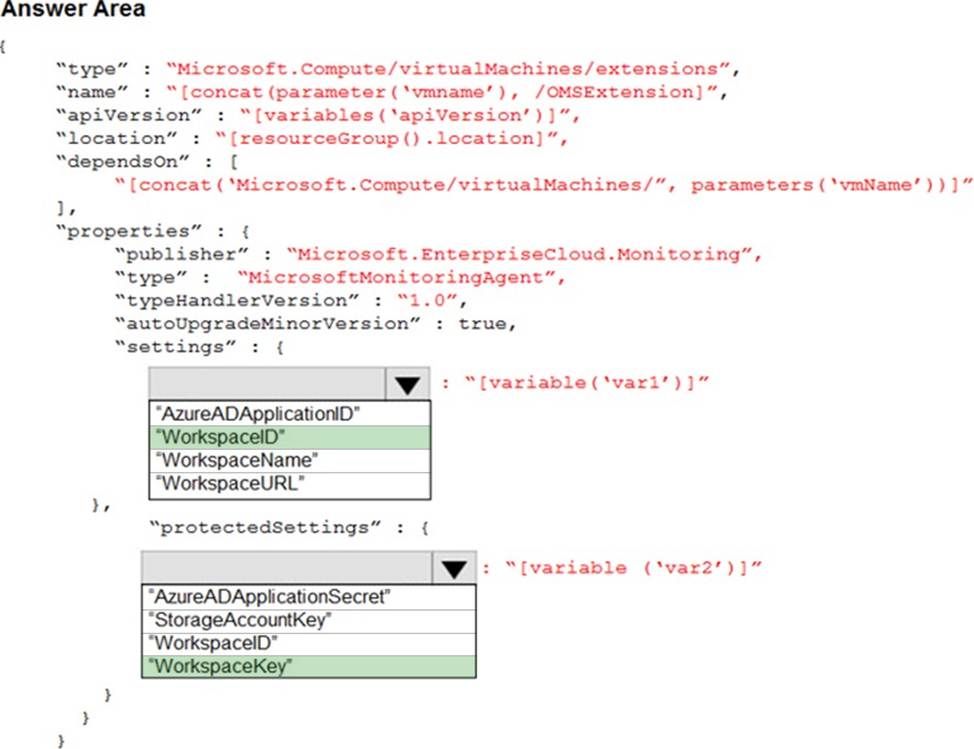
HOTSPOT
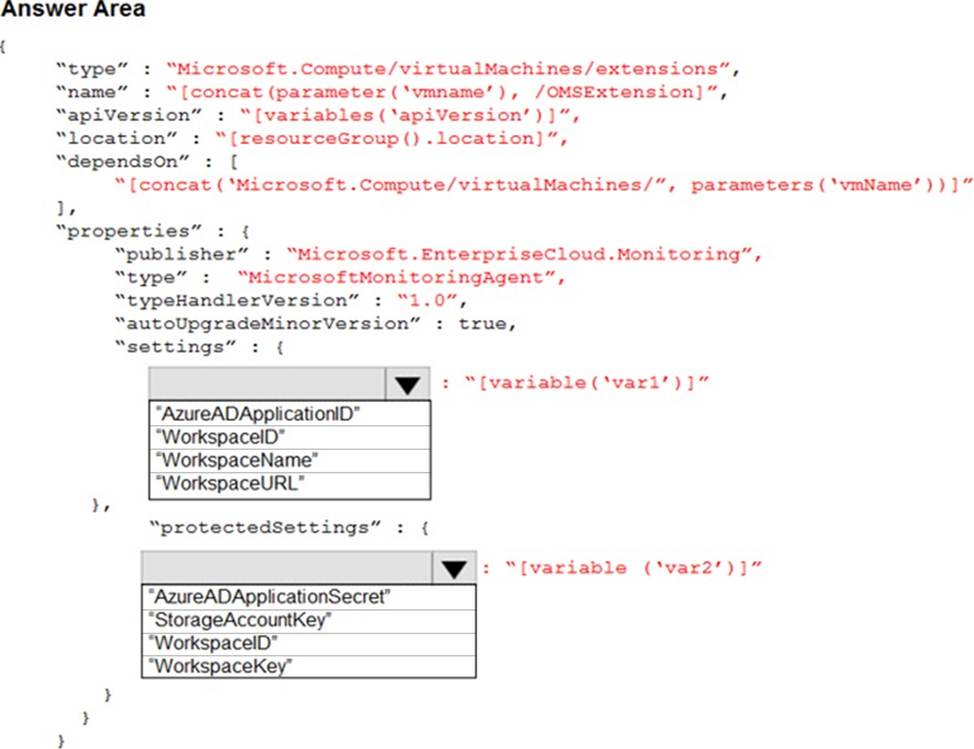
You plan to use Azure Log Analytics to collect logs from 200 servers that run Windows Server 2016.
You need to automate the deployment of the Microsoft Monitoring Agent to all the servers by using an Azure Resource Manager template.
How should you complete the template? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains the subnets shown in the following table.
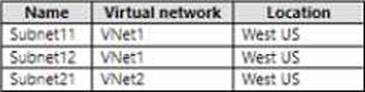
The subscription contains Azure web app named WebApp1 that has the following configurations.
* Region West Us
* Virtual network VNet1
* VNet integration on: Enabled
* Outbound subnet: Subnet11
* Windows plan (West US): ASP1
You plan to deploy an Azure web app named WebApp2 that will have the following settings:
* Region: West US
* VNet integration on-Enabled
* Windows plan (West UAS): WebApp2?
To which subnets can you integrate WebApp2?
- A . Subnet11 only
- B . Subnet2 only
- C . Subnet11 or subnet12 only
- D . Subnet2 or Subnet21 only
- E . Subnet11, subnet2, or Subnet21
HOTSPOT
You have an Azure subscription that is linked to an Azure AD tenant and contains the virtual machines shown in the following table.
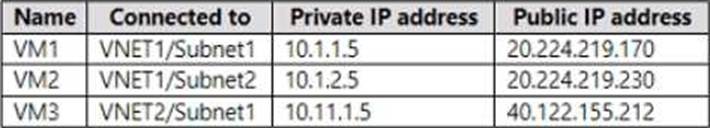
The subnets of the virtual networks have the service endpoints shown in the following table.
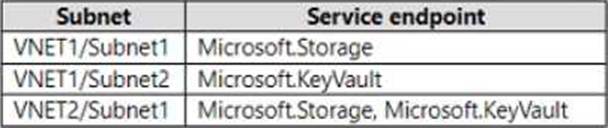
You create the resources shown in the following table.
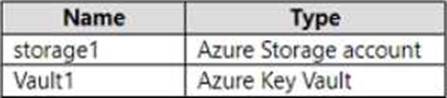
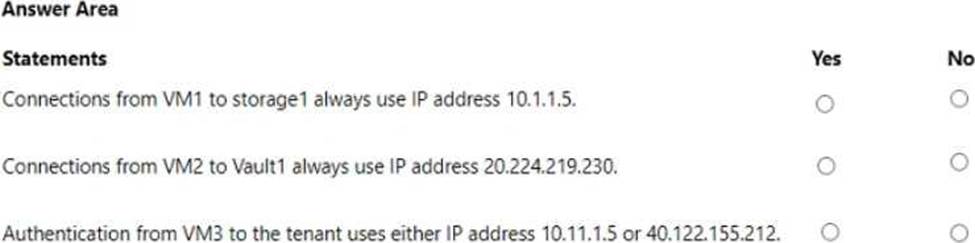
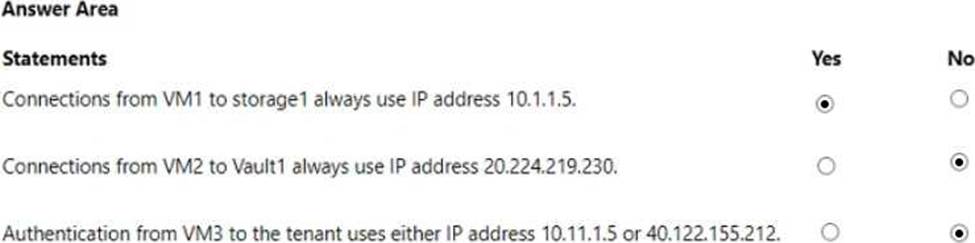
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
HOTSPOT
Your on-premises network contains the servers shown in the following table.
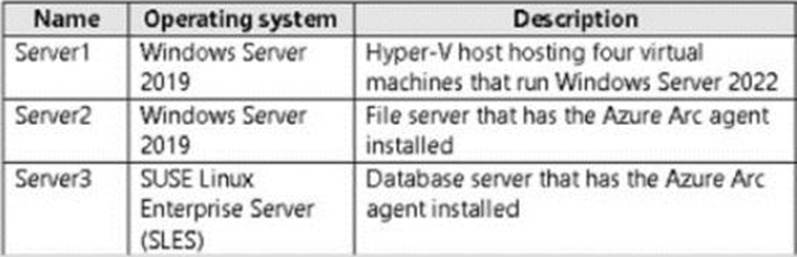
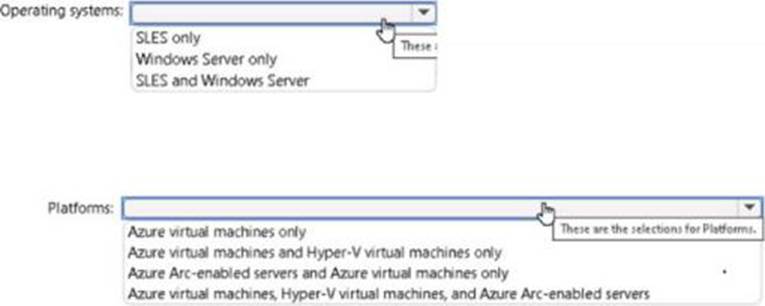
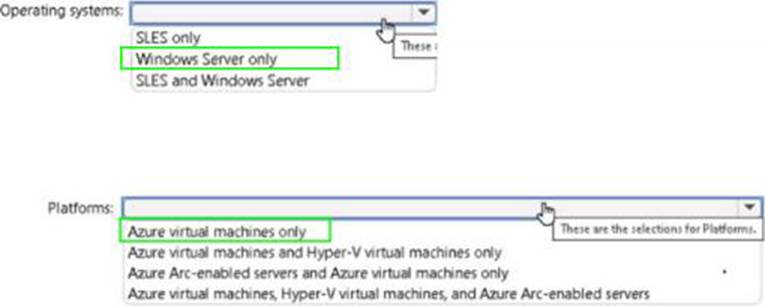
You have an Azure subscription that contains multiple virtual machines that run either Windows Server 2019 or SLES. You plan to implement adaptive application controls in Microsoft Defender for Cloud.
Which operating systems and platforms can you monitor? To answer, select the appropriate options in the answer area.