
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
You have an Azure Active Directory (Azure AD) tenant named Contoso.com and an Azure Service (AKS) cluster AKS1.
You discover that AKS1 cannot be accessed by using accounts from Contoso.com
You need to ensure AKS1 can be accessed by using accounts from Contoso.com The solution must minimize administrative effort.
What should you do first?
- A . From Azure recreate AKS1,
- B . From AKS1, upgrade the version of Kubermetes.
- C . From Azure AD, implement Azure AD Premium P2.
- D . From Azure AD, configure the User settings
You need to meet the technical requirements for the finance department users.
Which CAPolicy1 settings should you modify?
- A . Cloud apps or actions
- B . Conditions
- C . Grant
- D . Session
HOTSPOT
You have an Azure subscription named Subscription1 that contains the resources shown in the following table.
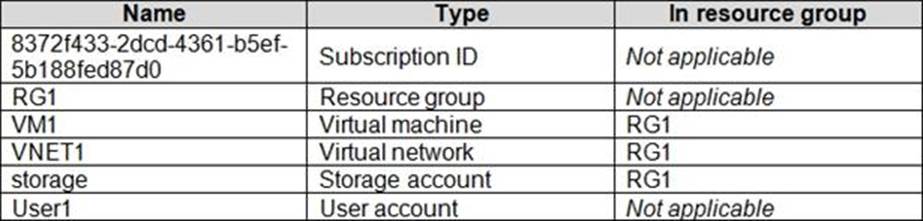
You create an Azure role by using the following JSON file.
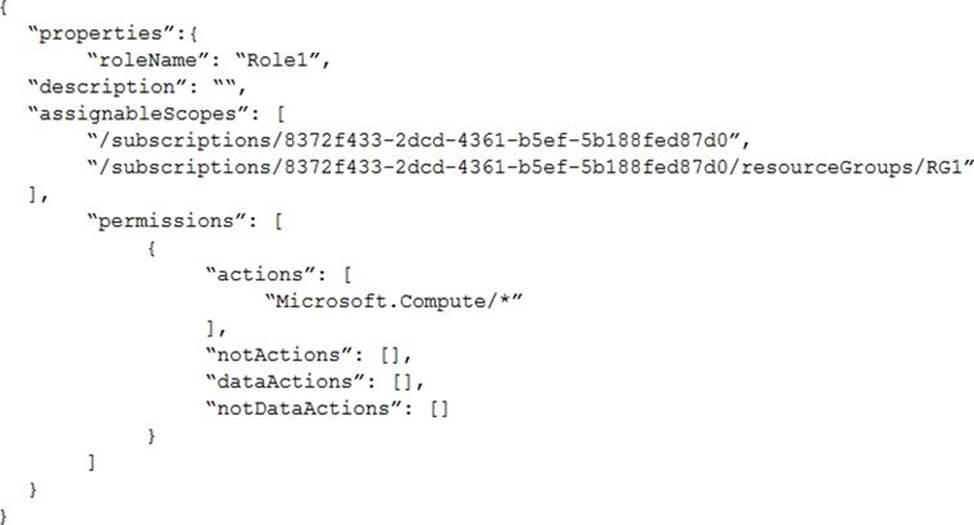
You assign Role1 to User1 for RG1.
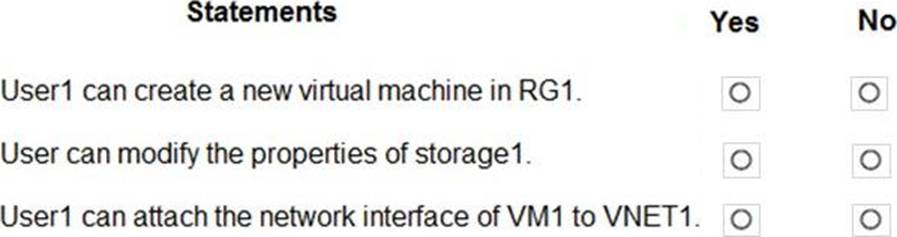
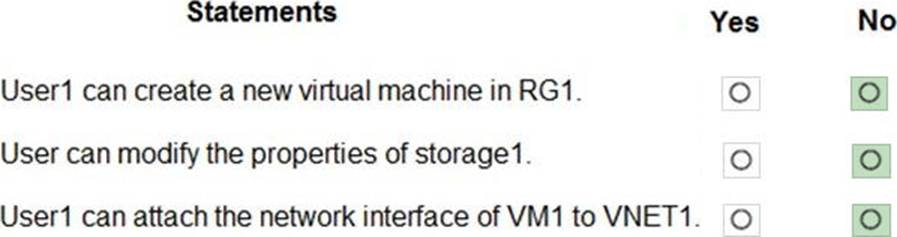
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
You have an Azure Active Directory (Azure AD) tenant that contains a group named Group1
You need to ensure that the members of Group1 sign in by using passwordless authentication
What should you do?
- A . Configure the Microsoft Authenticator authentication method policy.
- B . Configure the certificate-based authentication (CBA) policy.
- C . Configure the sign-in risk policy.
- D . Create a Conditional Access policy.
You have an Azure subscription that contains an Azure SQL server named SQL1. SQL1 contains. You need to use Microsoft Defender for Cloud to complete a vulnerability assessment for DB1.
What should you do first?
- A . From Advanced Threat Protection types, select SQL injection vulnerability.
- B . Configure the Send scan report to setting.
- C . Set Periodic recurring scans to ON.
- D . Enable the Microsoft Defender for SQL plan.
You have a Microsoft Entra tenant that contains a user named User1.
You plan to enable passwordless authentication for the tenant.
You need to ensure that User1 can enable the combined registration experience. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A . Security Administrator
- B . Global Administrator
- C . Privileged Role Administrator
- D . Authentication Administrator
HOTSPOT
You have an Azure subscription that contains the resources shown in the following table.
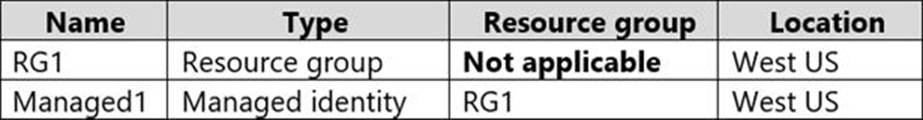
The subscription is linked to an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
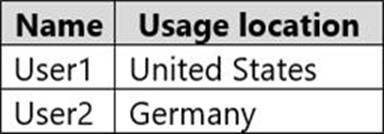
You create the groups shown in the following table.
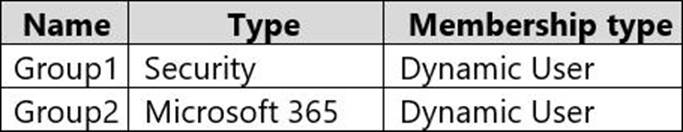
The membership rules for Group1 and Group2 are configured as shown in the following exhibit.
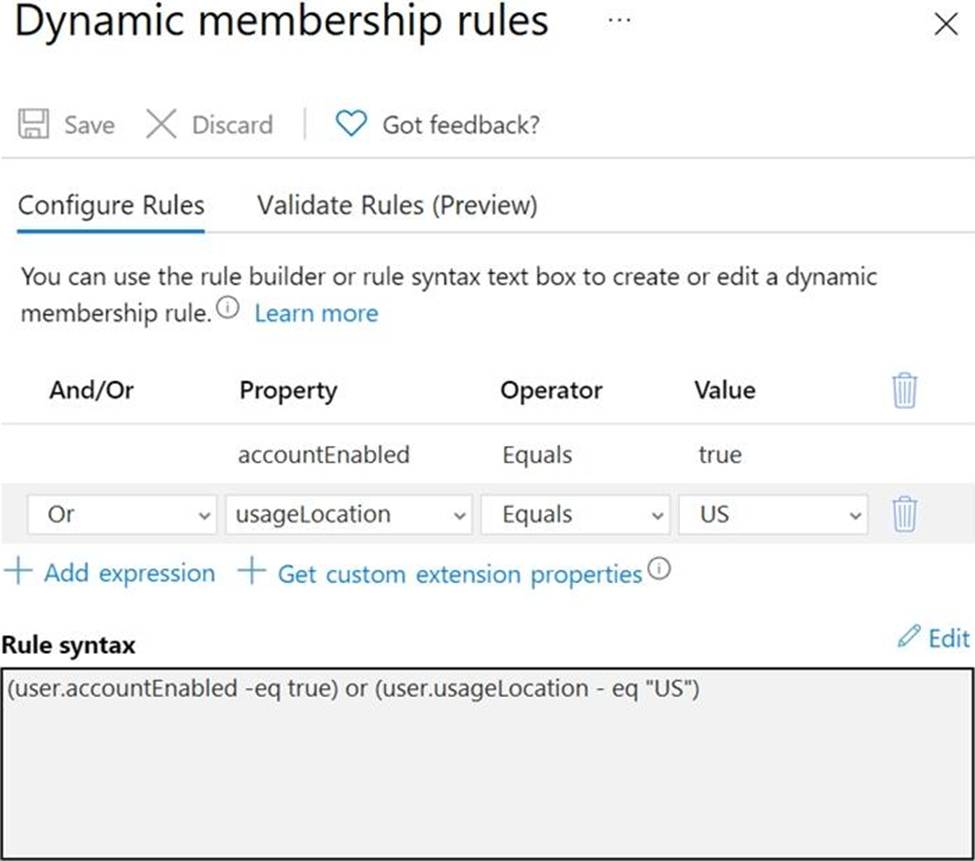
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
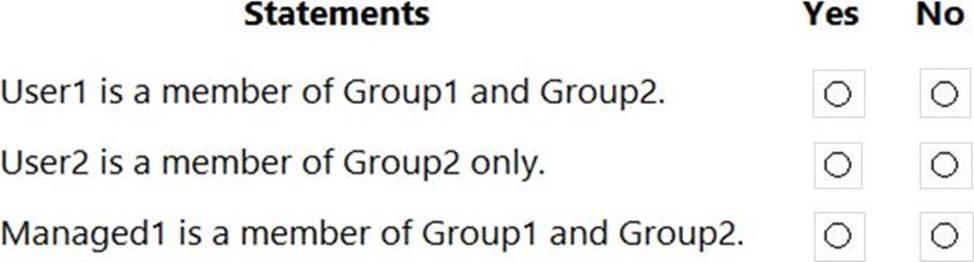
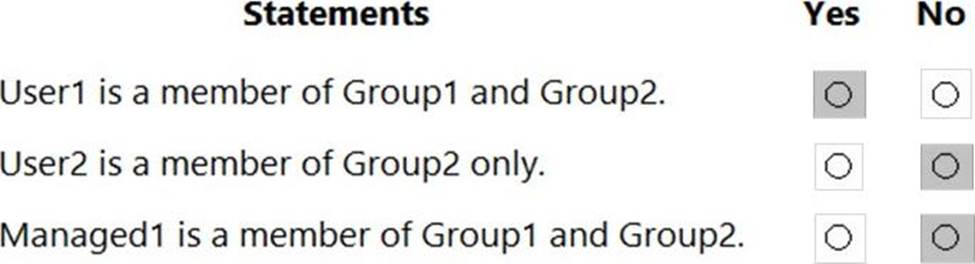
You have an Azure subscription named Sub1 that has Security defaults disabled.
The subscription contains the following users:
• Five users that have owner permissions for Sub1.
• Ten users that have owner permissions for Azure resources. None of the users have multi-factor authentication (MFA) enabled.
Sub1 has the secure score as shown in the Secure Score exhibit. (Click the Secure Score tab.)
You plan to enable MFA for the following users:
• Five users that have owner permissions for Sub1.
• Five users that have owner permissions for Azure resources.
By how many points will the secure score increase after you perform the planned changes?
- A . 0
- B . 5
- C . 7.5
- D . 10
- E . 14
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to rt As a result, these questions will not appear in the review screen.
You have an Azure subscription named Sub1.
You have an Azure Storage account named Sa1 in a resource group named RG1.
Users and applications access the blob service and the file service in Sal by using several shared access signatures {SASs) and stored access policies.
You discover that unauthorized users accessed both the rile service and the blob service.
You need to revoke all access to Sa1.
Solution: You regenerate the access keys.
Does this meet the goal?
- A . Yes
- B . No
You have an Azure subscription that contains a web app named App1.
Users must be able to select between a Google identity or a Microsoft identity when authenticating to App1.
You need to add Google as an identity provider in Azure AD.
Which two pieces of information should you configure? Each correct answer presents part of the solution.
Each correct selection is worth one point
- A . a tenant name
- B . a tenant ID
- C . the endpoint URL Of an application
- D . a client ID
- E . a client secret