
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
SIMULATION
Lab Task
Task 7
You need to ensure that connections through an Azure Application Gateway named Homepage-AGW are inspected for malicious requests.
HOTSPOT
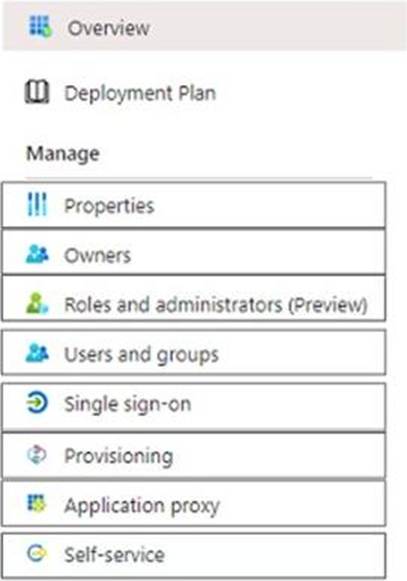
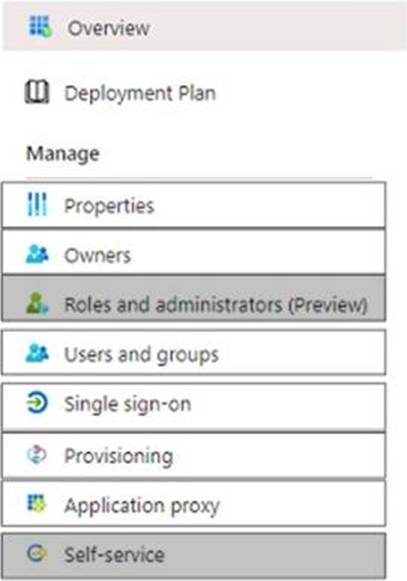
You have an Azure Active Directory (Azure AD) tenant that contains two users named User1 and
User2 and a registered app named App1.
You create an app-specific role named Role1.
You need to assign Role1 to User1 and enable User2 to request access to App1.
Which two settings should you modify? To answer select the appropriate settings in the answer area NOTE: Each correct selection is worth one pant.
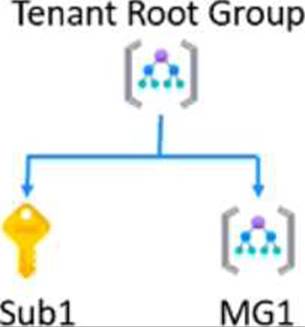
You have an Azure subscription named Sub1 that uses Microsoft Defender for Cloud.
You have the management group hierarchy shown in the following exhibit.
You create the definitions shown in the following table.
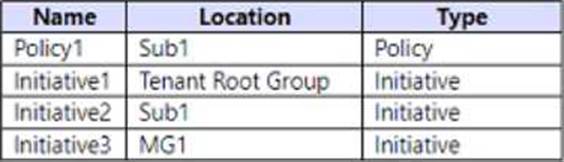
You need to use Defender for Cloud to add a security policy.
Which definitions can you use as a security policy?
- A . Policy1 only
- B . Policy1 and Initiative1 only
- C . Initiative1 and Initiative2 only
- D . Initiative1, Initiative2, and Initiatives only
- E . Policy1, Initiative1, Initiative2, and Initiative3
You have an Azure subscription that contains a SQL Server on Azure Virtual Machines instance named SQt1 and a Microsoft Sentinel workspace named Sentinel1.
You need to monitor security incidents on SQL1 by using Sentinel1.
What should you do first?
- A . On SQL1, enable SQL1 Server audit.
- B . On SQL1. install the Connected Machine agent for Azure Arc-enabled servers.
- C . From the Azure portal, create a Log Analytics workspace.
- D . From Sentinel1, enable VM insights.
HOTSPOT
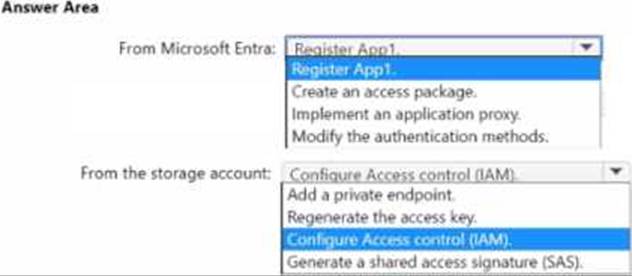
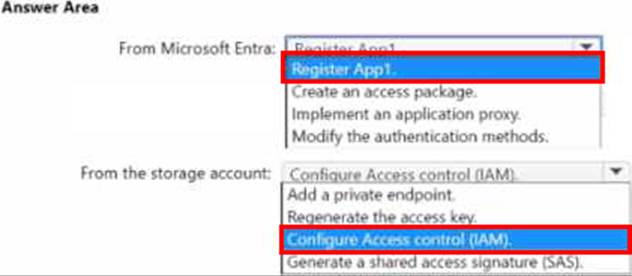
You have an Azure Storage account that contains a blob container named container! and a client application named App1. You need to enable App1 access to container1 by using Microsoft Entra authentication.
What should you do? lo answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that uses Microsoft Defender for Cloud.
You have an Amazon Web Service (AWS) account named AWS1 that is connected to defender for Cloud.
You need to ensure that AWS foundational Security Best Practices. The solution must minimize administrate effort.
What should do you in Defender for Cloud?
- A . Create a new customer assessment.
- B . Assign a built-in assessment.
- C . Assign a built-in compliance standard.
- D . Create a new custom standard.
HOTSPOT
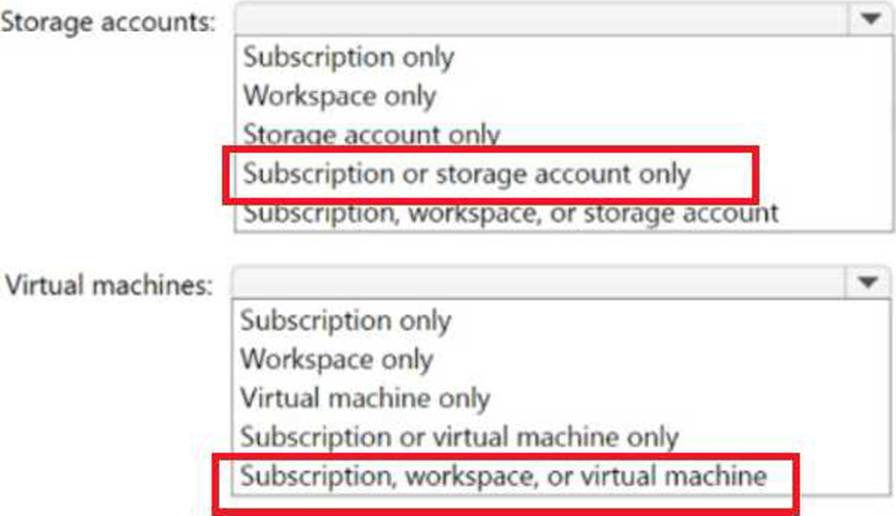
You have an Azure subscription named Sub1 that contains the resources shown in the following table.
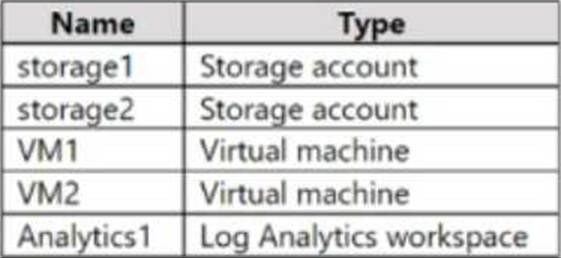
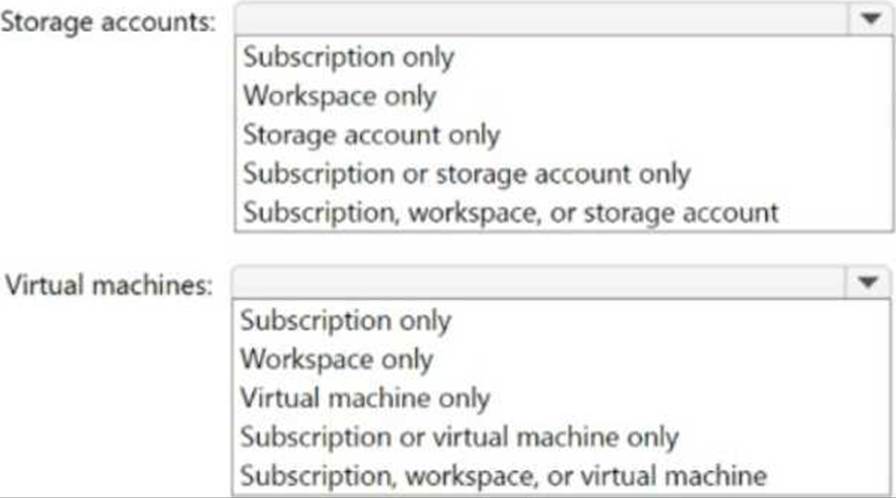
You need to enable Microsoft Defender for Cloud for storage accounts and virtual machines.
At which levels can you enable Defender for Cloud for the storage accounts and the virtual machines? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point
You have an Azure subscription that contains an Azure Active Directory (Azure AD) tenant and a user named User1.
The App registrations settings for the tenant are configured as shown in the following exhibit.
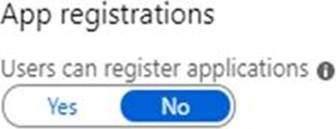
You plan to deploy an app named App1.
You need to ensure that User1 can register App1 in Azure AD. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A . App Configuration Data Owner for the subscription
- B . Managed Application Contributor for the subscription
- C . Cloud application administrator in Azure AD
- D . Application developer in Azure AD.
Your network contains an Active Directory forest named contoso.com. The forest contains a single domain.
You have an Azure subscription named Sub1 that is associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
You plan to deploy Azure AD Connect and to integrate Active Directory and the Azure AD tenant.
You need to recommend an integration solution that meets the following requirements:
Ensures that password policies and user logon restrictions apply to user accounts that are synced to the Tenant Minimizes the number of servers required for the solution.
Which authentication method should you include in the recommendation?
- A . federated identity with Active Directory Federation Services (AD FS)
- B . password hash synchronization with seamless single sign-on (SSO)
- C . pass-through authentication with seamless single sign-on (SSO)
You have 10 virtual machines on a single subnet that has a single network security group (NSG).
You need to log the network traffic to an Azure Storage account.
Which two actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . Install the Network Performance Monitor solution.
- B . Enable Azure Network Watcher.
- C . Enable diagnostic logging for the NSG.
- D . Enable NSG flow logs.
- E . Create an Azure Log Analytics workspace.