
Juniper JN0-637 Practice Exams
Last updated on Oct 21,2026- Exam Code: JN0-637
- Exam Name: Security, Professional (JNCIP-SEC)
- Certification Provider: Juniper
- Latest update: Oct 21,2026
Referring to the exhibit,
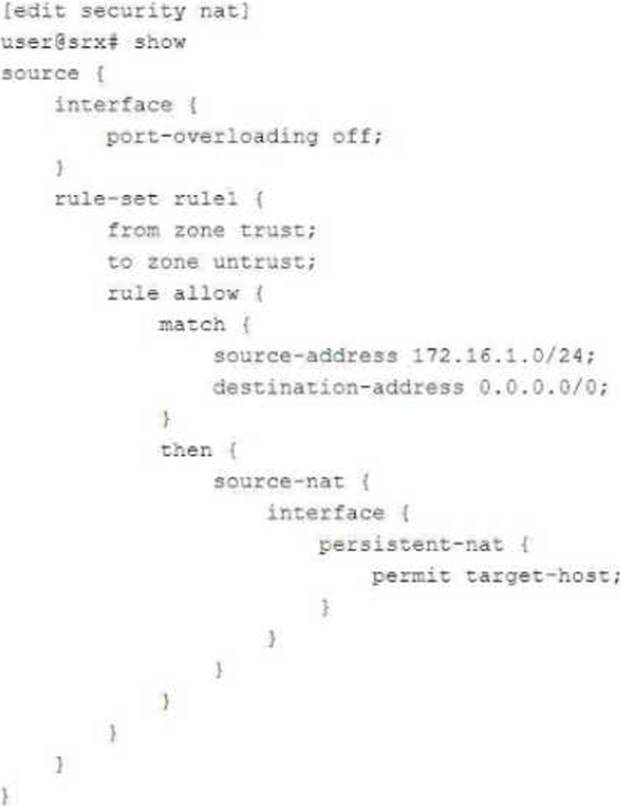
which two statements are correct about the NAT configuration? (Choose two.)
- A . Both the internal and the external host can initiate a session after the initial translation.
- B . Only a specific host can initiate a session to the reflexive address after the initial session.
- C . Any external host will be able to initiate a session to the reflexive address.
- D . The original destination port is used for the source port for the session.
You are deploying IPsec VPNs to securely connect several enterprise sites with ospf for dynamic routing. Some of these sites are secured by third-party devices not running Junos.
Which two statements are true for this deployment? (Choose two.)
- A . OSPF over IPsec can be used for intersite dynamic routing.
- B . Sites with overlapping address spaces can be supported.
- C . OSPF over GRE over IPsec is required to enable intersite dynamic routing
- D . Sites with overlapping address spaces cannot be supported.
You Implement persistent NAT to allow any device on the external side of the firewall to initiate traffic.
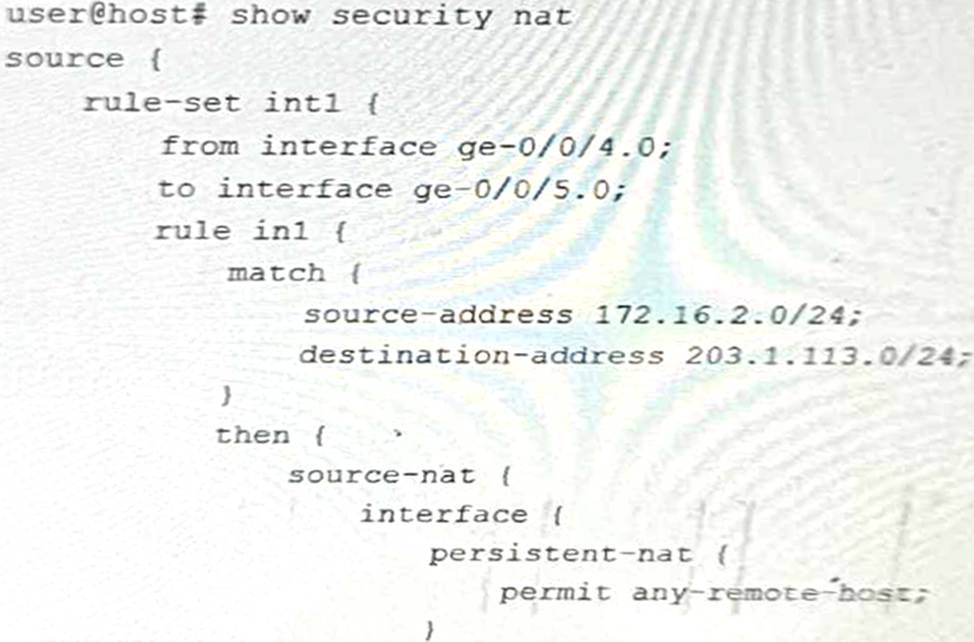
Referring to the exhibit, which statement is correct?
- A . The target-host parameter should be used instead of the any-remote-host parameter.
- B . The port-overloading parameter needs to be turned off in the NAT source interface configuration
- C . The target-host-port parameter should be used instead of the any-remote-host parameter
- D . The any-remote-host parameter does not support interface-based NAT and needs an IP pod to work.
You are configuring an interconnect logical system that is configured as a VPLS switch to allow two logical systems to communicate.
Which two parameters are required when configuring the logical tunnel interfaces? (Choose two.)
- A . Encapsulation ethernet must be used.
- B . The virtual tunnel interfaces should only be configured with two logical unit pairs per logical system interconnect.
- C . The logical tunnel interfaces should be configured with two logical unit pairs per logical system interconnect.
- D . Encapsulation ethernet-vpls must be used.
You are asked to create multiple virtual routers using a single SRX Series device. You must ensure that each virtual router maintains a unique copy of the routing protocol daemon (RPD) process.
Which solution will accomplish this task?
- A . Secure wire
- B . Tenant system
- C . Transparent mode
- D . Logical system
Which two statements are correct about the ICL in an active/active mode multinode HA environment? (Choose two.)
- A . The ICL is strictly a Layer 2 interface.
- B . The ICL uses a separate routing instance to communicate with remote multinode HA peers.
- C . The ICL traffic can be encrypted.
- D . The ICL is the local device management interface in a multinode HA environment.
You are asked to establish a hub-and-spoke IPsec VPN using an SRX Series device as the hub. All of the spoke devices are third-party devices.
Which statement is correct in this scenario?
- A . You must ensure that you are using aggressive mode when incorporating third-party devices as your spokes.
- B . You must statically configure the next-hop tunnel binding table entries for each of the third-party spoke devices.
- C . You must create a policy-based VPN on the hub device when peering with third-party devices.
- D . You must always peer using loopback addresses when using non-Junos devices as your spokes.
You have deployed a new site as shown in the exhibit. Hosts in the 10.10.10.0/24 network must access the DB1 server. The DB1 server must also have internet access the DB1 server encrypted.
Which two configuration statements will be required as part of the configuration on SRX1 to satisfy this requirement? (Choose two)
- A . set security macsec interfaces ge-0/0/1 connectivity association access-sw
- B . set protocols 12-learning global mode transpårent-bridge
- C . set security forwarding-options secure-wire access-sw interface ge-0/0/1.0
- D . set security macsec connectivity-association access-sw security-mode static-cak
You are attempting to ping the IP address that is assigned to the loopback interface on the SRX series device shown in the exhibit.
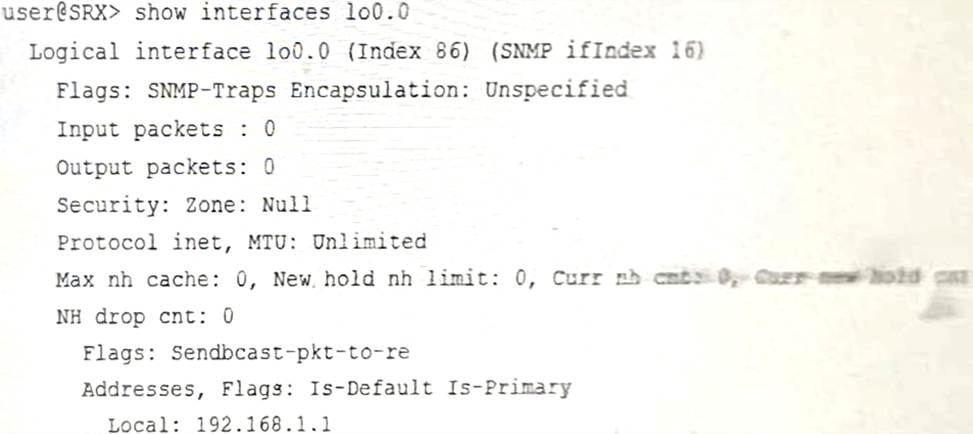
What is causing this problem?
- A . The loopback interface requires encapsulation.
- B . The loopback interface is not assigned to a security zone.
- C . The incorrect interface index ID is assigned to the loopback interface.
- D . The IP address on the loopback interface is a private address.