
Juniper JN0-637 Practice Exams
Last updated on Oct 21,2026- Exam Code: JN0-637
- Exam Name: Security, Professional (JNCIP-SEC)
- Certification Provider: Juniper
- Latest update: Oct 21,2026
A user reports that a specific application is not working properly. This application makes multiple connection to the server and must have the same address every time from a pool and this behavior needs to be changed.
What would solve this problem?
- A . Use STUN.
- B . Use DNS doctoring.
- C . Use the address-persistent parameter.
- D . Use the persistent-nat parameter.
A company has acquired a new branch office that has the same address space as one of its local networks, 192.168.100.0/24. The offices need to communicate with each other.
Which two NAT configurations will satisfy this requirement? (Choose two.)
- A . [edit security nat source]
user@OfficeA# show rule-set OfficeBtoA {
from zone OfficeB;
to zone OfficeA;
rule 1 {
match {
source-address 192.168.210.0/24;
destination-address 192.168.200.0/24;
}
then {
source-nat { interface; }
}
}
} - B . [edit security nat static]
user@OfficeA# show rule-set From-Office-B {
from interface ge-0/0/0.0;
rule 1 {
match {
destination-address 192.168.200.0/24;
}
then {
static-nat {
prefix { 192.168.100.0/24; }
}
}
}
} - C . [edit security nat static]
user@OfficeB# show rule-set From-Office-A {
from interface ge-0/0/0.0;
rule 1 {
match {
destination-address 192.168.210.0/24;
}
then {
static-nat {
prefix { 192.168.100.0/24; }
}
}
}
} - D . [edit security nat source]
user@OfficeB# show rule-set OfficeAtoB {
from zone OfficeA;
to zone OfficeB;
rule 1 {
match {
source-address 192.168.200.0/24;
destination-address 192.168.210.0/24;
}
then {
source-nat { interface; }
}
}
}
Exhibit:
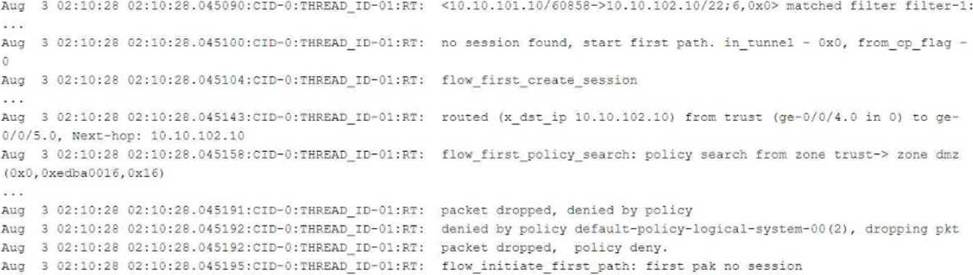
Referring to the flow logs exhibit, which two statements are correct? (Choose two.)
- A . The packet is dropped by the default security policy.
- B . The packet is dropped by a configured security policy.
- C . The data shown requires a traceoptions flag of host-traffic.
- D . The data shown requires a traceoptions flag of basic-datapath.
Referring to the exhibit, you are assigned the tenantSYS1 user credentials on an SRX series device.
In this scenario, which two statements are correct? (Choose two.)
- A . When you log in to the device, you will be located at the operational mode of the main system hierarchy.
- B . When you log in to the device, you will be located at the operational mode of the Tenant.SY51 logical system hierarchy.
- C . When you log in to the device, you will be permitted to view only the routing tables for the Tenant SYS1 logical system.
- D . When you log in to the device, you will be permitted to view all routing tables available on the on an SYS1 Series device.
Exhibit:
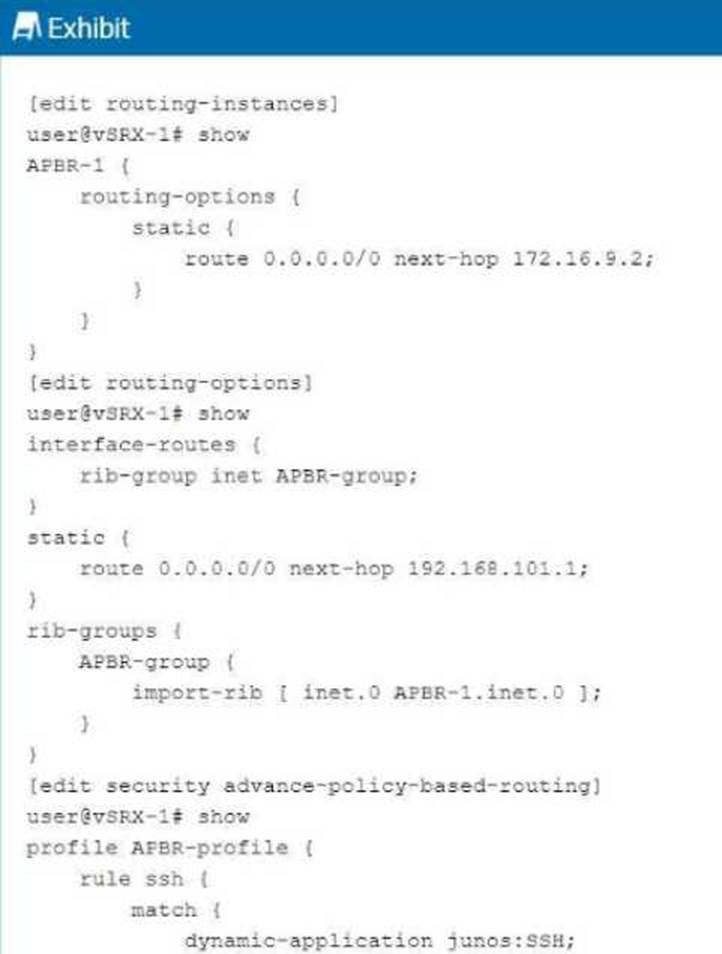
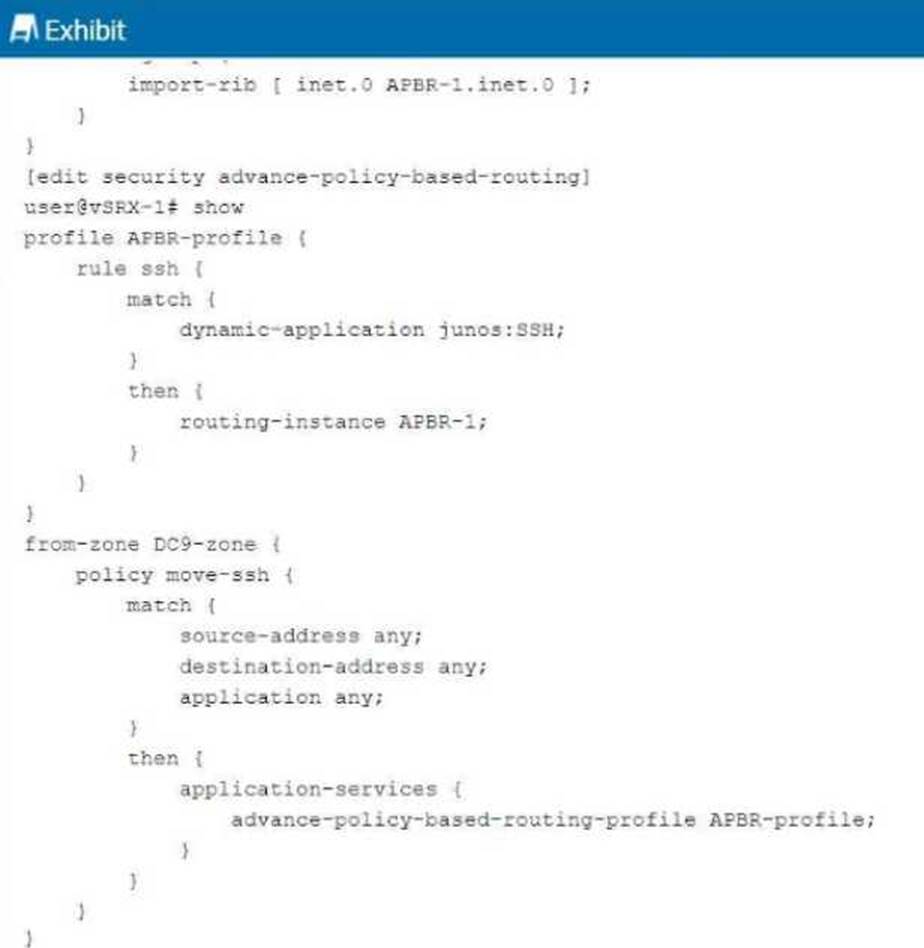
You are having problems configuring advanced policy-based routing.
What should you do to solve the problem?
- A . Apply a policy to the APBR RIB group to only allow the exact routes you need.
- B . Change the routing instance to a forwarding instance.
- C . Change the routing instance to a virtual router instance.
- D . Remove the default static route from the main instance configuration.
Click the Exhibit button.
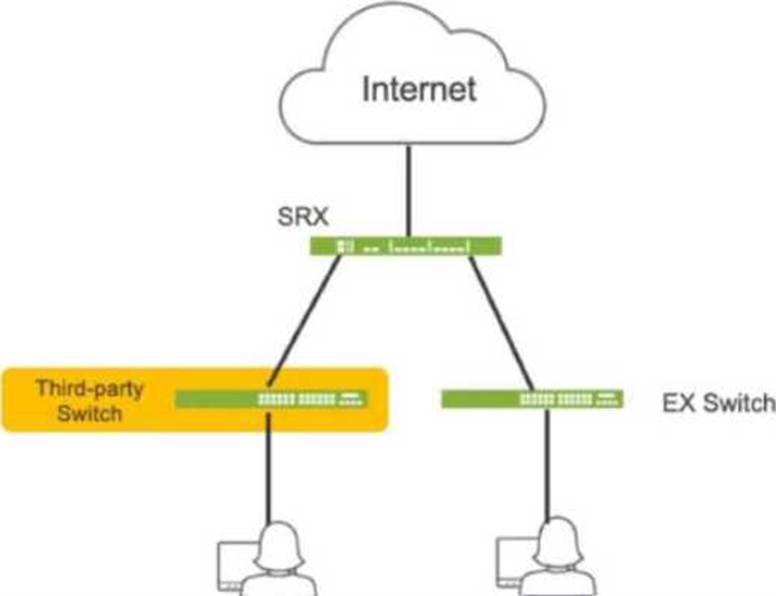
Referring to the exhibit, which three actions do you need to take to isolate the hosts at the switch port level if they become infected with malware? (Choose three.)
- A . Enroll the SRX Series device with Juniper ATP Cloud.
- B . Use a third-party connector.
- C . Deploy Security Director with Policy Enforcer.
- D . Configure AppTrack on the SRX Series device.
- E . Deploy Juniper Secure Analytics.
You are deploying a large-scale VPN spanning six sites.
You need to choose a VPN technology that satisfies the following requirements:
All sites must have secure reachability to all other sites.
New spoke sites can be added without explicit configuration on the hub site.
All spoke-to-spoke communication must traverse the hub site.
Which VPN technology will satisfy these requirements?
- A . ADVPN
- B . Group VPN
- C . Secure Connect VPN
- D . AutoVPN
You have a multinode HA default mode deployment and the ICL is down.
In this scenario, what are two ways that the SRX Series devices verify the activeness of their peers? (Choose two.)
- A . Custom IP addresses may be configured for the activeness probe.
- B . Fabric link heartbeats are used to verify the activeness of the peers.
- C . Each peer sends a probe with the virtual IP address as the destination IP address.
- D . Each peer sends a probe with the virtual IP address as the source IP address and the upstream router as the destination IP address.
Referring to the exhibit, you are attempting to set up a remote access VPN on your SRX series devices.
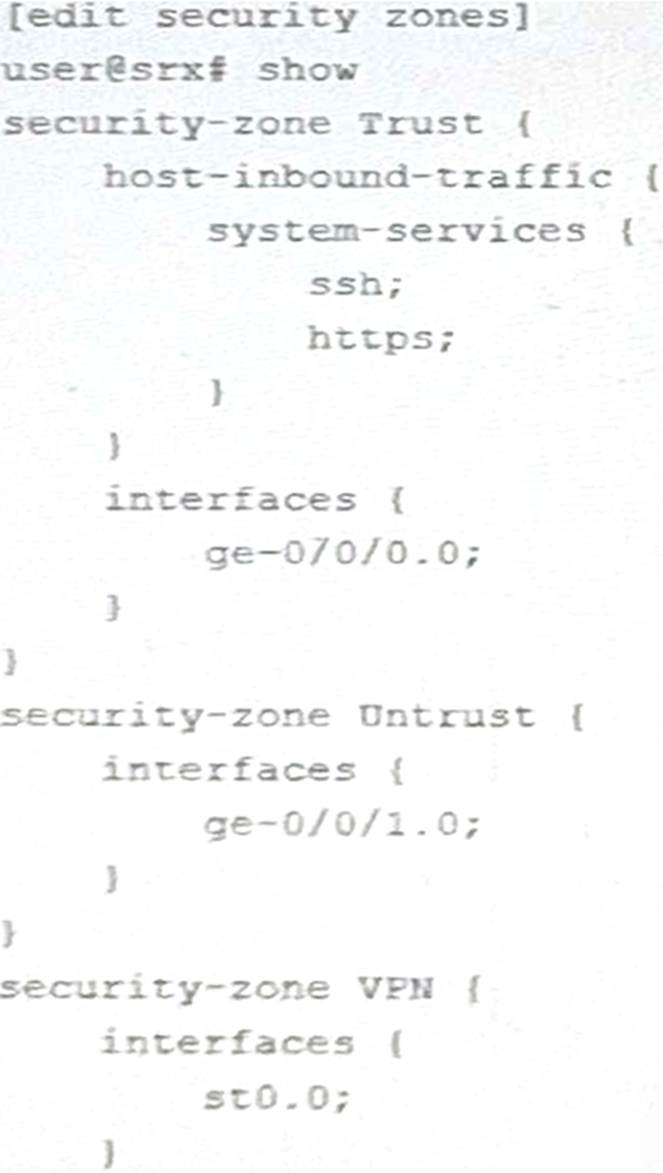
However you are unsure of which system services you should allow and in which zones they should be allowed to correctly finish the remote access VPN configuration Which two statements are correct? (Choose two.)
- A . You should add the host-inbound-traffic system-service ike statement to the Untrust zone.
- B . You should add the host-inbound-traffic system-service ike statement to the VPN zone.
- C . You should add the host-inbound-traffic system-service tcp-encap statement to the Untrust zone
- D . You should add the host-inbound-traffic system-service tcp-encap statement to the VPN zone
Referring to the exhibit,
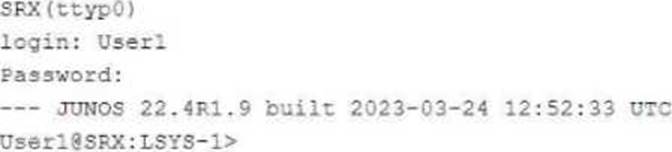
which two statements about User1 are true? (Choose two.)
- A . User1 has access to the configuration specific to their assigned logical system.
- B . User1 is logged in to logical system LSYS-1.
- C . User1 can add logical units to an interface that a primary administrator has not previously assigned.
- D . User1 can view outputs from other user logical systems.