
Juniper JN0-637 Practice Exams
Last updated on Oct 21,2026- Exam Code: JN0-637
- Exam Name: Security, Professional (JNCIP-SEC)
- Certification Provider: Juniper
- Latest update: Oct 21,2026
Click the Exhibit button.
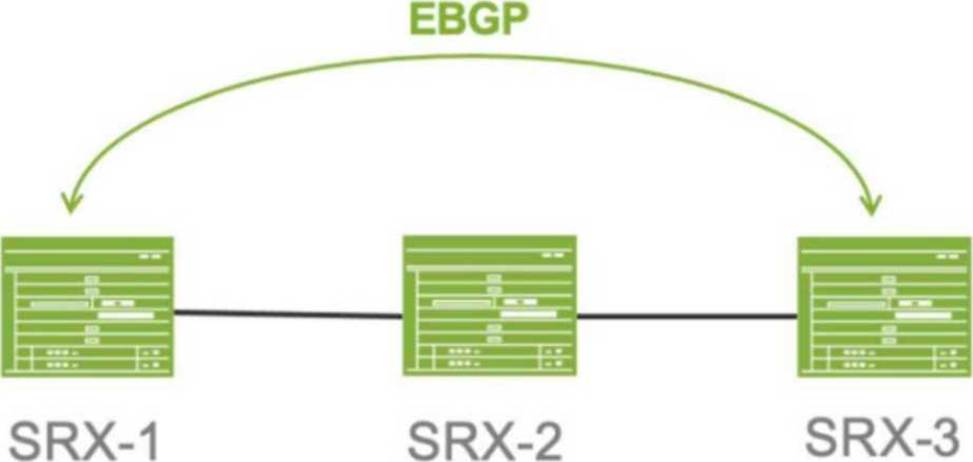
Referring to the exhibit. SRX-1 and SRX-3 have to be connected using EBGP. The BGP configuration on SRX-1 and SRX-3 is verified and correct.
Which configuration on SRX-2 would establish an EBGP connection successfully between SRX-1 and SRX-3?
- A . The host-inbound-traffic statements do not allow EBGP traffic to traverse SRX-2.
- B . The security policy to allow SRX-1 and SRX-3 to communicate on TCP port 79 should be configured.
- C . The security policy to allow SRX-1 and SRX-3 to communicate on TCP port 169 should be configured.
- D . The security policy to allow SRX-1 and SRX-3 to communicate on TCP port 179 should be configured.
You are asked to see if your persistent NAT binding table is exhausted.
Which show command would you use to accomplish this task?
- A . show security nat source persistent-nat-table summary
- B . show security nat source summary
- C . show security nat source pool all
- D . show security nat source persistent-nat-table all
Which two statements about policy enforcer and the forescout integration are true? (Choose two)
- A . 802.1X authenticated devices are supported.
- B . 802.1X authenticated devices are not supported.
- C . A Forescout CounterACT agent must be installed on third-party devices
- D . A Forescout CounterACT agent is agentless and does not need to be installed on third-party device
What are three configurable monitor components for a service redundancy group? (Choose two)
- A . Interface
- B . BFD
- C . hardware alarm
- D . IP
- E . ARP
Exhibit:
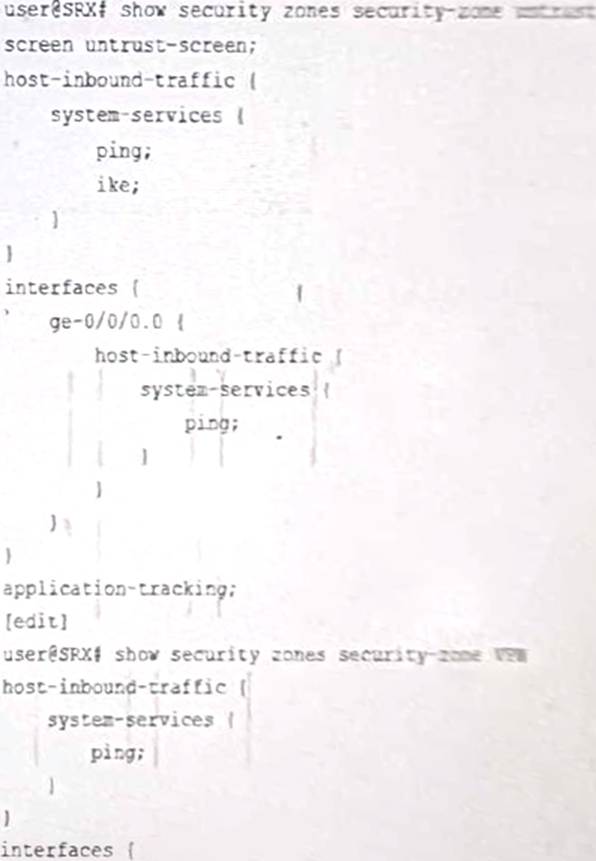
The Ipsec VPN does not establish when the peer initiates, but it does establish when the SRX series device initiates.
Referring to the exhibit, what will solve this problem?
- A . IKE needs to be added for the host-inbound traffic on the VPN zone.
- B . The screen configuration on the untrust zone needs to be modified.
- C . IKE needs to be added to the host-inbound traffic directly on the ge-0/0/0 interface.
- D . Application tracking on the untrust zone needs to be removed.
Exhibit:
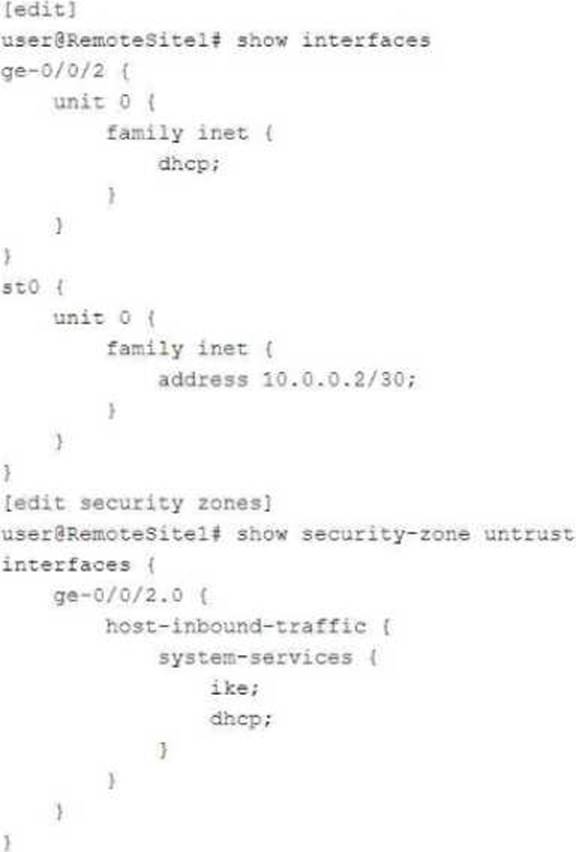
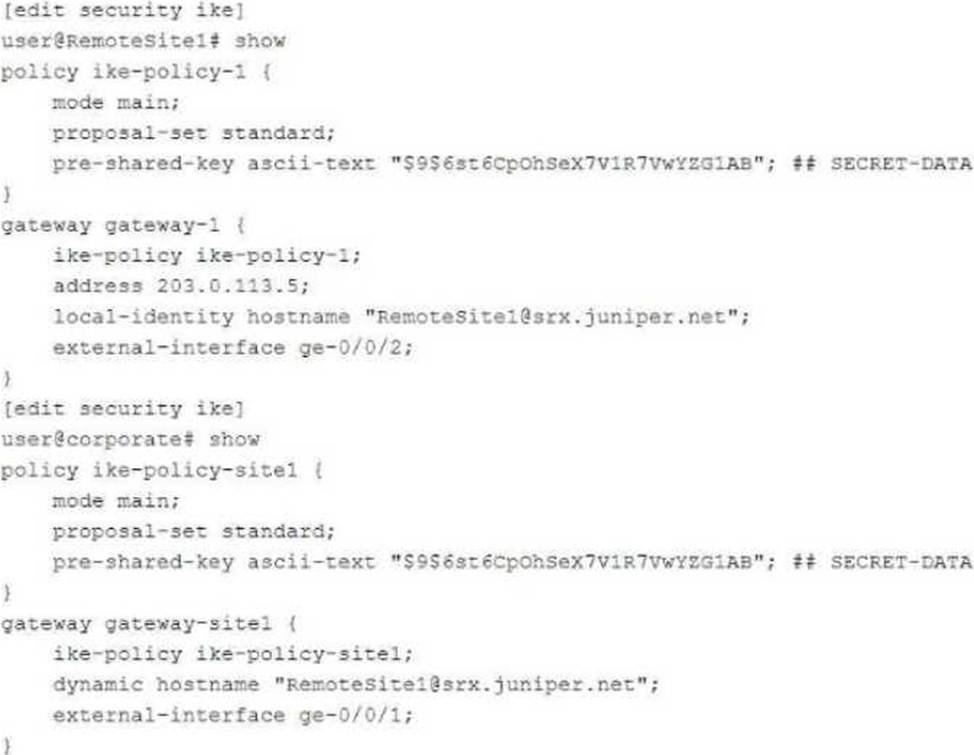
You are troubleshooting a new IPsec VPN that is configured between your corporate office and the RemoteSite1 SRX Series device. The VPN is not currently establishing. The RemoteSite1 device is being assigned an IP address on its gateway interface using DHCP.
Which action will solve this problem?
- A . On the RemoteSite1 device, change the IKE gateway external interface to st0.0.
- B . On both devices, change the IKE version to use version 2 only.
- C . On both devices, change the IKE policy proposal set to basic.
- D . On both devices, change the IKE policy mode to aggressive.
You need to set up source NAT so that external hosts can initiate connections to an internal device, but only if a connection to the device was first initiated by the internal device.
Which type of NAT solution provides this functionality?
- A . Address persistence
- B . Persistent NAT with any remote host
- C . Persistent NAT with target host
- D . Static NAT
Which two statements are true regarding NAT64? (Choose two.)
- A . An SRX Series device should be in flow-based forwarding mode for IPv4.
- B . An SRX Series device should be in packet-based forwarding mode for IPv4.
- C . An SRX Series device should be in packet-based forwarding mode for IPv6.
- D . An SRX Series device should be in flow-based forwarding mode for IPv6.
Which two statements are correct about advanced policy-based routing?
- A . It can use the application system cache to route traffic.
- B . The associated routing instance should be configured as a virtual router instance.
- C . It cannot use the application system cache to route traffic.
- D . The associated routing instance should be configured as a forwarding instance.
You are asked to connect two hosts that are directly connected to an SRX Series device. The traffic should flow unchanged as it passes through the SRX, and routing or switch lookups should not be performed. However, the traffic should still be subjected to security policy checks.
What will provide this functionality?
- A . MACsec
- B . Mixed mode
- C . Secure wire
- D . Transparent mode