
Fortinet NSE5_FSM-6.3 Practice Exams
Last updated on Oct 21,2026- Exam Code: NSE5_FSM-6.3
- Exam Name: Fortinet NSE 5 - FortiSIEM 6.3
- Certification Provider: Fortinet
- Latest update: Oct 21,2026
Refer to the exhibit.
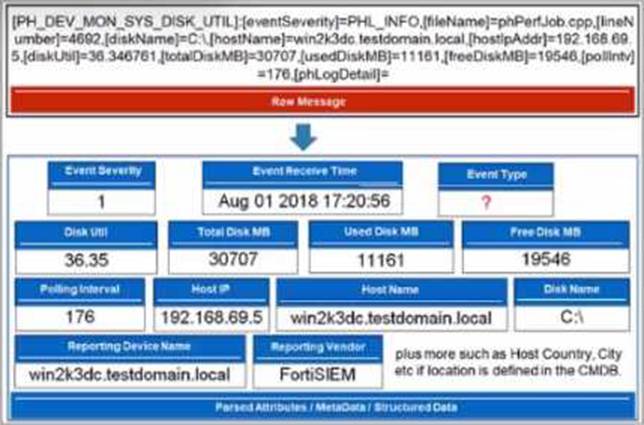
Which value will FortiSIEM use to populate the Event Type field?
- A . PHL_INFO
- B . phPerfJob
- C . PH_DSV_MON_SYS_DISK_UTIL
- D . diskUtil
A
Explanation:
Event Type Population: In FortiSIEM, the Event Type field is populated based on specific identifiers within the raw message or event log.
Raw Message Analysis: The exhibit shows a raw message with various components, including PH_DEV_MON_SYS_DISK_UTIL, PHL_INFO, phPerfJob, and diskUtil.
Primary Event Identifier: The PH_DEV_MON_SYS_DISK_UTIL at the beginning of the raw message is the primary identifier for the event type. It categorizes the type of event, in this case, a system disk utilization monitoring event.
Event Type Field: FortiSIEM uses this primary identifier to populate the Event Type field, providing a clear categorization of the event.
Reference: FortiSIEM 6.3 User Guide, Event Processing and Event Types section, details how event types are identified and populated in the system.
Which two FortiSIEM components work together to provide real-time event correlation?
- A . Supervisor and worker
- B . Collector and Windows agent
- C . Worker and collector
- D . Supervisor and collector
C
Explanation:
FortiSIEM Architecture: The FortiSIEM architecture includes several components such as Supervisors, Workers, Collectors, and Agents, each playing a distinct role in the SIEM ecosystem.
Real-Time Event Correlation: Real-time event correlation is a critical function that involves analyzing and correlating incoming events to detect patterns indicative of security incidents or operational issues.
Role of Supervisor and Worker:
Supervisor: The Supervisor oversees the entire FortiSIEM system, coordinating the processing and analysis of events.
Worker: Workers are responsible for processing and correlating the events received from Collectors and Agents.
Collaboration for Correlation: Together, the Supervisor and Worker components perform real-time event correlation by distributing the load and ensuring efficient processing of events to identify incidents in real-time.
Reference: FortiSIEM 6.3 User Guide, Event Correlation and Processing section, details how the Supervisor and Worker components collaborate for real-time event correlation.
Which command displays the Linux agent status?
- A . Service fsm-linux-agent status
- B . Service Ao-linux-agent status
- C . Service fortisiem-linux-agent status
- D . Service linux-agent status
C
Explanation:
Linux Agent in FortiSIEM: The FortiSIEM Linux agent is responsible for collecting logs and metrics from Linux devices and forwarding them to the FortiSIEM system.
Command for Checking Status: The correct command to check the status of the FortiSIEM Linux agent is service fortisiem-linux-agent status.
This command queries the status of the FortiSIEM Linux agent service, showing whether it is running, stopped, or encountering issues.
Usage: Properly checking the agent status helps ensure that data collection from Linux devices is functioning as expected.
Reference: FortiSIEM 6.3 User Guide, Linux Agent Installation and Management section, which includes commands for managing the Linux agent.
Consider the storage of anomaly baseline date that is calculated for different parameters.
Which database is used for storing this data?
- A . Event DB
- B . Profile DB
- C . SVNDB
- D . CMDB
D
Explanation:
Anomaly Baseline Data: Anomaly baseline data refers to the statistical profiles and baselines calculated for various parameters to detect deviations indicative of potential security incidents. Profile DB: The Profile DB is specifically designed to store such baseline data in FortiSIEM. Purpose: It maintains statistical profiles for different monitored parameters to facilitate anomaly detection.
Usage: This data is used by FortiSIEM to compare real-time metrics against the established baselines to identify anomalies.
Reference: FortiSIEM 6.3 User Guide, Database Architecture section, which describes the different databases used in FortiSIEM and their purposes, including the Profile DB for storing anomaly baseline
data.
FortiSIEM is deployed in disaster recovery mode.
When disaster strikes, which two tasks must you perform manually to achieve a successful disaster recovery operation? (Choose two.)
- A . Promote the secondary workers to the primary rotes using the phSecworker2priworker command.
- B . Promote the secondary supervisor to the primary role using the phSecondary2primary command.
- C . Change the DNS configuration to ensure that users, devices, and collectors log in to the secondary FortiSIEM.
- D . Change the configuration for shared storage NFS configured for EventDB to the secondary FortiSIEM.
A, C
Explanation:
Disaster Recovery Mode: FortiSIEM’s disaster recovery (DR) mode ensures that there is a backup system ready to take over in case the primary system fails.
Manual Tasks for DR Operation: In the event of a disaster, certain tasks must be performed manually to ensure a smooth transition to the secondary system.
Promoting the Secondary Supervisor:
Use the command phSecondary2primary to promote the secondary supervisor to the primary role. This command reconfigures the secondary supervisor to take over as the primary supervisor, ensuring continuity in management and coordination. Changing DNS Configuration:
Update the DNS configuration to direct all users, devices, and collectors to the secondary FortiSIEM instance. This ensures that all components in the environment can communicate with the newly promoted primary supervisor without manual reconfiguration of individual devices.
Reference: FortiSIEM 6.3 Administration Guide, Disaster Recovery section, provides detailed steps on promoting the secondary supervisor and updating DNS configurations during a disaster recovery operation.
Which process converts raw log data to structured data?
- A . Data classification
- B . Data validation
- C . Data parsing
- D . Data enrichment
C
Explanation:
Raw Log Data: When devices send logs to FortiSIEM, the data arrives in a raw, unstructured format.
Data Parsing Process: The process that converts this raw log data into a structured format is known as data parsing.
Data Parsing: This involves extracting relevant fields from the raw log entries and organizing them into a structured format, making the data usable for analysis, reporting, and correlation.
Significance of Structured Data: Structured data is essential for effective event correlation, alerting, and generating meaningful reports.
Reference: FortiSIEM 6.3 User Guide, Data Parsing section, which details how raw log data is transformed into structured data through parsing.
An administrator is configuring FortiSIEM to discover network devices and receive syslog from network devices.
Which statement is correct?
- A . FortiSIEM uses privileged credentials to tog in to devices and make network configuration changes.
- B . FortiSIEM automatically configures network devices to send syslog using the auto log discovery process.
- C . FortiSIEM automatically configures network devices to send syslog using the GUI discovery process
- D . Syslog configuration must be done manually on devices by the network administrator.
D
Explanation:
Syslog Configuration in FortiSIEM: For FortiSIEM to receive syslog messages from network devices, those devices need to be properly configured to send syslog data to FortiSIEM.
Manual Configuration Requirement: FortiSIEM does not automatically configure network devices to send syslog messages. Instead, this configuration must be performed manually by the network administrator.
Process Overview: The network administrator must access each device and set up the syslog parameters to direct log data to the FortiSIEM collector’s IP address.
Discovery Process: While FortiSIEM can discover network devices using SNMP, WMI, and other protocols, the configuration of syslog on these devices is beyond its scope and requires manual intervention.
Reference: FortiSIEM 6.3 User Guide, Device Configuration and Syslog Integration sections, which explain the requirements and steps for setting up syslog forwarding on network devices.
What are the four categories of incidents?
- A . Devices, users, high risk, and low risk
- B . Performance, devices, high risk, and low risk
- C . Performance, availability, security, and change
- D . Security, change, high risk, and low risk
C
Explanation:
Incident Categories in FortiSIEM: Incidents in FortiSIEM are categorized to help administrators quickly identify and prioritize the type of issue.
Four Main Categories:
Performance: Incidents related to the performance of devices and applications, such as high CPU usage or memory utilization.
Availability: Incidents affecting the availability of services or devices, such as downtime or connectivity issues.
Security: Incidents related to security events, such as failed login attempts, malware detection, or unauthorized access.
Change: Incidents triggered by changes in the configuration or state of devices, such as new software installations or configuration modifications.
Importance of Categorization: These categories help in the efficient management and response to different types of incidents, allowing for better resource allocation and quicker resolution.
Reference: FortiSIEM 6.3 User Guide, Incident Management section, which details the different categories of incidents and their significance.
How is a subparttern for a rule defined?
- A . Filters Aggregation. Group By definition
- B . Filters Group By definitions. Threshold
- C . Filters Threshold Time Window definitions
- D . Filters Aggregation Time Window definitions
D
Explanation:
Rule Subpattern Definition: In FortiSIEM, a subpattern within a rule is used to define specific conditions and criteria that must be met for the rule to trigger an incident or alert.
Components of a Subpattern: The subpattern includes the following elements:
Filters: Criteria to filter the events that the rule will evaluate.
Aggregation: Conditions that define how events should be aggregated or grouped for analysis. Time Window Definitions: Specifies the time frame over which the events will be evaluated to determine if the rule conditions are met.
Together, these components allow the system to efficiently and accurately detect patterns of interest within the event data.
Reference: FortiSIEM 6.3 User Guide, Rules and Patterns section, which explains the structure and configuration of rule subpatterns, including the use of filters, aggregation, and time window definitions.
An administrator defines SMTP as a critical process on a Linux server.
It the SMTP process is stopped. FortiSIEM will generate a critical event with which event type?
- A . Postfix-Mail-Stop
- B . PH_DEV_MON_PROC_STOP
- C . PH_DEV_MON_SMTP_STOP
- D . Generic_SMTP_Procoss_Exit
B
Explanation:
Process Monitoring in FortiSIEM: FortiSIEM can monitor critical processes on managed devices, such as an SMTP process on a Linux server.
Event Generation: When a critical process stops, FortiSIEM generates an event to alert administrators.
Event Types: Specific event types correspond to different monitored conditions. For a stopped process, the event type PH_DEV_MON_PROC_STOP is used.
Reasoning: The name PH_DEV_MON_PROC_STOP (Device Monitoring Process Stop) is a generic event type used by FortiSIEM to indicate that any monitored process, including SMTP, has stopped.
Reference: FortiSIEM 6.3 User Guide, Event Types section, explains the predefined event types and their usage in different monitoring scenarios.