
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
Which two configuration commands change the default behavior for content-inspected traffic while FortiGate is in conserve mode? (Choose two.)
- A . set av-failopen off
- B . set av-failopen pass
- C . set fail-open enable
- D . set ips fail-open disable
Refer to the exhibits, which show the configuration on FortiGate and partial session information for internet traffic from a user on the internal network.
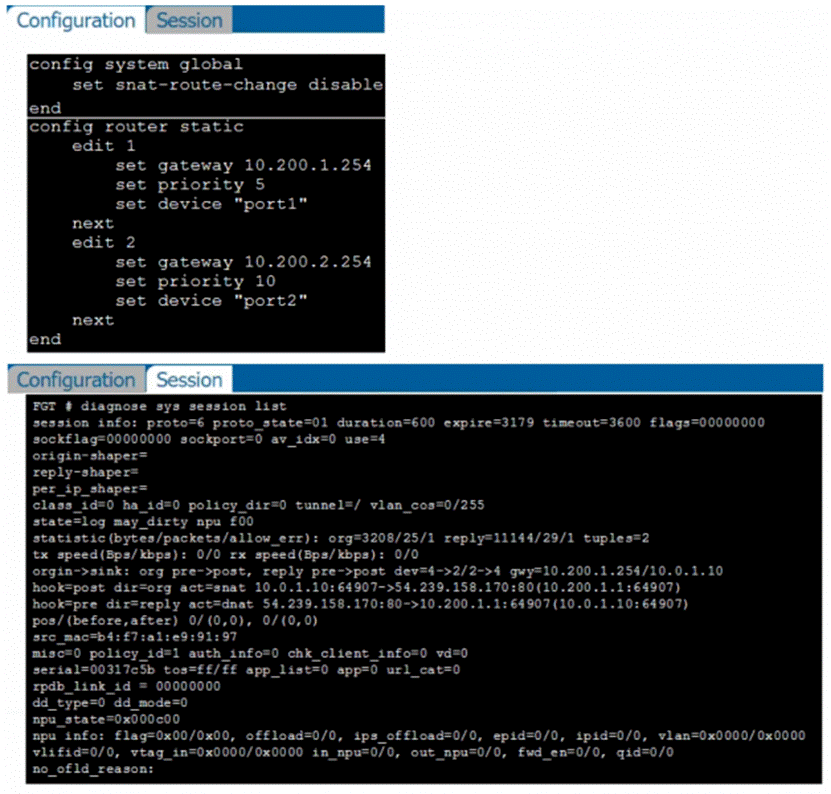
If the priority on route ID 2 were changed from 10 to 0, what would happen to traffic matching that user session?
- A . The session would remain in the session table, but its traffic would now egress from both port1 and port2.
- B . The session would remain in the session table, and its traffic would egress from port2.
- C . The session would be deleted, and the client would need to start a new session.
- D . The session would remain in the session table, and its traffic would egress from port1.
A company’s users on an IPsec VPN between FortiGate A and B have experienced intermittent issues since implementing VXLAN. The administrator suspects that packets exceeding the 1500-byte default MTU are causing the problems.
In which situation would adjusting the interface’s maximum MTU value help resolve issues caused by protocols that add extra headers to IP packets?
- A . Adjust the MTU on interfaces only if FortiGate has the FortiGuard enterprise bundle, which allows MTU modification.
- B . Adjust the MTU on interfaces in all FortiGate devices that support the latest family of Fortinet SPUs: NP7, CP9 and SP5.
- C . Adjust the MTU on interfaces in controlled environments where all devices along the path allow MTU interface changes.
- D . Adjust the MTU on interfaces only in wired connections like PPPoE, optic fiber, and ethernet cable.
C
Explanation:
When usingIPsec VPNsandVXLAN, additional headers are added to packets, which can exceed thedefault 1500-byte MTU. This can lead tofragmentation issues, dropped packets, or degraded performance.
To resolve this, theMTU (Maximum Transmission Unit) should be adjustedonly if all devices in the network path support it. Otherwise, some devices may still drop or fragment packets, leading to continued issues.
Why adjusting MTU helps:
#VXLAN adds a 50-byte overheadto packets.
#IPsec adds additional encapsulation (ESP, GRE, etc.), increasing the packet size.
# If packets exceed the MTU, they may befragmented or dropped, causing intermittent connectivity issues.
# Lowering the MTU on interfaces ensurespackets stay within the supported size limitacross all network devices.
What is an OSPF area border router?
- A . A router with interfaces in multiple OSPF areas.
- B . A router with all its interfaces in the backbone area.
- C . A router that is redistributing connected subnets into the OSPF network.
- D . A router that is redistributing non-OSPF routes into the OSPF network.
Refer to the exhibit, which shows a revision history window in the FortiManager device layer.
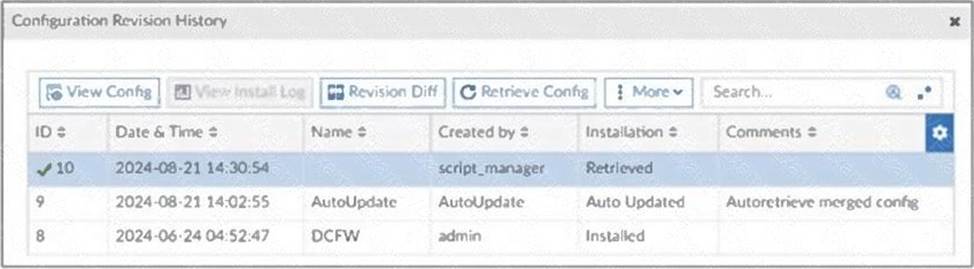
The IT team is trying to identify the administrator responsible for the most recent update in the FortiGate device database.
Which conclusion can you draw about this scenario?
- A . This retrieved process was automatically triggered by a Remote FortiGate Directly (via CLI) script.
- B . The user script_manager is an API user from the Fortinet Developer Network (FDN) retrieving a configuration.
- C . To identify the user who created the event, check it on the Configuration and Installation widget on FortiGate within the FortiManager device layer.
- D . Find the user in the FortiManager system logs and use the type=script command to find the administrator user in the user field.
D
Explanation:
TheConfiguration Revision Historywindow inFortiManagershows that the most recent configuration change (ID 10) was created byscript_managerwith the actionRetrieved.
Sincescript_manageris a system-level script execution user, the IT team needs to findwho actually triggered this script. This can be done by:
# Checking theFortiManager system logsforscript execution events.
# Using thetype=scriptfilter to locate the administrator associated with the script execution.
Exhibits:
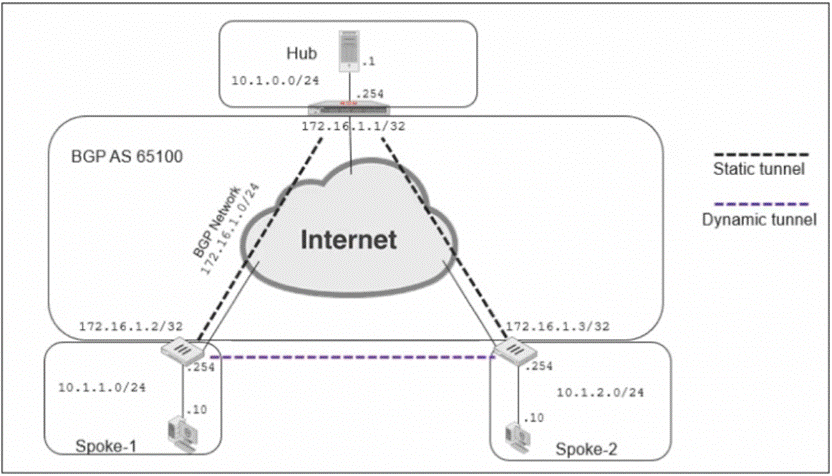
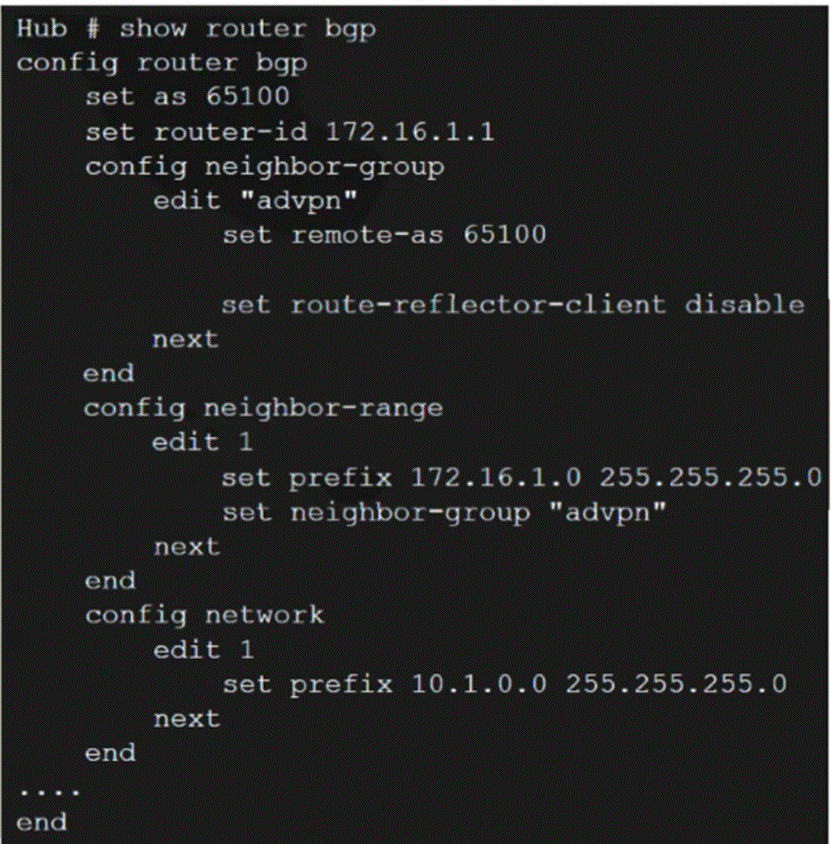
Refer to the exhibits, which contain the network topology and BGP configuration for a hub.
An administrator is trying to configure ADVPN with a hub-spoke VPN setup using iBGP. All the VPNs are up and connected to the hub. The hub is receiving route information from both spokes over iBGP; however, the spokes are not receiving route information from each other.
What change must the administrator make to the hub BGP configuration so that the routes learned by one spoke are forwarded to the other spokes?
- A . Configure the hub as a route reflector client.
- B . Change the router id to 10.1.0.254.
- C . Configure an individual neighbor and remove neighbor-range configuration.
- D . Make the configuration of remote-as different from the configuration of local-as.
Which two statements about an auxiliary session are true? (Choose two.)
- A . With the auxiliary session setting enabled, ECMP traffic is accelerated to the NP6 processor.
- B . With the auxiliary session setting disabled, for each traffic path, FortiGate will use the same auxiliary session.
- C . With the auxiliary session disabled, only auxiliary sessions will be offloaded.
- D . With the auxiliary session setting enabled, two sessions will be created in case of routing change.
What are two impacts on applications if adjusting the TCP Maximum Segment Size (MSS) on FortiGate? (Choose two.)
- A . The MSS configuration is prone to errors since it requires a thorough understanding of the network path.
- B . The packet count increases adding unnecessary TCP headers when the MSS value is increased.
- C . The overall data throughput is decreased when there is a decrease in MSS value.
- D . The network efficiency improves when there is a decrease in MSS value.
Which of the following steps are executed to get antivirus and IPS updates using the pull method? (Choose three.)
- A . FortiGate starts sending rating queries to one of the servers in the list.
- B . FortiGate registers its public IP address in FortiGuard.
- C . FortiGate gets a list of server IP addresses that can be contacted.
- D . FortiGate contacts DNS to resolve update.fortiguard.net.
- E . FortiGate periodically queries for pending updates.
Examine the output from the ‘diagnose vpn tunnel list’ command shown in the exhibit; then answer the question below.
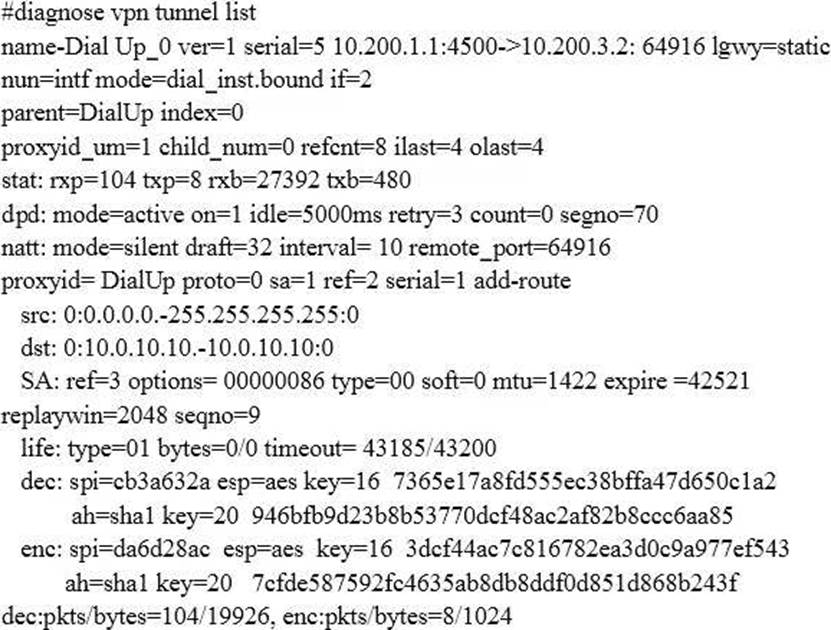
Which command can be used to sniffer the ESP traffic for the VPN DialUP_0?
- A . diagnose sniffer packet any ‘port 500’
- B . diagnose sniffer packet any ‘esp’
- C . diagnose sniffer packet any ‘host 10.0.10.10’
- D . diagnose sniffer packet any ‘port 4500’