
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
Examine the output of the ‘diagnose ips anomaly list’ command shown in the exhibit; then answer the question below.
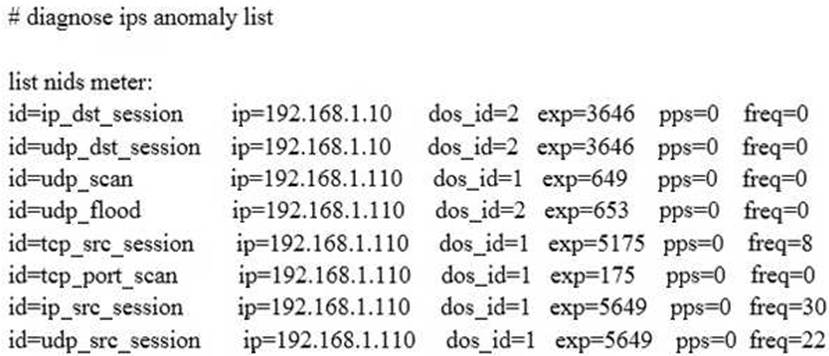
Which IP addresses are included in the output of this command?
- A . Those whose traffic matches a DoS policy.
- B . Those whose traffic matches an IPS sensor.
- C . Those whose traffic exceeded a threshold of a matching DoS policy.
- D . Those whose traffic was detected as an anomaly by an IPS sensor.
Refer to the exhibit, which shows a partial web filter profile configuration.
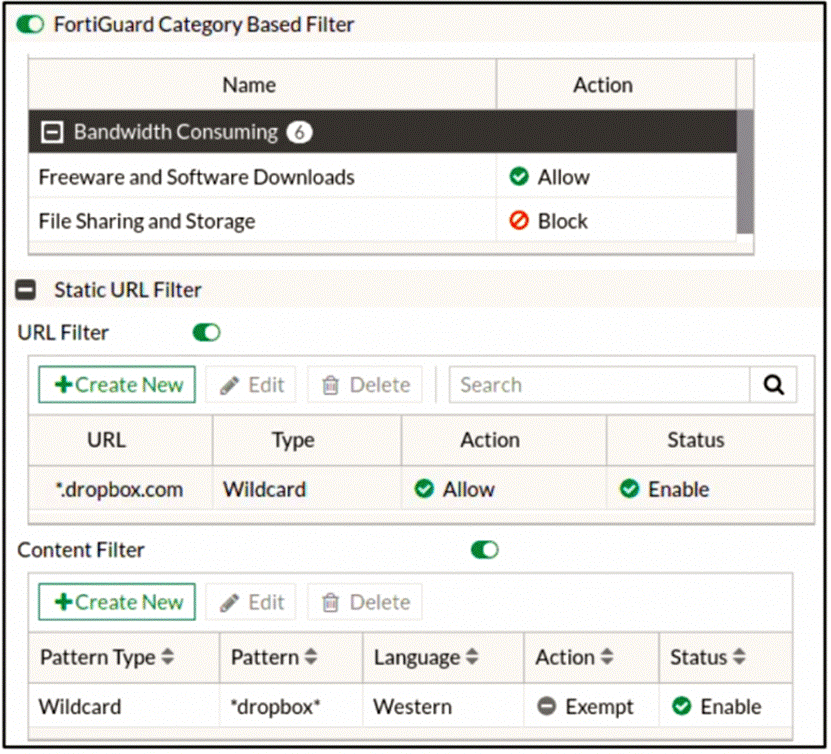
Which action will FortiGate take if a user attempts to access www.dropbox.com, which is categorized as File Sharing and Storage?
- A . FortiGate will block the connection, based on the FortiGuard category based filter configuration.
- B . FortiGate will block the connection as an invalid URL.
- C . FortiGate will exempt the connection, based on the Web Content Filter configuration.
- D . FortiGate will allow the connection, based onthe URL Filter configuration.
When a FortiLink interface is configured on a FortiGate, which VLAN is typically set as the default allowed VLAN on all connected FortiSwitch ports?
- A . Sniffer VLAN
- B . Camera VLAN
- C . Quarantine VLAN
- D . Management VLAN
Refer to the exhibit, which shows an enterprise network connected to an internet service provider.
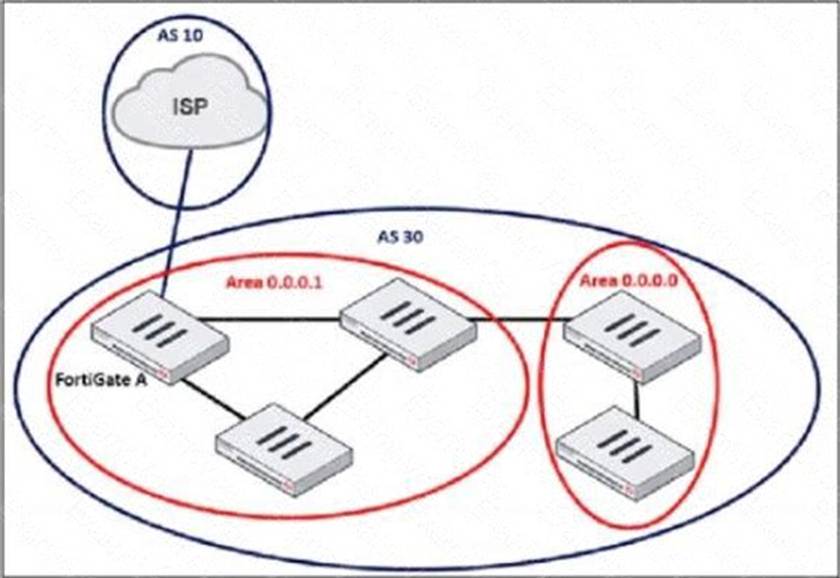
The administrator must configure the BGP section of FortiGate A to give internet access to the enterprise network.
Which command must the administrator use to establish a connection with the internet service provider?
- A . config neighbor
- B . config redistribute bgp
- C . config router route-map
- D . config redistribute ospf
A
Explanation:
InBGP (Border Gateway Protocol), aneighbor (peer) configurationis required to establish a connection between two BGP routers. SinceFortiGate A is connecting to the ISP (Autonomous System 10) from AS 30, the administrator must define theISP’s BGP router as a neighbor.
Theconfig neighborcommand is used to:
#Define the ISP’s IP address as a BGP peer
#Specify the remote AS (AS 10 in this case)
#Allow BGP route exchanges between FortiGate A and the ISP
Which configuration can be used to reduce the number of BGP sessions in an IBGP network?
- A . Neighbor range
- B . Route reflector
- C . Next-hop-self
- D . Neighbor group
View the exhibit, which contains a partial output of an IKE real-time debug, and then answer the question below.
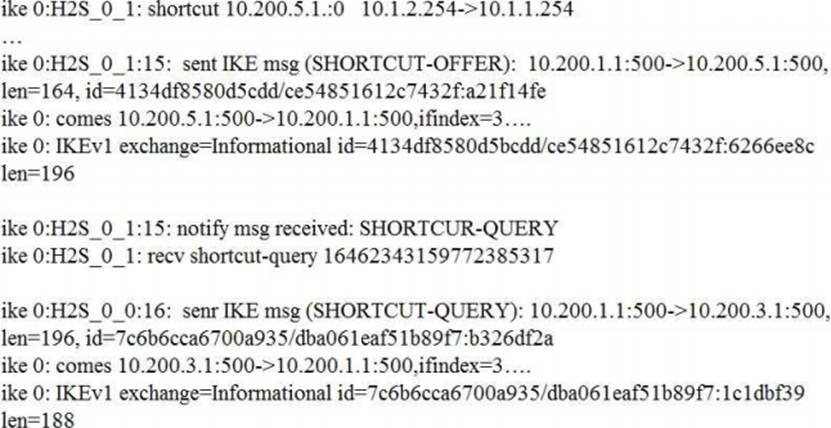
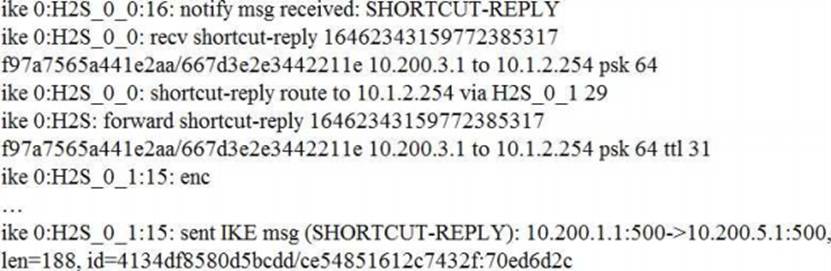
Based on the debug output, which phase-1 setting is enabled in the configuration of this VPN?
- A . auto-discovery-sender
- B . auto-discovery-forwarder
- C . auto-discovery-shortcut
- D . auto-discovery-receiver
A FortiGate device has the following LDAP configuration:
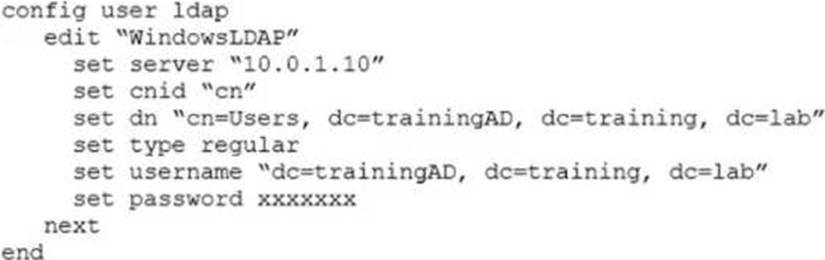
The administrator executed the ‘dsquery’ command in the Windows LDAp server 10.0.1.10, and got the following output:
>dsquery user -samid administrator
"CN-Administrator, CN-Users, DC=trainingAD, DC-training, DC-lab"
Based on the output, what FortiGate LDAP setting is configured incorrectly?
- A . cnid.
- B . username.
- C . password.
- D . dn.
View the exhibit, which contains a session entry, and then answer the question below.
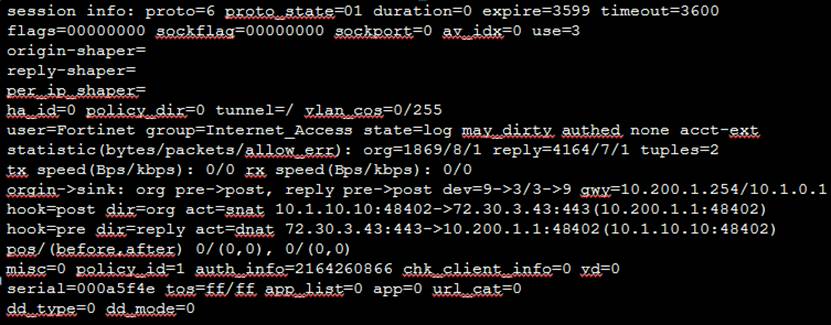
Which statement is correct regarding this session?
- A . This traffic is using the VIP and central NAT tables.
- B . This session was successfully authenticated.
- C . Further packets for this session will be blocked.
- D . This session is offloaded to the NPU.
One firewall policy in an enterprise firewall is essentially used for IPS.
Which configuration must the administrator check in this firewall policy to validate optimum performance for IPS?
- A . set cp-accel-mode enable
- B . set inspection-mode proxy
- C . set offload enable
- D . set np-acceleration enable
View the exhibit, which contains the partial output of an IKE real time debug, and then answer the question below.
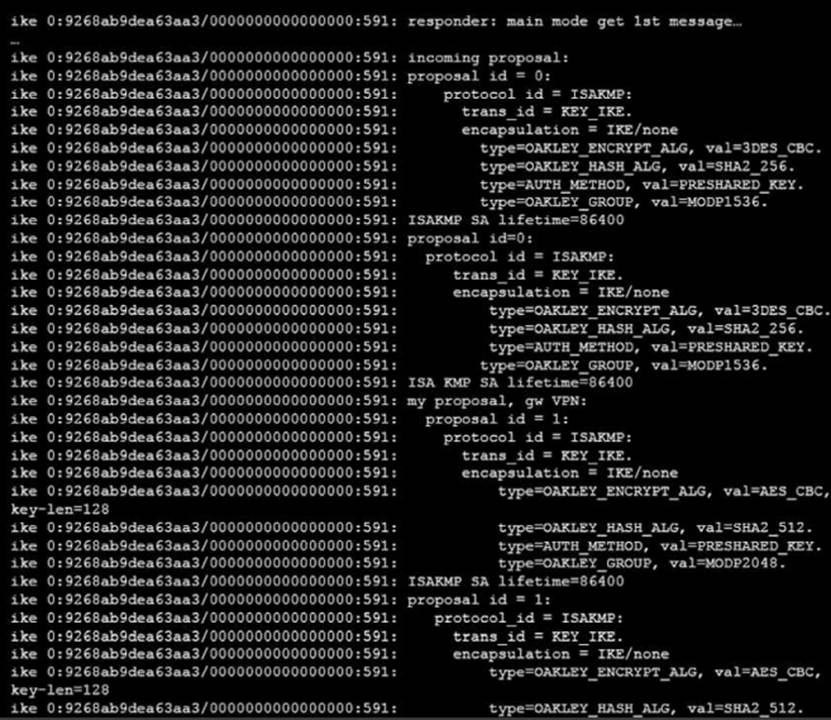
The administrator does not have access to the remote gateway.
Based on the debug output, what configuration changes can the administrator make to the local gateway to resolve the phase 1 negotiation error?
- A . Change phase 1 encryption to AESCBC and authentication to SHA128.
- B . Change phase 1 encryption to 3DES and authentication to CBC.
- C . Change phase 1 encryption to AES128 and authentication to SHA512.
- D . Change phase 1 encryption to 3DES and authentication to SHA256.