
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Nov 16,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Nov 16,2026
What configuration changes can reduce the memory utilization in a FortiGate? (Choose two.)
- A . Reduce the session time to live.
- B . Increase the TCP session timers.
- C . Increase the FortiGuard cache time to live.
- D . Reduce the maximum file size to inspect.
How does FortiManager handle FortiGuard requests from FortiGate devices, when it is configured as a local FDS?
- A . FortiManager can download and maintain local copies of FortiGuard databases.
- B . FortiManager supports only FortiGuard push to managed devices.
- C . FortiManager will respond to update requests only if they originate from a managed device.
- D . FortiManager does not support rating requests.
Which statement about memory conserve mode is true?
- A . A FortiGate exits conserve mode when the configured memory use threshold reaches yellow.
- B . A FortiGate Starts dropping all the new and old sessions when the configured memory use threshold reaches extreme.
- C . A FortiGate starts dropping new sessions when the configured memory use threshold reaches red
- D . A FortiGate enters conserve mode when the configured memory use threshold reaches red
Which two statements correctly describe the characteristics of the Fortinet Security Fabric? (Choose two.)
- A . It supports an open API, allowing third-party product integration.
- B . It provides a single pane of glass for reporting for all devices in the Security Fabric.
- C . The core of the Security Fabric includes FortiMail, FortiWeb, and FortiSandbox.
- D . It contains individual management platforms for each device to provide granular control.
An administrator received a FortiAnalyzer alert that a 1 ## disk filled up in a day. Upon investigation, they found thousands of unusual DNS log requests, such as JHCMQK.website.com, with no answers. They later discovered that DNS exfiltration was occurring through both UDP and TLS.
How can the administrator prevent this data theft technique?
- A . Create an inline-CASB to protect against DNS exfiltration.
- B . Configure a File Filter profile to prevent DNS exfiltration.
- C . Enable DNS Filter to protect against DNS exfiltration.
- D . Use an IPS profile and DNS exfiltration-related signatures.
D
Explanation:
The excessiveDNS log requests with random subdomainssuggest aDNS exfiltration attack, where attackers encode and transmit data via DNS queries. Since this technique can useboth UDP and TLS (DoH – DNS over HTTPS), a comprehensive security approach is needed.
Using anIPS profile with DNS exfiltration-specific signaturesallows FortiGate to:
#Detect and block abnormal DNS query patternsoften used in exfiltration.
#Inspect encrypted DNS (DoH, DoT) trafficif SSL inspection is enabled.
#Identify known exfiltration domains and techniquesbased on FortiGuard threat intelligence.
What are valid options for handling DNS requests sent directly to a FortiGates interface IP? (Choose three.)
- A . Conditional-forward.
- B . Forward-only.
- C . Non-recursive.
- D . Iterative.
- E . Recursive.
Refer to the exhibits.
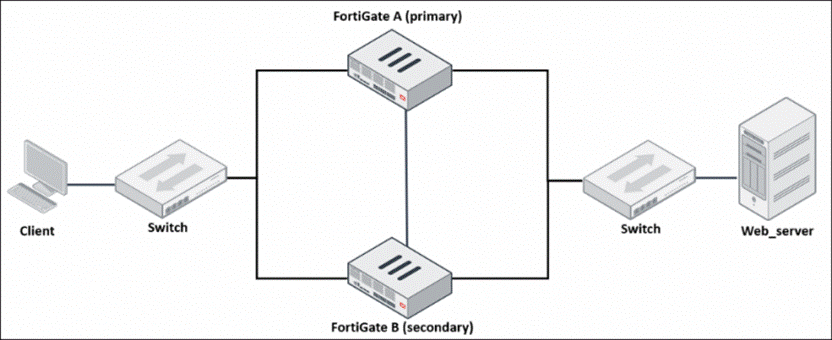
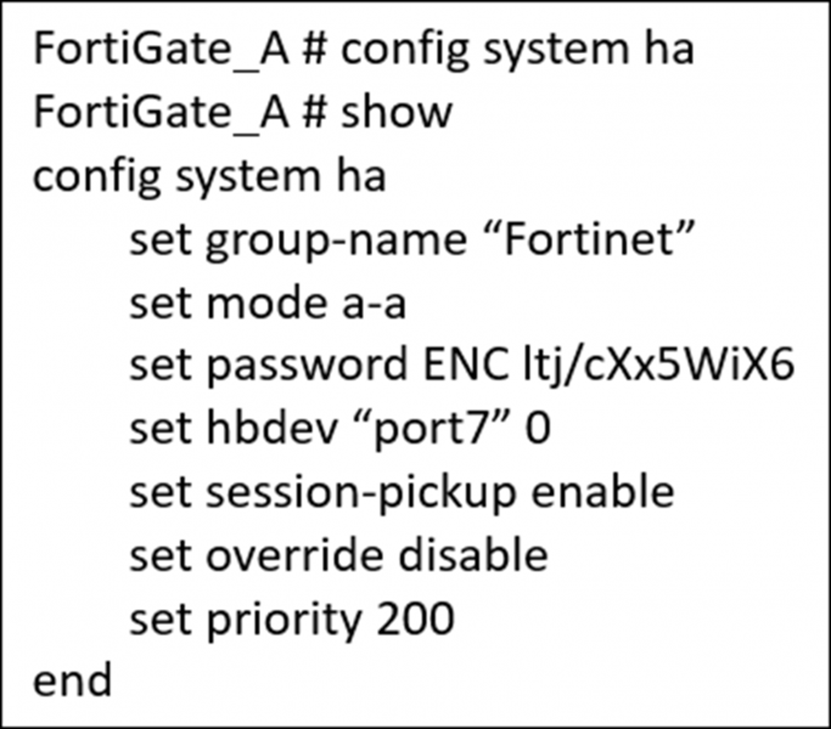
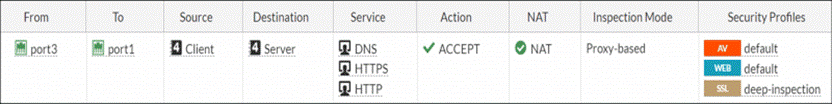
The exhibits show a network diagram, the output from the command config system ha, and a firewall policy.
What source MAC address does the web server detect when a user accesses it?
- A . The virtual MAC address of FortiGate B.
- B . The physical MAC address of FortiGate B.
- C . The virtual MAC address of FortiGate A.
- D . The physical MAC address of FortiGate A.
A FortiGate is configured as an explicit web proxy. Clients using this web proxy are reposting DNS errors when accessing any website.
The administrator executes the following debug commands and observes that the n-dns-timeout counter is increasing:
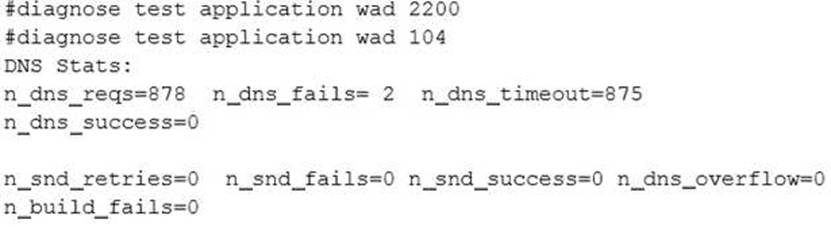
What should the administrator check to fix the problem?
- A . The connectivity between the FortiGate unit and the DNS server.
- B . The connectivity between the client workstations and the DNS server.
- C . That DNS traffic from client workstations is allowed by the explicit web proxy policies.
- D . That DNS service is enabled in the explicit web proxy interface.
An administrator must standardize the deployment of FortiGate devices across branches with consistent interface roles and policy packages using FortiManager.
What is the recommended best practice for interface assignment in this scenario?
- A . Enable metadata variables to use dynamic configurations in the standard interfaces of FortiManager.
- B . Use the Install On feature in the policy package to automatically assign different interfaces based on the branch.
- C . Create interfaces using device database scripts to use them on the same policy package of FortiGate devices.
- D . Create normalized interface types per-platform to automatically recognize device layer interfaces based on the FortiGate model and interface name.
A
Explanation:
Whenstandardizing the deployment of FortiGate devices across branchesusing FortiManager, thebest practiceis to usemetadata variables. This allows fordynamic interface configurationwhile maintaining a single, consistent policy packagefor all branches.
#Metadata variablesin FortiManager enableinterface roles and configurations to be dynamically assigned based on the specific FortiGate device.
# This ensuresscalabilityandconsistent security policy enforcementacross all branches without manually adjusting interface settings for each device.
# When a new branch FortiGate is deployed, metadata variables automaticallymap to the correct physical interfaces, reducing manual configuration errors.
Refer to the exhibit, which shows a FortiGate configuration.
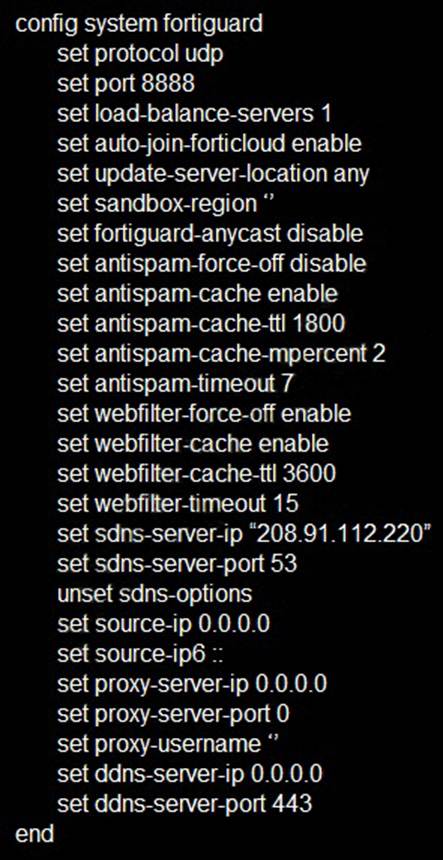
An administrator is troubleshooting a web filter issue on FortiGate. The administrator has configured a web filter profile and applied it to a policy; however, the web filter is not inspecting any traffic that is passing through the policy.
What must the administrator change to fix the issue?
- A . The administrator must increase webfilter-timeout.
- B . The administrator must change protocol to TCP.
- C . The administrator must enable fortiguard-anycast.
- D . The administrator must disable webfilter-force-off.