
EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
You have been hired as an intern at a start-up company. Your first task is to help set up a basic web server for the company’s new website. The team leader has asked you to make sure the server is secure from common – threats.
Based on your knowledge from studying for the CEH exam, which of the following actions should be your priority to secure the web server?
- A . Installing a web application firewall
- B . limiting the number of concurrent connections to the server
- C . Encrypting the company’s website with SSL/TLS
- D . Regularly updating and patching the server software
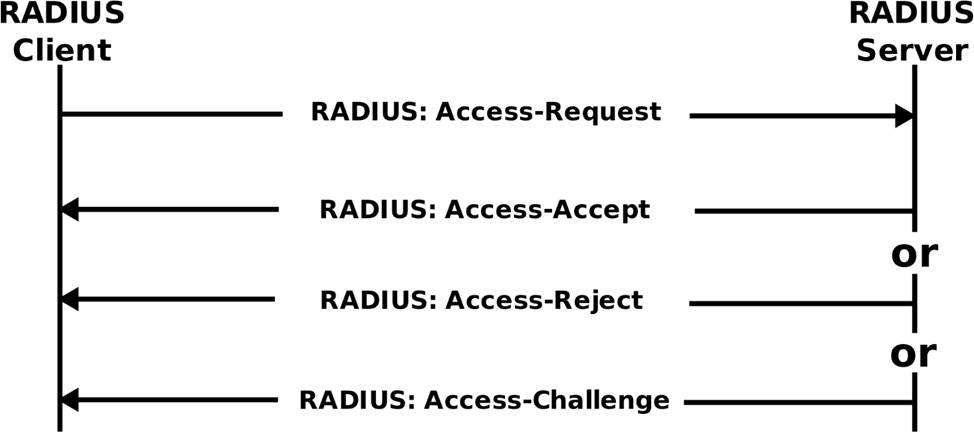
An Internet Service Provider (ISP) has a need to authenticate users connecting via analog modems, Digital Subscriber Lines (DSL), wireless data services, and Virtual Private Networks (VPN) over a Frame Relay network.
Which AAA protocol is the most likely able to handle this requirement?
- A . TACACS+
- B . DIAMETER
- C . Kerberos
- D . RADIUS
What is a NULL scan?
- A . A scan in which all flags are turned off
- B . A scan in which certain flags are off
- C . A scan in which all flags are on
- D . A scan in which the packet size is set to zero
- E . A scan with an illegal packet size
Why should the security analyst disable/remove unnecessary ISAPI filters?
- A . To defend against social engineering attacks
- B . To defend against webserver attacks
- C . To defend against jailbreaking
- D . To defend against wireless attacks
Attacker Simon targeted the communication network of an organization and disabled the security controls of NetNTLMvl by modifying the values of LMCompatibilityLevel, NTLMMinClientSec, and RestrictSendingNTLMTraffic. He then extracted all the non-network logon tokens from all the active processes to masquerade as a legitimate user to launch further attacks.
What is the type of attack performed by Simon?
- A . Internal monologue attack
- B . Combinator attack
- C . Rainbow table attack
- D . Dictionary attack
Which of the following DoS tools is used to attack target web applications by starvation of available sessions on the web server?
The tool keeps sessions at halt using never-ending POST transmissions and sending an arbitrarily large content-length header value.
- A . My Doom
- B . Astacheldraht
- C . R-U-Dead-Yet?(RUDY)
- D . LOIC
Bob wants to ensure that Alice can check whether his message has been tampered with. He creates a checksum of the message and encrypts it using asymmetric cryptography.
What key does Bob use to encrypt the checksum for accomplishing this goal?
- A . Alice’s private key
- B . Alice’s public key
- C . His own private key
- D . His own public key
Morris, an attacker, wanted to check whether the target AP is in a locked state. He attempted using different utilities to identify WPS-enabled APs in the target wireless network. Ultimately, he succeeded with one special command-line utility.
Which of the following command-line utilities allowed Morris to discover the WPS-enabled APs?
- A . wash
- B . ntptrace
- C . macof
- D . net View
User A is writing a sensitive email message to user B outside the local network. User A has chosen to use PKI to secure his message and ensure only user B can read the sensitive email.
At what layer of the OSI layer does the encryption and decryption of the message take place?
- A . Application
- B . Transport
- C . Session
- D . Presentation
A large enterprise has been experiencing sporadic system crashes and instability, resulting in limited access to its web services. The security team suspects it could be a result of a Denial of Service (DoS) attack. A significant increase in traffic was noticed in the network logs, with patterns suggesting packet sizes exceeding the prescribed size limit.
Which among the following DoS attack techniques best describes this scenario?
- A . UDP flood attack
- B . Smurf attack
- C . Pulse wave attack
- D . Ping of Death attack