
EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
Which of the following tools can be used to perform a zone transfer?
- A . NSLookup
- B . Finger
- C . Dig
- D . Sam Spade
- E . Host
- F . Netcat
- G . Neotrace
Allen, a professional pen tester, was hired by xpertTech solutWns to perform an attack simul-ation on the organization’s network resources. To perform the attack, he took advantage of the NetBIOS API and targeted the NetBIOS service. B/enumerating NetBIOS, he found that port 139 was open and could see the resources that could be accessed or viewed on a remote system. He came across many NetBIOS codes during enumeration.
identify the NetBIOS code used for obtaining the messenger service running for the logged-in user?
- A . <1B>
- B . <00>
- C . <03>
- D . <20>
As a security analyst for Sky Secure Inc., you are working with a client that uses a multi-cloud strategy, utilizing services from several cloud providers. The client wants to implement a system that will provide unified security management across all their cloud platforms. They need a solution that allows them to consistently enforce security policies, identify and respond to threats, and maintain visibility of all their cloud resources.
Which of the following should you recommend as the best solution?
- A . Use a hardware-based firewall to secure all cloud resources.
- B . implement separate security management tools for each cloud platform.
- C . Use a Cloud Access Security Broker (CASB).
- D . Rely on the built-in security features of each cloud platform.
John, a disgruntled ex-employee of an organization, contacted a professional hacker to exploit the organization. In the attack process, the professional hacker Installed a scanner on a machine belonging to one of the vktims and scanned several machines on the same network to Identify vulnerabilities to perform further exploitation.
What is the type of vulnerability assessment tool employed by John in the above scenario?
- A . Proxy scanner
- B . Agent-based scanner
- C . Network-based scanner
- D . Cluster scanner
You just set up a security system in your network.
In what kind of system would you find the following string of characters used as a rule within its configuration? alert tcp any any -> 192.168.100.0/24 21 (msg: ““FTP on the network!””;)
- A . A firewall IPTable
- B . FTP Server rule
- C . A Router IPTable
- D . An Intrusion Detection System
Which among the following is the best example of the hacking concept called "clearing tracks"?
- A . After a system is breached, a hacker creates a backdoor to allow re-entry into a system.
- B . During a cyberattack, a hacker injects a rootkit into a server.
- C . An attacker gains access to a server through an exploitable vulnerability.
- D . During a cyberattack, a hacker corrupts the event logs on all machines.
Consider the following Nmap output:
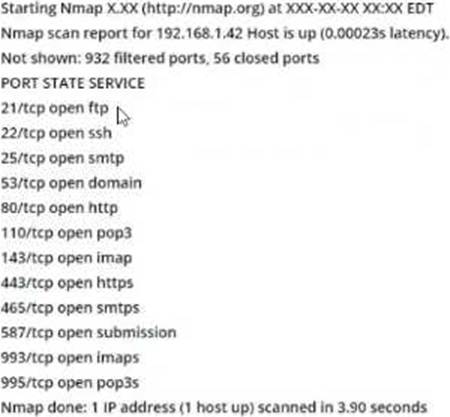
What command-line parameter could you use to determine the type and version number of the web server?
- A . -sv
- B . -Pn
- C . -V
- D . -ss
Security administrator John Smith has noticed abnormal amounts of traffic coming from local computers at night. Upon reviewing, he finds that user data have been exfilltrated by an attacker. AV tools are unable to find any malicious software, and the IDS/IPS has not reported on any non-whitelisted programs, what type of malware did the attacker use to bypass the company’s application whitelisting?
- A . Phishing malware
- B . Zero-day malware
- C . File-less malware
- D . Logic bomb malware
A network administrator discovers several unknown files in the root directory of his Linux FTP server. One of the files is a tarball, two are shell script files, and the third is a binary file is named "nc." The FTP server’s access logs show that the anonymous user account logged in to the server, uploaded the files, and extracted the contents of the tarball and ran the script using a function provided by the FTP server’s software. The “ps” command shows that the “nc” file is running as process, and the netstat command shows the “nc” process is listening on a network port.
What kind of vulnerability must be present to make this remote attack possible?
- A . File system permissions
- B . Privilege escalation
- C . Directory traversal
- D . Brute force login