
EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
A well-resourced attacker intends to launch a highly disruptive DDoS attack against a major online retailer. The attacker aims to exhaust all the network resources while keeping their identity concealed. Their method should be resistant to simple defensive measures such as IP-based blocking.
Based on these objectives, which of the following attack strategies would be most effective?
- A . The attacker should instigate a protocol-based SYN flood attack, consuming connection state tables on the retailer’s servers
- B . The attacker should execute a simple ICMP flood attack from a single IP, exploiting the retailer’s ICMP processing
- C . The attacker should leverage a botnet to launch a Pulse Wave attack, sending high-volume traffic pulses at regular intervals
- D . The attacker should initiate a volumetric flood attack using a single compromised machine to overwhelm the retailer’s network bandwidth
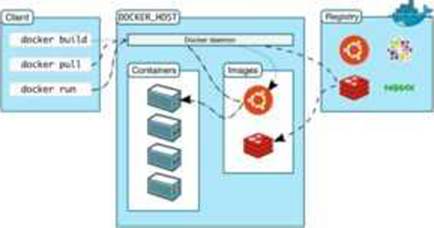
Annie, a cloud security engineer, uses the Docker architecture to employ a client/server model in the application she is working on. She utilizes a component that can process API requests and handle various Docker objects, such as containers, volumes. Images, and networks.
What is the component of the Docker architecture used by Annie in the above scenario?
- A . Docker client
- B . Docker objects
- C . Docker daemon
- D . Docker registries
You need a tool that can do network intrusion prevention and intrusion detection, function as a network sniffer, and record network activity, what tool would you most likely select?
- A . Nmap
- B . Cain & Abel
- C . Nessus
- D . Snort
Gilbert, a web developer, uses a centralized web API to reduce complexity and increase the Integrity of updating and changing data. For this purpose, he uses a web service that uses HTTP methods such as PUT. POST. GET. and DELETE and can improve the overall performance, visibility, scalability, reliability, and portability of an application.
What is the type of web-service API mentioned in the above scenario?
- A . JSON-RPC
- B . SOAP API
- C . RESTful API
- D . REST API
John wants to send Marie an email that includes sensitive information, and he does not trust the network that he is connected to. Marie gives him the idea of using PGP.
What should John do to communicate correctly using this type of encryption?
- A . Use his own public key to encrypt the message.
- B . Use Marie’s public key to encrypt the message.
- C . Use his own private key to encrypt the message.
- D . Use Marie’s private key to encrypt the message.
You’re the security manager for a tech company that uses a database to store sensitive customer data. You have implemented countermeasures against SQL injection attacks. Recently, you noticed some suspicious activities and suspect an attacker is using SQL injection techniques. The attacker is believed to use different forms of payloads in his SQL queries.
In the case of a successful SQL injection attack, which of the following payloads would have the most significant impact?
- A . ‘OR ‘T="1: This payload manipulates the WHERE clause of an SQL statement, allowing the attacker to view unauthorized data
- B . ‘OR username LIKE ‘%: This payload uses the LIKE operator to search for a specific pattern in a column
- C . OR ‘a’=’a; DROP TABLE members; –: This payload combines the manipulation of the WHERE clause with a destructive action, causing data loss
- D . UNION SELECT NULL, NULL, NULL — : This payload manipulates the UNION SQL operator, enabling the attacker to retrieve data from different database tables
You are tasked to perform a penetration test. While you are performing information gathering, you
find an employee list in Google. You find the receptionist’s email, and you send her an email changing the source email to her boss’s email (boss@company). In this email, you ask for a pdf with information. She reads your email and sends back a pdf with links. You exchange the pdf links with your malicious links (these links contain malware) and send back the modified pdf, saying that the links don’t work. She reads your email, opens the links, and her machine gets infected. You now have access to the company network.
What testing method did you use?
- A . Social engineering
- B . Piggybacking
- C . Tailgating
- D . Eavesdropping
Sam is a penetration tester hired by Inception Tech, a security organization. He was asked to perform port scanning on a target host in the network. While performing the given task, Sam sends FIN/ACK probes and determines that an RST packet is sent in response by the target host, indicating that the port is closed.
What is the port scanning technique used by Sam to discover open ports?
- A . Xmas scan
- B . IDLE/IPID header scan
- C . TCP Maimon scan
- D . ACK flag probe scan
The configuration allows a wired or wireless network interface controller to pass all traffic it receives to the Central Processing Unit (CPU), rather than passing only the frames that the controller is intended to receive.
Which of the following is being described?
- A . Multi-cast mode
- B . Promiscuous mode
- C . WEM
- D . Port forwarding