
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Which of the following best describes the document that defines the expectation to network customers that patching will only occur between 2:00 a.m. and 4:00 a.m?
- A . SLA
- B . LOI
- C . MOU
- D . KPI
Which of the following best describes the goal of a disaster recovery exercise as preparation for possible incidents?
- A . TO provide metrics and test continuity controls
- B . To verify the roles of the incident response team
- C . To provide recommendations for handling vulnerabilities
- D . To perform tests against implemented security controls
A regulated organization experienced a security breach that exposed a list of customer names with corresponding PH data.
Which of the following is the best reason for developing the organization’s communication plans?
- A . For the organization’s public relations department to have a standard notification
- B . To ensure incidents are immediately reported to a regulatory agency
- C . To automate the notification to customers who were impacted by the breach
- D . To have approval from executive leadership on when communication should occur
A security analyst is reviewing the network security monitoring logs listed below:
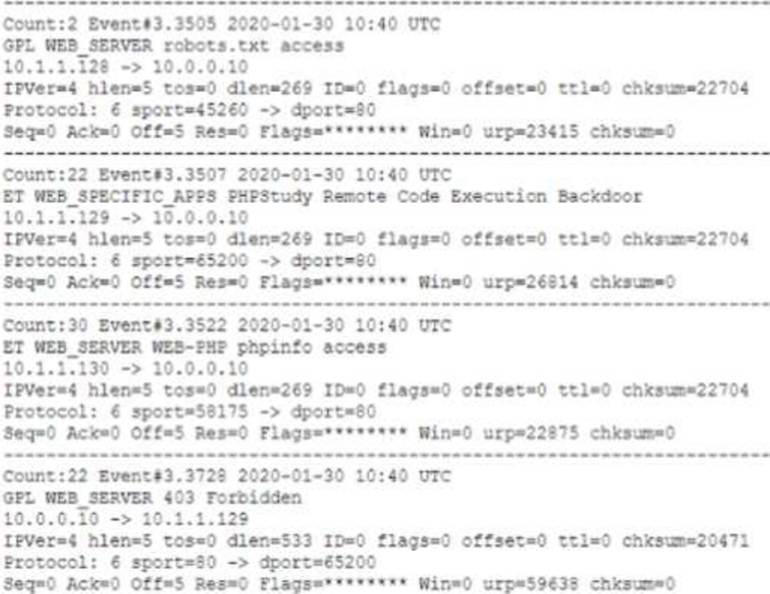
Which of the following is the analyst most likely observing? (Select two).
- A . 10.1.1.128 sent potential malicious traffic to the web server.
- B . 10.1.1.128 sent malicious requests, and the alert is a false positive
- C . 10.1.1.129 successfully exploited a vulnerability on the web server
- D . 10.1.1.129 sent potential malicious requests to the web server
- E . 10.1.1.129 can determine mat port 443 is being used
- F . 10.1.1.130 can potentially obtain information about the PHP version
While reviewing web server logs, an analyst notices several entries with the same time stamps, but all contain odd characters in the request line.
Which of the following steps should be taken next?
- A . Shut the network down immediately and call the next person in the chain of command.
- B . Determine what attack the odd characters are indicative of
- C . Utilize the correct attack framework and determine what the incident response will consist of.
- D . Notify the local law enforcement for incident response
During an incident response procedure, a security analyst acquired the needed evidence from the hard drive of a compromised machine.
Which of the following actions should the analyst perform next to ensure the data integrity of the evidence?
- A . Generate hashes for each file from the hard drive.
- B . Create a chain of custody document.
- C . Determine a timeline of events using correct time synchronization.
- D . Keep the cloned hard drive in a safe place.
A Chief Information Security Officer wants to map all the attack vectors that the company faces each day.
Which of the following recommendations should the company align their security controls around?
- A . OSSTMM
- B . Diamond Model Of Intrusion Analysis
- C . OWASP
- D . MITRE ATT&CK
A security analyst is monitoring a company’s network traffic and finds ping requests going to accounting and human resources servers from a SQL server. Upon investigation, the analyst discovers a technician responded to potential network connectivity issues.
Which of the following is the best way for the security analyst to respond?
- A . Report this activity as a false positive, as the activity is legitimate.
- B . Isolate the system and begin a forensic investigation to determine what was compromised.
- C . Recommend network segmentation to the management team as a way to secure the various environments.
- D . Implement host-based firewalls on all systems to prevent ping sweeps in the future.
Which of the following phases of the Cyber Kill Chain involves the adversary attempting to establish communication with a successfully exploited target?
- A . Command and control
- B . Actions on objectives
- C . Exploitation
- D . Delivery
While reviewing a vulnerability assessment, an analyst notices the following issue is identified in the report:
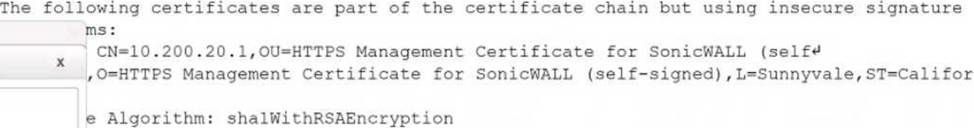
this finding, which of the following would be most appropriate for the analyst to recommend to the network engineer?
- A . Reconfigure the device to support only connections leveraging TLSv1.2.
- B . Obtain a new self-signed certificate and select AES as the hashing algorithm.
- C . Replace the existing certificate with a certificate that uses only MD5 for signing.
- D . Use only signed certificates with cryptographically secure certificate sources.