
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
The management team requests monthly KPI reports on the company’s cybersecurity program.
Which of the following KPIs would identify how long a security threat goes unnoticed in the environment?
- A . Employee turnover
- B . Intrusion attempts
- C . Mean time to detect
- D . Level of preparedness
A security analyst received a malicious binary file to analyze.
Which of the following is the best technique to perform the analysis?
- A . Code analysis
- B . Static analysis
- C . Reverse engineering
- D . Fuzzing
A security analyst is trying to identify possible network addresses from different source networks belonging to the same company and region.
Which of the following shell script functions could help achieve the goal?
- A . function w() { a=$(ping -c 1 $1 | awk-F ”/” ’END{print $1}’) && echo “$1 | $a” }
- B . function x() { b=traceroute -m 40 $1 | awk ’END{print $1}’) && echo “$1 | $b” }
- C . function y() { dig $(dig -x $1 | grep PTR | tail -n 1 | awk -F ”.in-addr” ’{print $1}’).origin.asn.cymru.com TXT +short }
- D . function z() { c=$(geoiplookup$1) && echo “$1 | $c” }
A security analyst is trying to identify possible network addresses from different source networks belonging to the same company and region.
Which of the following shell script functions could help achieve the goal?
- A . function w() { a=$(ping -c 1 $1 | awk-F ”/” ’END{print $1}’) && echo “$1 | $a” }
- B . function x() { b=traceroute -m 40 $1 | awk ’END{print $1}’) && echo “$1 | $b” }
- C . function y() { dig $(dig -x $1 | grep PTR | tail -n 1 | awk -F ”.in-addr” ’{print $1}’).origin.asn.cymru.com TXT +short }
- D . function z() { c=$(geoiplookup$1) && echo “$1 | $c” }
A penetration tester is conducting a test on an organization’s software development website.
The penetration tester sends the following request to the web interface:
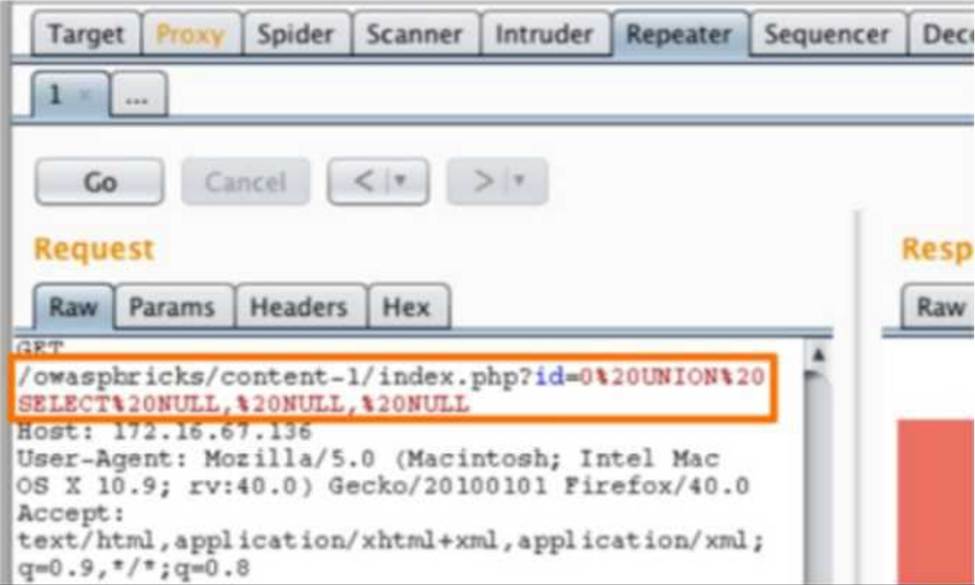
Which of the following exploits is most likely being attempted?
- A . SQL injection
- B . Local file inclusion
- C . Cross-site scripting
- D . Directory traversal
Given the output below:
#nmap 7.70 scan initiated Tues, Feb 8 12:34:56 2022 as: nmap -v -Pn -p 80,8000,443 –script http-* -oA server.out 192.168.220.42
Which of the following is being performed?
- A . Cross-site scripting
- B . Local file inclusion attack
- C . Log4] check
- D . Web server enumeration
Which of the following is the first step that should be performed when establishing a disaster recovery plan?
- A . Agree on the goals and objectives of the plan
- B . Determine the site to be used during a disaster
C Demonstrate adherence to a standard disaster recovery process - C . Identity applications to be run during a disaster
The steering committee for information security management annually reviews the security incident register for the organization to look for trends and systematic issues. The steering committee wants to rank the risks based on past incidents to improve the security program for next year.
Below is the incident register for the organization:
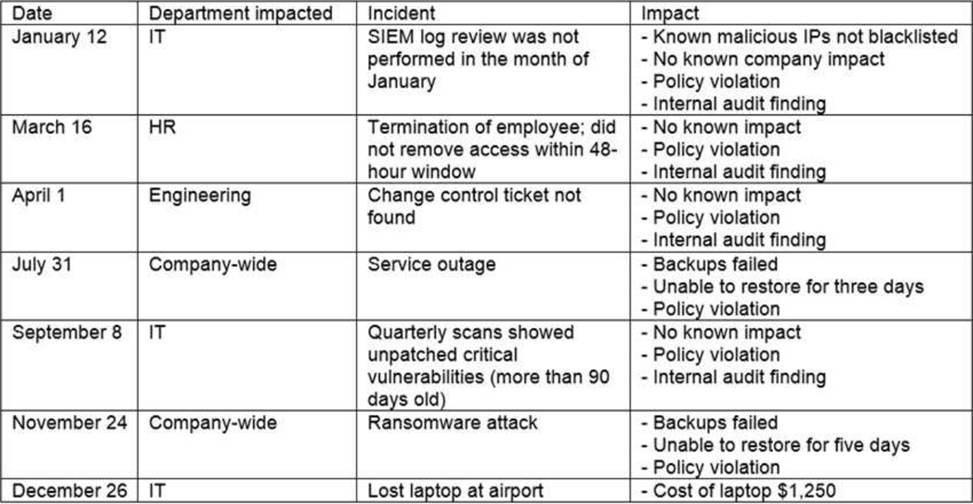
Which of the following should the organization consider investing in first due to the potential impact of availability?
- A . Hire a managed service provider to help with vulnerability management.
- B . Build a warm site in case of system outages.
- C . Invest in a failover and redundant system, as necessary.
- D . Hire additional staff for the IT department to assist with vulnerability management and log review.
A recent penetration test discovered that several employees were enticed to assist attackers by visiting specific websites and running downloaded files when prompted by phone calls.
Which of the following would best address this issue?
- A . Increasing training and awareness for all staff
- B . Ensuring that malicious websites cannot be visited
- C . Blocking all scripts downloaded from the internet
- D . Disabling all staff members’ ability to run downloaded applications
A security analyst is validating a particular finding that was reported in a web application vulnerability scan to make sure it is not a false positive.
The security analyst uses the snippet below:
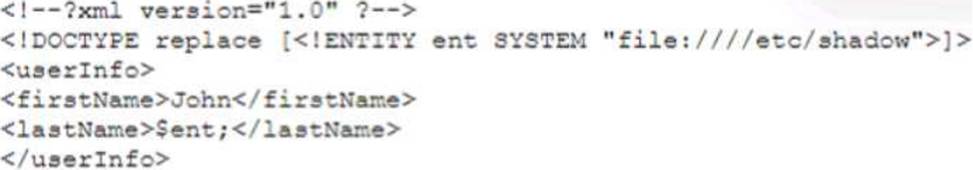
Which of the following vulnerability types is the security analyst validating?
- A . Directory traversal
- B . XSS
- C . XXE
- D . SSRF