
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Which of the following risk management principles is accomplished by purchasing cyber insurance?
- A . Accept
- B . Avoid
- C . Mitigate
- D . Transfer
In the last hour, a high volume of failed RDP authentication attempts has been logged on a critical server. All of the authentication attempts originated from the same remote IP address and made use of a single valid domain user account.
Which of the following mitigating controls would be most effective to reduce the rate of success of this brute-force attack? (Select two).
- A . Increase the granularity of log-on event auditing on all devices.
- B . Enable host firewall rules to block all outbound traffic to TCP port 3389.
- C . Configure user account lockout after a limited number of failed attempts.
- D . Implement a firewall block for the IP address of the remote system.
- E . Install a third-party remote access tool and disable RDP on all devices.
- F . Block inbound to TCP port 3389 from untrusted remote IP addresses at the perimeter firewall.
A cryptocurrency service company is primarily concerned with ensuring the accuracy of the data on one of its systems. A security analyst has been tasked with prioritizing vulnerabilities for remediation for the system.
The analyst will use the following CVSSv3.1 impact metrics for prioritization:
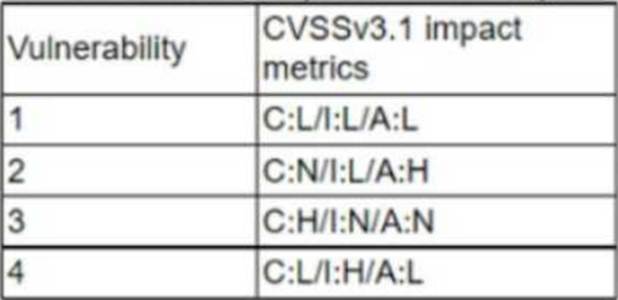
Which of the following vulnerabilities should be prioritized for remediation?
- A . 1
- B . 2
- C . 3
- D . 4
Which of the following most accurately describes the Cyber Kill Chain methodology?
- A . It is used to correlate events to ascertain the TTPs of an attacker.
- B . It is used to ascertain lateral movements of an attacker, enabling the process to be stopped.
- C . It provides a clear model of how an attacker generally operates during an intrusion and the actions to take at each stage
- D . It outlines a clear path for determining the relationships between the attacker, the technology used, and the target
A security team is concerned about recent Layer 4 DDoS attacks against the company website.
Which of the following controls would best mitigate the attacks?
- A . Block the attacks using firewall rules.
- B . Deploy an IPS in the perimeter network.
- C . Roll out a CDN.
- D . Implement a load balancer.
A company’s internet-facing web application has been compromised several times due to identified design flaws. The company would like to minimize the risk of these incidents from reoccurring and has provided the developers with better security training. However, the company cannot allocate any more internal resources to the issue.
Which of the following are the best options to help identify flaws within the system? (Select two).
- A . Deploying a WAF
- B . Performing a forensic analysis
- C . Contracting a penetration test
- D . Holding a tabletop exercise
- E . Creating a bug bounty program
- F . Implementing threat modeling
During an investigation, an analyst discovers the following rule in an executive’s email client:
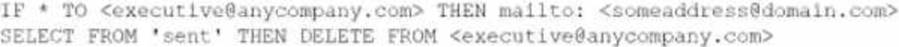
The executive is not aware of this rule.
Which of the following should the analyst do first to evaluate the potential impact of this security incident?
- A . Check the server logs to evaluate which emails were sent to <someaddress@domain,com>.
- B . Use the SIEM to correlate logging events from the email server and the domain server.
- C . Remove the rule from the email client and change the password.
- D . Recommend that the management team implement SPF and DKIM.
A vulnerability analyst is writing a report documenting the newest, most critical vulnerabilities identified in the past month.
Which of the following public MITRE repositories would be best to review?
- A . Cyber Threat Intelligence
- B . Common Vulnerabilities and Exposures
- C . Cyber Analytics Repository
ATT&CK
A vulnerability analyst is writing a report documenting the newest, most critical vulnerabilities identified in the past month.
Which of the following public MITRE repositories would be best to review?
- A . Cyber Threat Intelligence
- B . Common Vulnerabilities and Exposures
- C . Cyber Analytics Repository
ATT&CK
After a security assessment was done by a third-party consulting firm, the cybersecurity program recommended integrating DLP and CASB to reduce analyst alert fatigue.
Which of the following is the best possible outcome that this effort hopes to achieve?
- A . SIEM ingestion logs are reduced by 20%.
- B . Phishing alerts drop by 20%.
- C . False positive rates drop to 20%.
- D . The MTTR decreases by 20%.