
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A company has decided to expose several systems to the internet, The systems are currently available internally only. A security analyst is using a subset of CVSS3.1 exploitability metrics to prioritize the vulnerabilities that would be the most exploitable when the systems are exposed to the internet.
The systems and the vulnerabilities are shown below:
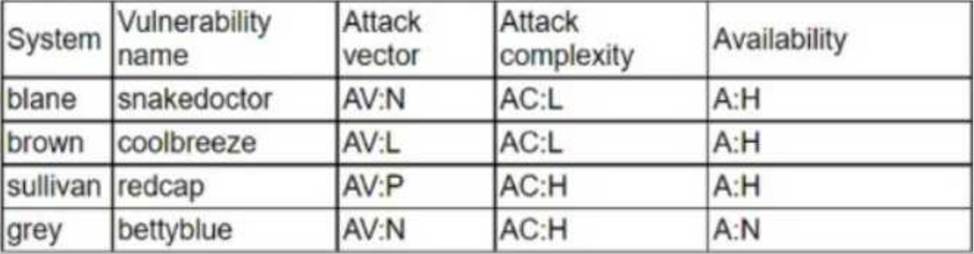
Which of the following systems should be prioritized for patching?
- A . brown
- B . grey
- C . blane
- D . sullivan
A security analyst has found a moderate-risk item in an organization’s point-of-sale application. The organization is currently in a change freeze window and has decided that the risk is not high enough to correct at this time.
Which of the following inhibitors to remediation does this scenario illustrate?
- A . Service-level agreement
- B . Business process interruption
- C . Degrading functionality
- D . Proprietary system
A vulnerability management team is unable to patch all vulnerabilities found during their weekly scans.
Using the third-party scoring system described below, the team patches the most urgent vulnerabilities:
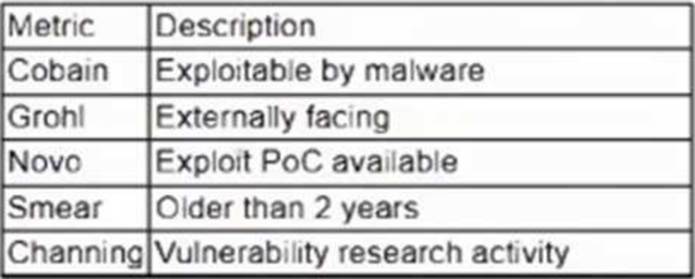
Additionally, the vulnerability management team feels that the metrics Smear and Channing are less important than the others, so these will be lower in priority.
Which of the following vulnerabilities should be patched first, given the above third-party scoring system?
- A . InLoud:
Cobain: Yes
Grohl: No
Novo: Yes
Smear: Yes
Channing: No - B . TSpirit:
Cobain: Yes
Grohl: Yes
Novo: Yes
Smear: No
Channing: No - C . ENameless:
Cobain: Yes
Grohl: No
Novo: Yes
Smear: No
Channing: No - D . PBleach:
Cobain: Yes
Grohl: No
Novo: No
Smear: No
Channing: Yes
The Chief Information Security Officer (CISO) of a large management firm has selected a cybersecurity framework that will help the organization demonstrate its investment in tools and systems to protect its data.
Which of the following did the CISO most likely select?
- A . PCI DSS
- B . COBIT
- C . ISO 27001
- D . ITIL
The Chief Information Security Officer (CISO) of a large management firm has selected a cybersecurity framework that will help the organization demonstrate its investment in tools and systems to protect its data.
Which of the following did the CISO most likely select?
- A . PCI DSS
- B . COBIT
- C . ISO 27001
- D . ITIL
An organization identifies a method to detect unexpected behavior, crashes, or resource leaks in a system by feeding invalid, unexpected, or random data to stress the application.
Which of the following best describes this testing methodology?
- A . Reverse engineering
- B . Static
- C . Fuzzing
- D . Debugging
The security analyst received the monthly vulnerability report.
The following findings were included in the report
• Five of the systems only required a reboot to finalize the patch application.
• Two of the servers are running outdated operating systems and cannot be patched
The analyst determines that the only way to ensure these servers cannot be compromised is to isolate them.
Which of the following approaches will best minimize the risk of the outdated servers being compromised?
- A . Compensating controls
- B . Due diligence
- C . Maintenance windows
- D . Passive discovery
An analyst is reviewing a vulnerability report and must make recommendations to the executive team. The analyst finds that most systems can be upgraded with a reboot resulting in a single downtime window. However, two of the critical systems cannot be upgraded due to a vendor appliance that the company does not have access to.
Which of the following inhibitors to remediation do these systems and associated vulnerabilities best represent?
- A . Proprietary systems
- B . Legacy systems
- C . Unsupported operating systems
- D . Lack of maintenance windows
After completing a review of network activity. the threat hunting team discovers a device on the network that sends an outbound email via a mail client to a non-company email address daily at 10:00 p.m.
Which of the following is potentially occurring?
- A . Irregular peer-to-peer communication
- B . Rogue device on the network
- C . Abnormal OS process behavior
- D . Data exfiltration
An incident response team finished responding to a significant security incident. The management team has asked the lead analyst to provide an after-action report that includes lessons learned.
Which of the following is the most likely reason to include lessons learned?
- A . To satisfy regulatory requirements for incident reporting
- B . To hold other departments accountable
- C . To identify areas of improvement in the incident response process
- D . To highlight the notable practices of the organization’s incident response team