
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Given the following CVSS string-CVSS:3.0/AV: N/AC: L/PR: N/UI: N/3: U/C: K/I: K/A:H
Which of the following attributes correctly describes this vulnerability?
- A . A user is required to exploit this vulnerability.
- B . The vulnerability is network based.
- C . The vulnerability does not affect confidentiality.
- D . The complexity to exploit the vulnerability is high.
A company is in the process of implementing a vulnerability management program. no-lich of the following scanning methods should be implemented to minimize the risk of OT/ICS devices malfunctioning due to the vulnerability identification process?
- A . Non-credentialed scanning
- B . Passive scanning
- C . Agent-based scanning
- D . Credentialed scanning
Which of the following techniques can help a SOC team to reduce the number of alerts related to the internal security activities that the analysts have to triage?
- A . Enrich the SIEM-ingested data to include all data required for triage.
- B . Schedule a task to disable alerting when vulnerability scans are executing.
- C . Filter all alarms in the SIEM with low severity.
- D . Add a SOAR rule to drop irrelevant and duplicated notifications.
An organization would like to ensure its cloud infrastructure has a hardened configuration. A requirement is to create a server image that can be deployed with a secure template.
Which of the following is the best resource to ensure secure configuration?
- A . CIS Benchmarks
- B . PCI DSS
- C . OWASP Top Ten
- D . ISO 27001
The Chief Information Security Officer wants to eliminate and reduce shadow IT in the enterprise. Several high-risk cloud applications are used that increase the risk to the organization.
Which of the following solutions will assist in reducing the risk?
- A . Deploy a CASB and enable policy enforcement
- B . Configure MFA with strict access
- C . Deploy an API gateway
- D . Enable SSO to the cloud applications
A company is implementing a vulnerability management program and moving from an on-premises environment to a hybrid IaaS cloud environment.
Which of the following implications should be considered on the new hybrid environment?
- A . The current scanners should be migrated to the cloud
- B . Cloud-specific misconfigurations may not be detected by the current scanners
- C . Existing vulnerability scanners cannot scan laaS systems
- D . Vulnerability scans on cloud environments should be performed from the cloud
Which of the following security operations tasks are ideal for automation?
- A . Suspicious file analysis:
– Look for suspicious-looking graphics in a folder.
– Create subfolders in the original folder based on category of graphics found.
– Move the suspicious graphics to the appropriate subfolder - B . Firewall IoC block actions:
Examine the firewall logs for IoCs from the most recently published zero-day exploit
Take mitigating actions in the firewall to block the behavior found in the logs
Follow up on any false positives that were caused by the block rules - C . Security application user errors:
Search the error logs for signs of users having trouble with the security application Look up the user’s phone number
Call the user to help with any questions about using the application - D . Email header analysis:
Check the email header for a phishing confidence metric greater than or equal to five
Add the domain of sender to the block list
Move the email to quarantine
An organization has tracked several incidents that are listed in the following table:
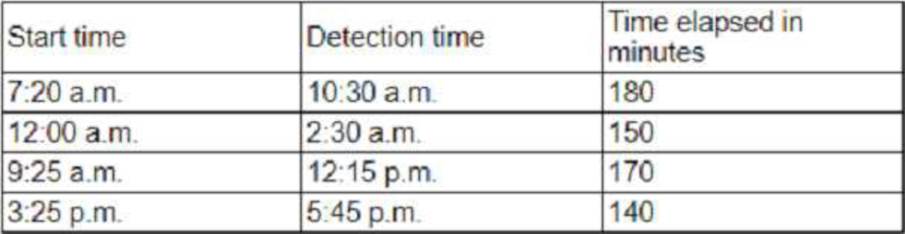
Which of the following is the organization’s MTTD?
- A . 140
- B . 150
- C . 160
- D . 180
An analyst investigated a website and produced the following:
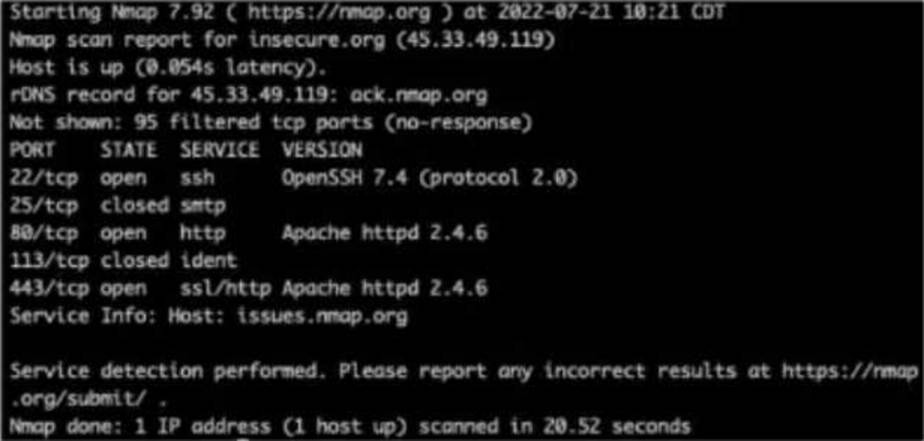
Which of the following syntaxes did the analyst use to discover the application versions on this vulnerable website?
- A . nmap -sS -T4 -F insecure.org
- B . nmap -o insecure.org
- C . nmap -sV -T4 -F insecure.org
- D . nmap -A insecure.org
After conducting a cybersecurity risk assessment for a new software request, a Chief Information Security Officer (CISO) decided the risk score would be too high. The CISO refused the software request.
Which of the following risk management principles did the CISO select?
- A . Avoid
- B . Transfer
- C . Accept
- D . Mitigate