
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A security analyst recently used Arachni to perform a vulnerability assessment of a newly developed web application.
The analyst is concerned about the following output:
[+] XSS: In form input ‘txtSearch’ with action https://localhost/search.aspx
[-] XSS: Analyzing response #1…
[-] XSS: Analyzing response #2…
[-] XSS: Analyzing response #3…
[+] XSS: Response is tainted. Looking for proof of the vulnerability.
Which of the following is the most likely reason for this vulnerability?
- A . The developer set input validation protection on the specific field of search.aspx.
- B . The developer did not set proper cross-site scripting protections in the header.
- C . The developer did not implement default protections in the web application build.
- D . The developer did not set proper cross-site request forgery protections.
A company recently removed administrator rights from all of its end user workstations. An analyst uses CVSSv3.1 exploitability metrics to prioritize the vulnerabilities for the workstations and produces the following information:
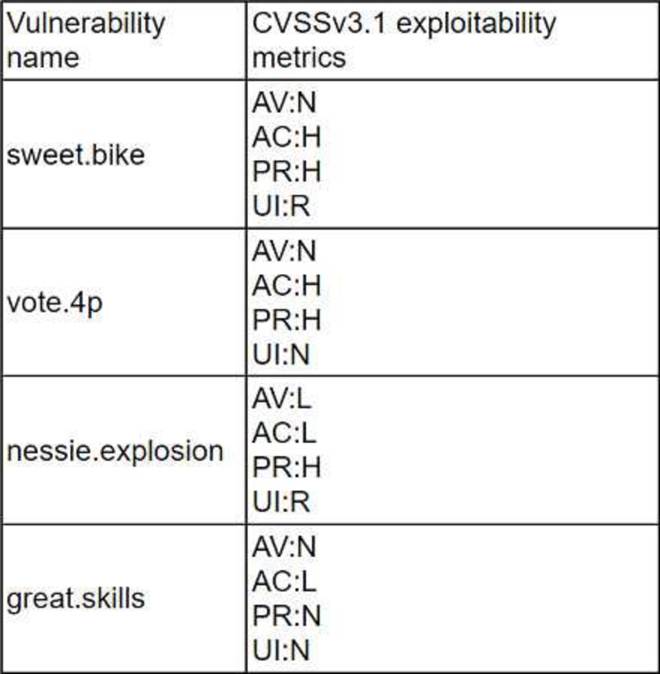
Which of the following vulnerabilities should be prioritized for remediation?
- A . nessie.explosion
- B . vote.4p
- C . sweet.bike
- D . great.skills
An analyst is examining events in multiple systems but is having difficulty correlating data points.
Which of the following is most likely the issue with the system?
- A . Access rights
- B . Network segmentation
- C . Time synchronization
- D . Invalid playbook
An email hosting provider added a new data center with new public IP addresses.
Which of the following most likely needs to be updated to ensure emails from the new data center do not get blocked by spam filters?
- A . DKIM
- B . SPF
- C . SMTP
- D . DMARC
A development team is preparing to roll out a beta version of a web application and wants to quickly test for vulnerabilities, including SQL injection, path traversal, and cross-site scripting.
Which of the following tools would the security team most likely recommend to perform this test?
- A . Has heat
- B . OpenVAS
- C . OWASP ZAP
- D . Nmap
A security analyst observed the following activity from a privileged account:
. Accessing emails and sensitive information
. Audit logs being modified
. Abnormal log-in times
Which of the following best describes the observed activity?
- A . Irregular peer-to-peer communication
- B . Unauthorized privileges
- C . Rogue devices on the network
- D . Insider attack
An organization’s email account was compromised by a bad actor. Given the following Information:
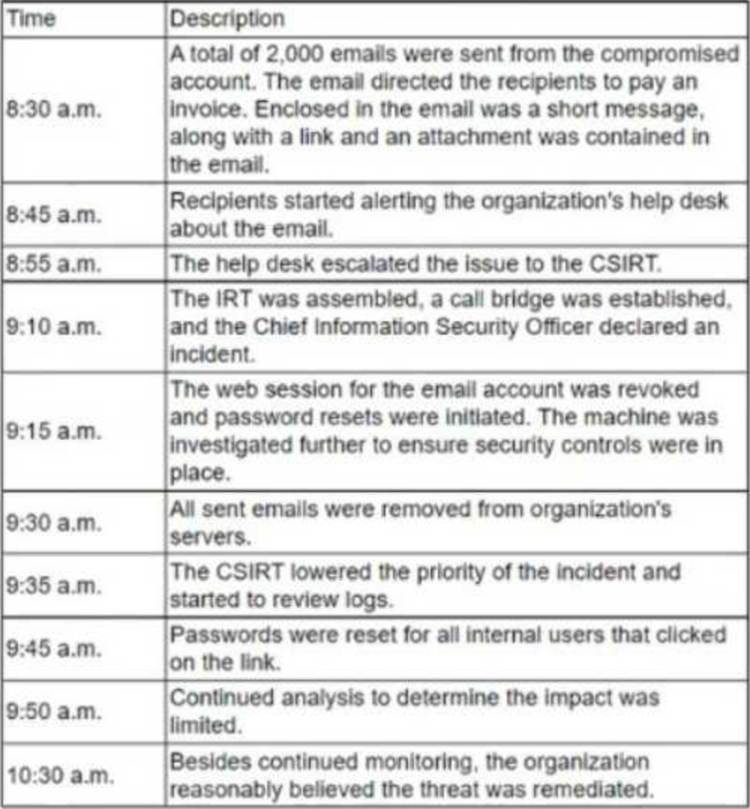
Which of the following is the length of time the team took to detect the threat?
- A . 25 minutes
- B . 40 minutes
- C . 45 minutes
- D . 2 hours
A security analyst wants to capture large amounts of network data that will be analyzed at a later time. The packet capture does not need to be in a format that is readable by humans, since it will be put into a binary file called "packetCapture." The capture must be as efficient as possible, and the analyst wants to minimize the likelihood that packets will be missed.
Which of the following commands will best accomplish the analyst’s objectives?
- A . tcpdump -w packetCapture
- B . tcpdump -a packetCapture
- C . tcpdump -n packetCapture
- D . nmap -v > packetCapture
- E . nmap -oA > packetCapture
A security analyst needs to ensure that systems across the organization are protected based on the sensitivity of the content each system hosts. The analyst is working with the respective system owners to help determine the best methodology that seeks to promote confidentiality, availability,
and integrity of the data being hosted.
Which of the following should the security analyst perform first to
categorize and prioritize the respective systems?
- A . Interview the users who access these systems,
- B . Scan the systems to see which vulnerabilities currently exist.
- C . Configure alerts for vendor-specific zero-day exploits.
- D . Determine the asset value of each system.
A security analyst has identified a new malware file that has impacted the organization. The malware is polymorphic and has built-in conditional triggers that require a connection to the internet. The CPU has an idle process of at least 70%.
Which of the following best describes how the security analyst can effectively review the malware without compromising the organization’s network?
- A . Utilize an RDP session on an unused workstation to evaluate the malware.
- B . Disconnect and utilize an existing infected asset off the network.
- C . Create a virtual host for testing on the security analyst workstation.
- D . Subscribe to an online service to create a sandbox environment.