
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
While reviewing a vulnerability assessment, an analyst notices the following issue is identified in the report:
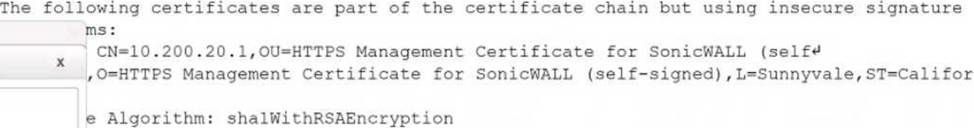
this finding, which of the following would be most appropriate for the analyst to recommend to the network engineer?
- A . Reconfigure the device to support only connections leveraging TLSv1.2.
- B . Obtain a new self-signed certificate and select AES as the hashing algorithm.
- C . Replace the existing certificate with a certificate that uses only MD5 for signing.
- D . Use only signed certificates with cryptographically secure certificate sources.
A disgruntled open-source developer has decided to sabotage a code repository with a logic bomb that will act as a wiper.
Which of the following parts of the Cyber Kill Chain does this act exhibit?
- A . Reconnaissance
- B . Weaponization
- C . Exploitation
- D . Installation
Each time a vulnerability assessment team shares the regular report with other teams, inconsistencies regarding versions and patches in the existing infrastructure are discovered.
Which of the following is the best solution to decrease the inconsistencies?
- A . Implementing credentialed scanning
- B . Changing from a passive to an active scanning approach
- C . Implementing a central place to manage IT assets
- D . Performing agentless scanning
A security audit for unsecured network services was conducted, and the following output was generated:
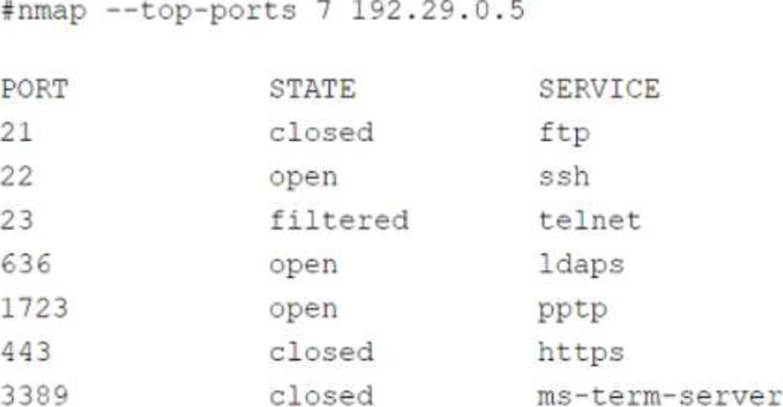
Which of the following services should the security team investigate further? (Select two).
- A . 21
- B . 22
- C . 23
- D . 636
- E . 1723
- F . 3389
The following output is from a tcpdump al the edge of the corporate network:
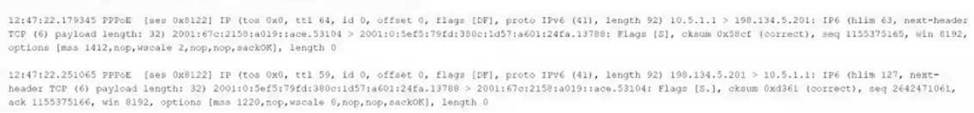
Which of the following best describes the potential security concern?
- A . Payload lengths may be used to overflow buffers enabling code execution.
- B . Encapsulated traffic may evade security monitoring and defenses
- C . This traffic exhibits a reconnaissance technique to create network footprints.
- D . The content of the traffic payload may permit VLAN hopping.
Which of the following stakeholders are most likely to receive a vulnerability scan report? (Select two).
- A . Executive management
- B . Law enforcement
- C . Marketing
- D . Legal
- E . Product owner
- F . Systems admininstration
K company has recently experienced a security breach via a public-facing service. Analysis of the event on the server was traced back to the following piece of code:
SELECT ’ From userjdata WHERE Username = 0 and userid8 1 or 1=1;―
Which of the following controls would be best to implement?
- A . Deploy a wireless application protocol.
- B . Remove the end-of-life component.
- C . Implement proper access control.
- D . Validate user input.
During an internal code review, software called "ACE" was discovered to have a vulnerability that allows the execution of arbitrary code. The vulnerability is in a legacy, third-party vendor resource that is used by the ACE software. ACE is used worldwide and is essential for many businesses in this industry. Developers informed the Chief Information Security Officer that removal of the vulnerability will take time.
Which of the following is the first action to take?
- A . Look for potential loCs in the company.
- B . Inform customers of the vulnerability.
- C . Remove the affected vendor resource from the ACE software.
- D . Develop a compensating control until the issue can be fixed permanently.
A company is in the process of implementing a vulnerability management program, and there are concerns about granting the security team access to sensitive data.
Which of the following scanning methods can be implemented to reduce the access to systems while providing the most accurate vulnerability scan results?
- A . Credentialed network scanning
- B . Passive scanning
- C . Agent-based scanning
- D . Dynamic scanning
During the log analysis phase, the following suspicious command is detected-
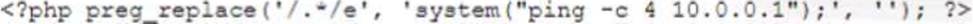
Which of the following is being attempted?
- A . Buffer overflow
- B . RCE
- C . ICMP tunneling
- D . Smurf attack