
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
During the log analysis phase, the following suspicious command is detected-
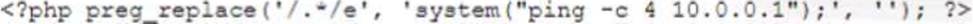
Which of the following is being attempted?
- A . Buffer overflow
- B . RCE
- C . ICMP tunneling
- D . Smurf attack
Which of the following would a security analyst most likely use to compare TTPs between different known adversaries of an organization?
- A . MITRE ATTACK
- B . Cyber Kill Cham
- C . OWASP
- D . STIXTAXII
A Chief Information Security Officer wants to implement security by design, starting ……
vulnerabilities, including SQL injection, FRI, XSS, etc.
Which of the following would most likely meet the requirement?
- A . Reverse engineering
- B . Known environment testing
- C . Dynamic application security testing
- D . Code debugging
Which of the following in the digital forensics process is considered a critical activity that often includes a graphical representation of process and operating system events?
- A . Registry editing
- B . Network mapping
- C . Timeline analysis
- D . Write blocking
The Chief Information Security Officer is directing a new program to reduce attack surface risks and threats as part of a zero trust approach. The IT security team is required to come up with priorities for the program.
Which of the following is the best priority based on common attack frameworks?
- A . Reduce the administrator and privileged access accounts
- B . Employ a network-based IDS
- C . Conduct thorough incident response
- D . Enable SSO to enterprise applications
A vulnerability analyst received a list of system vulnerabilities and needs to evaluate the relevant impact of the exploits on the business. Given the constraints of the current sprint, only three can be remediated.
Which of the following represents the least impactful risk, given the CVSS3.1 base scores?
- A . AV:N/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:L – Base Score 6.0
- B . AV:N/AC:H/PR:H/UI:N/S:C/C:H/I:L/A:L – Base Score 7.2
- C . AV:N/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:H – Base Score 6.4
- D . AV:N/AC:H/PR:N/UI:N/S:C/C:L/I:L/A:L – Base Score 6.5
A vulnerability analyst received a list of system vulnerabilities and needs to evaluate the relevant impact of the exploits on the business. Given the constraints of the current sprint, only three can be remediated.
Which of the following represents the least impactful risk, given the CVSS3.1 base scores?
- A . AV:N/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:L – Base Score 6.0
- B . AV:N/AC:H/PR:H/UI:N/S:C/C:H/I:L/A:L – Base Score 7.2
- C . AV:N/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:H – Base Score 6.4
- D . AV:N/AC:H/PR:N/UI:N/S:C/C:L/I:L/A:L – Base Score 6.5
A Chief Information Officer wants to implement a BYOD strategy for all company laptops and mobile phones. The Chief Information Security Officer is concerned with ensuring all devices are patched and running some sort of protection against malicious software.
Which of the following existing technical controls should a security analyst recommend to best meet all the requirements?
- A . EDR
- B . Port security
- C . NAC
- D . Segmentation
Which of the following would likely be used to update a dashboard that integrates…..
- A . Webhooks
- B . Extensible Markup Language
- C . Threat feed combination
- D . JavaScript Object Notation
A security analyst is reviewing the logs of a web server and notices that an attacker has attempted to exploit a SQL injection vulnerability.
Which of the following tools can the analyst use to analyze the attack and prevent future attacks?
- A . A web application firewall
- B . A network intrusion detection system
- C . A vulnerability scanner
- D . A web proxy