
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A security analyst received an alert regarding multiple successful MFA log-ins for a particular user
When reviewing the authentication logs the analyst sees the following:
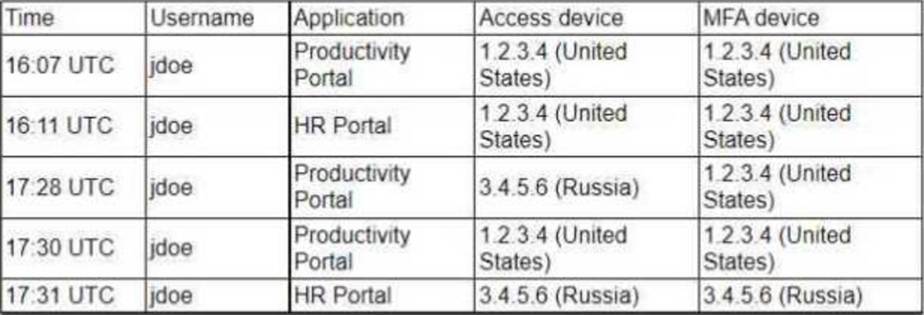
Which of the following are most likely occurring, based on the MFA logs? (Select two).
- A . Dictionary attack
- B . Push phishing
- C . impossible geo-velocity
- D . Subscriber identity module swapping
- E . Rogue access point
- F . Password spray
SIMULATION
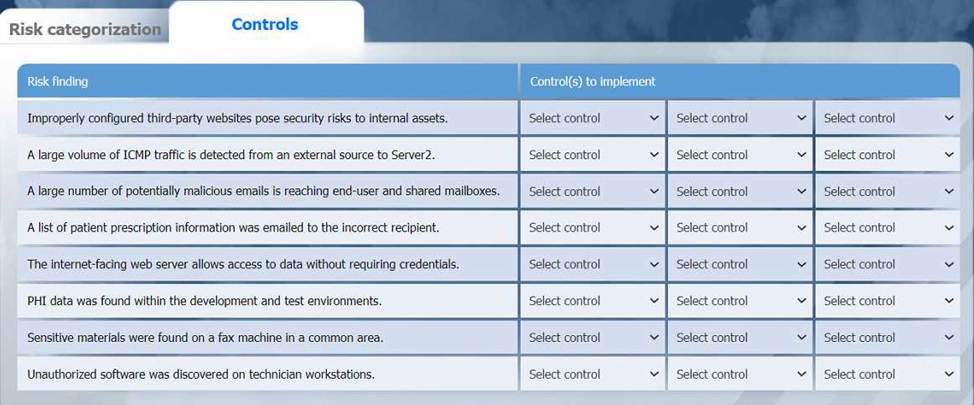
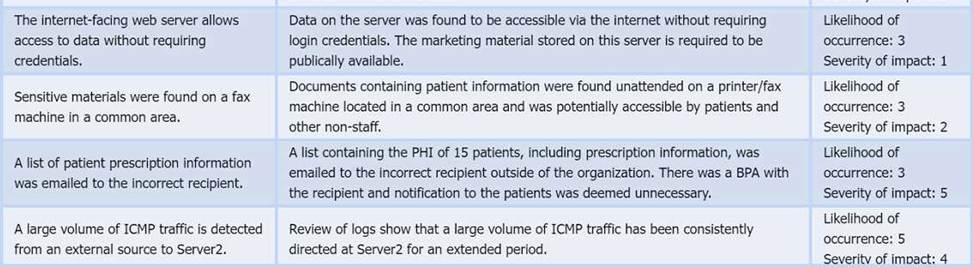
A healthcare organization must develop an action plan based on the findings from a risk assessment.
The action plan must consist of:
・ Risk categorization
・ Risk prioritization
. Implementation of controls
INSTRUCTIONS
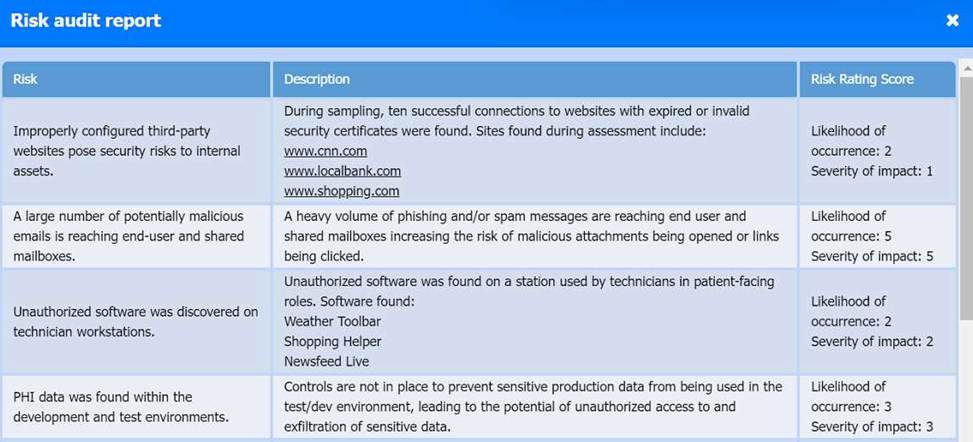
Click on the audit report, risk matrix, and SLA expectations documents to review their contents.
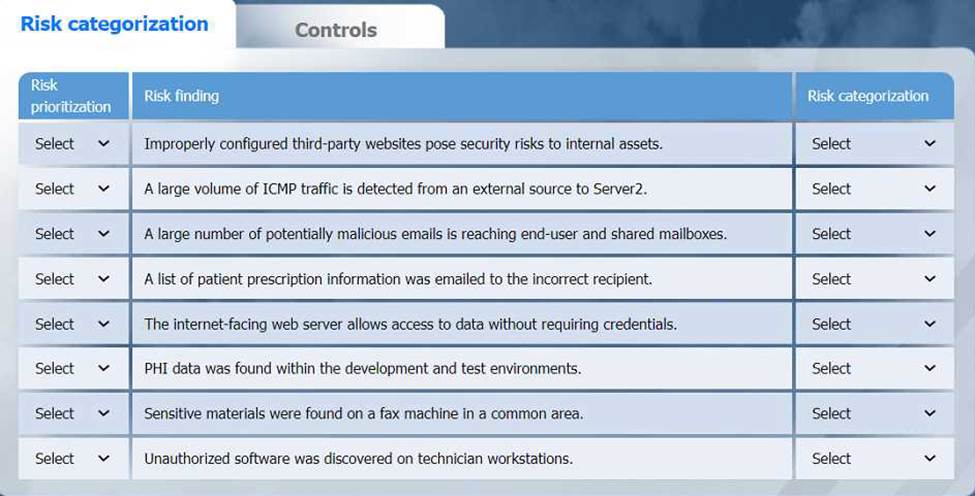
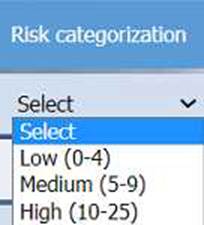
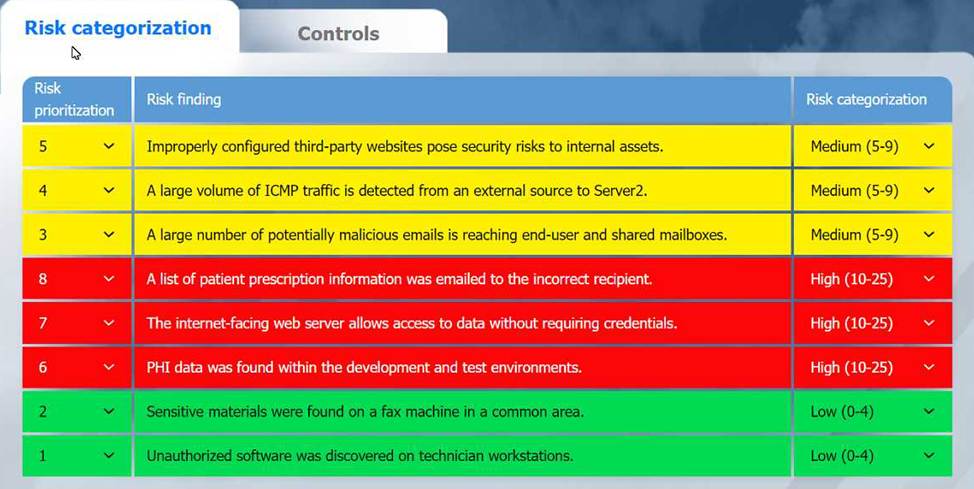
On the Risk categorization tab, determine the order in which the findings must be prioritized for remediation according to the risk rating score. Then, assign a categorization to each risk.
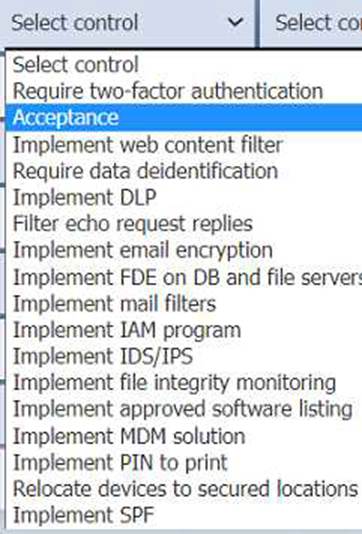
On the Controls tab, select the appropriate control(s) to implement for each risk finding. Findings may have more than one control implemented. Some controls may be used more than once or not at all.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
During normal security monitoring activities, the following activity was observed:
cd C:UsersDocumentsHREmployees
takeown/f .*
SUCCESS:
Which of the following best describes the potentially malicious activity observed?
- A . Registry changes or anomalies
- B . Data exfiltration
- C . Unauthorized privileges
- D . File configuration changes
During security scanning, a security analyst regularly finds the same vulnerabilities in a critical application.
Which of the following recommendations would best mitigate this problem if applied along the SDLC phase?
- A . Conduct regular red team exercises over the application in production
- B . Ensure that all implemented coding libraries are regularly checked
- C . Use application security scanning as part of the pipeline for the CI/CDflow
- D . Implement proper input validation for any data entry form
An analyst received an alert regarding an application spawning a suspicious command shell process Upon further investigation, the analyst observes the following registry change occurring immediately after the suspicious event:

Which of the following was the suspicious event able to accomplish?
- A . Impair defenses.
- B . Establish persistence.
- C . Bypass file access controls.
- D . Implement beaconing.
A cybersecurity analyst is doing triage in a SIEM and notices that the time stamps between the firewall and the host under investigation are off by 43 minutes.
Which of the following is the most likely scenario occurring with the time stamps?
- A . The NTP server is not configured on the host.
- B . The cybersecurity analyst is looking at the wrong information.
- C . The firewall is using UTC time.
- D . The host with the logs is offline.
HOTSPOT
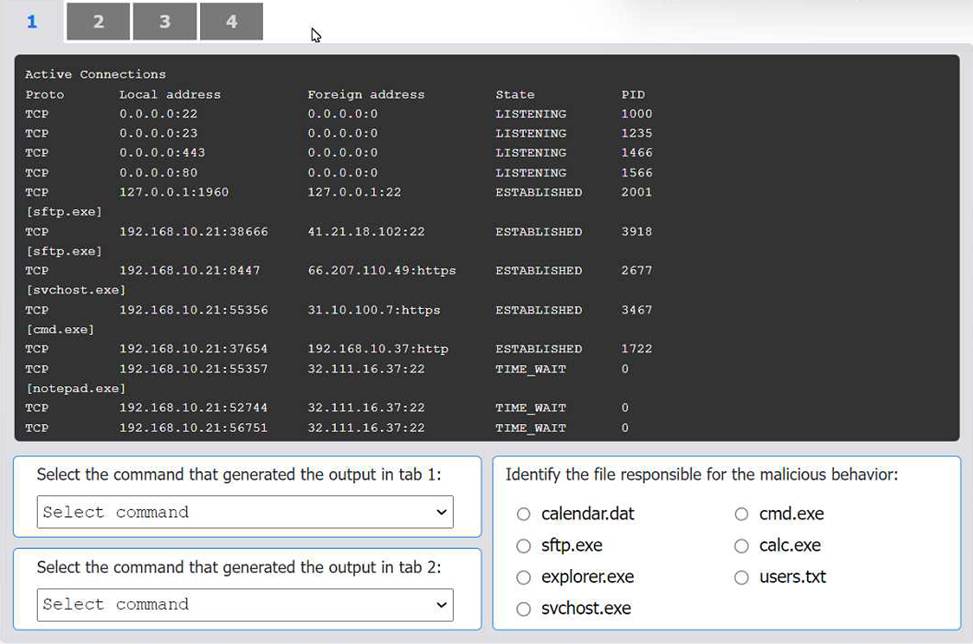
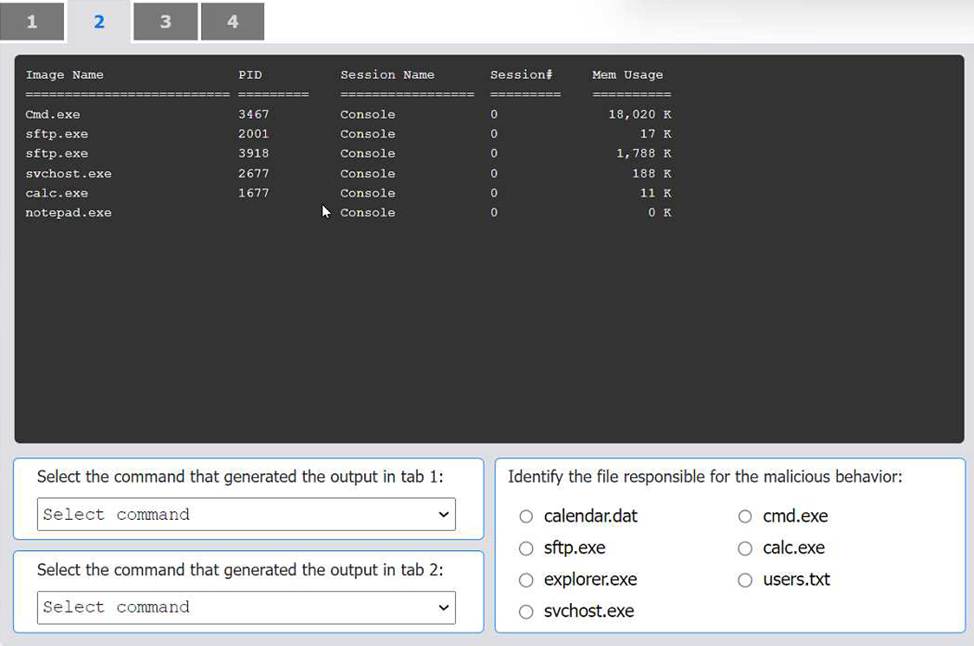
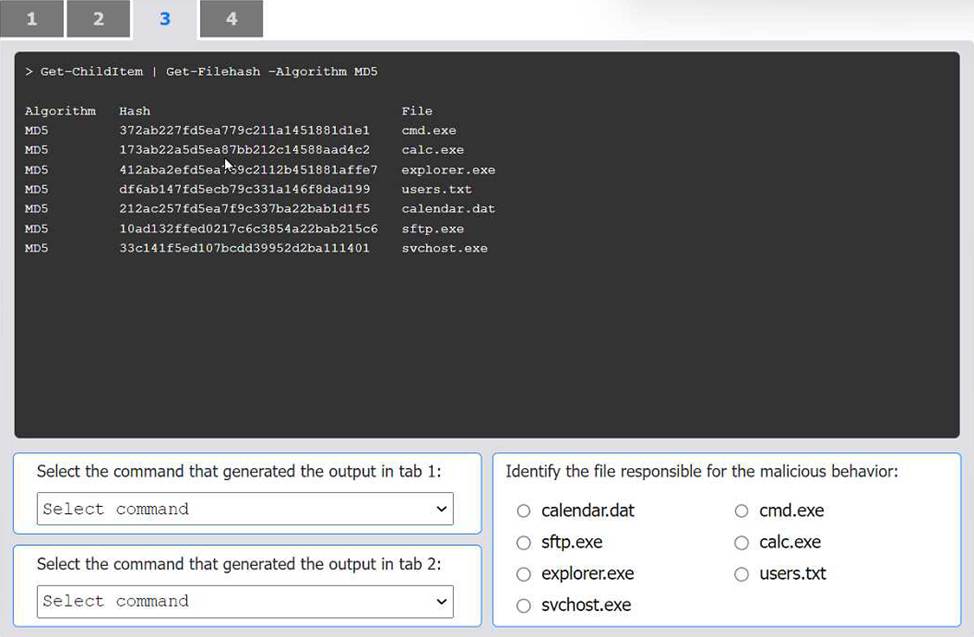
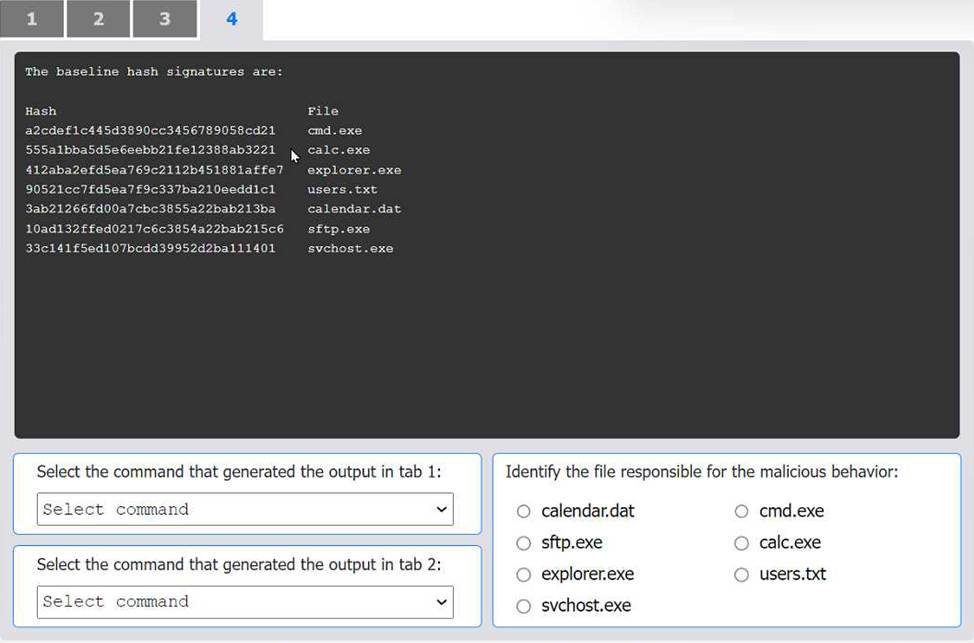
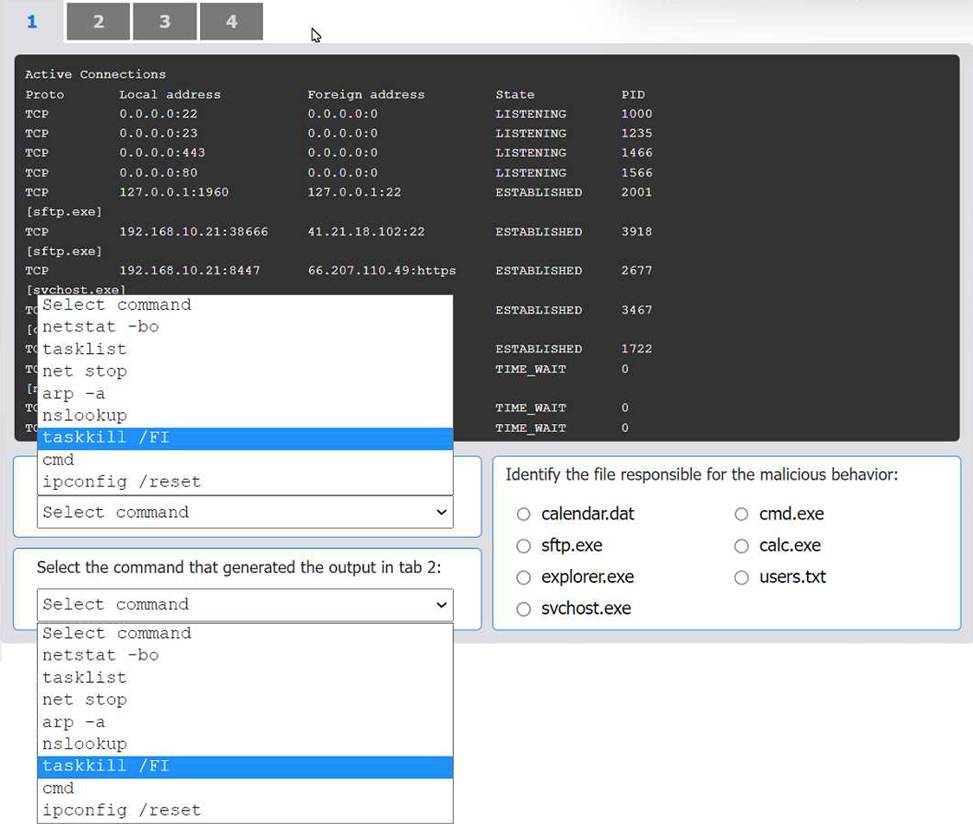
An organization has noticed large amounts of data are being sent out of its network. An analyst is identifying the cause of the data exfiltration.
INSTRUCTIONS
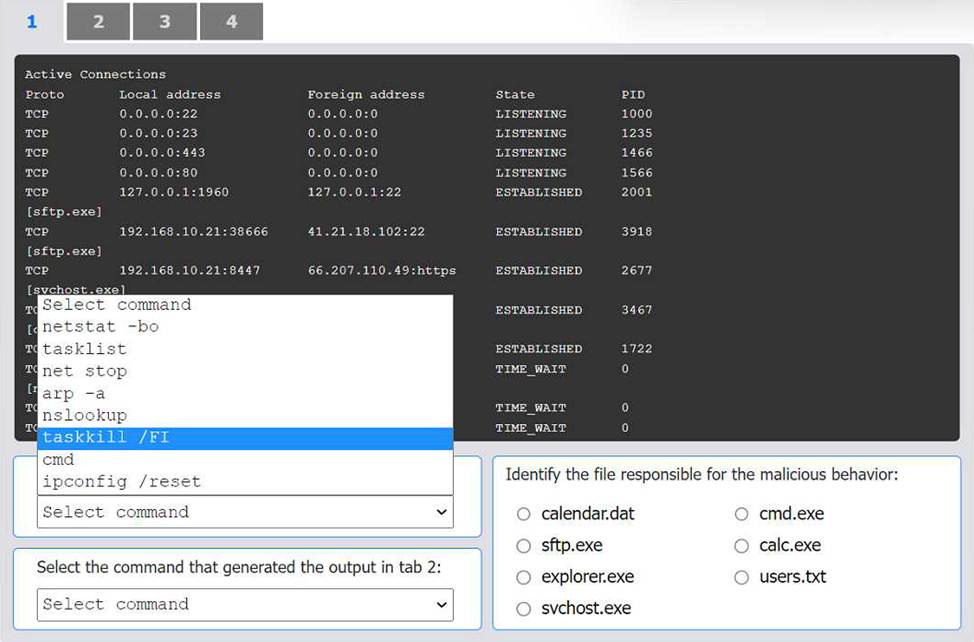
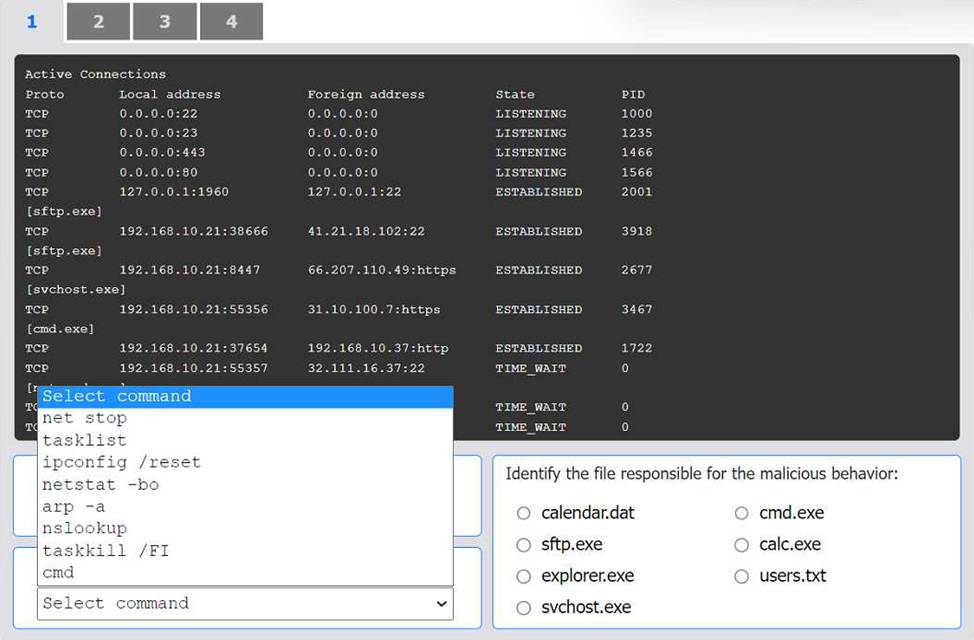
Select the command that generated the output in tabs 1 and 2.
Review the output text in all tabs and identify the file responsible for the malicious behavior.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
A SOC analyst observes reconnaissance activity from an IP address. The activity follows a pattern of short bursts toward a low number of targets. An open-source review shows that the IP has a bad reputation. The perimeter firewall logs indicate the inbound traffic was allowed. The destination hosts are high-value assets with EDR agents installed.
Which of the following is the best action for the SOC to take to protect against any further activity from the source IP?
- A . Add the IP address to the EDR deny list.
- B . Create a SIEM signature to trigger on any activity from the source IP subnet detected by the web proxy or firewalls for immediate notification.
- C . Implement a prevention policy for the IP on the WAF
- D . Activate the scan signatures for the IP on the NGFWs.
The vulnerability analyst reviews threat intelligence regarding emerging vulnerabilities affecting workstations that are used within the company:
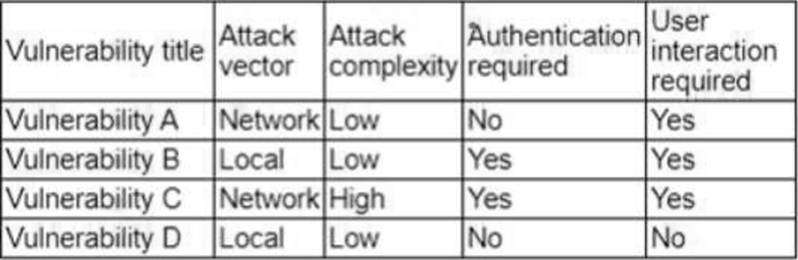
Which of the following vulnerabilities should the analyst be most concerned about, knowing that end users frequently click on malicious links sent via email?
- A . Vulnerability A
- B . Vulnerability B
- C . Vulnerability C
- D . Vulnerability D
Which of the following concepts is using an API to insert bulk access requests from a file into an identity management system an example of?
- A . Command and control
- B . Data enrichment
- C . Automation
- D . Single sign-on