
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A company is aiming to test a new incident response plan. The management team has made it clear that the initial test should have no impact on the environment. The company has limited resources to support testing.
Which of the following exercises would be the best approach?
- A . Tabletop scenarios
- B . Capture the flag
- C . Red team vs. blue team
- D . Unknown-environment penetration test
A cybersecurity analyst notices unusual network scanning activity coming from a country that the company does not do business with.
Which of the following is the best mitigation technique?
- A . Geoblock the offending source country
- B . Block the IP range of the scans at the network firewall.
- C . Perform a historical trend analysis and look for similar scanning activity.
- D . Block the specific IP address of the scans at the network firewall
While reviewing web server logs, a security analyst found the following line:
<IMG SRC=’vbscript:msgbox("test")’>
Which of the following malicious activities was attempted?
- A . Command injection
- B . XML injection
- C . Server-side request forgery
- D . Cross-site scripting
An incident response analyst is investigating the root cause of a recent malware outbreak. Initial binary analysis indicates that this malware disables host security services and performs cleanup routines on it infected hosts, including deletion of initial dropper and removal of event log entries and prefetch files from the host.
Which of the following data sources would most likely reveal evidence of the root cause? (Select two).
- A . Creation time of dropper
- B . Registry artifacts
- C . EDR data
- D . Prefetch files
- E . File system metadata
- F . Sysmon event log
Which of the following is the best reason to implement an MOU?
- A . To create a business process for configuration management
- B . To allow internal departments to understand security responsibilities
- C . To allow an expectation process to be defined for legacy systems
- D . To ensure that all metrics on service levels are properly reported
A security analyst has found the following suspicious DNS traffic while analyzing a packet capture:
• DNS traffic while a tunneling session is active.
• The mean time between queries is less than one second.
• The average query length exceeds 100 characters.
Which of the following attacks most likely occurred?
- A . DNS exfiltration
- B . DNS spoofing
- C . DNS zone transfer
- D . DNS poisoning
When undertaking a cloud migration of multiple SaaS application, an organizations system administrator struggled … identity and access management to cloud-based assets.
Which of the following service models would have reduced the complexity of this project?
- A . CASB
- B . SASE
- C . ZTNA
- D . SWG
An older CVE with a vulnerability score of 7.1 was elevated to a score of 9.8 due to a widely available exploit being used to deliver ransomware.
Which of the following factors would an analyst most likely communicate as the reason for this escalation?
- A . Scope
- B . Weaponization
- C . CVSS
- D . Asset value
A vulnerability scan of a web server that is exposed to the internet was recently completed.
A security analyst is reviewing the resulting vector strings:
Vulnerability 1: CVSS: 3.0/AV: N/AC: L/PR: N/UI: N/S: U/C: H/I: L/A: L
Vulnerability 2: CVSS: 3.0/AV: L/AC: H/PR: N/UI: N/S: U/C: L/I: L/A: H
Vulnerability 3: CVSS: 3.0/AV: A/AC: H/PR: L/UI: R/S: U/C: L/I: H/A: L
Vulnerability 4: CVSS: 3.0/AV: P/AC: L/PR: H/UI: N/S: U/C: H/I: N/A: L
Which of the following vulnerabilities should be patched first?
- A . Vulnerability 1
- B . Vulnerability 2
- C . Vulnerability 3
- D . Vulnerability 4
A security analyst reviews the following Arachni scan results for a web application that stores PII data:
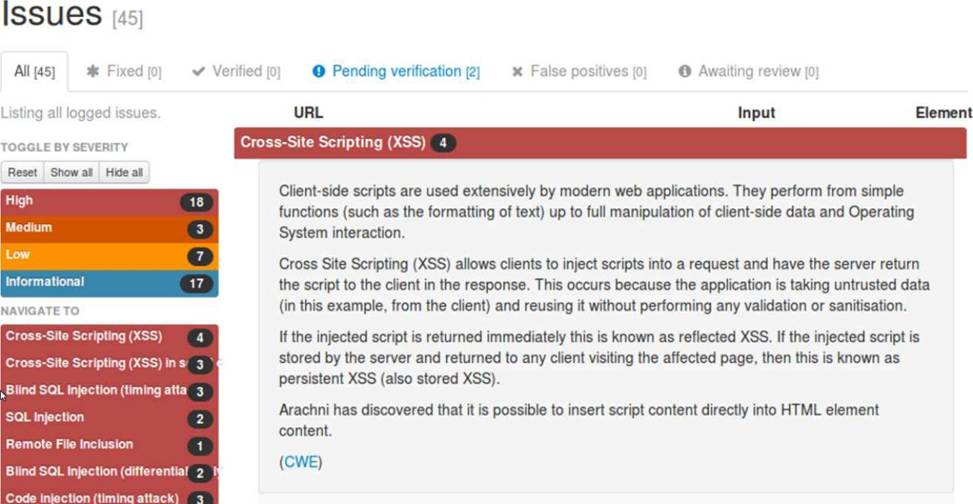
Which of the following should be remediated first?
- A . SQL injection
- B . RFI
- C . XSS
- D . Code injection