
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A network security analyst for a large company noticed unusual network activity on a critical system.
Which of the following tools should the analyst use to analyze network traffic to search for malicious activity?
- A . WAF
- B . Wireshark
- C . EDR
- D . Nmap
A recent vulnerability scan resulted in an abnormally large number of critical and high findings that require patching. The SLA requires that the findings be remediated within a specific amount of time.
Which of the following is the best approach to ensure all vulnerabilities are patched in accordance with the SLA?
- A . Integrate an IT service delivery ticketing system to track remediation and closure.
- B . Create a compensating control item until the system can be fully patched.
- C . Accept the risk and decommission current assets as end of life.
- D . Request an exception and manually patch each system.
An analyst discovers unusual outbound connections to an IP that was previously blocked at the web proxy and firewall. Upon further investigation, it appears that the proxy and firewall rules that were in place were removed by a service account that is not recognized.
Which of the following parts of the Cyber Kill Chain does this describe?
- A . Delivery
- B . Command and control
- C . Reconnaissance
- D . Weaporization
An incident response team receives an alert to start an investigation of an internet outage. The outage is preventing all users in multiple locations from accessing external SaaS resources. The team determines the organization was impacted by a DDoS attack.
Which of the following logs should the team review first?
- A . CDN
- B . Vulnerability scanner
- C . DNS
- D . Web server
SIMULATION
An organization’s website was maliciously altered.
INSTRUCTIONS
Review information in each tab to select the source IP the analyst should be concerned about, the indicator of compromise, and the two appropriate corrective actions.
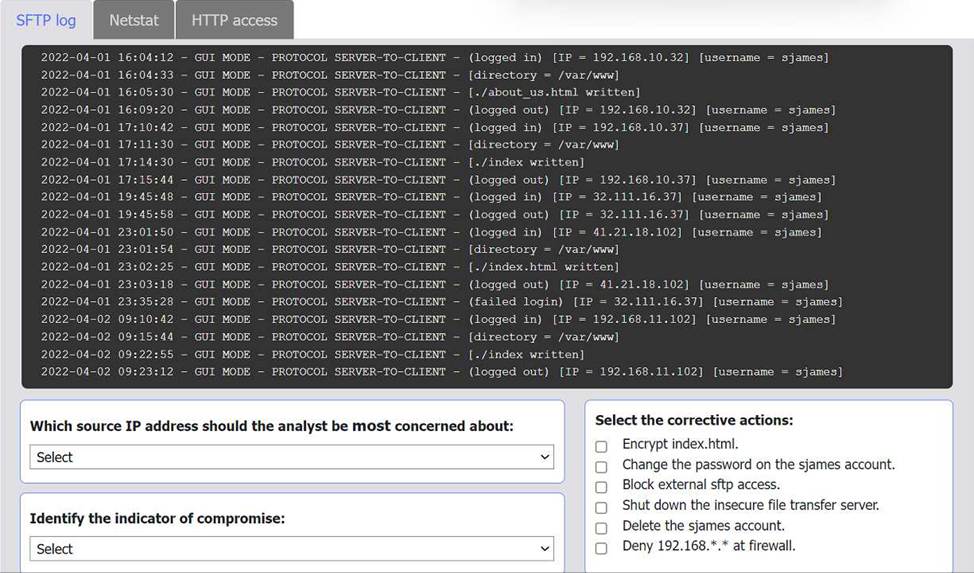
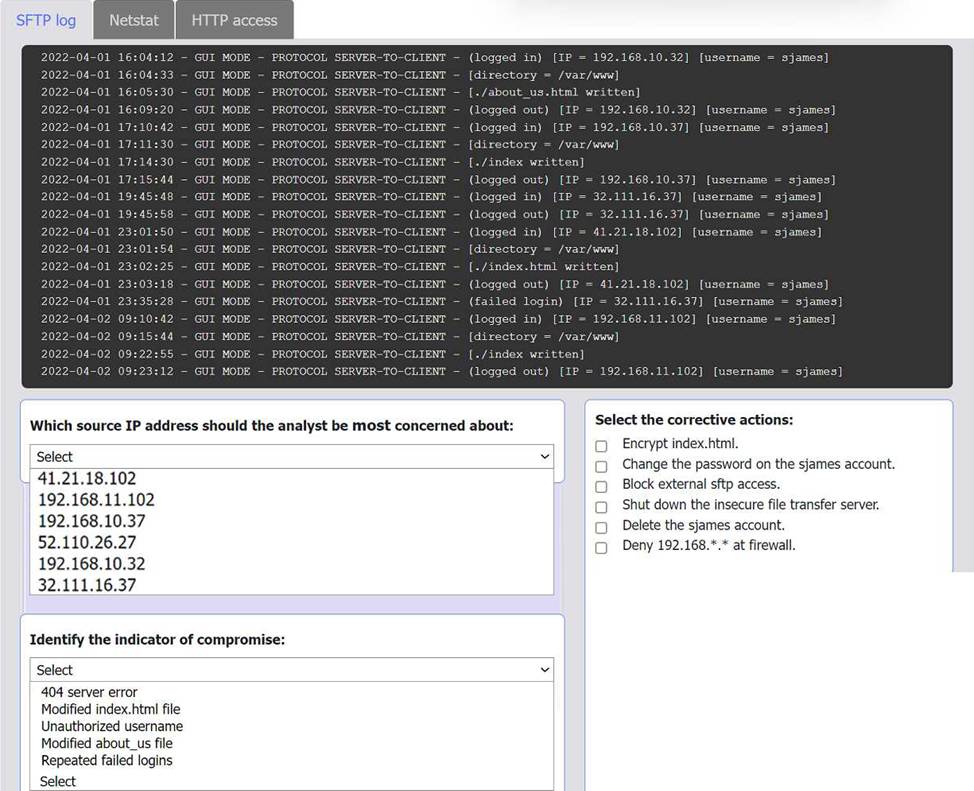
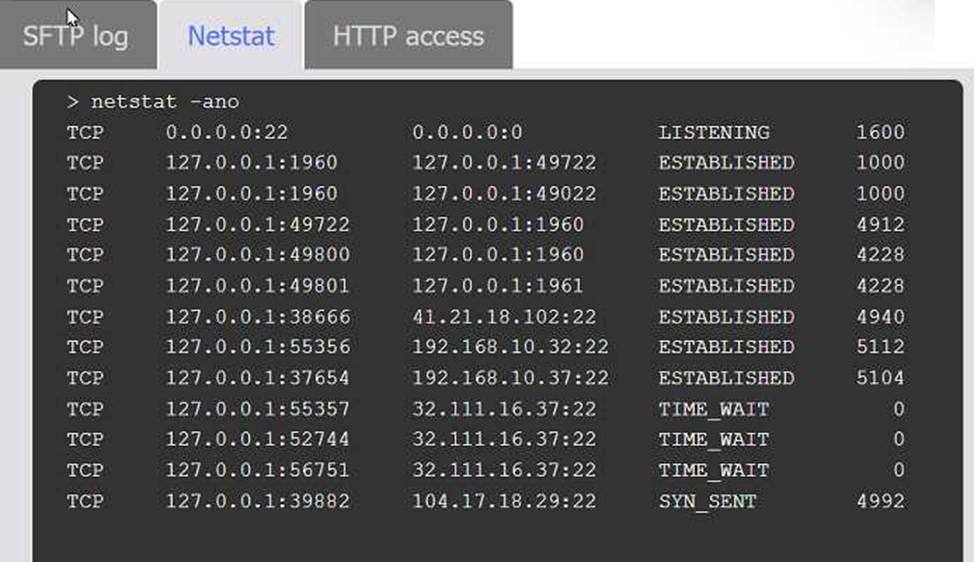
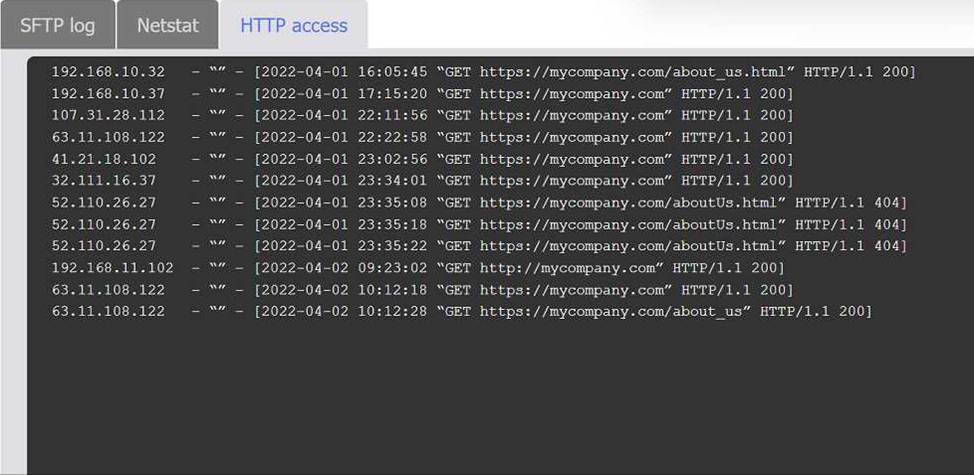
Patches for two highly exploited vulnerabilities were released on the same Friday afternoon.
Information about the systems and vulnerabilities is shown in the tables below:
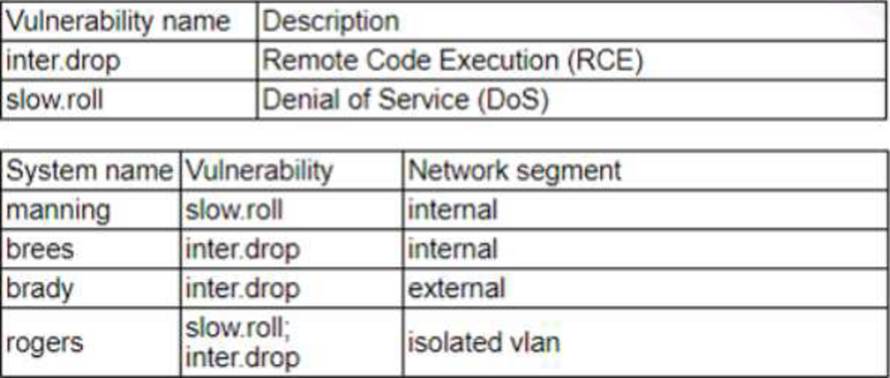
Which of the following should the security analyst prioritize for remediation?
- A . rogers
- B . brady
- C . brees
- D . manning
Which of following would best mitigate the effects of a new ransomware attack that was not properly stopped by the company antivirus?
- A . Install a firewall.
- B . Implement vulnerability management.
- C . Deploy sandboxing.
- D . Update the application blocklist.
Which of the following tools would work best to prevent the exposure of PII outside of an organization?
- A . PAM
- B . IDS
- C . PKI
- D . DLP
An analyst reviews a recent government alert on new zero-day threats and finds the following CVE metrics for the most critical of the vulnerabilities:
CVSS: 3.1/AV:N/AC: L/PR:N/UI:N/S:C/C:H/I:H/A:H/E:U/RL:W/RC:R
Which of the following represents the exploit code maturity of this critical vulnerability?
- A . E:U
- B . S:C
- C . RC:R
- D . AV:N
- E . AC:L
Following an attack, an analyst needs to provide a summary of the event to the Chief Information Security Officer. The summary needs to include the who-what-when information and evaluate the effectiveness of the plans in place.
Which of the following incident management life cycle processes
does this describe?
- A . Business continuity plan
- B . Lessons learned
- C . Forensic analysis
- D . Incident response plan