
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
HOTSPOT
A security analyst performs various types of vulnerability scans.
Review the vulnerability scan results to determine the type of scan that was executed and if a false positive occurred for each device. Instructions:
Select the Results Generated drop-down option to determine if the results were generated from a credentialed scan, non-credentialed scan, or a compliance scan.
For ONLY the credentialed and non-credentialed scans, evaluate the results for false positives and check the findings that display false positives. NOTE: If you would like to uncheck an option that is currently selected, click on the option a second time.
Lastly, based on the vulnerability scan results, identify the type of Server by dragging the Server to the results.
The Linux Web Server, File-Print Server and Directory Server are draggable.
If at any time you would like to bring back the initial state of the simulation, please select the Reset All button. When you have completed the simulation, please select the Done button to submit. Once the simulation is submitted, please select the Next button to continue.
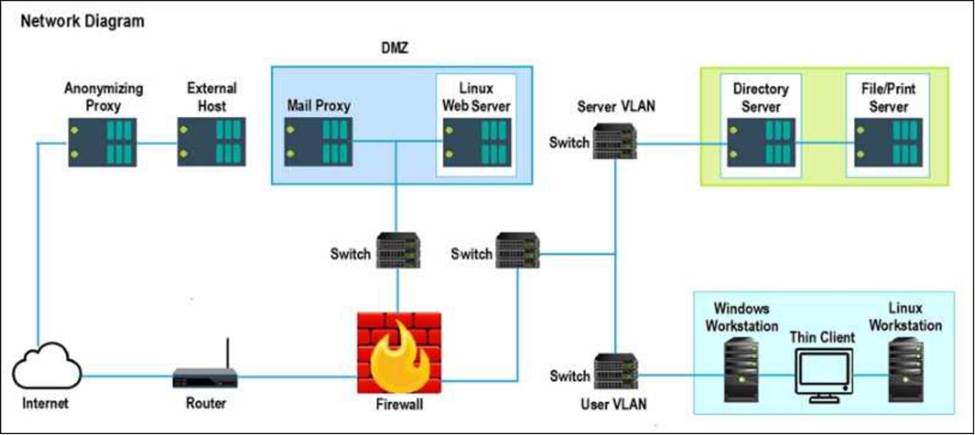
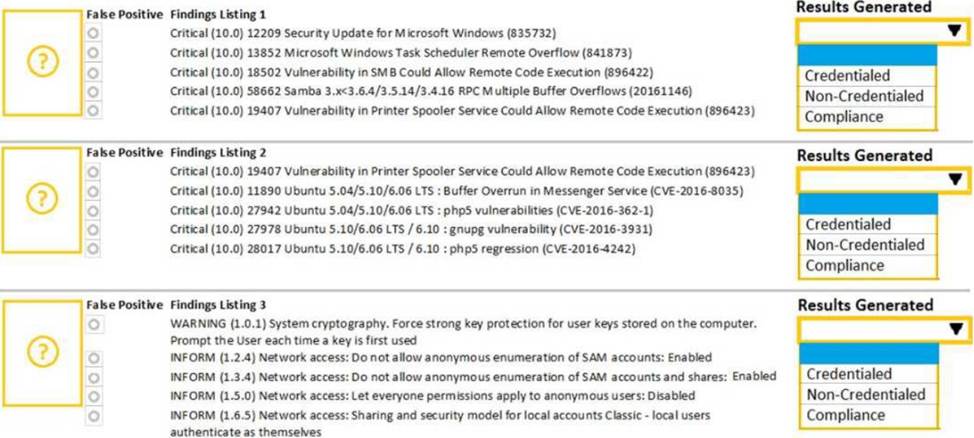
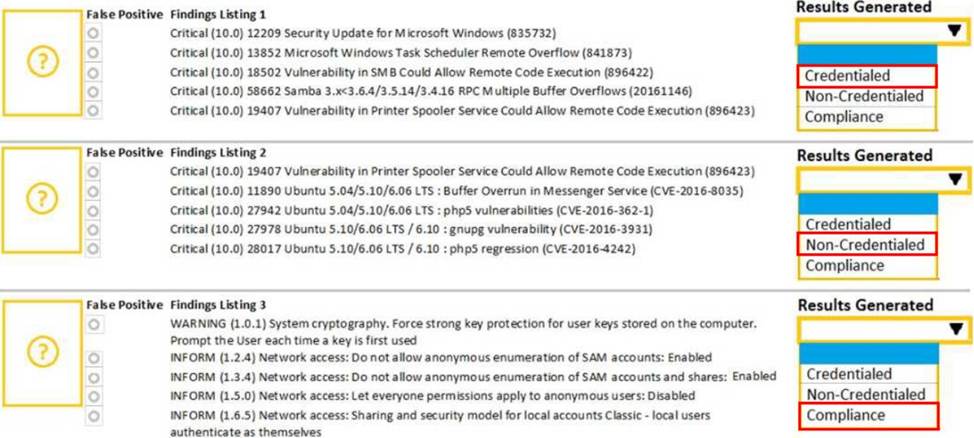
An analyst is becoming overwhelmed with the number of events that need to be investigated for a timeline.
Which of the following should the analyst focus on in order to move the incident forward?
- A . Impact
- B . Vulnerability score
- C . Mean time to detect
- D . Isolation
A security analyst has prepared a vulnerability scan that contains all of the company’s functional subnets. During the initial scan, users reported that network printers began to print pages that contained unreadable text and icons.
Which of the following should the analyst do to ensure this behavior does not oocur during subsequent vulnerability scans?
- A . Perform non-credentialed scans.
- B . Ignore embedded web server ports.
- C . Create a tailored scan for the printer subnet.
- D . Increase the threshold length of the scan timeout.
An organization implemented an extensive firewall access-control blocklist to prevent internal network ranges from communicating with a list of IP addresses of known command-and-control domains A security analyst wants to reduce the load on the firewall.
Which of the following can the analyst implement to achieve similar protection and reduce the load on the firewall?
- A . A DLP system
- B . DNS sinkholing
- C . IP address allow list
- D . An inline IDS
Which of the following is often used to keep the number of alerts to a manageable level when establishing a process to track and analyze violations?
- A . Log retention
- B . Log rotation
- C . Maximum log size
- D . Threshold value
A team of analysts is developing a new internal system that correlates information from a variety of sources analyzes that information, and then triggers notifications according to company policy.
Which of the following technologies was deployed?
- A . SIEM
- B . SOAR
- C . IPS
- D . CERT
New employees in an organization have been consistently plugging in personal webcams despite the company policy prohibiting use of personal devices. The SOC manager discovers that new employees are not aware of the company policy.
Which of the following will the SOC manager most likely recommend to help ensure new employees are accountable for following the company policy?
- A . Human resources must email a copy of a user agreement to all new employees
- B . Supervisors must get verbal confirmation from new employees indicating they have read the user agreement
- C . All new employees must take a test about the company security policy during the cjitoardmg process
- D . All new employees must sign a user agreement to acknowledge the company security policy
New employees in an organization have been consistently plugging in personal webcams despite the company policy prohibiting use of personal devices. The SOC manager discovers that new employees are not aware of the company policy.
Which of the following will the SOC manager most likely recommend to help ensure new employees are accountable for following the company policy?
- A . Human resources must email a copy of a user agreement to all new employees
- B . Supervisors must get verbal confirmation from new employees indicating they have read the user agreement
- C . All new employees must take a test about the company security policy during the cjitoardmg process
- D . All new employees must sign a user agreement to acknowledge the company security policy
Which of the following is the BEST option to protect a web application against CSRF attacks?
- A . Update the web application to the latest version.
- B . Set a server-side rate limit for CSRF token generation.
- C . Avoid the transmission of CSRF tokens using cookies.
- D . Configure the web application to only use HTTPS and TLS 1.3.
Which of the following best describes the process of requiring remediation of a known threat within a given time frame?
- A . SLA
- B . MOU
- C . Best-effort patching
- D . Organizational governance