
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Which of the following software assessment methods world peak times?
- A . Security regression testing
- B . Stress testing
- C . Static analysis testing
- D . Dynamic analysis testing
- E . User acceptance testing
Which of the following describes how a CSIRT lead determines who should be communicated with and when during a security incident?
- A . The lead should review what is documented in the incident response policy or plan
- B . Management level members of the CSIRT should make that decision
- C . The lead has the authority to decide who to communicate with at any t me
- D . Subject matter experts on the team should communicate with others within the specified area of expertise
While a security analyst for an organization was reviewing logs from web servers. the analyst found several successful attempts to downgrade HTTPS sessions to use cipher modes of operation susceptible to padding oracle attacks.
Which of the following combinations of configuration changes should the organization make to remediate this issue? (Select two).
- A . Configure the server to prefer TLS 1.3.
- B . Remove cipher suites that use CBC.
- C . Configure the server to prefer ephemeral modes for key exchange.
- D . Require client browsers to present a user certificate for mutual authentication.
- E . Configure the server to require HSTS.
- F . Remove cipher suites that use GCM.
You are a penetration tester who is reviewing the system hardening guidelines for a company.
Hardening guidelines indicate the following.
There must be one primary server or service per device.
Only default port should be used
Non- secure protocols should be disabled.
The corporate internet presence should be placed in a protected subnet
Instructions:
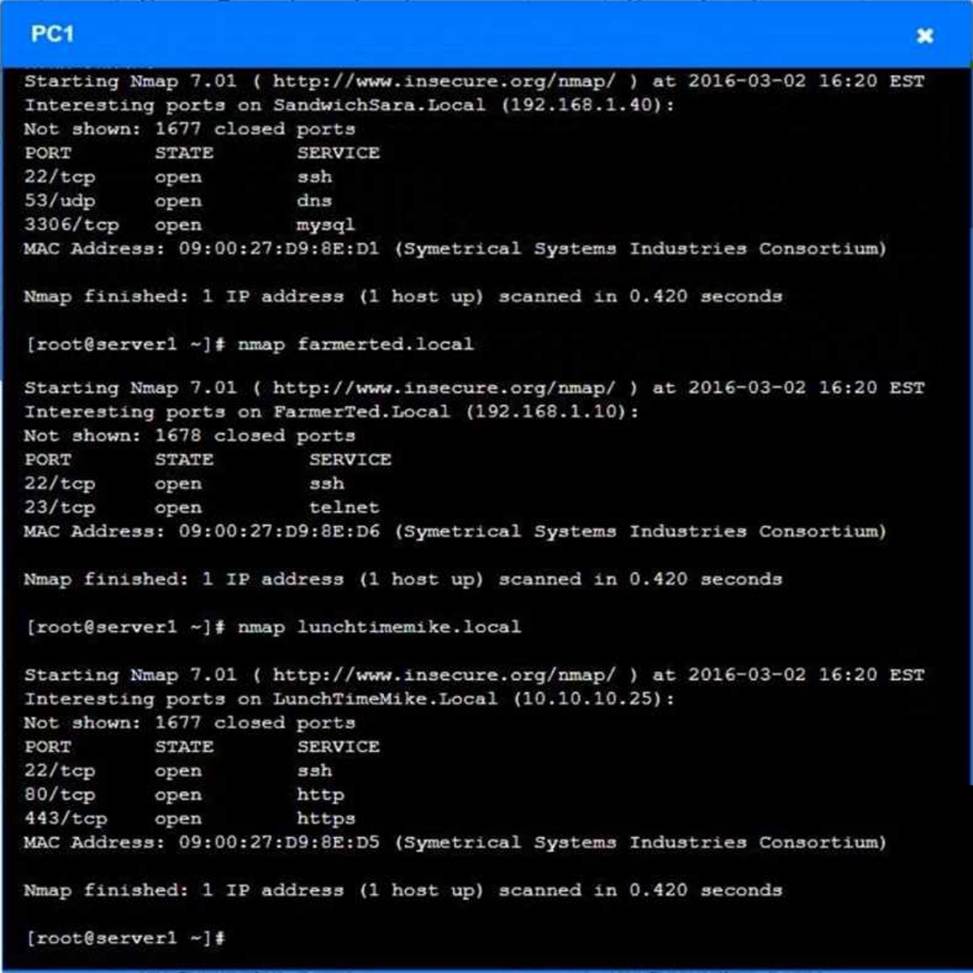
Using the available tools, discover devices on the corporate network and the services running on these devices.
You must determine
ip address of each device
The primary server or service each device
The protocols that should be disabled based on the hardening guidelines
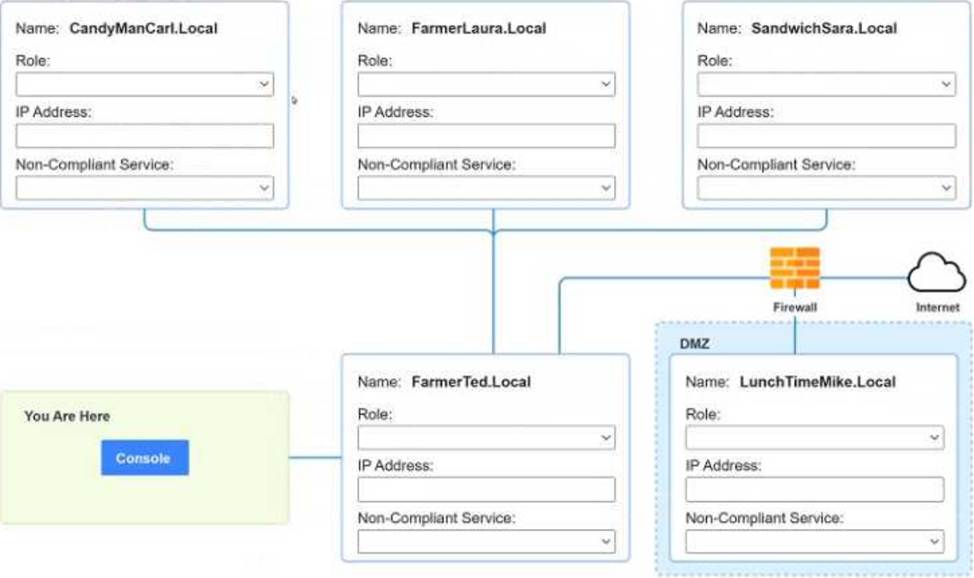
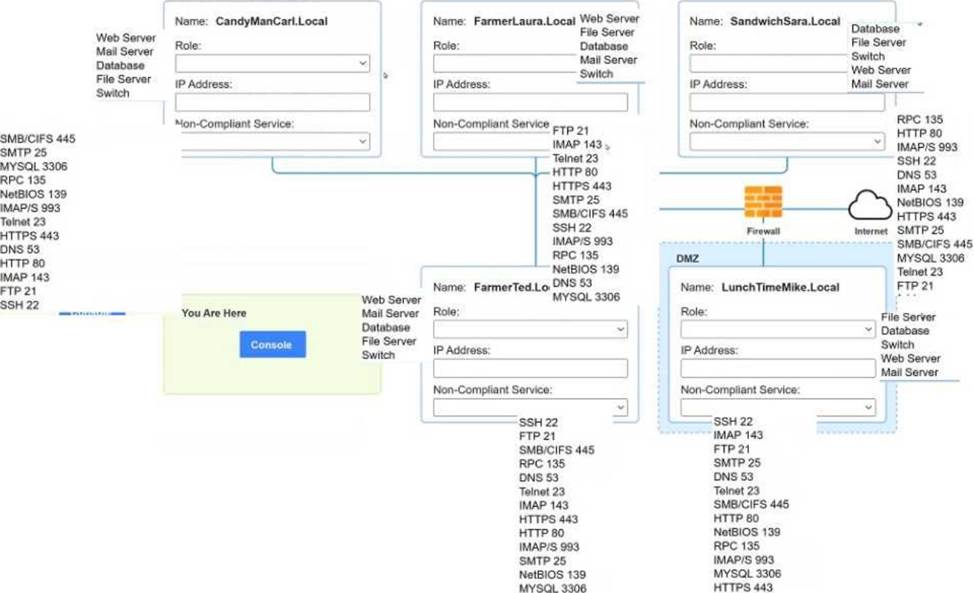
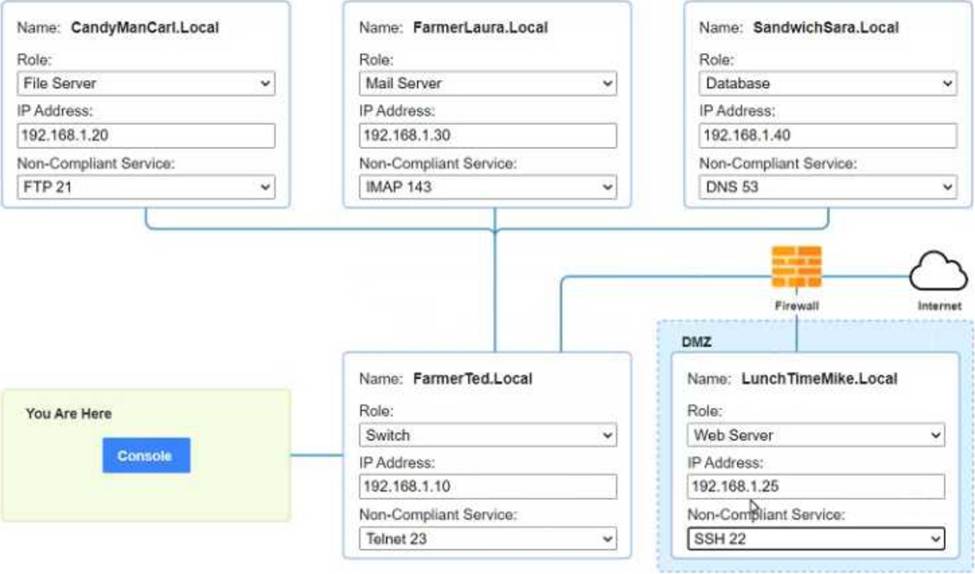
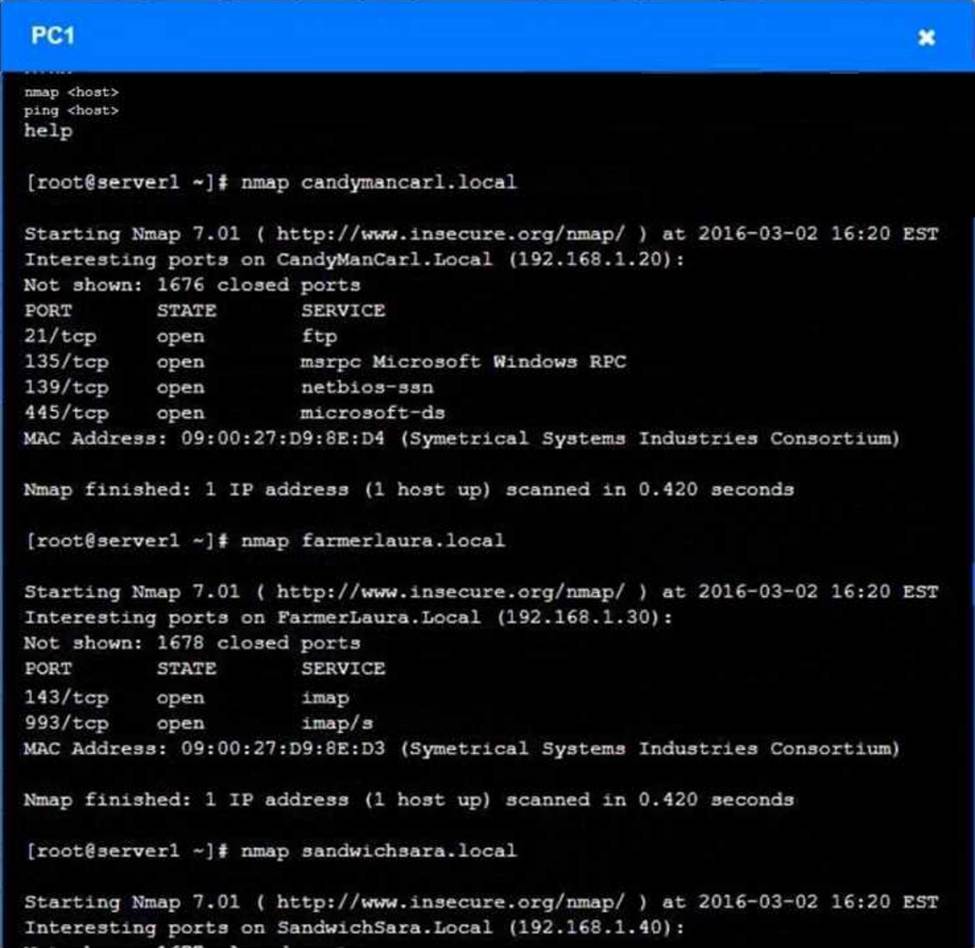
Due to an incident involving company devices, an incident responder needs to take a mobile phone to the lab for further investigation.
Which of the following tools should be used to maintain the integrity of the mobile phone while it is transported? (Select two).
- A . Signal-shielded bag
- B . Tamper-evident seal
- C . Thumb drive
- D . Crime scene tape
- E . Write blocker
- F . Drive duplicator
A technician working at company.com received the following email:
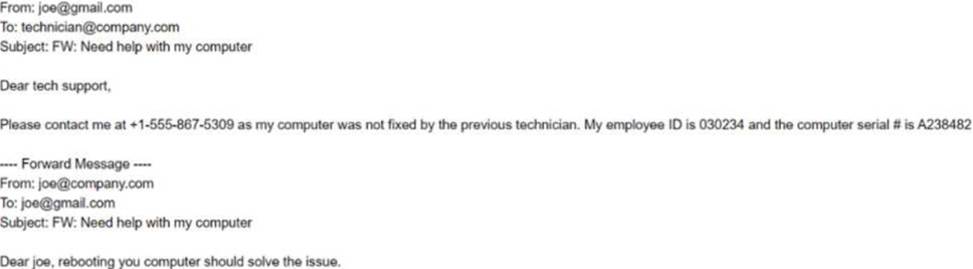
After looking at the above communication, which of the following should the technician recommend to the security team to prevent exposure of sensitive information and reduce the risk of corporate data being stored on non-corporate assets?
- A . Forwarding of corporate email should be disallowed by the company.
- B . A VPN should be used to allow technicians to troubleshoot computer issues securely.
- C . An email banner should be implemented to identify emails coming from external sources.
- D . A rule should be placed on the DLP to flag employee IDs and serial numbers.
An attacker has just gained access to the syslog server on a LAN. Reviewing the syslog entries has allowed the attacker to prioritize possible next targets.
Which of the following is this an example of?
- A . Passive network foot printing
- B . OS fingerprinting
- C . Service port identification
- D . Application versioning
Which of the following responsibilities does the legal team have during an incident management event? (Select two).
- A . Coordinate additional or temporary staffing for recovery efforts.
- B . Review and approve new contracts acquired as a result of an event.
- C . Advise the Incident response team on matters related to regulatory reporting.
- D . Ensure all system security devices and procedures are in place.
- E . Conduct computer and network damage assessments for insurance.
- F . Verify that all security personnel have the appropriate clearances.
An incident response team found IoCs in a critical server. The team needs to isolate and collect technical evidence for further investigation.
Which of the following pieces of data should be collected first in order to preserve sensitive information before isolating the server?
- A . Hard disk
- B . Primary boot partition
- C . Malicious tiles
- D . Routing table
- E . Static IP address
While reviewing the web server logs a security analyst notices the following snippet
…./…./boot.ini
Which of the following is being attempted?
- A . Directory traversal
- B . Remote file inclusion
- C . Cross-site scripting
- D . Remote code execution
- E . Enumeration of/etc/pasawd