
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A cybersecurity team has witnessed numerous vulnerability events recently that have affected operating systems. The team decides to implement host-based IPS, firewalls, and two-factor authentication.
Which of the following does this most likely describe?
- A . System hardening
- B . Hybrid network architecture
- C . Continuous authorization
- D . Secure access service edge
A company creates digitally signed packages for its devices.
Which of the following best describes the
method by which the security packages are delivered to the company’s customers?
- A . Antitamper mechanism
- B . SELinux
- C . Trusted firmware updates
- D . eFuse
A risk assessment concludes that the perimeter network has the highest potential for compromise by
an attacker, and it is labeled as a critical risk environment.
Which of the following is a valid compensating control to reduce the volume of valuable information in the perimeter network that an attacker could gain using active reconnaissance techniques?
- A . A control that demonstrates that all systems authenticate using the approved authentication method
- B . A control that demonstrates that access to a system is only allowed by using SSH
- C . A control that demonstrates that firewall rules are peer reviewed for accuracy and approved before deployment
- D . A control that demonstrates that the network security policy is reviewed and updated yearly
During an audit, several customer order forms were found to contain inconsistencies between the actual price of an item and the amount charged to the customer. Further investigation narrowed the cause of the issue to manipulation of the public-facing web form used by customers to order products.
Which of the following would be the best way to locate this issue?
- A . Reduce the session timeout threshold
- B . Deploy MFA for access to the web server.
- C . Implement input validation.
- D . Run a dynamic code analysis.
A company’s security team is updating a section of the reporting policy that pertains to inappropriate use of resources (e.g., an employee who installs crypto miners on workstations in the office).
Besides the security team, which of the following groups should the issue be escalated to first in order to comply with industry best practices?
- A . Help desk
- B . Law enforcement
- C . Legal department
- D . Board member
When starting an investigation, which of the following must be done first?
- A . Notify law enforcement
- B . Secure the scene
- C . Seize all related evidence
- D . Interview the witnesses
A laptop that is company owned and managed is suspected to have malware. The company implemented centralized security logging.
Which of the following log sources will confirm the malware infection?
- A . XDR logs
- B . Firewall logs
- C . IDS logs
- D . MFA logs
A company has a primary control in place to restrict access to a sensitive database. However, the company discovered an authentication vulnerability that could bypass this control.
Which of the following is the best compensating control?
- A . Running regular penetration tests to identify and address new vulnerabilities
- B . Conducting regular security awareness training of employees to prevent social engineering attacks
- C . Deploying an additional layer of access controls to verify authorized individuals
- D . Implementing intrusion detection software to alert security teams of unauthorized access attempts
A security analyst is reviewing events that occurred during a possible compromise.
The analyst obtains the following log:
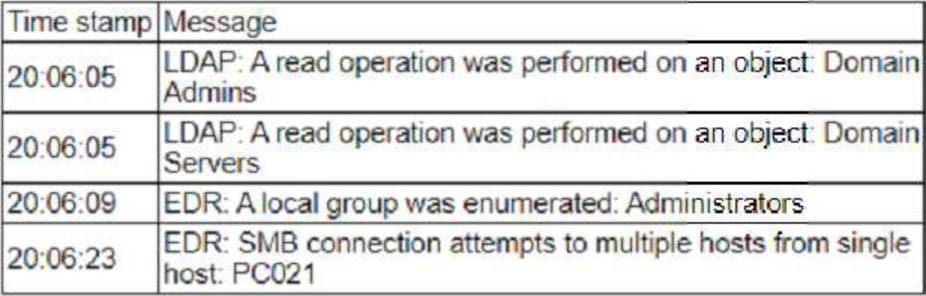
Which of the following is most likely occurring, based on the events in the log?
- A . An adversary is attempting to find the shortest path of compromise.
- B . An adversary is performing a vulnerability scan.
- C . An adversary is escalating privileges.
- D . An adversary is performing a password stuffing attack.
The analyst reviews the following endpoint log entry:

Which of the following has occurred?
- A . Registry change
- B . Rename computer
- C . New account introduced
- D . Privilege escalation