
CompTIA CS0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: CS0-003
- Exam Name: CompTIA Cybersecurity Analyst (CySA+) Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
Which of the following explains the importance of a timeline when providing an incident response report?
- A . The timeline contains a real-time record of an incident and provides information that helps to simplify a postmortem analysis.
- B . An incident timeline provides the necessary information to understand the actions taken to mitigate the threat or risk.
- C . The timeline provides all the information, in the form of a timetable, of the whole incident response process including actions taken.
- D . An incident timeline presents the list of commands executed by an attacker when the system was compromised, in the form of a timetable.
Which of the following best describes the key goal of the containment stage of an incident response process?
- A . To limit further damage from occurring
- B . To get services back up and running
- C . To communicate goals and objectives of the incident response plan
- D . To prevent data follow-on actions by adversary exfiltration
During a security test, a security analyst found a critical application with a buffer overflow vulnerability.
Which of the following would be best to mitigate the vulnerability at the application level?
- A . Perform OS hardening.
- B . Implement input validation.
- C . Update third-party dependencies.
- D . Configure address space layout randomization.
The security team at a company, which was a recent target of ransomware, compiled a list of hosts that were identified as impacted and in scope for this incident.
Based on the following host list:
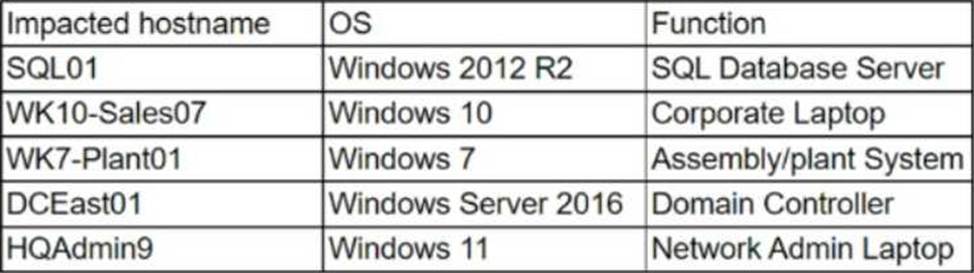
Which of the following systems was most pivotal to the threat actor in its distribution of the encryption binary via Group Policy?
- A . SQL01
- B . WK10-Sales07
- C . WK7-Plant01
- D . DCEast01
- E . HQAdmin9
A cybersecurity analyst is reviewing SIEM logs and observes consistent requests originating from an internal host to a blocklisted external server.
Which of the following best describes the activity that is taking place?
- A . Data exfiltration
- B . Rogue device
- C . Scanning
- D . Beaconing
Which of the following is a useful tool for mapping, tracking, and mitigating identified threats and vulnerabilities with the likelihood and impact of occurrence?
- A . Risk register
- B . Vulnerability assessment
- C . Penetration test
- D . Compliance report
An attacker recently gained unauthorized access to a financial institution’s database, which contains confidential information. The attacker exfiltrated a large amount of data before being detected and blocked. A security analyst needs to complete a root cause analysis to determine how the attacker was able to gain access.
Which of the following should the analyst perform first?
- A . Document the incident and any findings related to the attack for future reference.
- B . Interview employees responsible for managing the affected systems.
- C . Review the log files that record all events related to client applications and user access.
- D . Identify the immediate actions that need to be taken to contain the incident and minimize damage.
A security alert was triggered when an end user tried to access a website that is not allowed per organizational policy. Since the action is considered a terminable offense, the SOC analyst collects the authentication logs, web logs, and temporary files, reflecting the web searches from the user’s workstation, to build the case for the investigation.
Which of the following is the best way to ensure that the investigation complies with HR or privacy policies?
- A . Create a timeline of events detailinq the date stamps, user account hostname and IP information associated with the activities
- B . Ensure that the case details do not reflect any user-identifiable information Password protect the evidence and restrict access to personnel related to the investigation
- C . Create a code name for the investigation in the ticketing system so that all personnel with access will not be able to easily identity the case as an HR-related investigation
- D . Notify the SOC manager for awareness after confirmation that the activity was intentional
An analyst is conducting routine vulnerability assessments on the company infrastructure. When performing these scans, a business-critical server crashes, and the cause is traced back to the vulnerability scanner.
Which of the following is the cause of this issue?
- A . The scanner is running without an agent installed.
- B . The scanner is running in active mode.
- C . The scanner is segmented improperly.
- D . The scanner is configured with a scanning window.
An analyst needs to provide recommendations based on a recent vulnerability scan:
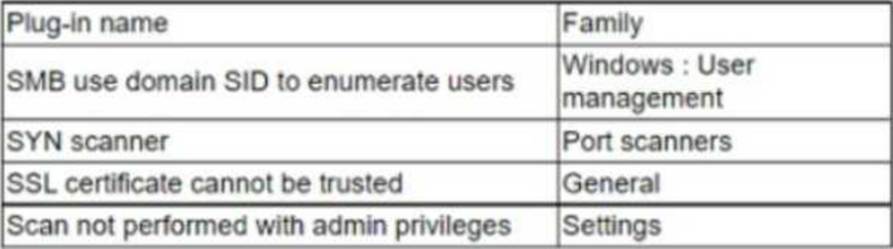
Which of the following should the analyst recommend addressing to ensure potential vulnerabilities are identified?
- A . SMB use domain SID to enumerate users
- B . SYN scanner
- C . SSL certificate cannot be trusted
- D . Scan not performed with admin privileges