
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Refer to the exhibit.
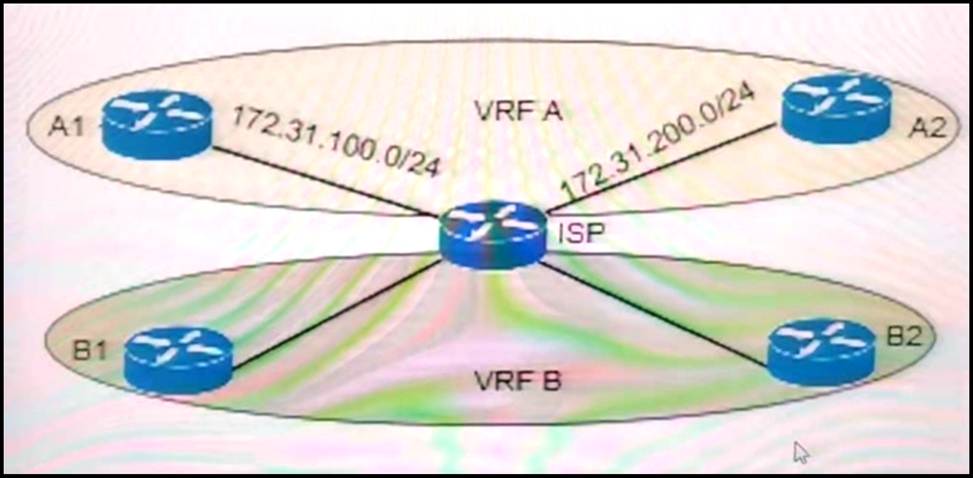
The ISP router is fully configured for customer A and customer B using the VRF-Lite feature.
What is the minimum configuration required for customer A to communicate between routers A1 and A2?
- A . A1
interface fa0/0
description To->ISP
ip add 172.31.100.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.100.1 0.0.0.255 area 0
A2
interface fa0/0
description To->ISP
ip add 172.31.200.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.200.1 0.0.0.255 area 0 - B . A1
interface fa0/0
description To->ISP
ip vrf forwarding A
ip add 172.31.100.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.100.1 0.0.0.255 area 0
A2
interface fa0/0
description To->ISP
ip vrf forwarding A
ip add 172.31.200.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.200.1 0.0.0.255 area 0 - C . A1
interface fa0/0
description To->ISP
ip add 172.31.200.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.200.1 0.0.0.255 area 0
A2
interface fa0/0
description To->ISP
ip add 172.31.100.1 255.255.255.0
no shut
!
router ospf 100
net 172.31.100.1 0.0.0.255 area 0 - D . A1
interface fa0/0
description To->ISP
ip vrf forwarding A
ip add 172.31.100.1 255.255.255.0
no shut
!
router ospf 100 vrf A
net 172.31.200.1 0.0.0.255 area 0
A2
interface fa0/0
description To->ISP
ip vrf forwarding A
ip add 172.31.100.1 255.255.255.0
no shut
!
router ospf 100 vrf A
net 172.31.200.1 0.0.0.255 area 0
C
Explanation:
A1 and A2 routers do not know they belong to VRF A.
The two interfaces of ISP (which are connected to A1 & A2) should be configured like this (we only show the configure of one interface):
ISP router:
interface g0/0
description ISP->To_CustomerA
ip vrf forwarding A
ip address 172.31.100.2 255.255.255.0
router ospf 100 vrf A
network 172.31.200.2 0.0.0.255 area 0
Refer to the exhibit.
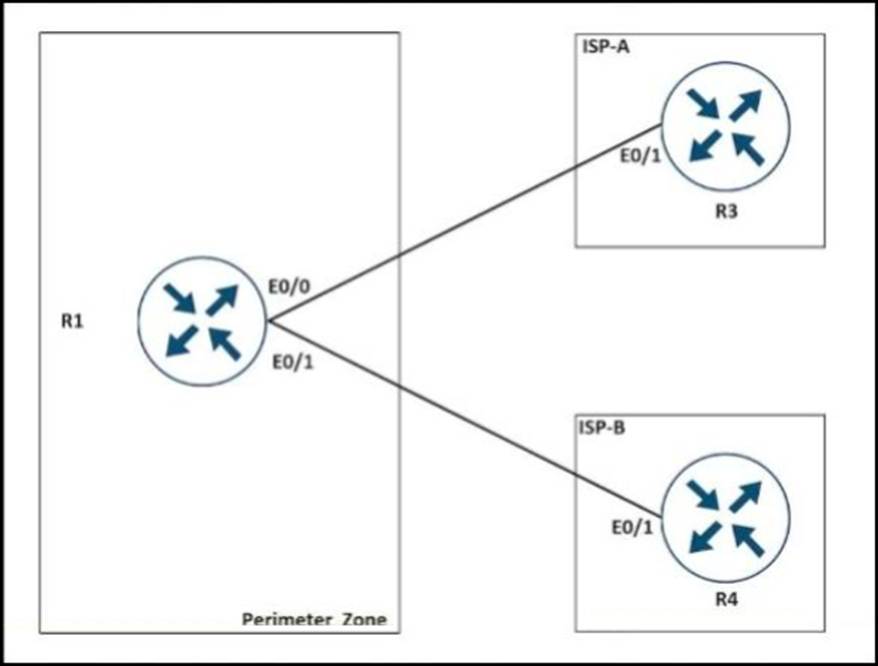
A network is under a cyberattack. A network engineer connected to R1 by SSH and enabled the terminal monitor via SSH session to find the source and destination of the attack. The session was flooded with messages, which made it impossible for the engineer to troubleshoot the issue.
Which command resolves this issue on R1?
- A . no terminal monitor
- B . (config)#terminal no monitor
- C . #terminal no monitor
- D . (config)#no terminal monitor
C
Explanation:
To turn off terminal monitor, use “terminal no monitor” in the enable mode
Refer to the exhibit.
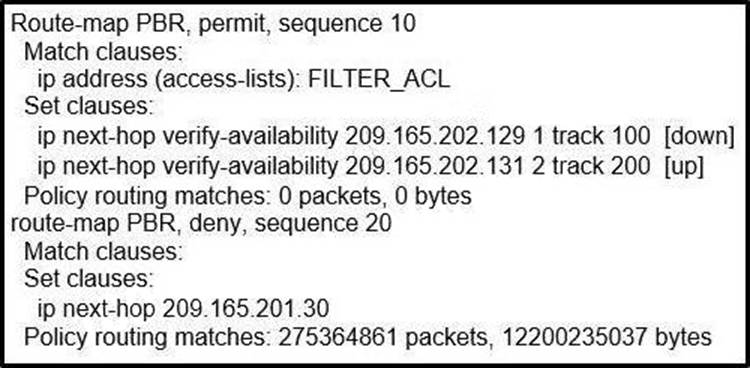
An engineer has configured policy-based routing and applied the configured to the correct interface.
How is the configuration applied to the traffic that matches the access list?
- A . It is sent to 209.165.202.131.
- B . It is sent to 209.165.202.129.
- C . It is dropped.
- D . It is forwarded using the routing table lookup.
A
Explanation:
The set ip next-hop verify-availability command in route-map configuration mode to configure policy routing to verify the reachability of the next hop of a route map before the router performs policy routing to that next hop. In this question we see track 100 is down so the PBR will not use this next-hop, it will use the second next-hop with track 200 (up).
Refer to the exhibit.
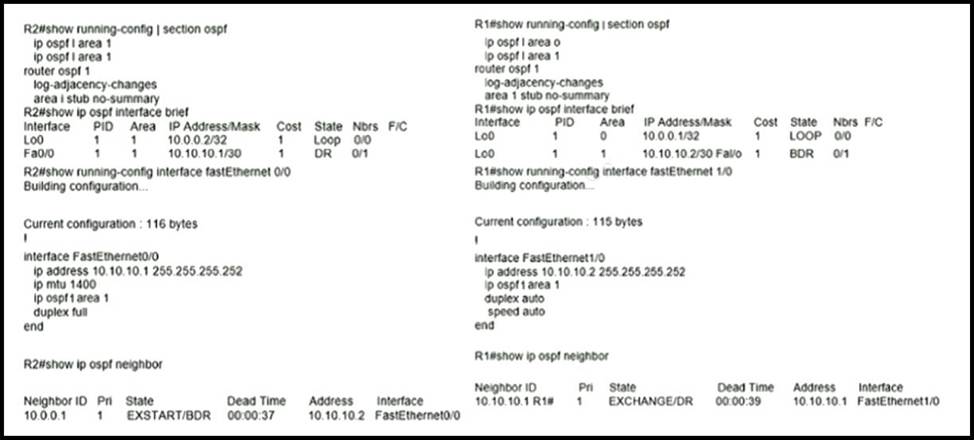
Which action restores OSPF adjacency between R1 and R2?
- A . Change the IP MTU of R1 Fa1/0 to 1300
- B . Change the IP MTU of R2 Fa0/0 to 1300
- C . Change the IP MTU of R1 Fa1/0 to 1500
- D . Change the IP MTU of R2 Fa0/0 to 1500
Refer to the exhibit.
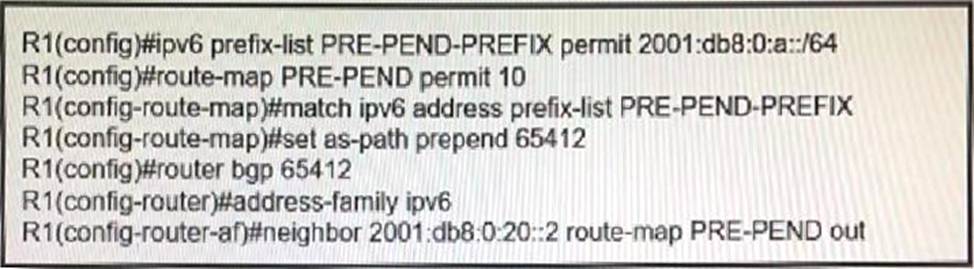
R1 has a route map configured, which results in a loss of partial IPv6 prefixes for the BGP neighbor, resulting in service degradation.
How can the full service be restored?
- A . The neighbor requires a soft reconfiguration, and this will clear the policy without resetting the BGP TCP connection.
- B . The prefix lit requires all prefixes that R1 is advertising to be added to it, and this will allow additional prefixes to be advertised.
- C . The route map requires a deny 20 statement without set conditions, and this will allow additional prefixes to be advertised.
- D . The route map requires a permit 20 statement without set conditions, and this will allow additional prefixes to be advertised.
Refer to the exhibit.
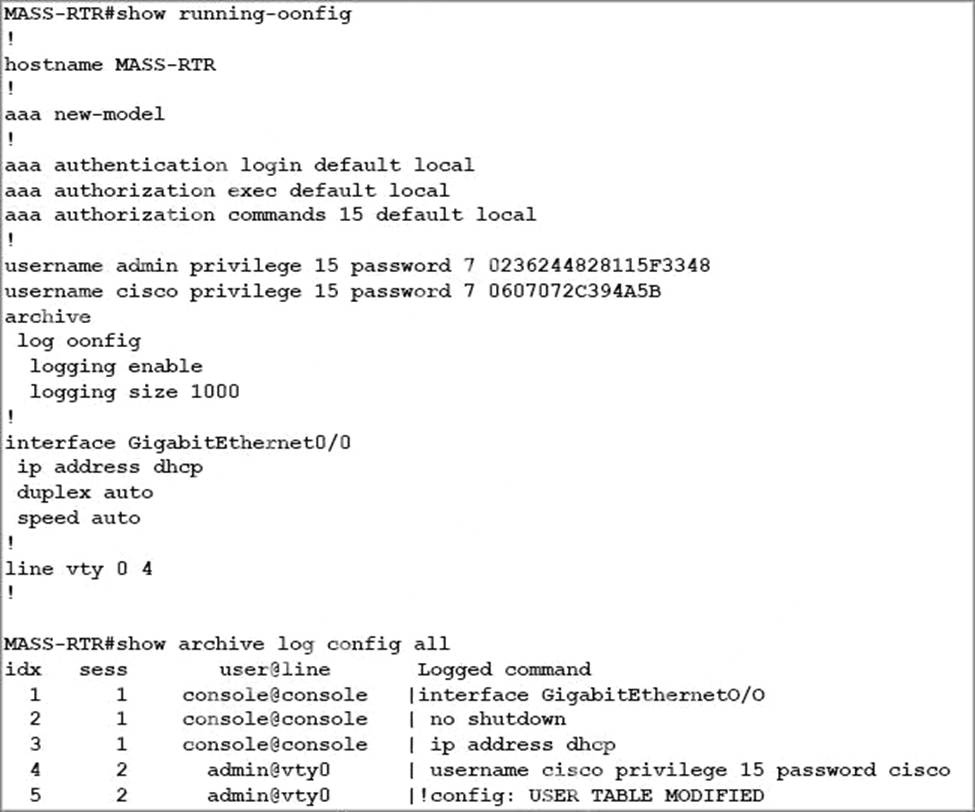
A client is concerned that passwords are visible when running this show archive log config all.
Which router configuration is needed to resolve this issue?
- A . MASS-RTR(config-archive-log-cfg)#password encryption aes
- B . MASS-RTR(config)#aaa authentication arap
- C . MASS-RTR(config)#service password-encryption
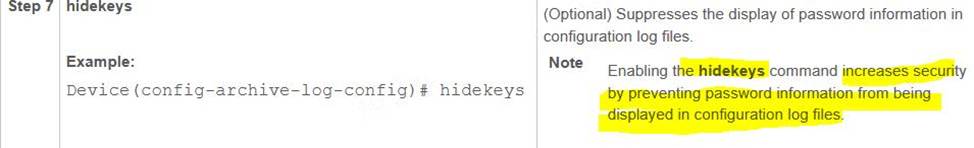
- D . MASS-RTR(config-archive-log-cfg)#hidekeys
D
Explanation:
How is the LDP router ID used in an MPLS network?
- A . The MPLS LOP router ID must match the IGP router ID.
- B . If not configured, the operational physical interface is chosen as the router ID oven d a loopback is configured.
- C . The loopback with the highest IP address is selected as the router ID
- D . The force keyword changes the router ID to the speeded address without causing any impact.
Refer to the exhibit.
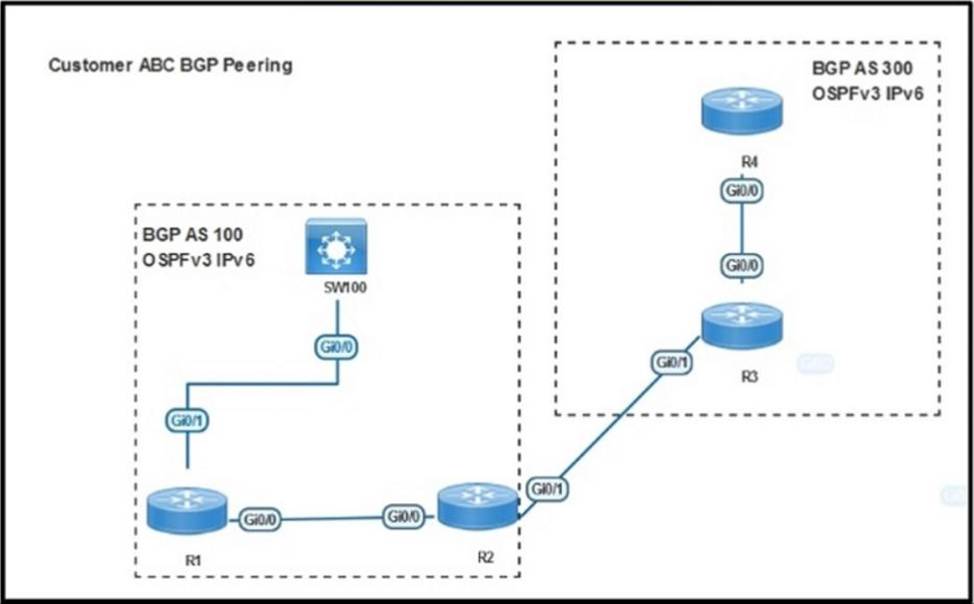
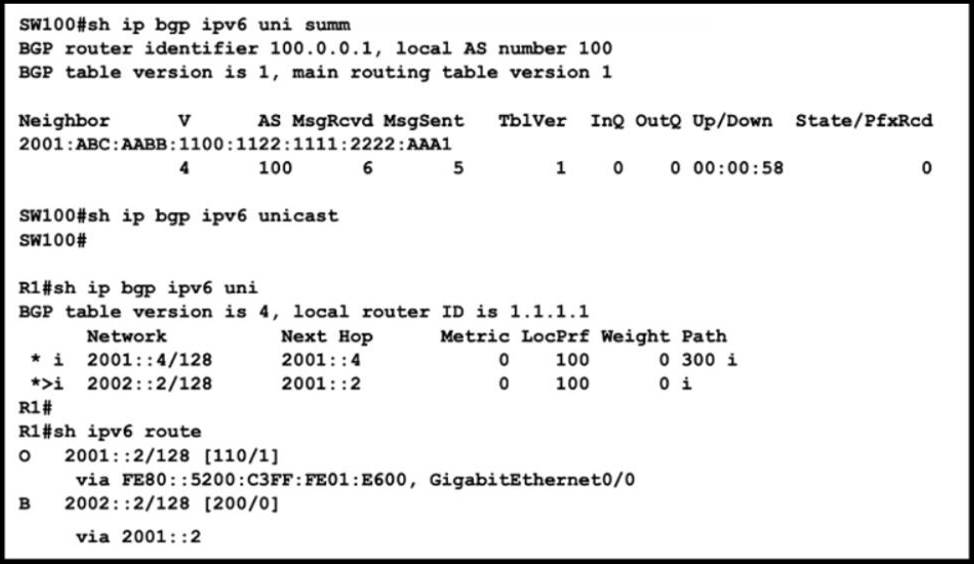
SW100 cannot receive routes from R1.
Which configuration resolves the issue?
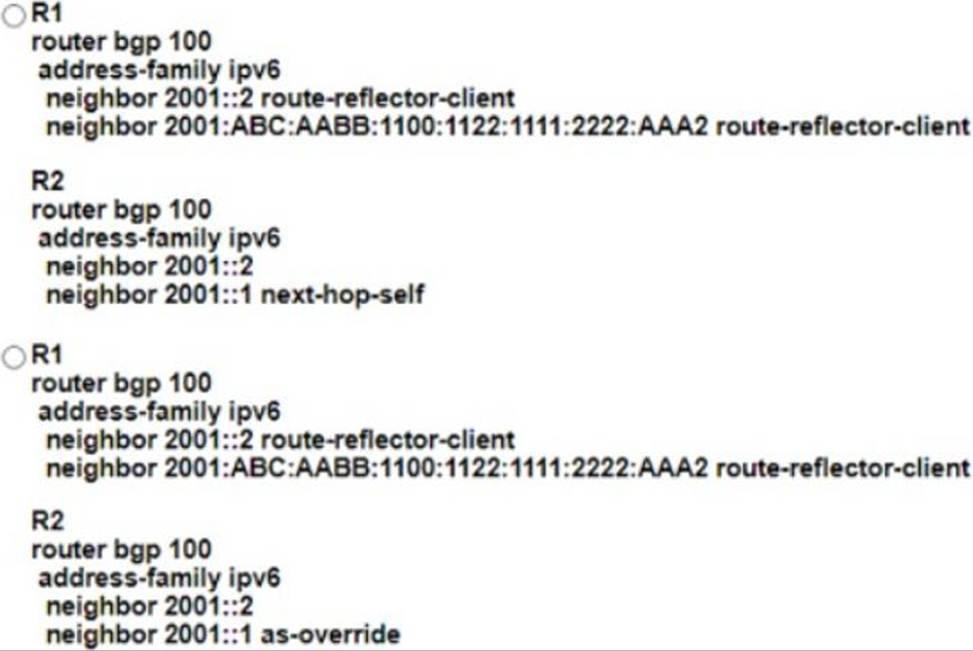
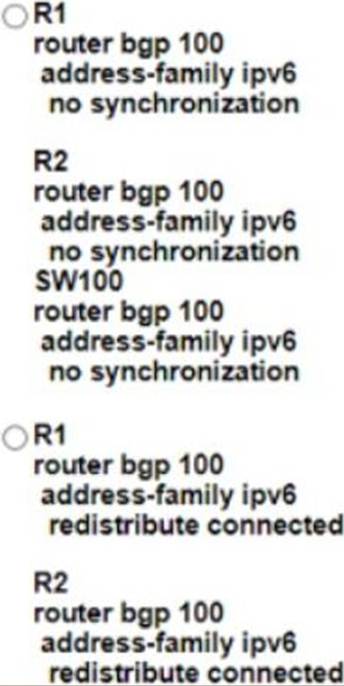
- A . Option A
- B . Option B
- C . Option C
- D . Option C
Refer to the exhibit.
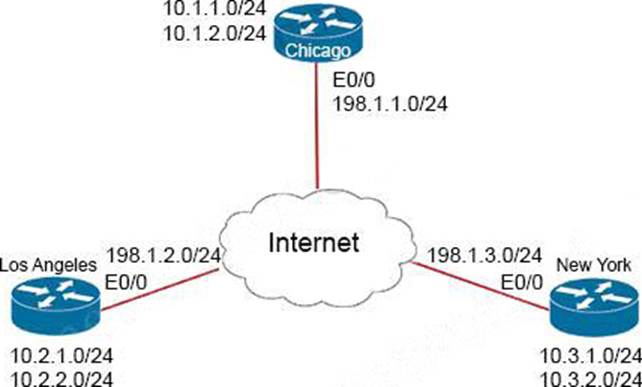
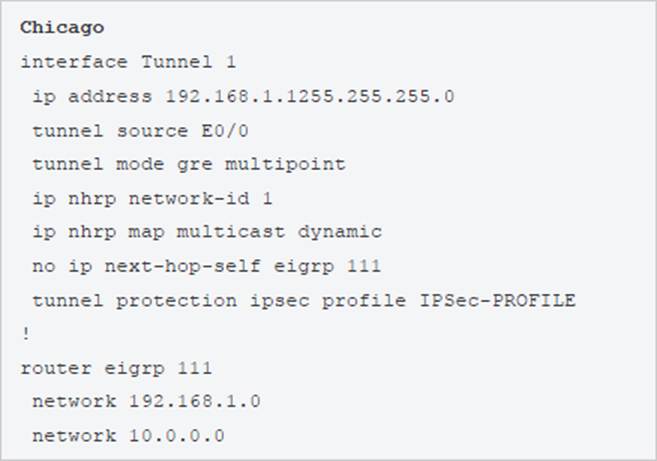
The Los Angeles and New York routers are receiving routes from Chicago but not from each other.
Which configuration fixes the issue?
- A . Interface Tunnel1no ip split-horizon eigrp 111
- B . Interface Tunnel1Ip next-hop-self elgrp 111
- C . Interface Tunnel1tunnel mode Ipsec Ipv4
- D . Interface Tunnel1tunnel protection ipsec profile IPSec-PROFILE
A
Explanation:
In this topology, Chicago router (Hub) will receive advertisements from Los Angeles (Spoke1) router on its tunnel interface. The problem here is that it also has a connection with New York (Spoke2) on that same tunnel interface. If we don’t disable EIGRP split-horizon, then the Hub will not relay routes from Spoke1 to Spoke2 and the other way around. That is because it received those routes on interface Tunnel1 and therefore it cannot advertise back out that same interface (splithorizon rule). Therefore we must disable split-horizon on the Hub router to make sure the Spokes know about each other.
Refer to the exhibit.
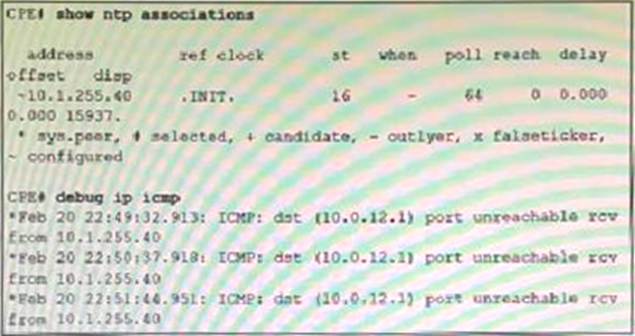
An administrator is troubleshooting a time synchronization problem for the router time to another Cisco IOS XE-based device that has recently undergone hardening.
Which action resolves the issue?
- A . Allow NTP in the ingress ACL on 10.1.225.40 by permitting UDP destined to port 123.
- B . Ensure that he CPE router has a valid route to 10.1.255. 40 for NTP and rectify if not reachable.
- C . NTP service is disabled and must be enabled on 10.1.225.40.
- D . Allow NTP in the ingress ACL on 10.1.255.40 by permitting TCP destined to port 123.