
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Refer to the exhibit.
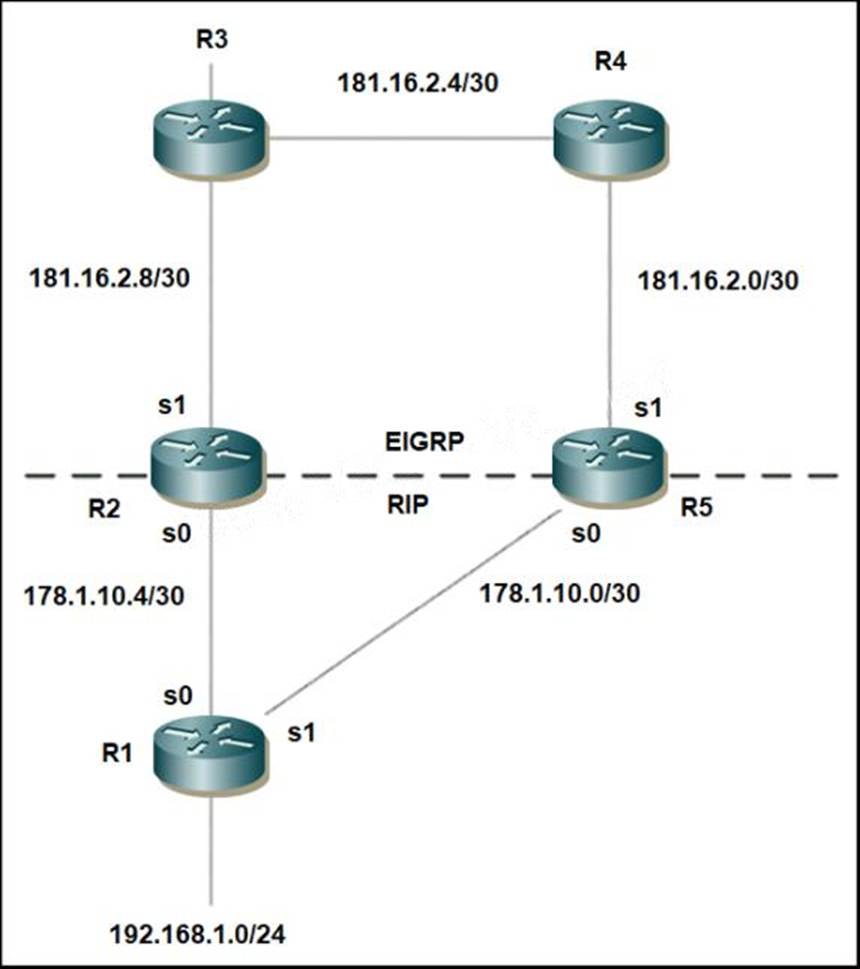
Mutual redistribution is enabled between RIP and EIGRP on R2 and R5.
Which configuration resolves the routing loop for the 192.168.1.0/24 network?
- A . R2:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s1
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any
R5:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s0
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any - B . R2:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s0
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any
R5:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s0
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any - C . R2:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s0
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any
R5:
router eigrp 10
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s1
!
router rip
network 178.1.0.0
redistribute eigrp 10 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any - D . R2:
router eigrp 7
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s1
!
router rip
network 178.1.0.0
redistribute eigrp 7 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any
R5:
router eigrp 7
network 181.16.0.0
redistribute rip metric 1 1 1 1 1
distribute-list 1 in s1
!
router rip
network 178.1.0.0
redistribute eigrp 7 metric 2
!
access-list 1 deny 192.168.1.0
access-list 1 permit any
D
Explanation:
https://www.cisco.com/c/en/us/support/docs/ip/enhanced-interior-gateway-routing-protocol-eigrp/8606-redist.html
The network administrator configured R1 to authenticate Telnet connections based on Cisco ISE using TACACS+. ISE has been configured with an IP address of 192.168.1.5 and with a network device pointing toward R1(192.168.1.1) with a shared secret password of Cisco123.
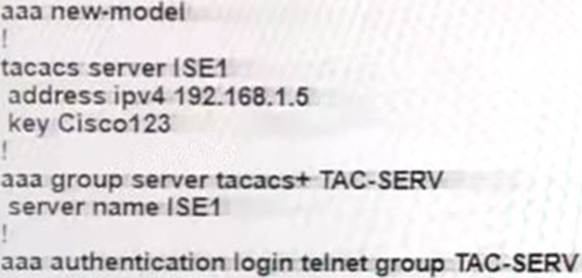
The administrator cannot authenticate to R1 based on ISE.
Which configuration fixes the issue?
- A . ip tacacs-server host 192.168.1.5 key Cisco123
- B . line vty 0 4login authentication TAC-SERV
- C . line vty 0 4login authentication telnet
- D . tacacs-server host 192.168.1.5 key Cisco123
C
Explanation:
The last command “aaa authentication login telnet group TAC-SERV” created the method list name telnet so we need to assign it to line vty.
Reference: https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/200208-Configure-ISE-2-0-IOS-TACACS-Authentic.html
An engineer failed to run diagnostic commands on devices using Cisco DNA Center.
Which action in Cisco DNA Center resolves the issue?
- A . Enable Command Runner
- B . Enable APIs
- C . Enable CDP
- D . Enable Secure Shell
Refer to the exhibit.
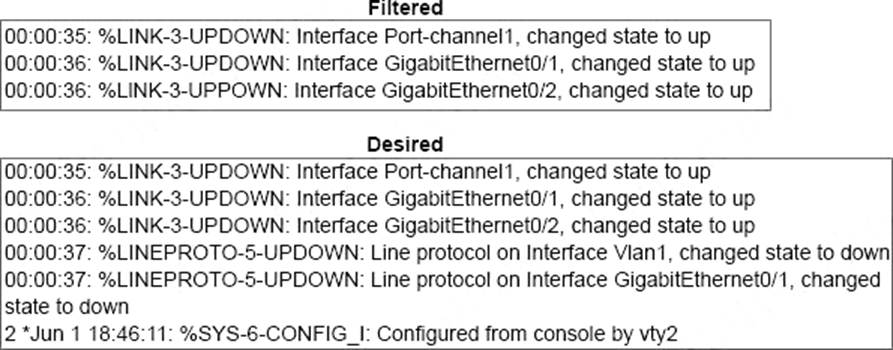
Refer to the exhibits. An engineer filtered messages based on severity to minimize log messages. After applying the filter, the engineer noticed that it filtered required messages as well.
Which action must the engineer take to resolve the issue?
- A . Configure syslog level 2.
- B . Configure syslog level 3.
- C . Configure syslog level 4.
- D . Configure syslog level 5.
In which two ways does the IPv6 First-Hop Security Binding Table operate? (Choose two.)
- A . by IPv6 routing protocols to securely build neighborships without the need of authentication
- B . by the recovery mechanism to recover the binding table in the event of a device reboot
- C . by IPv6 HSRP to make sure neighbors are authenticated before being used as gateways
- D . by various IPv6 guard features to validate the data link layer address
- E . by storing hashed keys for IPsec tunnels for the built-in IPsec features
B,D
Explanation:
Overview of the IPv6 First-Hop Security Binding Table
A database table of IPv6 neighbors connected to the device is created from information sources such as NDP snooping. This database, or binding table, is used by variousIPv6 guard features to validate the link-layer address (LLA), the IPv4 or IPv6 address, and the prefix binding of the neighbors to prevent spoofing and redirect attacks.
IPv6 First-Hop Security Binding Table Recovery Mechanism The IPv6 first-hop security binding table recovery mechanism enables the binding table to recover in the event of a device reboot.
Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/15-s/ip6-fhs-bind-table.html
Refer to the exhibit.
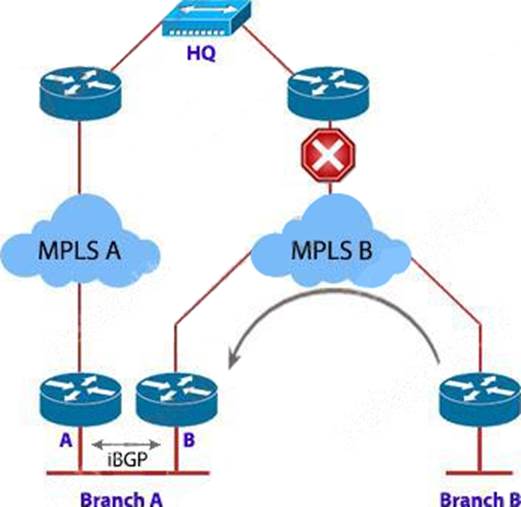
Troubleshoot and ensure that branch B only ever uses the MPLS B network to reach HQ.
Which action achieves this requirement?
- A . Introduce an AS path filter on branch A routers so that only local prefixes are advertised into BGP
- B . increase the local preference for all HQ prefixes received at branch B from the MPLS B network to
be higher than the local preferences used on the MPLS A network - C . Introduce AS path prepending on the branch A MPLS B network connection so that any HQ advertisements from branch A toward the MPLS B network are prepended three times
- D . Modify the weight of all HQ prefixes received at branch B from the MPLS B network to be higher than the weights used on the MPLS A network
A
Explanation:
If we modify the weight, increase local preference or use AS path prepending then we can only make MPLS B prefer over MPLS
Which IP precedence value does BFD use to prioritize traffic within an infrastructure device?
- A . 4
- B . 5
- C . 6
- D . 7
Refer to the exhibit.
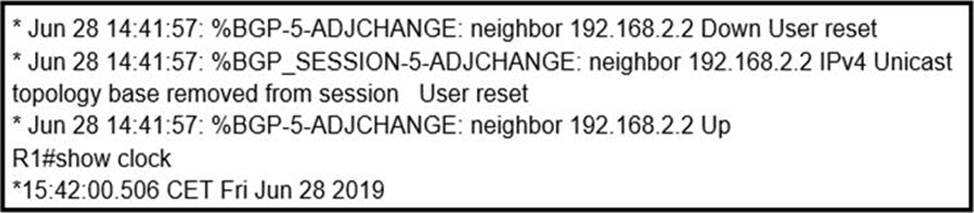
An engineer is troubleshooting BGP on a device but discovers that the clock on the device does not correspond to the time stamp of the log entries.
Which action ensures consistency between the two times?
- A . Configure the service timestamps log uptime command in global configuration mode.
- B . Configure the logging clock synchronize command in global configuration mode.
- C . Configure the service timestamps log datetime localtime command in global configuration mode.
- D . Make sure that the clock on the device is synchronized with an NTP server.
C
Explanation:
https://www.cisco.com/c/en/us/td/docs/routers/xr12000/software/xr12k_r3-
9/system_management/command/reference/yr39xr12k_chapter4.html#wp1784026936
By default, syslog and debug messages are stamped by UTC, regardless of the time zone that device
configured. You should append localtime key word to "service timestamp {log | debug} datetime msec" global command to change that behavior.
https://community.cisco.com/t5/networking-documents/router-log-timestamp-entries-are-different-from-the-system-clock/ta-p/3132258
https://www.cisco.com/E-
Learning/bulk/public/tac/cim/cib/using_cisco_ios_software/cmdrefs/service_timestamps.htm
Refer to the exhibit.
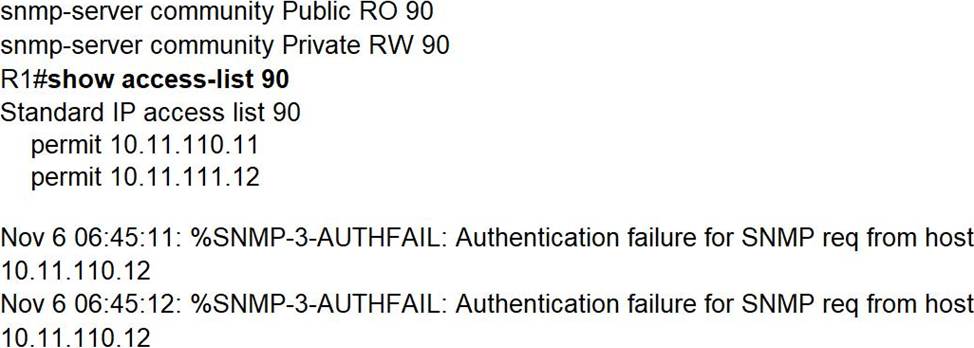
A network administrator notices these console messages from host 10.11.110.12 originating from interface E1/0. The administrator considers this an unauthorized attempt to access SNMP on R1.
Which action prevents the attempts to reach R1 E1/0?
- A . Configure IOS control plane protection using ACL 90 on interface E1/0
- B . Configure IOS management plane protection using ACL 90 on interface E1/0
- C . Create an inbound ACL on interface E1/0 to deny SNMP from host 10.11.110.12
- D . Add a permit statement including the host 10.11.110.12 into ACL 90
Refer to the exhibit.
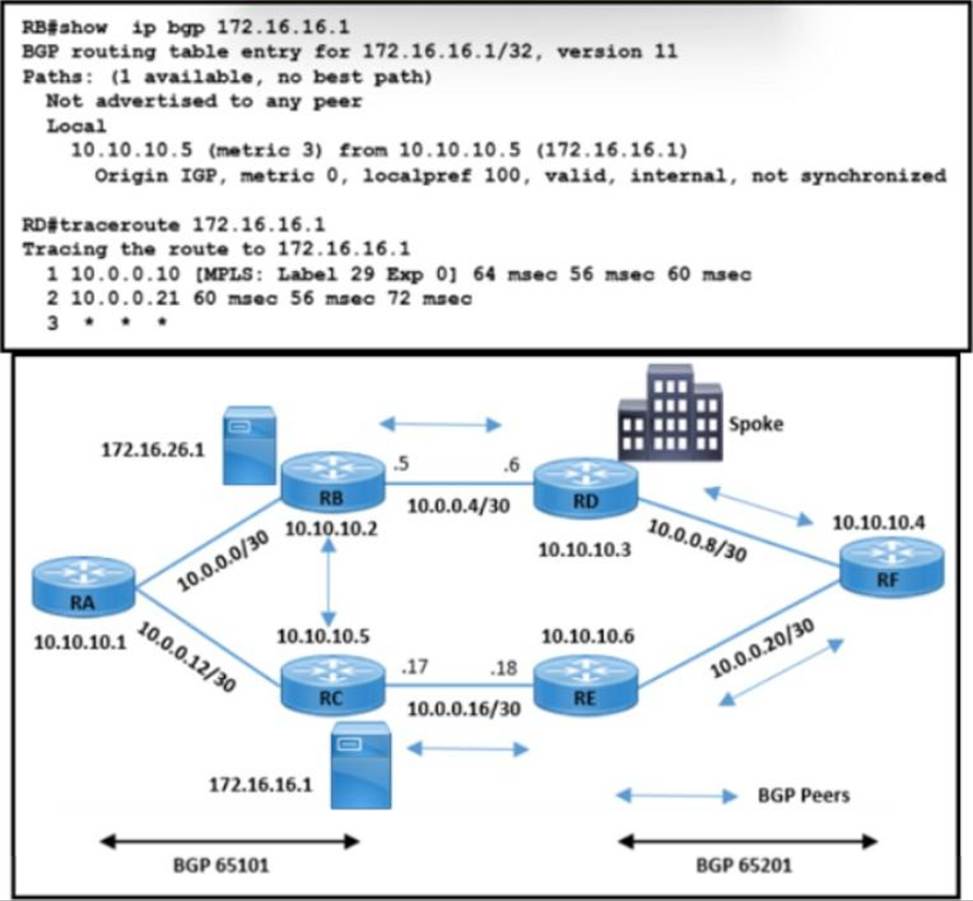
A customer reported an issue with a fiber link failure between RC and RE Users connected through the spoke location face disconnection and packet drops with the primary email server (172.16.16.1) but have no issues with the backup email server (172.16.26.1). All the router loopback IPs are advertised through the OSPF protocol.
Which configuration resolves the issue?
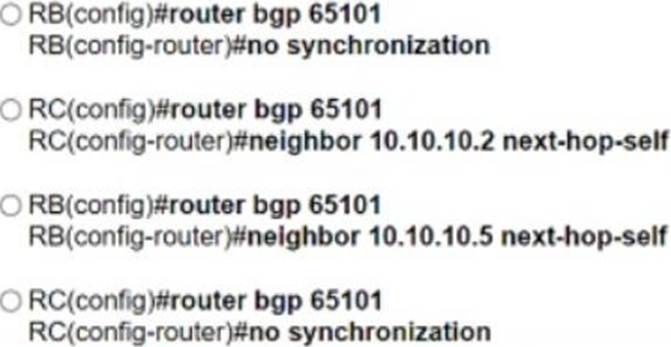
- A . Option A
- B . Option B
- C . Option C
- D . Option D