
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Refer to the exhibit.
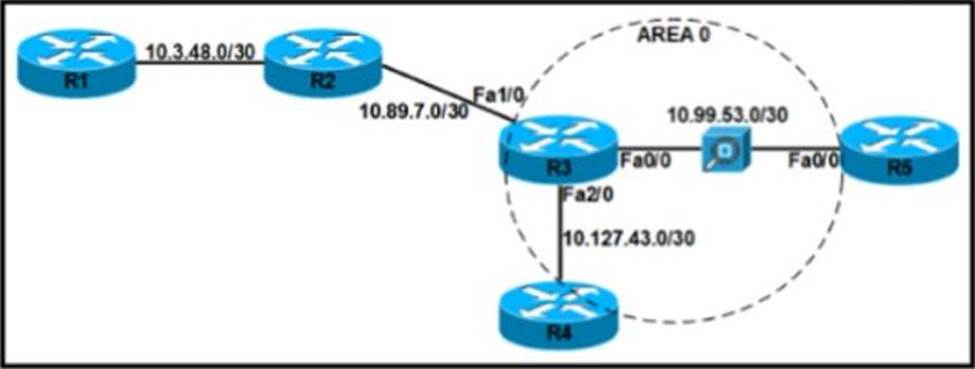
The security department recently installed a monitoring device between routers R3 and R5, which a loss of network connectivity for users connected to R5. Troubleshooting revealed that the monitoring device cannot forward multicast packets. The team already updated R5 with the correct configuration.
Which configuration must be implemented on R3 to resolve the problem by ensuring R3 as the DR for the R3-R5 segment?
- A . interface fastethernet0/0
ip address 10.99.53.1 255.255.255.252
ip access-group 122 in
ip ospf network non-broadcast
ip ospf priority 0
!
router ospf 10
router-id 10.10.3.255
neighbor 10.99.53.2
!
access-list 122 permit 89 host 10.99.53.2 host 10.99.53.1
access-list 122 deny 89 any any
access-list 122 permit tcp any any
access-list 122 permit udp any any
access-list 122 permit icmp any any - B . interface fastethernet0/0
ip address 10.99.53.1 255.255.255.252
ip access-group 122 in
ip ospf network non-broadcast
ip ospf priority 0
!
router ospf 10
router-id 10.10.3.255
network 10.99.53.0 0.0.0.3 area 0
neighbor 10.99.53.2
!
access-list 122 permit 89 host 10.99.53.2 host 10.99.53.1
access-list 122 deny 89 any any
access-list 122 permit tcp any any
access-list 122 permit udp any any
access-list 122 permit icmp any any - C . interface fastethernet0/0
ip address 10.99.53.1 255.255.255.252
ip access-group 122 in
ip ospf network non-broadcast
ip ospf priority 100
!
router ospf 10
router-id 10.10.3.255
network 10.99.53.0 0.0.0.3 area 0
neighbor 10.99.53.2
access-list 122 permit 89 host 10.99.53.2 host 10.99.53.1
access-list 122 deny 89 any any
access-list 122 permit tcp any any
access-list 122 permit udp any any
access-list 122 permit icmp any any - D . interface fastethernet0/0
ip address 10.99.53.1 255.255.255.252
ip access-group 122 in
ip ospf network point-to-point
ip ospf priority 100
!
router ospf 10
router-id 10.10.3.255
network 10.99.53.0 0.0.0.3 area 0
neighbor 10.99.53.2
!
access-list 122 permit 89 host 10.99.53.2 host 10.99.53.1
access-list 122 deny 89 any any
access-list 122 permit tcp any any
access-list 122 permit udp any any
access-list 122 permit icmp any any
Refer to the exhibit.
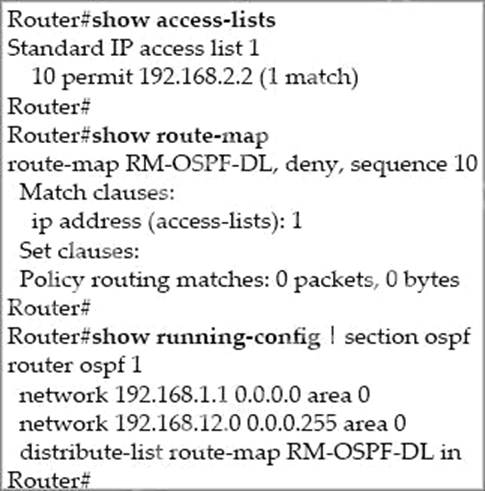
Which two actions should be taken to access the server? (Choose two.)
- A . Modify the access list to add a second line of permit ip any
- B . Modify the access list to deny the route to 192.168.2.2.
- C . Modify distribute list seq 10 to permit the route to 192.168.2.2.
- D . Add a sequence 20 in the route map to permit access list 1.
- E . Add a floating static route to reach to 192.168.2.2 with administrative distance higher than OSPF
Refer to the exhibit.
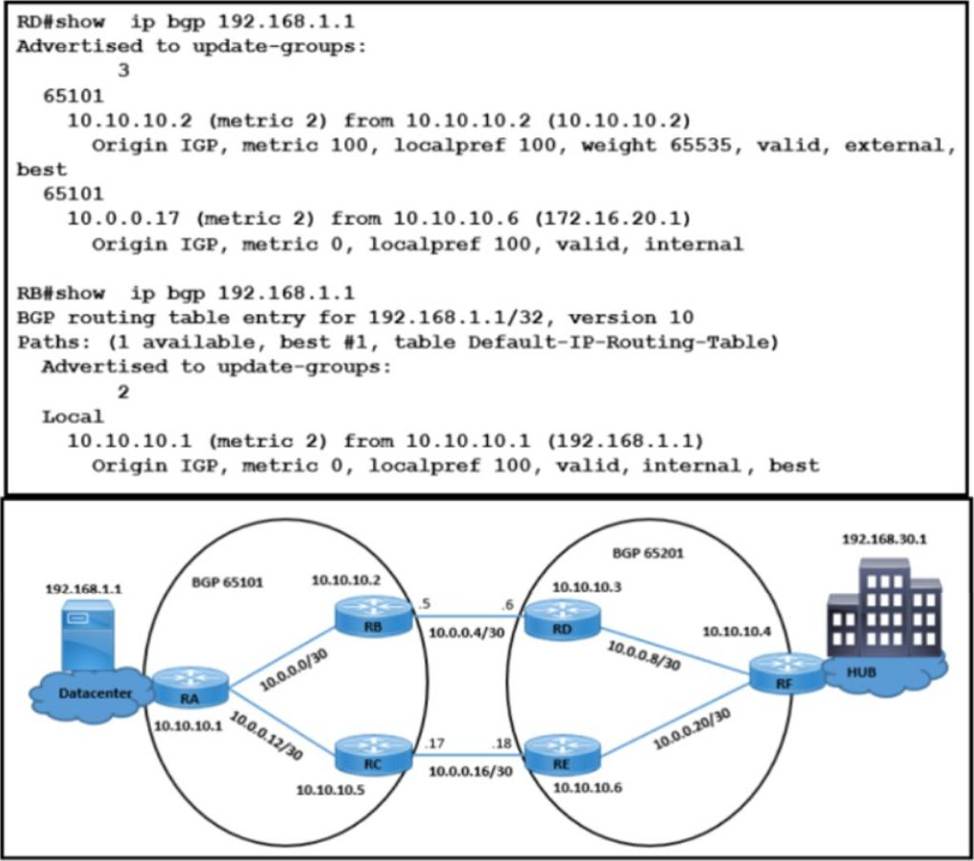
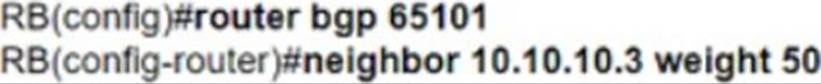
A customer finds that traffic from the application server (192.168.1.1) to the HUB site passes through a congested path that causes random packet drops. The NOC team influences the BGP path with MED on RB. but RD still sees that traffic coming from RA is not taking an alternate route.
Which configuration resolves the issue?
A customer finds that traffic from the application server (192.168.1.1) to the HUB site passes through a congested path that causes random packet drops. The NOC team influences the BGP path with MED on RB. but RD still sees that traffic coming from RA is not taking an alternate route.
Which configuration resolves the issue?
A)

B)

C)
D)

- A . Option A
- B . Option B
- C . Option C
- D . Option D
What is a role of route distinguishers in an MPLS network?
- A . Route distinguishers define which prefixes are imported and exported on the edge router
- B . Route distinguishers allow multiple instances of a routing table to coexist within the edge router.
- C . Route distinguishers are used for label bindings.
- D . Route distinguishers make a unique VPNv4 address across the MPLS network
Refer to the exhibit.
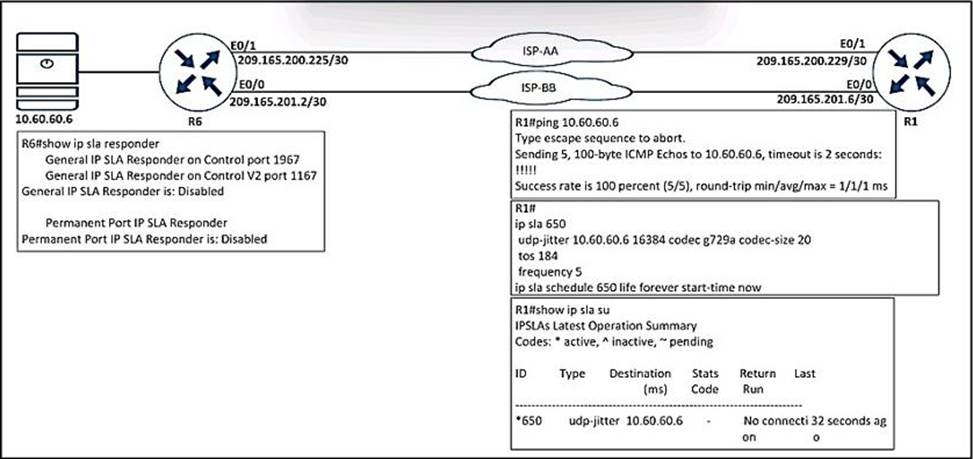
Which configuration resolves the IP SLA issue from R1 to the server?
- A . R6(config)#ip sla responder
- B . R6(config)#ip sla responder udp-echo ipaddress 10.60.60.6 po 5000
- C . R6(config)#ip sla 650
R6(config-ip-sla)ff udp-jitter 10.60.60.6 - D . R6(config)#ip sla schedule 10 life forever start-time now
Which two methods use IPsec to provide secure connectivity from the branch office to the headquarters office? (Choose two.)
- A . DMVPN
- B . MPLS VPN
- C . Virtual Tunnel Interface (VTI)
- D . SSL VPN
- E . PPPoE
Refer to the exhibit.
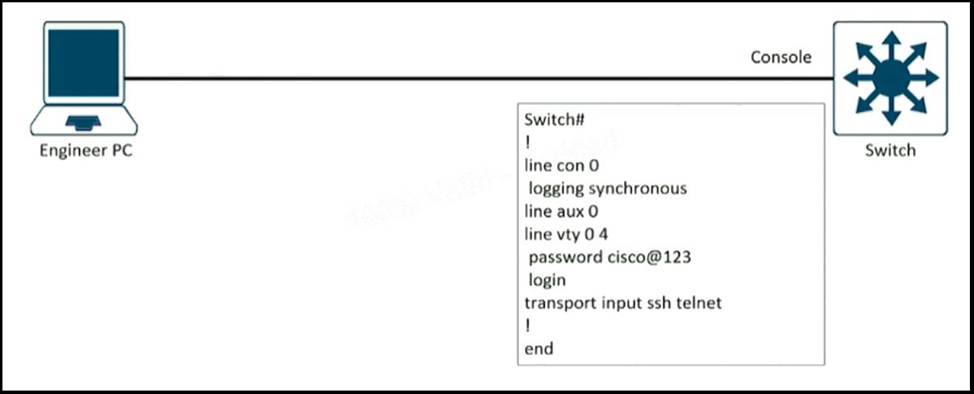
An engineer must block access to the console ports for all corporate remote Cisco devices based on the recent corporate security policy but the security team stilt can connect through the console port.
Which configuration on the console port resolves the issue?
- A . transport input telnet
- B . login and password
- C . no exec
- D . exec 0.0
C
Explanation:
“no exec” will disable access to a line. It is used if we want to allow only outgoing session (and disable incoming session) so this command will block all console port access.
There is no “exec 0 0” command. We can only find the “exec prompt” command in IOS Version 15.4(2)T4.
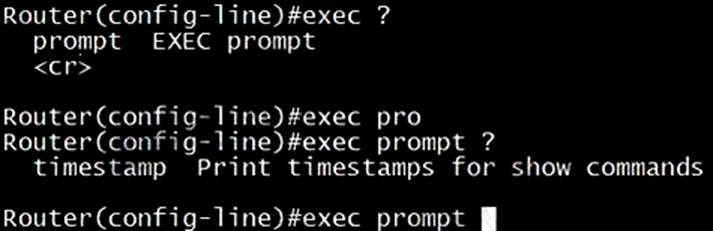
The most similar command is “exec-timeout 0 0” command, which is used to prevent Telnet/SSH sessions from timing out.
Refer to the exhibit.
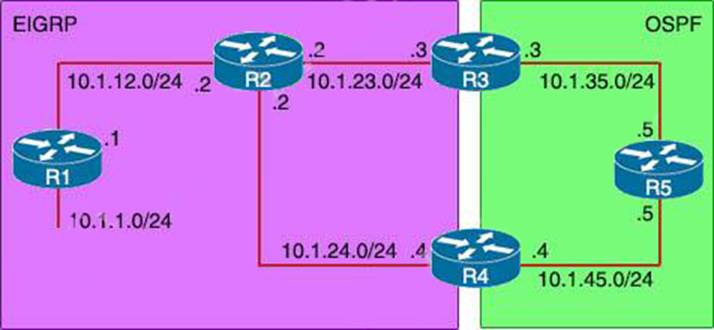
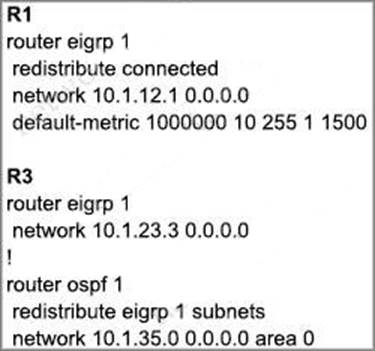
To provide reachability to network 10.1.1.0 /24 from R5, the network administrator redistributes EIGRP into OSPF on R3 but notices that R4 is now taking a ……….. path through R5 to reach 10.1.1.0/24 network.
Which action fixes the issue while keeping the reachability from R5 to 10.1.1.0/24 network?
- A . Change the administrative distance of the external EIGRP to 90.
- B . Apply the outbound distribution list on R5 toward R4 in OSPF.
- C . Change the administrative distance of OSPF to 200 on R5.
- D . Redistribute OSPF into EIGRP on R4
Refer to the exhibit.
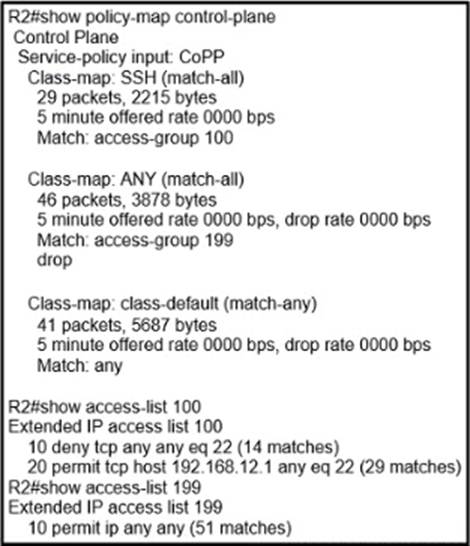
Which action limits the access to R2 from 192.168.12.1?
- A . Swap sequence 10 with sequence 20 in access-list 100.
- B . Modify sequence 20 to permit tcp host 192.168.12.1 eq 22 any to access-list 100
- C . Swap sequence 20 with sequence 10 in access-list 100
- D . Modify sequence 10 to deny tcp any eq 22 any to access-list 100.
Refer to the exhibit.
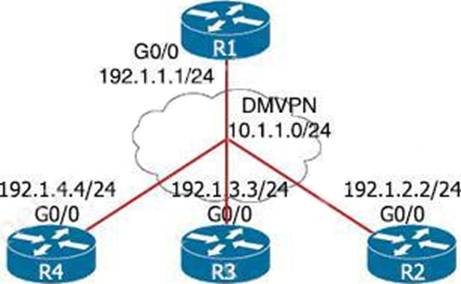
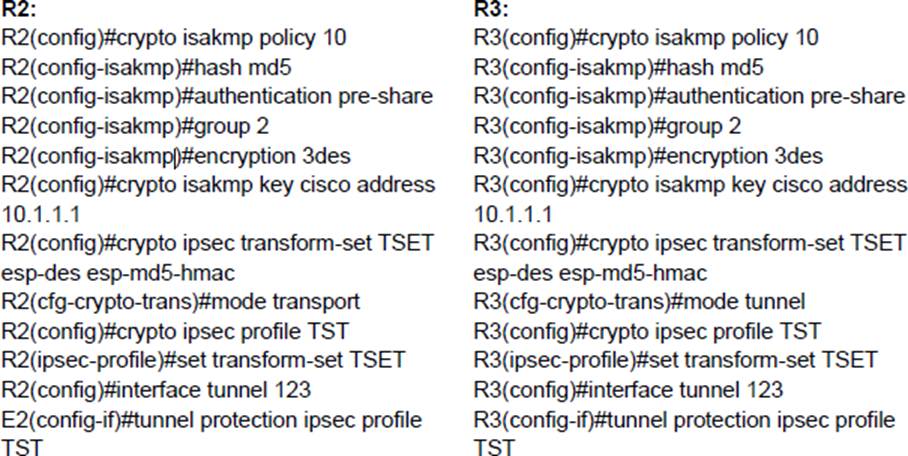
After applying IPsec, the engineer observed that the DMVPN tunnel went down, and both spoke-to-spoke and hub were not establishing.
Which two actions resolve the issue? (Choose two.)
- A . Configure the crypto isakmp key cisco address 192.1.1.1 on R2 and R3
- B . Configure the crypto isakmp key cisco address 0.0.0.0 on R2 and R3.
- C . Change the mode from mode tunnel to mode transport on R3
- D . Change the mode from mode transport to mode tunnel on R2.
- E . Remove the crypto isakmp key cisco address 10.1.1.1 on R2 and R3
A, D
Explanation:
*When using DMVPN with IPSec, it is unnecessary to use tunnel mode. Because DMVPN uses GRE which means that a new IP header is already added by GRE. The GRE encapsulation happens on the tunnel interface before the encryption process takes place.