
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
DRAG DROP
Drag and drop the IPv6 first hop security device roles from the left onto the corresponding descriptions on the right.
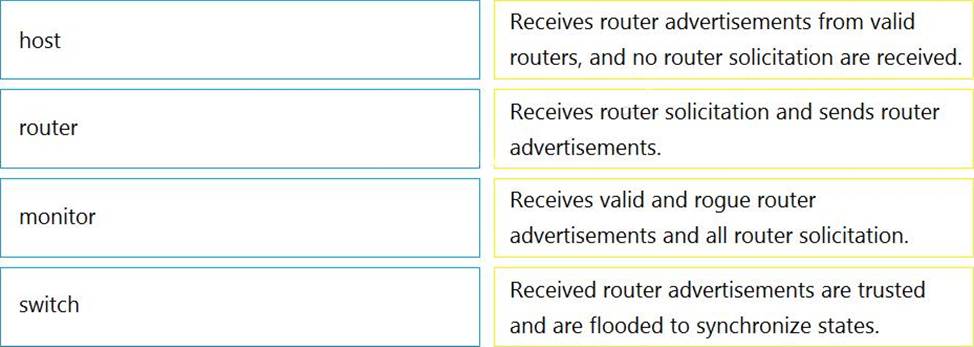
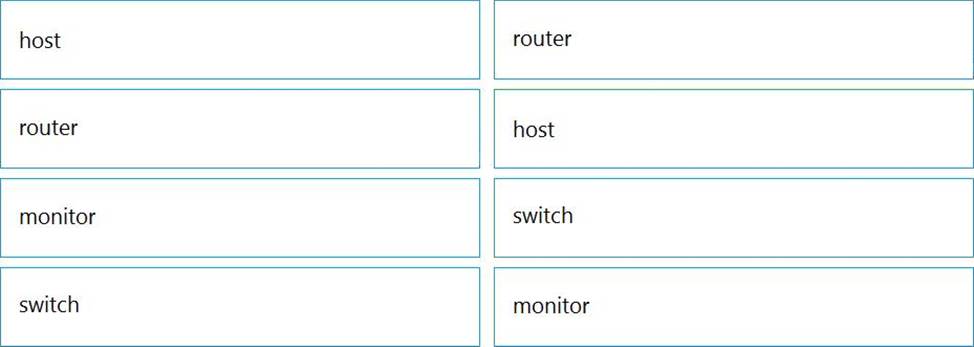
Explanation:
Graphical user interface, text, application, email Description automatically generated
Reference: https://www.cisco.com/c/en/us/td/docs/switches/datacenter/nexus9000/sw/7-x/security/configuration/guide/b_Cisco_Nexus_9000_Series_NX-OS_Security_Configuration_Guide_7x/b_Cisco_Nexus_9000_Series_NX-OS_Security_Configuration_Guide_7x_chapter_011011.pdf
Refer to the exhibit.
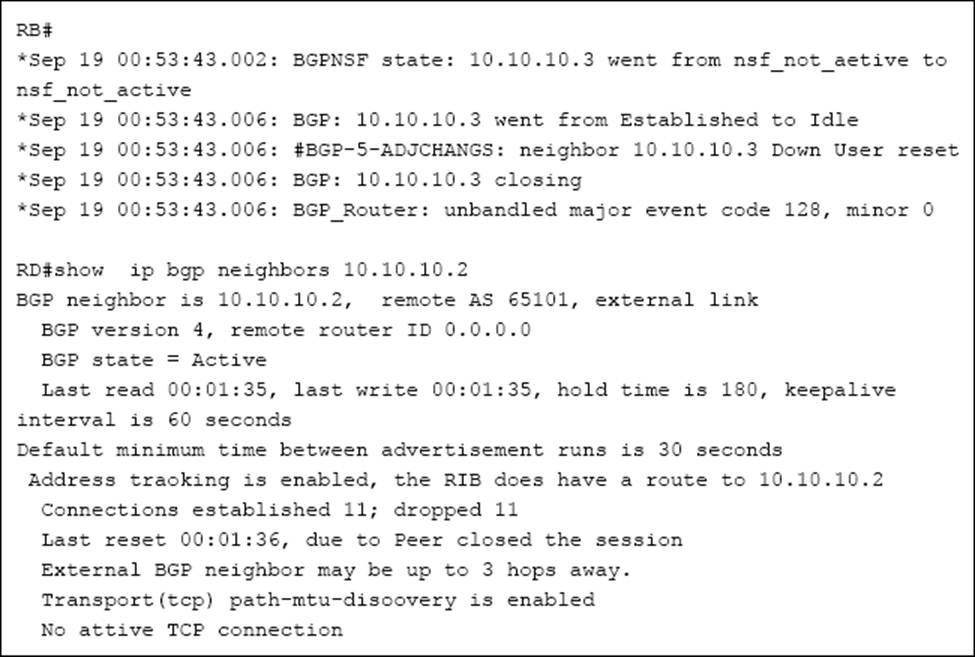
A NOC team receives a ticket that data traffic from RA to RF is not forwarded when the link between the RC-RE path goes down. All routers learn loopback IP through the IGP protocol.
Which configuration resolves?
- A . RD(config)#router bgp B5201
RD(config-router)# neighbor 10.10.10.2 update-source loopback 0 - B . RD(config-router)# neighbor bgp 65101
RB(config-router)# neighbor 10.10.10.3 ebgp-multihop 3 - C . RB(config)# router bgp 65101
RB(config)#neighbor 10.10.10.3 update-source loopback 0 - D . RD(config)# router bgp 65201
RDI(config-router)# neighbor 10.10.10.2 ebgp-multihop 3
Which command is used to check IP SLA when an interface is suspected to receive lots of traffic with options?
- A . show track
- B . show threshold
- C . show timer
- D . show delay
Refer to the exhibit.
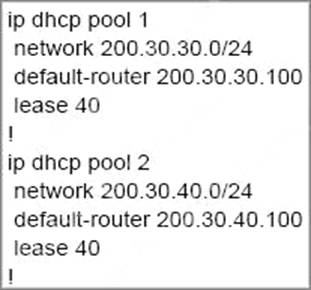
The server for the finance department is not reachable consistently on the 200.30.40.0/24 network and after every second month it gets a new IP address.
Which two actions must be taken to resolve this Issue? (Choose two.)
- A . Configure the server to use DHCP on the network with default gateway 200 30.40.100.
- B . Configure the server with a static IP address and default gateway.
- C . Configure the router to exclude a server IP address.
- D . Configure the server to use DHCP on the network with default gateway 200 30.30.100.
- E . Configure the router to exclude a server IP address and default gateway.
Refer to the exhibit.
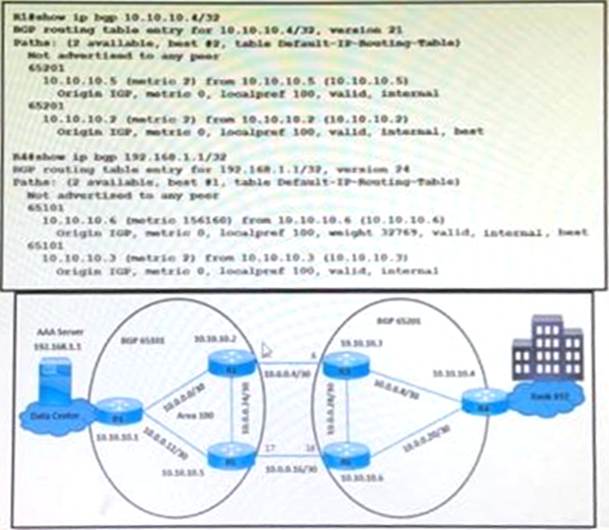
A customer reports that user traffic of bank XYZ to the AAA server is not using the primary path via the R3-R2 link.
The network team observes:
No fiber is cut on links R2 and R3.
As101 and AS 201 routers established BGP peering.
Which configuration resolves the issue?
A)
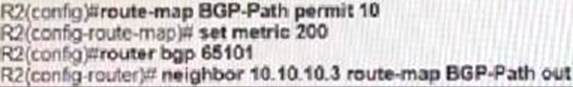
B)

C)

D)
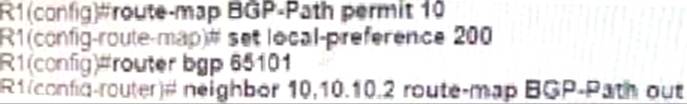
- A . Option A
- B . Option B
- C . Option C
- D . Option D
DRAG DROP
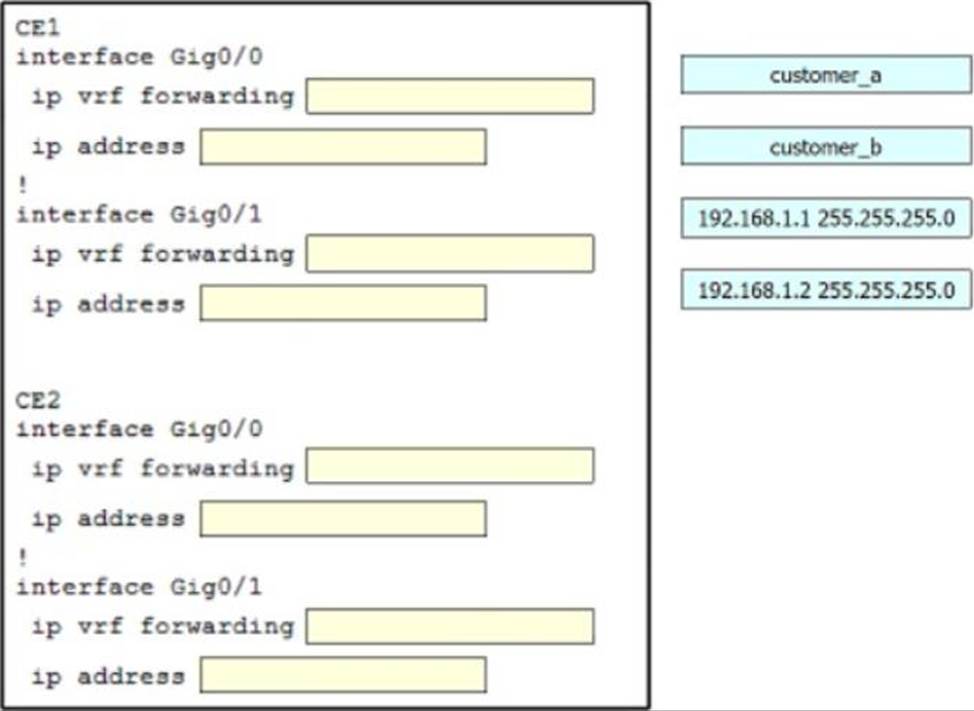
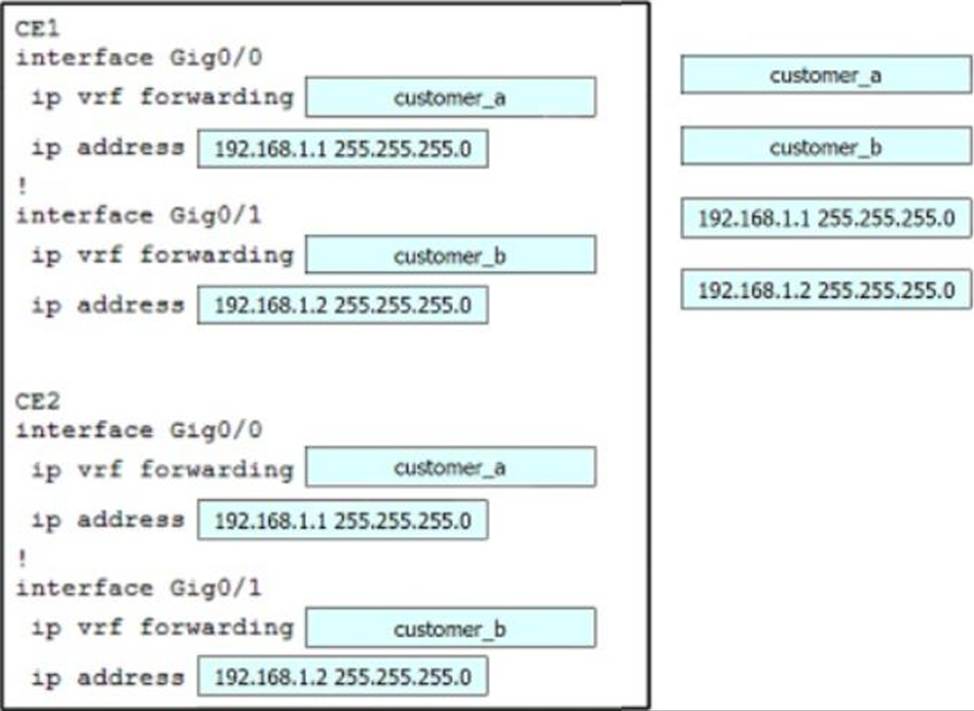
An engineer must establish a connection between two CE routers for two customers with overlapping IP addresses Customer_a is connected to interfaces Gig0/0, and Customer_b is connected to interfaces Gig0/1.
Routers CE1 and CE2 are configured as follows:
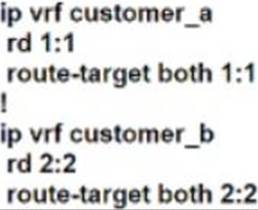
Drag and drop the code snippets from the right onto the boxes in the configuration to establish the needed connection. Snippets may be used more than once.
SIMULATION
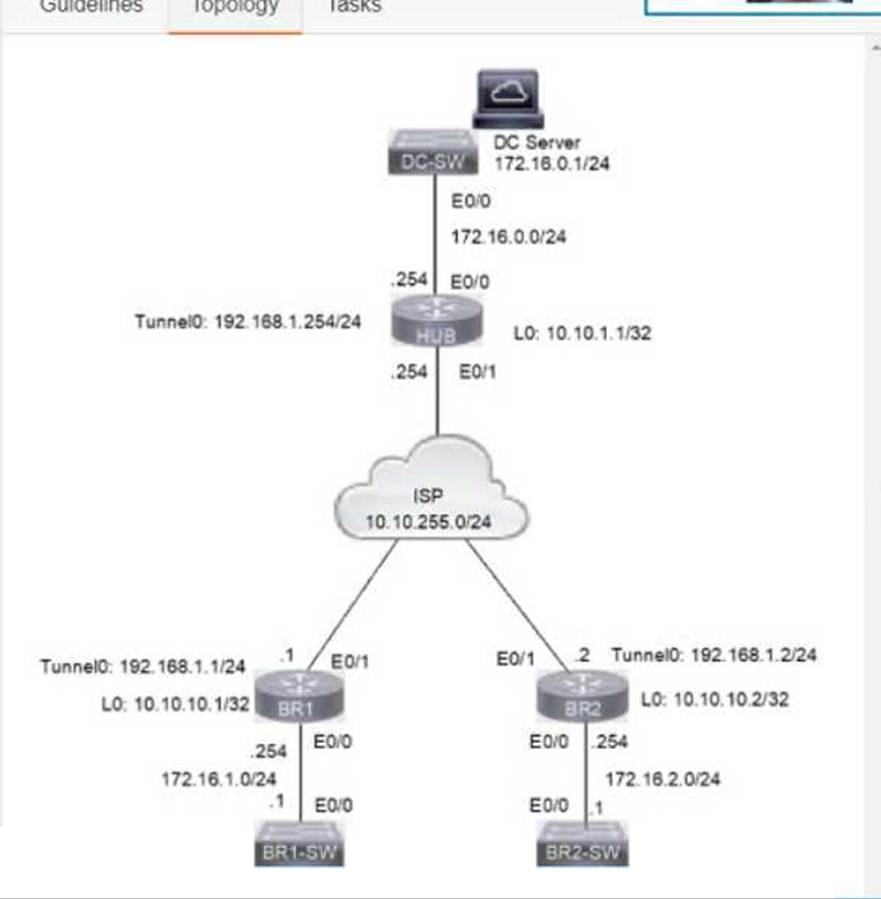
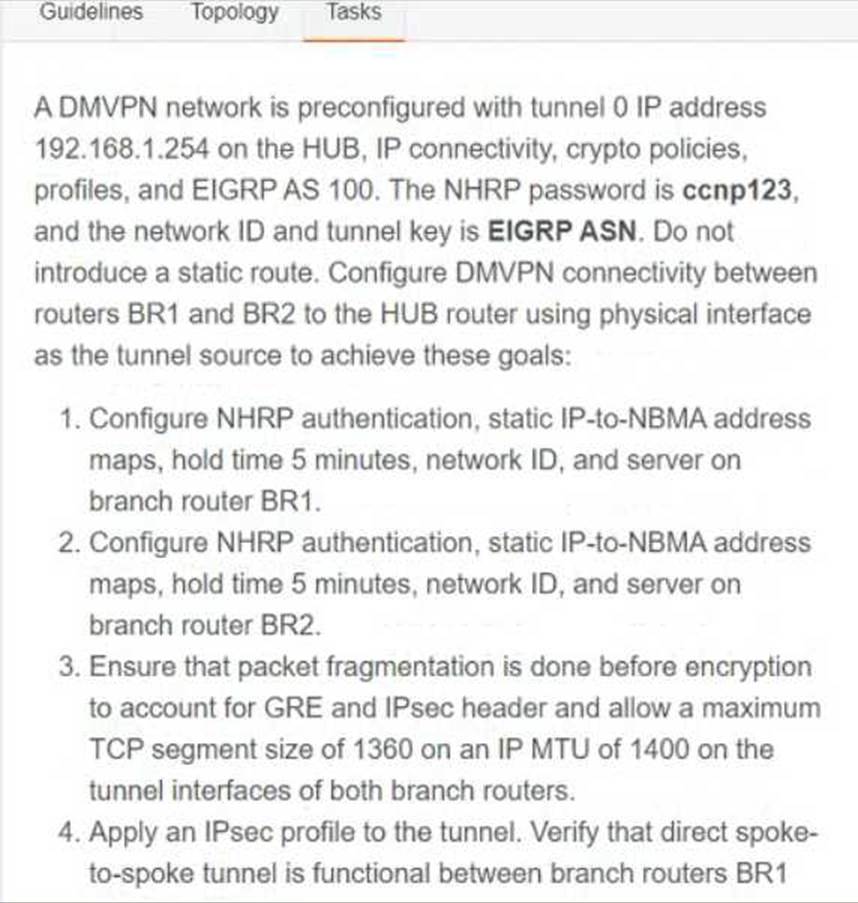
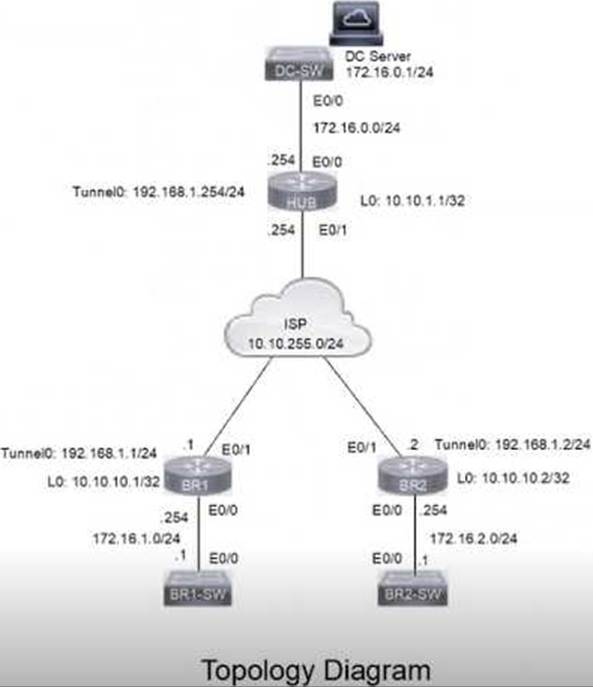
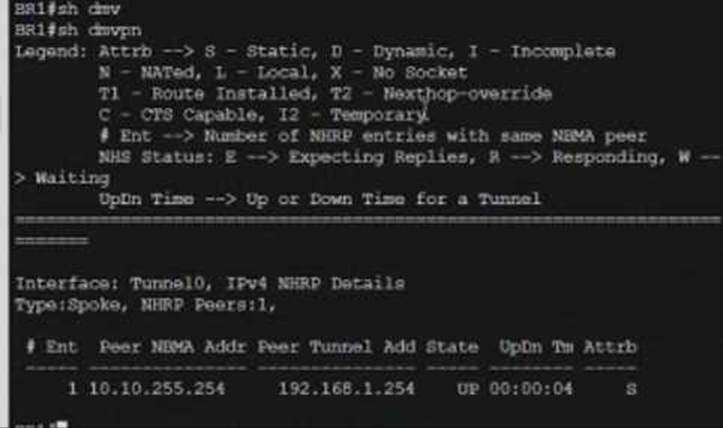
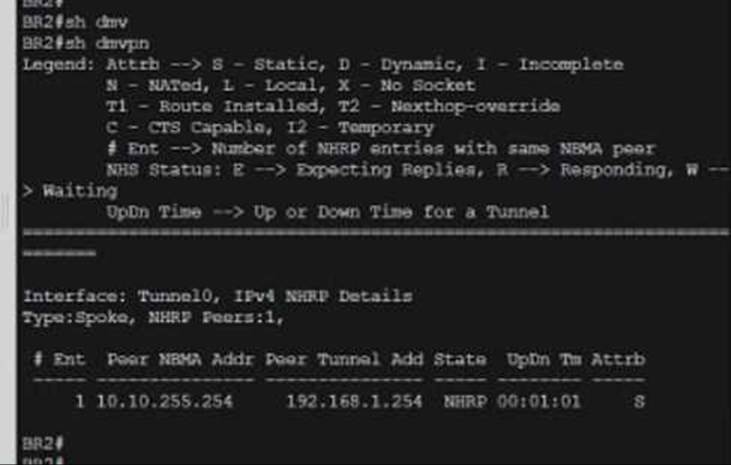
A DMVPN network is preconfigured with tunnel 0 IP address 192.168.1.254 on the HUB, IP connectivity, crypto policies, profiles, and EIGRP AS 100. The NHRP password is ccnp123, and the network ID and tunnel key is EIGRP ASN Do not introduce a static route.
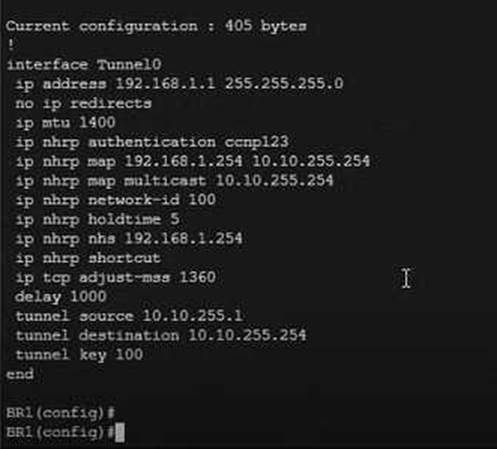
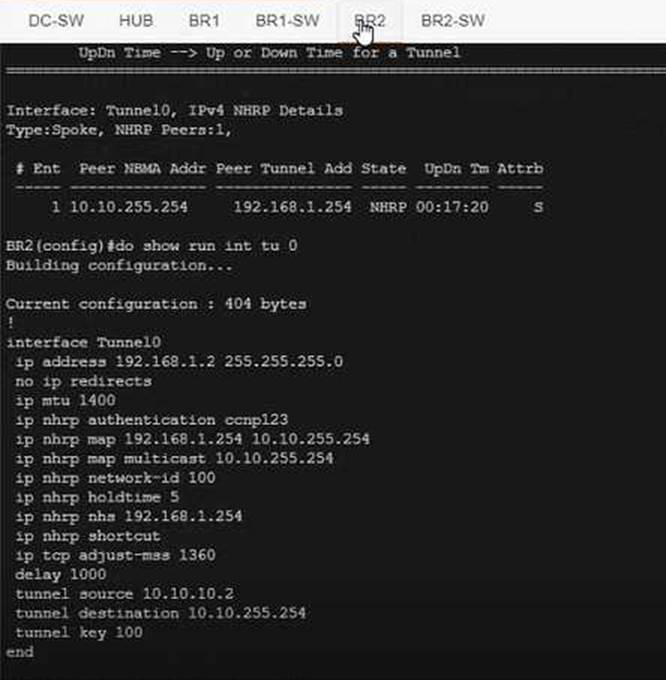
Configure DMVPN connectivity between routers BR1 and BR2 to the HUB router using physical interface as the tunnel source to achieve these goals:
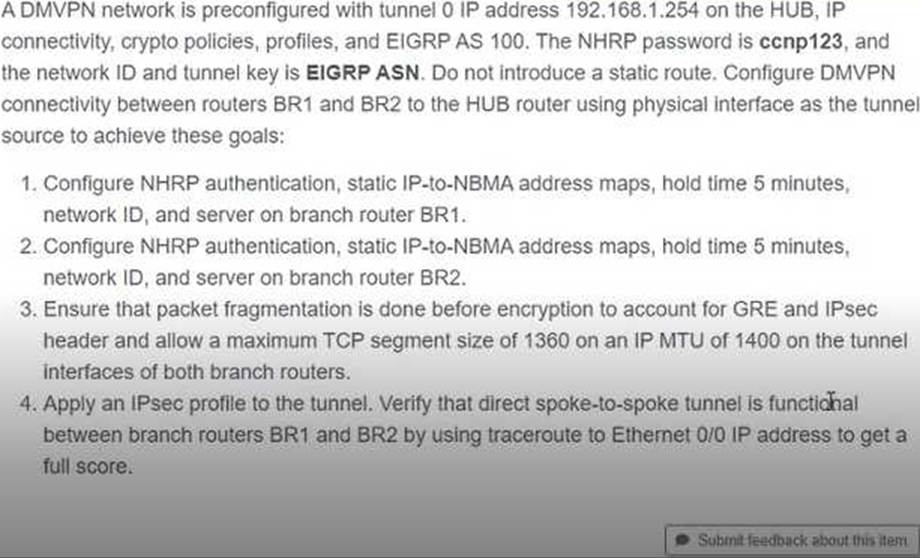
ON BR1
ON BR2
Verification: –
Which feature drops packets if the source address is not found in the snooping table?
- A . IPv6 Source Guard
- B . IPv6 Destination Guard
- C . IPv6 Prefix Guard
- D . Binding Table Recovery
A
Explanation:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/xe-3s/ip6f-xe-3s-book/ip6-snooping.pdf
What is a limitation of IPv6 RA Guard?
- A . It is not supported in hardware when TCAM is programmed
- B . It does not offer protection in environments where IPv6 traffic is tunneled.
- C . It cannot be configured on a switch port interface in the ingress direction
- D . Packets that are dropped by IPv6 RA Guard cannot be spanned
B
Explanation:
Restrictions for IPv6 RA Guard
The IPv6 RA Guard feature does not offer protection in environments where IPv6 traffic is tunneled.
This feature is supported only in hardware when the ternary content addressable memory (TCAM) is programmed.
This feature can be configured on a switch port interface in the ingress direction.
This feature supports host mode and router mode.
This feature is supported only in the ingress direction; it is not supported in the egress direction.
This feature is not supported on EtherChannel and EtherChannel port members.
This feature is not supported on trunk ports with merge mode.
This feature is supported on auxiliary VLANs and private VLANs (PVLANs). In the case of PVLANs, primary VLAN features are inherited and merged with port features.
Packets dropped by the IPv6 RA Guard feature can be spanned.
Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/xe-16-10/ip6f-xe-16-10-book/ip6-ra-guard.html#GUID-589AF00C-7499-439F-AD23-51005D61CAB7
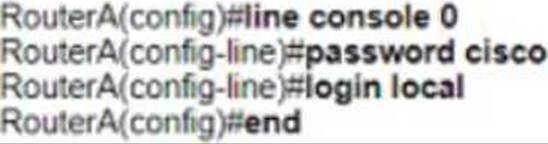
Refer to the exhibit.
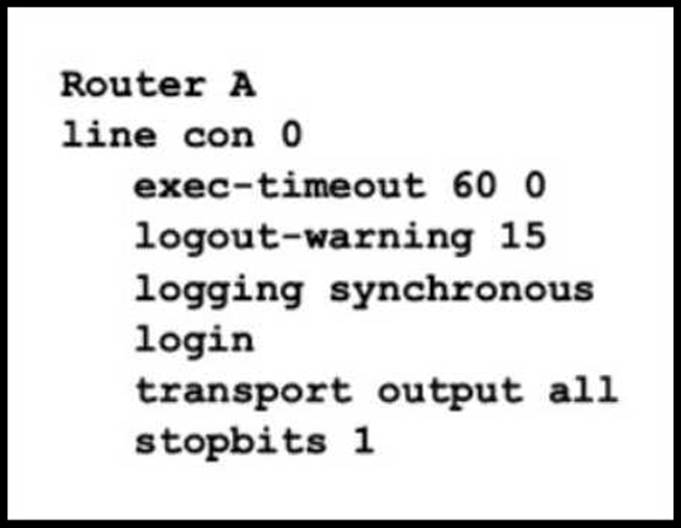
After a misconfiguration by a junior engineer, the console access to router A is not working.
Which configuration allows access to router A?
A)

B)
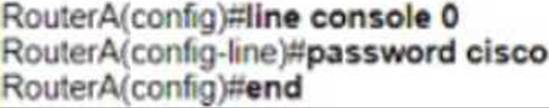
C)
- A . Option A
- B . Option B
- C . Option C
- D . Option D