
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Refer to the exhibit.
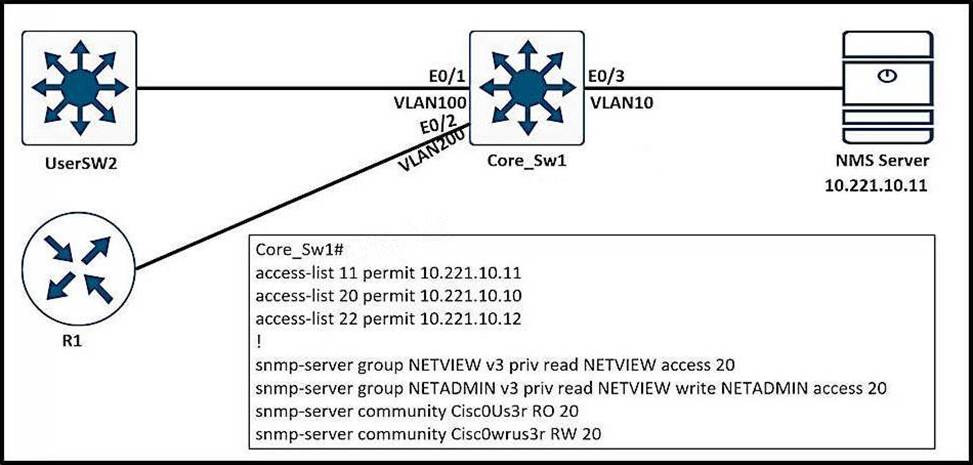
- A . access-list 20 permit 10.221.10.12
- B . snmp-server group NETVIEW v2c priv read NETVIEW access 20
- C . snmp-server group NETADMIN v3 priv read NETVIEW write NETADMIN access 22
- D . access-list 20 permit 10.221.10.11
Refer to the exhibit.
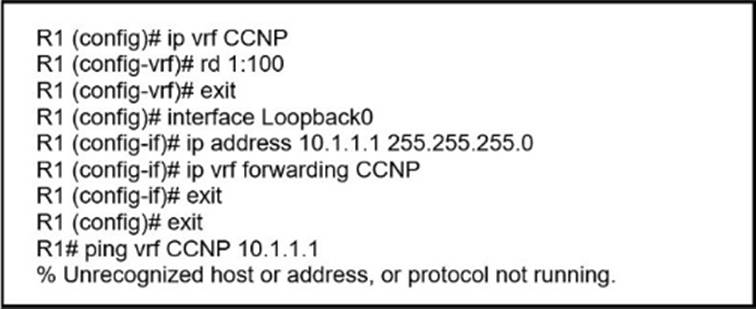
Which command must be configured to make VRF CCNP work?
- A . interface Loopback0
vrf forwarding CCNP - B . interface Loopback0
ip address 10.1.1.1 255.255.255.0 - C . interface Loopback0
ip address 10.1.1.1 255.255.255.0
vrf forwarding CCNP - D . interface Loopback0
ip address 10.1.1.1 255.255.255.0
ip vrf forwarding CCNP
Refer to the exhibit.
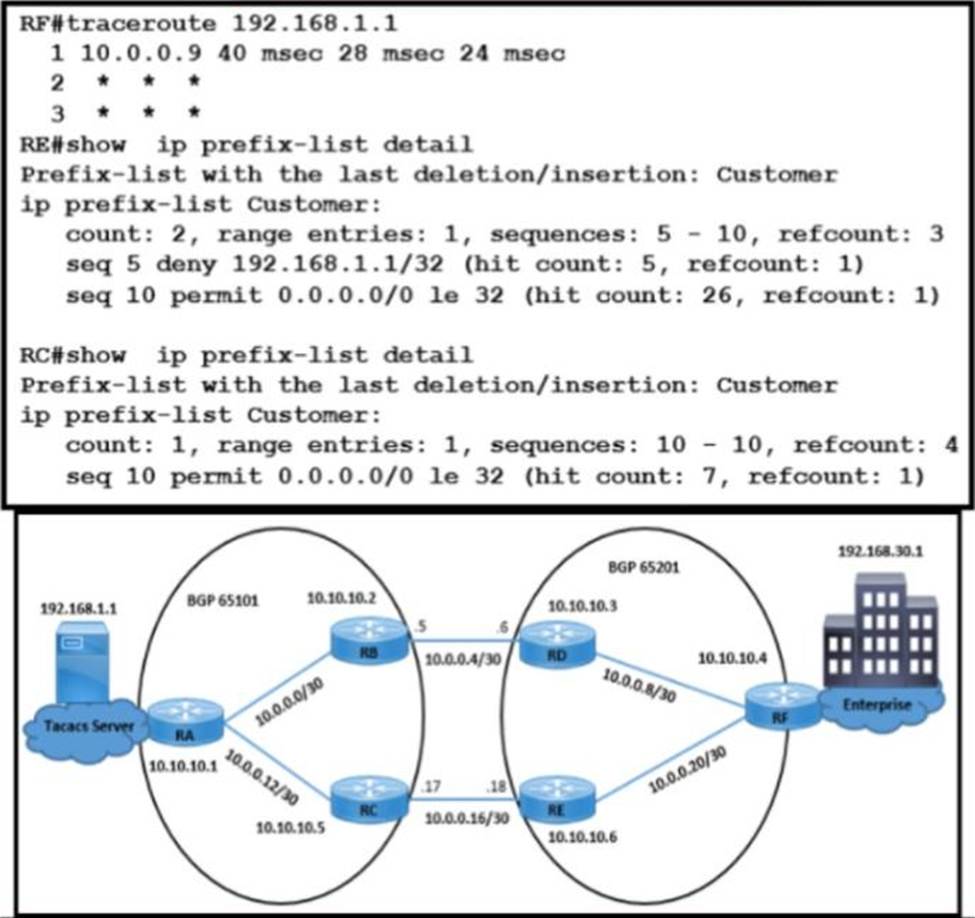
The enterprise users fail to authenticate with the TACACS server when a direct fiber link fails between RB and RD.
The NOC team observes:
✑ Users connected on AS65201 fail to authenticate with TACACS server 192 168 1 1
✑ Users connected on AS65101 successfully authenticate with TACACS server 192 168 1 1
✑ All AS65101 and AS65201 users are configured to authenticate with the TACACS server
Which configuration resolves the issue?
A)

B)

C)

D)

- A . Option A
- B . Option B
- C . Option C
- D . Option D
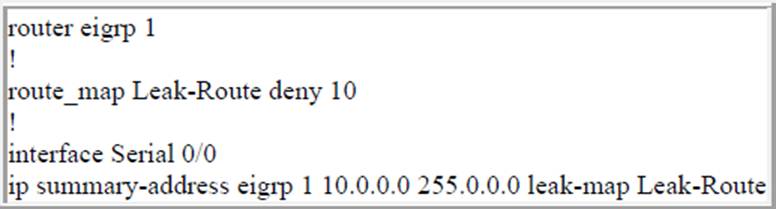
An engineer configured a leak-map command to summarize EIGRP routes and advertise specifically loopback 0 with an IP of 10.1.1.1.255.255.255.252 along with the summary route. After finishing configuration, the customer complained not receiving summary route with specific loopback address.
Which two configurations will fix it? (Choose two.)
- A . Configure access-list 1 permit 10.1.1.0.0.0.0.3.
- B . Configure access-list 1 permit 10.1.1.1.0.0.0.252.
- C . Configure access-list 1 and match under route-map Leak-Route.
- D . Configure route-map Leak-Route permit 10 and match access-list 1.
- E . Configure route-map Leak-Route permit 20.
A,D
Explanation:
When you configure an EIGRP summary route, all networks that fall within the range of your summary are suppressed and no longer advertised on the interface. Only the summary route is advertised. But if we want to advertise a network that has been suppressed along with the summary route then we can use leak-map feature.
The below commands will fix the configuration in this question:
R1(config)#access-list 1 permit 10.1.1.0 0.0.0.3
R1(config)#route-map Leak-Route permit 10 // this command will also remove the “route_map
Leak-Route deny 10” command.
R1(config-route-map)#match ip address 1
DRAG DROP
Drag and drop the MPLS VPN device types from me left onto the definitions on the right.
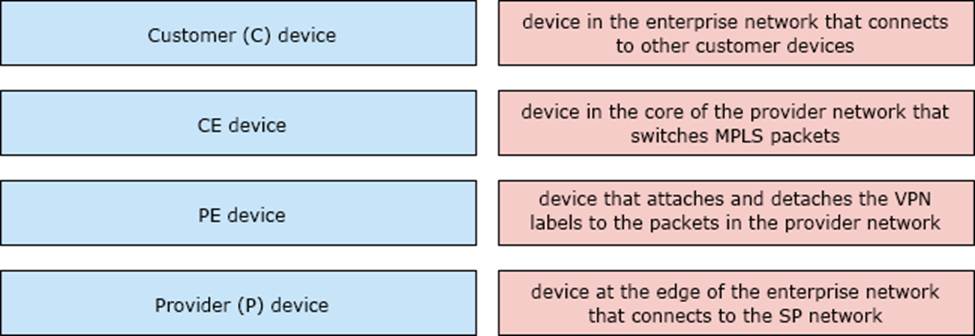
DRAG DROP
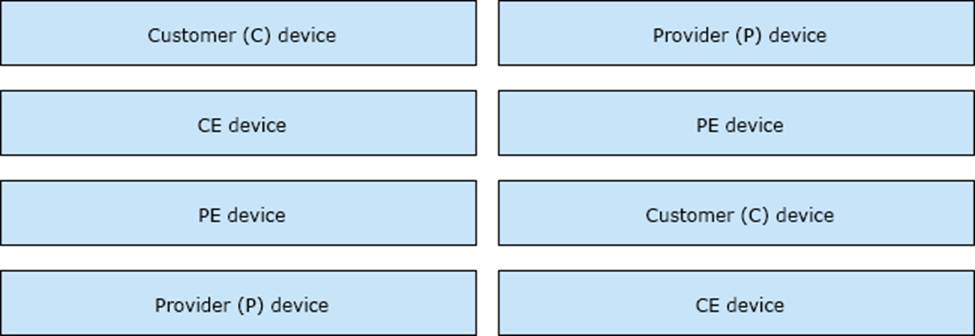
Drag and drop the MPLS VPN device types from me left onto the definitions on the right.
DRAG DROP
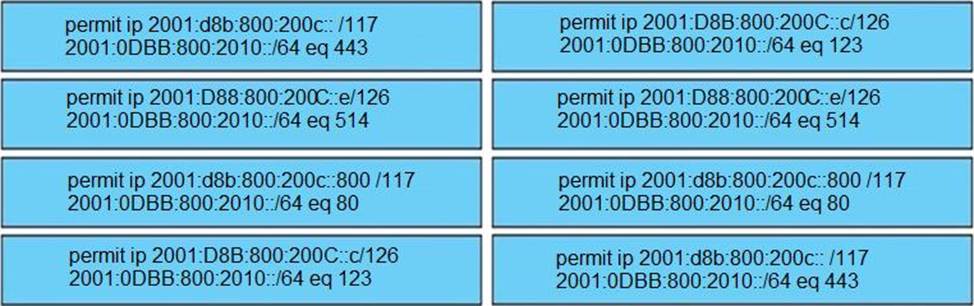
Drag and drop the addresses from the left onto the correct IPv6 filter purposes on the right.
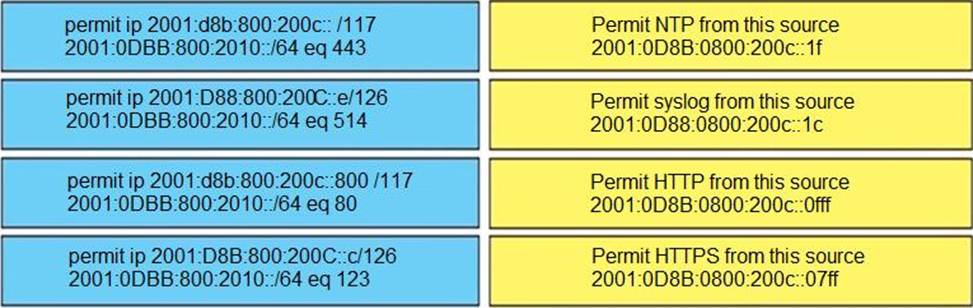
Explanation:
HTTP and HTTPs run on TCP port 80 and 443, respectively and we have to remember them.
Syslog runs on UDP port 514 while NTP runs on UDP port 123 so if we remember them we can find
out the matching answers easily. But maybe there is some typos in this question as
2001:d88:800:200c::c/126 only ranges from 2001:d88:800:200c:0:0:0:c to 2001:d88:800:200c:0:0:0:f
(4 hosts in total). It does not cover host 2001:0D88:0800:200c::1f. Same for
2001:D88:800:200c::e/126, which also ranges from 2001:d88:800:200c:0:0:0:c to
2001:d88:800:200c:0:0:0:f and does not cover host 2001:0D88:0800:200c::1c.
Refer to the exhibit.
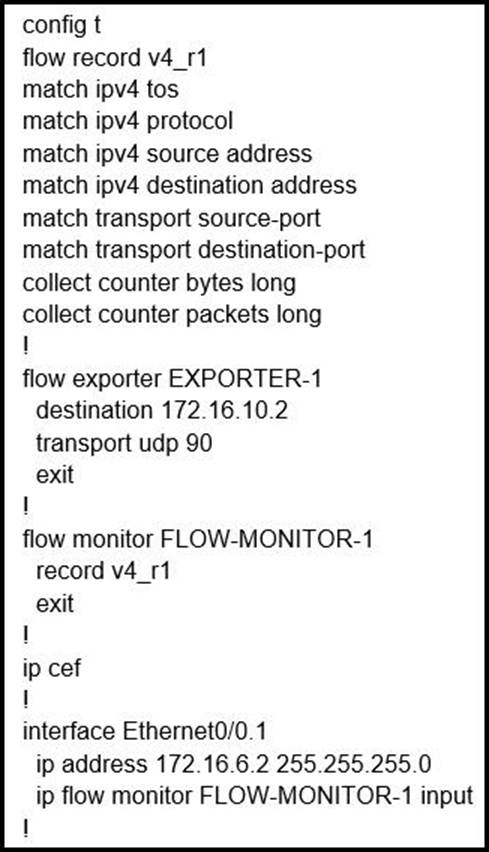
Why is the remote NetFlow server failing to receive the NetFlow data?
- A . The flow exporter is configured but is not used.
- B . The flow monitor is applied in the wrong direction.
- C . The flow monitor is applied to the wrong interface.
- D . The destination of the flow exporter is not reachable.
Refer to the exhibit.
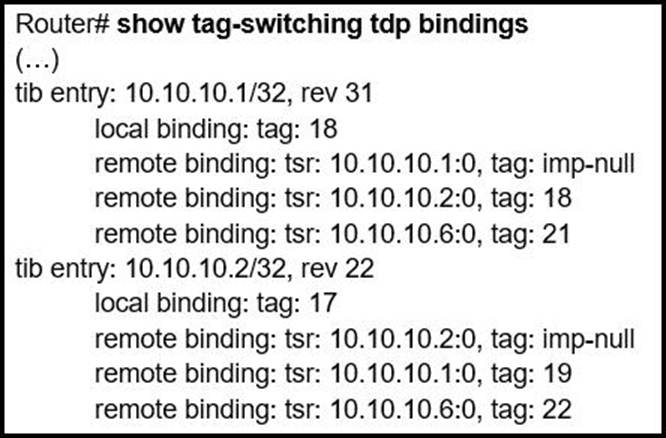
What does the imp-null tag represent in the MPLS VPN cloud?
- A . Pop the label
- B . Impose the label
- C . Include the EXP bit
- D . Exclude the EXP bit
A
Explanation:
The Dimp-null‖ (implicit null) tag instructs the upstream router to pop the tag entry off the tag stack before forwarding the packet.
Note: pop means Dremove the top MPLS label‖
Refer to the exhibit.
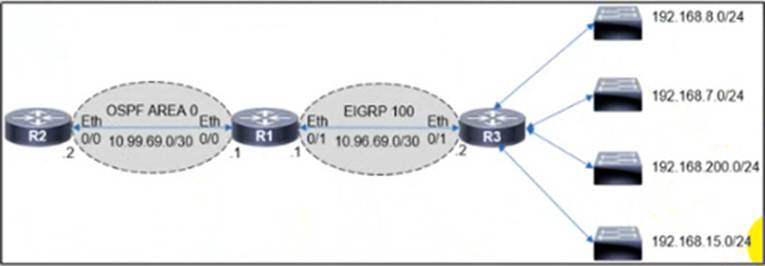
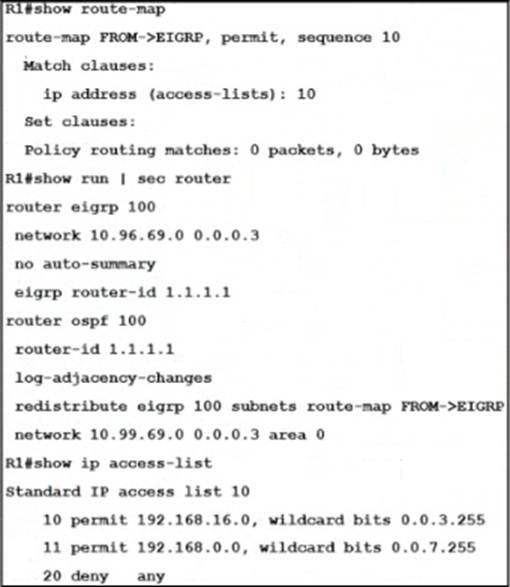
The engineer configured route redistribution in the network but soon received reports that R2 cannot access 192 168 7 0/24 and 192 168 15 0/24 subnets.
Which configuration resolves the issue?
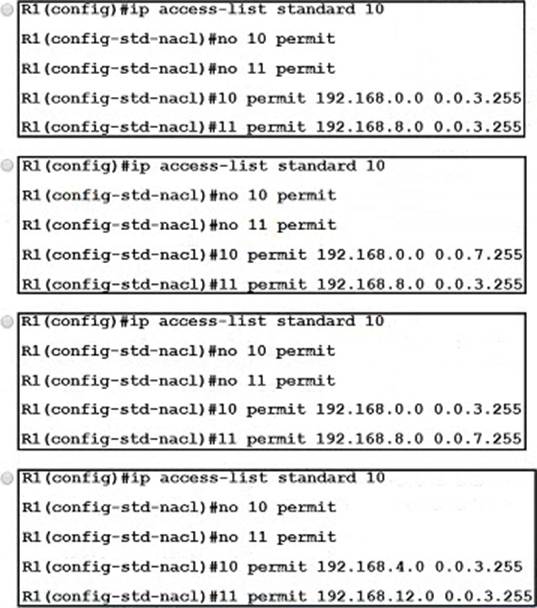
- A . Option A
- B . Option B
- C . Option C
- D . Option D