
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which two components are required for MPLS Layer 3 VPN configuration? (Choose two)
- A . Use pseudowire for Layer 2 routes
- B . Use MP-BGP for customer routes
- C . Use OSPF between PE and CE
- D . Use a unique RD per customer VRF
- E . Use LDP for customer routes
Refer to the exhibit.
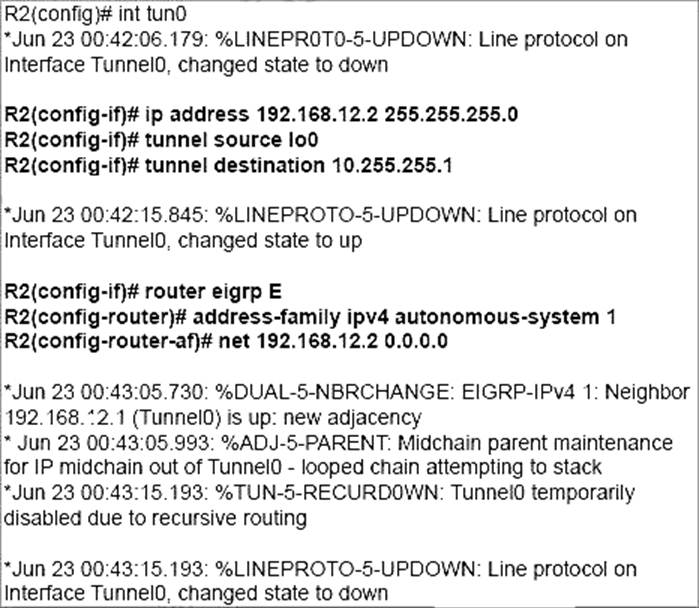
An administrator is configuring a GRE tunnel to establish an EIGRP neighbor to a remote router. The other tunnel endpoint is already configured. After applying the configuration as shown, the tunnel started flapping.
Which action resolves the issue?
- A . Stop sending a route matching the tunnel destination across the tunnel.
- B . Modify the network command to use the Tunne10 Interface netmask.
- C . Advertise the Loopback0 interface from R2 across the tunnel.
- D . Readdress the IP network on the Tunne10 on both routers using the /31 netmask.
Refer to the exhibit.
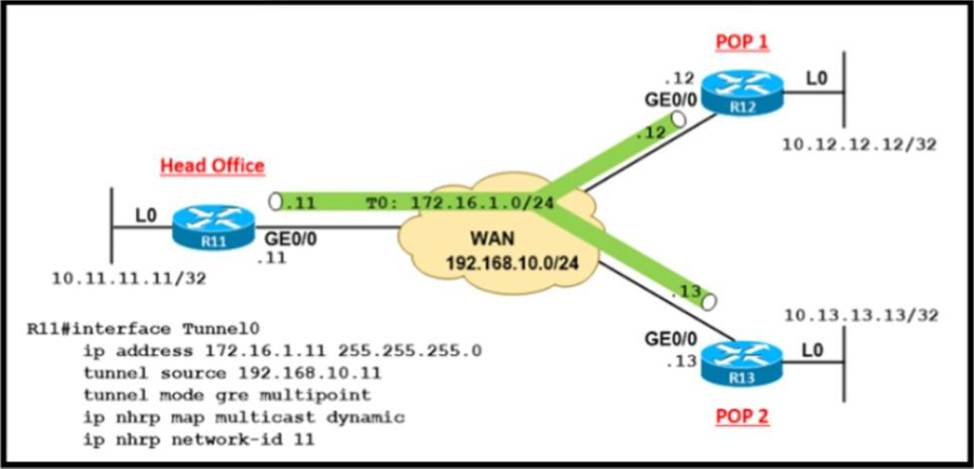
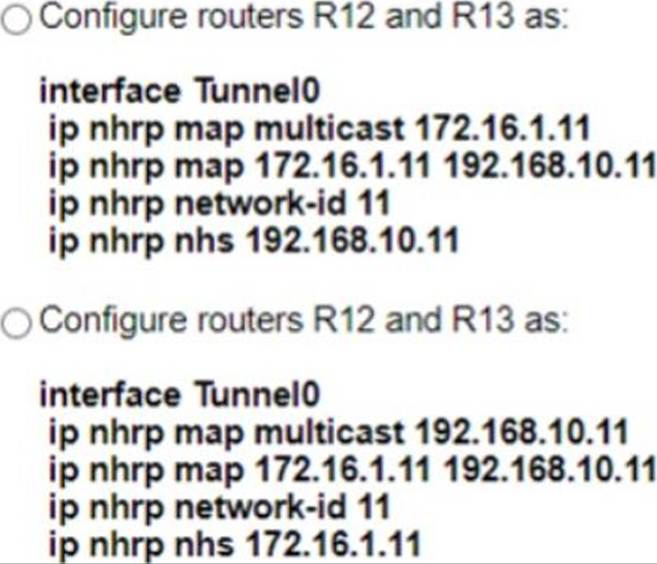
A company builds WAN infrastructure between the head office and POPs using DMVPN hub-and-spoke topology to provide end-to-end communication All POPs must maintain point-to-point connectivity with the head office.
Which configuration meets the requirement at routers R12 and R13?
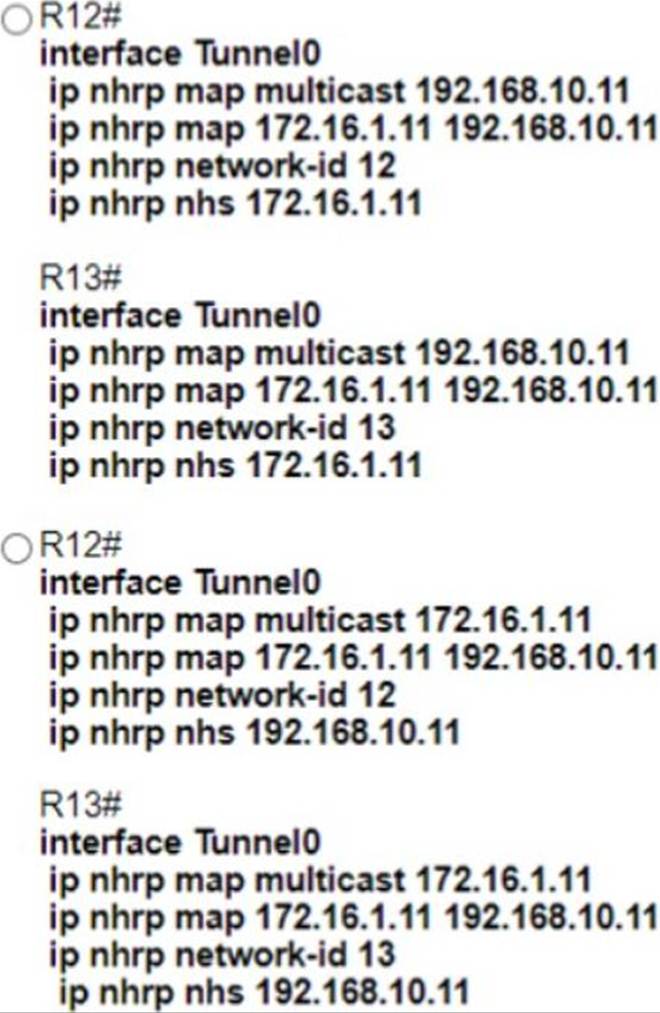
- A . Option A
- B . Option B
- C . Option C
- D . Option D
Refer to the exhibit.
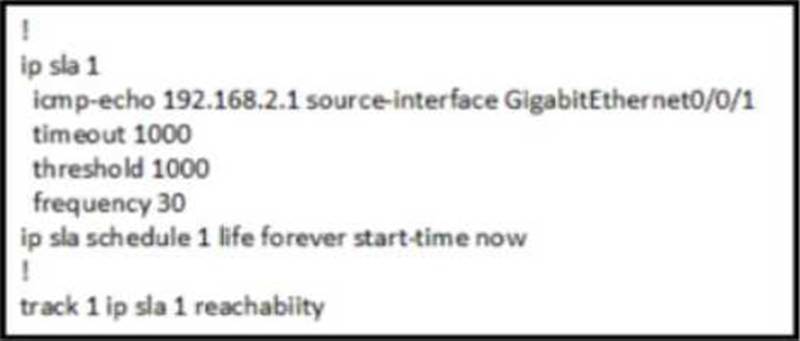
An engineer observes that every time the ICMP packet is lost at a polling interval, track 1 goes down, which causes unnecessary disruption and instability in the network. The engineer does not want the traffic to be rerouted if the loss of ICMP packets is negligible. If the packet loss is persistent for a longer duration, the track must go down and the traffic must be rerouted.
Which action resolves the issue?
- A . Change the IP SLA schedule to run only at certain intervals.
- B . Increase the threshold value from 1000 to 1500.
- C . Increase the timeout value from 1000 to 1500
- D . Define a delay timer under track 1.
What is an advantage of using BFD?
- A . It detects local link failure at layer 1 and updates routing table.
- B . It detects local link failure at layer 2 and updates routing protocols.
- C . It has sub-second failure detection for layer 1 and layer 3 problems.
- D . It has sub-second failure detection for layer 1 and layer 2 problems.
Refer to the exhibit.
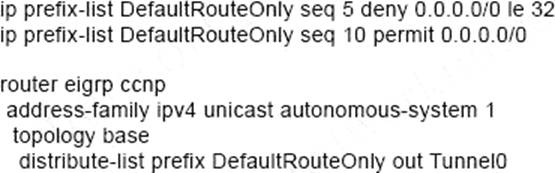
The administrator configured route advertisement to a remote low resources router to use only the default route to reach any network but failed.
Which action resolves this issue?
- A . Change the direction of the distribute-list command from out to in.
- B . Remove the line with the sequence number 5 from the prefix list.
- C . Remove the prefix keyword from the distribute-list command.
- D . Remove the line with the sequence number 10 from the prefix list.
Refer to the exhibit.
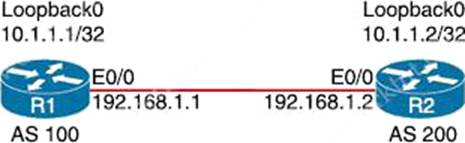
The R1 and R2 configurations are:
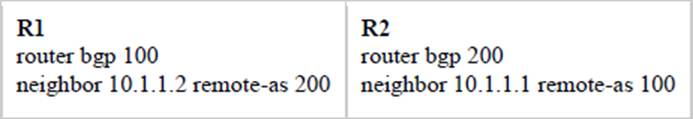
The neighbor is not coming up.
Which two sets of configurations bring the neighbors up? (Choose two.)
- A . R2
ip route 10.1.1.1 255.255.255.255 192.168.1.1
!
router bgp 200
neighbor 10.1.1.1 tti-security hops 1
neighbor 10.1.1.1 update-source loopback 0 - B . R2
ip route 10.1.1.1 255.255.255.255 192.168.1.1
!
router bgp 200
neighbor 10.1.1.1 disable-connected-check
neighbor 10.1.1.1 update-source loopback 0 - C . R2
ip route 10.1.1.2 255.255.255.255 192.168.1.2
!
router bgp 100
neighbor 10.1.1.2 ttl-security hops 1
neighbor 10.1.1.2 update-source loopback 0 - D . R1
ip route 10.1.1.2 255.255.255.255 192.168.1.2
!
router bgp 100
neighbor 10.1.1.1 ttl-security hops 1
neighbor 10.1.1.2 update-source loopback 0 - E . R1
ip route 10.1.1.2 255.255.255.255 192.168.1.2
!
router bgp 100
neighbor 10.1.1.2 disable-connected-check
neighbor 10.1.1.2 update-source Loopback0
B,E
Explanation:

Disable-connected-check enables a directly connected eBGP neighbor to peer using a loopback address without adjusting the default TTL of 1. In disable connected check the router does not decrease the TTL of an IP packet that is destined to itself so it only counts or considers as one hop between the two loopbacks of the routers.
An engineer configured a company’s multiple area OSPF head office router and Site A cisco routers with VRF lite.
Each site router is connected to a PE router of an MPLS backbone.
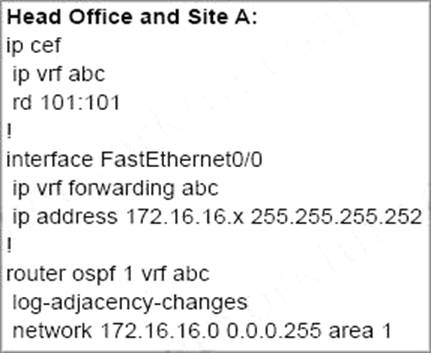
After finishing both site router configurations, none of the LSA 3,4 5, and 7 are installed at Site A router.
Which configuration resolves this issue?
- A . configure capability vrf-lite on Site A and its connected PE router under router ospf 1 vrf abc
- B . configure capability vrf-lite on Head Office and its connected PE router under router ospf 1 vrf abc
- C . configure capability vrf-lite on both PE routers connected to Head Office and Site A routers under routtr ospf 1 vrf abc
- D . configure capability vrf-lite on Head Office and Site A routers under router ospf 1 vrf abc
Refer to the exhibit.
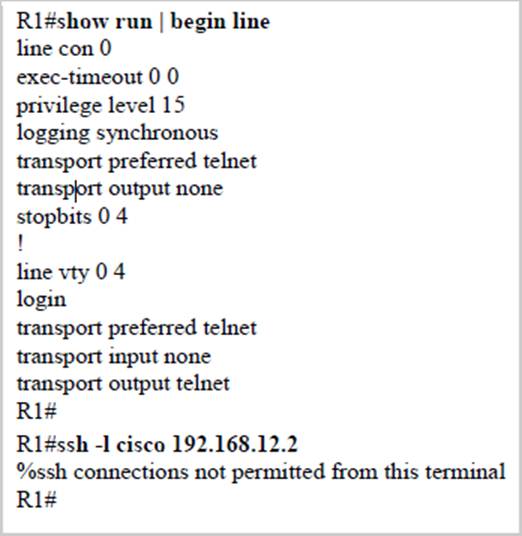
An engineer receives this error message when trying to access another router in-band from the serial interface connected to the console of R1.
Which configuration is needed on R1 to resolve this issue?
Option A
R1(config)#line console 0
R1(config-line)#transport preferred ssh
Option B
R1(config)#line vty 0
R1(config-line)#transport output ssh
Option C
R1(config)#line vty 0
R1(config-line)#transport output ssh
R1(config-line)#transport preferred ssh
Option D
R1(config)#line console 0
R1(config-line)#transport output ssh
- A . Option A
- B . Option B
- C . Option C
- D . Option D
D
Explanation:
https://community.cisco.com/t5/other-network-architecture/out-of-band-router-access/td-p/333295
The “transport output none” command prevents any protocol connection made from R1. Therefore our SSH connection to 192.168.12.2 was refused. In order to fix this problem we can configure “transport output ssh” under “line console 0” of R1.
Note: The parameter “-l” specifies the username to log in as on the remote machine.
Refer to the exhibit.
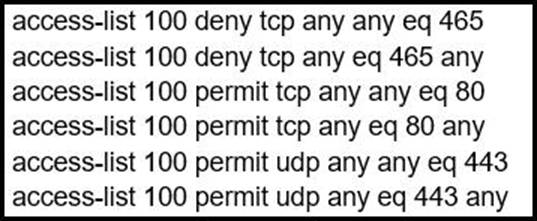
During troubleshooting it was discovered that the device is not reachable using a secure web browser.
What is needed to fix the problem?
- A . permit tcp port 443
- B . permit udp port 465
- C . permit tcp port 465
- D . permit tcp port 22