
Cisco 300-410 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
An engineer configured a DHCP server for Cisco IP phones to download its configuration from a TFTP server, but the IP phones failed to toad the configuration.
What must be configured to resolve the issue?
- A . BOOTP port 67
- B . DHCP option 66
- C . BOOTP port 68
- D . DHCP option 69
B
Explanation:
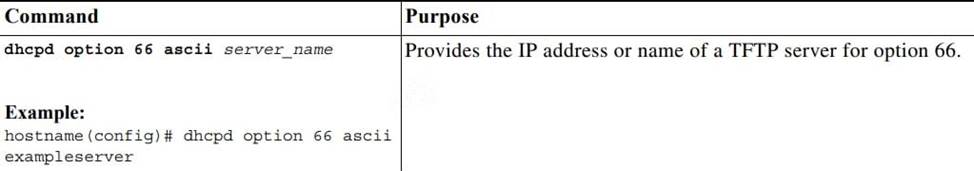
DHCP options 3, 66, and 150 are used to configure Cisco IP Phones. Cisco IP Phones download their configuration from a TFTP server. When a Cisco IP Phone starts, ifit does not have both the IP address and TFTP server IP address preconfigured, it sends a request with option 150 or 66 to the DHCP server to obtain this information.
+ DHCP option 150 provides the IP addresses of a list of TFTP servers.
+ DHCP option 66 gives the IP address or the hostname of a single TFTP server.
Reference: http://www.cisco.com/c/en/us/td/docs/security/asa/asa84/configuration/guide/asa_84_cli_config/basic_dhcp.pdf
What is a characteristic of Layer 3 MPLS VPNs?
- A . LSP signaling requires the use of unnumbered IP links for traffic engineering.
- B . Traffic engineering supports multiple IGP instances
- C . Traffic engineering capabilities provide QoS and SLAs.
- D . Authentication is performed by using digital certificates or preshared keys.
C
Explanation:
Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/mp_te_diffserv/configuration/15-mt/mp-te-diffserv-15-mt-book/mp-te-diffserv-aw.html
MPLS traffic engineering supports only a single IGP process/instance
The MPLS traffic engineering feature does not support routing and signaling of LSPs over unnumbered IP links.
Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/mp_te_path_setup/configuration/xe-3s/mp-te-path-setup-xe-3s-book/mp-te-enhance-xe.html
During the maintenance window an administrator accidentally deleted the Telnet-related configuration that permits a Telnet connection from the inside network (Eth0/0) to the outside of the networking between Friday C Sunday night hours only.
Which configuration resolves the issue?
- A . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit udp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday 22:00 to 05:00 - B . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit tcp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic 22:00 to 05:00 - C . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit tcp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday 22:00 to 05:00 - D . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit udp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday
During the maintenance window an administrator accidentally deleted the Telnet-related configuration that permits a Telnet connection from the inside network (Eth0/0) to the outside of the networking between Friday C Sunday night hours only.
Which configuration resolves the issue?
- A . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit udp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday 22:00 to 05:00 - B . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit tcp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic 22:00 to 05:00 - C . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit tcp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday 22:00 to 05:00 - D . interface Ethernet0/0
ip address 10.1.1.1 255.255.255.0
ip access-group 101 in
!
access-list 101 permit udp 10.1.1.0 0.0.0.255 172.16.1.0 0.0.0.255
eq telnet time-range change window
!
time-range change window
periodic Friday Saturday Sunday
What is a MPLS PHP label operation?
- A . Downstream node signals to remove the label.
- B . It improves P router performance by not performing multiple label lookup.
- C . It uses implicit-NULL for traffic congestion from source to destination forwarding
- D . PE removes the outer label before sending to the P router.
A DMVPN single hub topology is using IPsec + mGRE with OSPF.
What should be configured on the hub to ensure it will be the designated router?
- A . tunnel interface of the hub with ip nhrp ospf dr
- B . OSPF priority to 0
- C . route map to set the metrics of learned routes to 110
- D . OSPF priority greater than 1
D
Explanation:
By default, the priority is 1 on all routers so we can set the OSPF priority of the hub to a value which is greater than 1 to make sure it would become the DR.
An engineer must configure a Cisco router to initiate secure connections from the router to other devices in the network but kept failing.
Which two actions resolve the issue? (Choose two.)
- A . Configure a source port for the SSH connection to initiate
- B . Configure a TACACS+ server and enable it
- C . Configure transport input ssh command on the console
- D . Configure a domain name
- E . Configure a crypto key to be generated
D,E
Explanation:
Follow these guidelines when configuring the switch as an SSH server or SSH client:
+ An RSA key pair generated by a SSHv1 server can be used by an SSHv2 server, and the reverse.
+ If the SSH server is running on a stack master and the stack master fails, the new stack master uses the RSA key pair generated by the previous stack master
+ If you get CLI error messages after entering the crypto key generate rsa global configuration command, an RSA key pair has not been generated. Reconfigure the hostname and domain, and then enter the crypto key generate rsa command.
+ When generating the RSA key pair, the message No host name specified might appear. If it does, you must configure a hostname by using the hostname global configuration command.
+ When generating the RSA key pair, the message No domain specified might appear. If it does, you must configure an IP domain name by using the ip domain-nameglobal configuration command.
+ When configuring the local authentication and authorization authentication method, make sure that AAA is disabled on the console.
Reference: https://www.cisco.com/en/US/docs/switches/lan/catalyst3850/software/release/3.2_0_se/multibook/configuration_guide/b_consolidated_config_guide_3850_chapter_01100
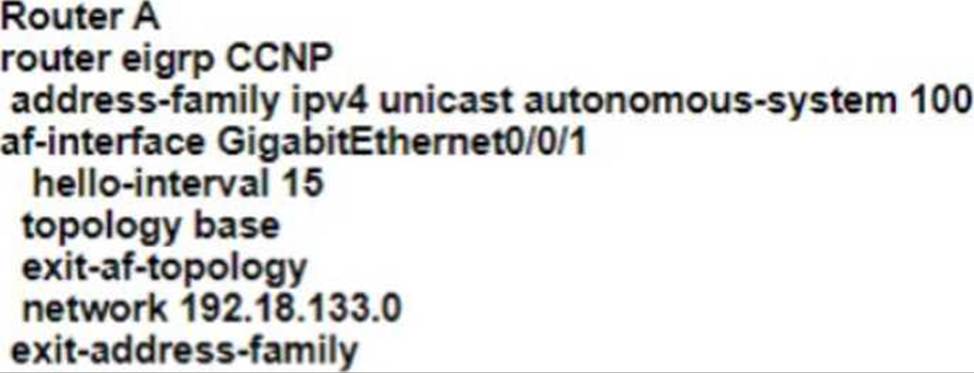
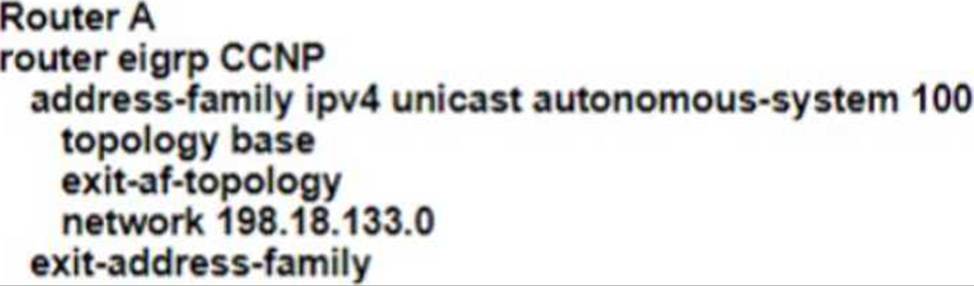
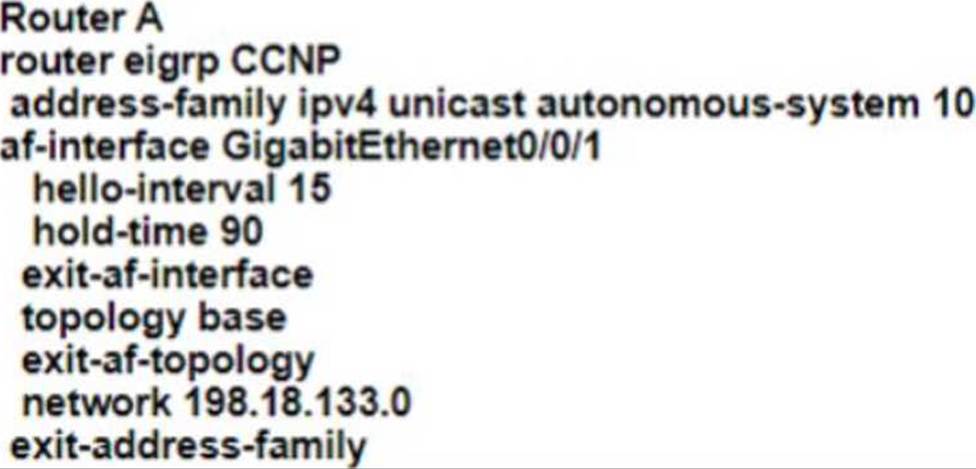
Refer to the exhibit.
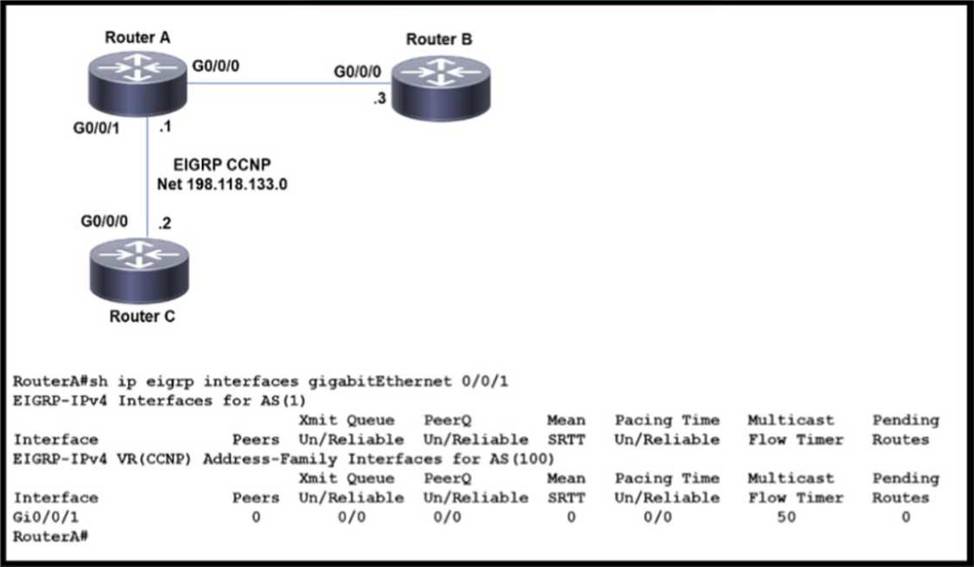
EIGRP adjacency between router A and router C is not working as expected.
Which two configurations resolve the issue? (Choose two)
A)
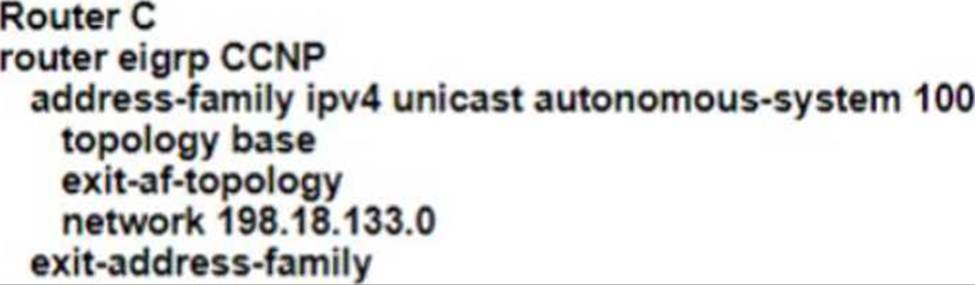
B)
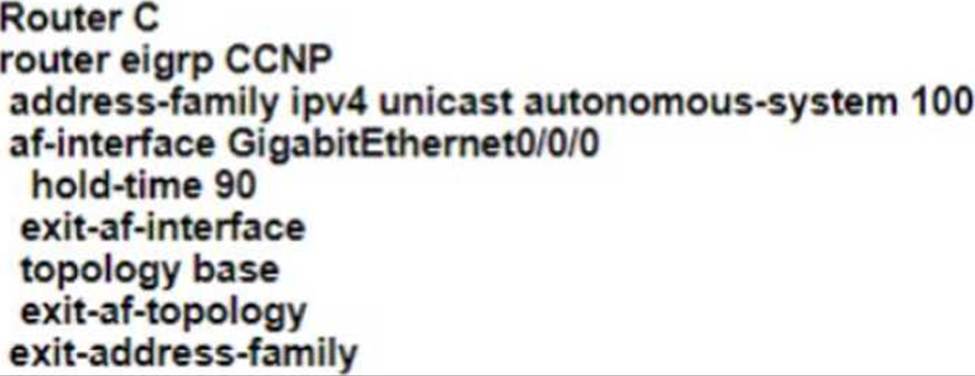
C)
D)
E)
- A . Option A
- B . Option B
- C . Option C
- D . Option D
- E . Option E
Refer to the exhibit.

The network administrator must mutually redistribute routes at the Chicago router to the LA and NewYork routers.
The configuration of the Chicago router is this:
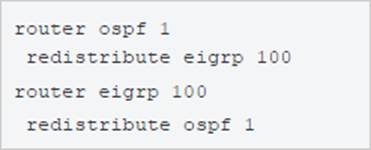
After the configuration, the LA router receives all the NewYork routes, but NewYork router does not receive any LA routes.
Which set of configurations fixes the problem on the Chicago router?
- A . router ospf 1
redistribute eigrp 100 metric 20 - B . router eigrp 100
redistribute ospf 1 metric 10 10 10 10 10 - C . router eigrp 100
redistribute ospf 1 subnets - D . router ospf 1
redistribute eigrp 100 subnets
B
Explanation:
“LA router receives all the NewYork routes but it does not receive any LA routes” because when redistrubuting into EIGRP, we must configure the default metric.
Refer to the exhibit.
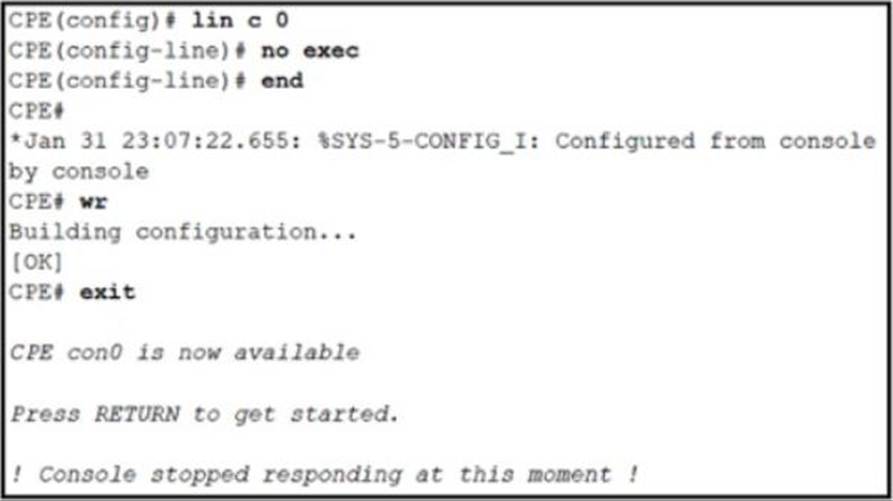
An administrator is attempting to disable the automatic logout after a period of inactivity. After logging out the console stopped responding to all keyword inputs.
Remote access through SSH still work resolves the issue?
- A . Configure the exec command on line con 0.
- B . Configure the absolute-timeout command on line con 0.
- C . Configure the default exec-timeout command on line con 0.
- D . Configure the no exec-timeout command on line con 0.