
Cisco 300-410 Practice Exams
Last updated on Oct 01,2026- Exam Code: 300-410
- Exam Name: Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- Certification Provider: Cisco
- Latest update: Oct 01,2026
Which configuration feature should be used to block rogue router advertisements instead of using the IPv6 Router Advertisement Guard feature?
- A . VACL blocking broadcast frames from nonauthorized hosts
- B . PVLANs with promiscuous ports associated to route advertisements and isolated ports for nodes
- C . PVLANs with community ports associated to route advertisements and isolated ports for nodes
- D . IPv4 ACL blocking route advertisements from nonauthorized hosts
B
Explanation:
The IPv6 Router Advertisement Guard feature provides support for allowing the network administrator to block or reject unwanted or rogue router advertisement guard messages that arrive at the network device platform. Router Advertisements are used by devices to announce themselves on the link. The IPv6 Router Advertisement Guard feature analyzes these router advertisements and filters out router advertisements that are sent by unauthorized devices.
Certain switch platforms can already implement some level of rogue RA filtering by the administrator configuring Access Control Lists (ACLs) that block RA ICMP messages that might be inbound on “user” ports.
Reference: https://datatracker.ietf.org/doc/html/rfc6104
DRAG DROP
Drag and drop the MPLS VPN device types from the left onto the definitions on the right.
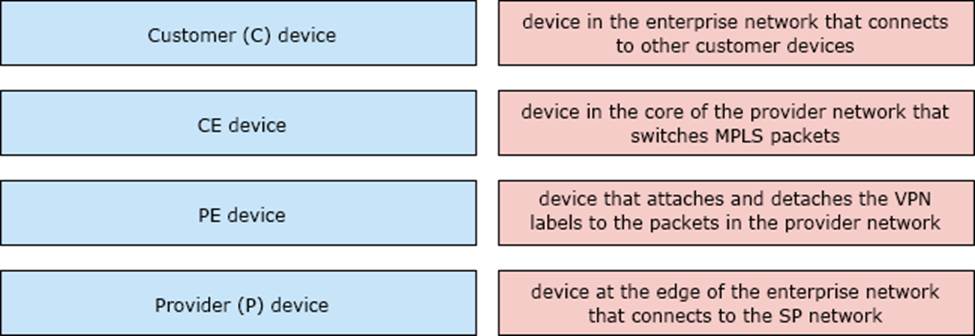
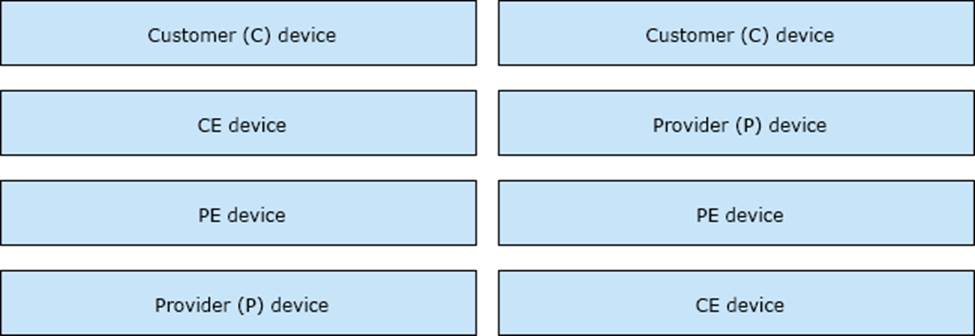
Explanation:
Graphical user interface,
application Description automatically generated
Refer to the exhibit.
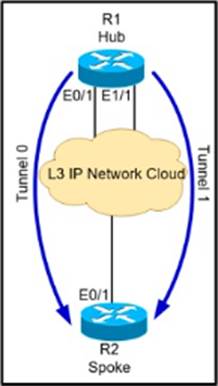
The hub and spoke are connected via two DMVPN tunnel interfaces The NHRP is configured and the tunnels are detected on the hub and the spoke.
Which configuration command adds an IPsec profile on both tunnel interfaces to encrypt traffic?
- A . tunnel protection ipsec profile DMVPN multipoint
- B . tunnel protection ipsec profile DMVPN tunnel1
- C . tunnel protection ipsec profile DMVPN shared
- D . tunnel protection ipsec profile DMVPN unique
Refer to the exhibit.
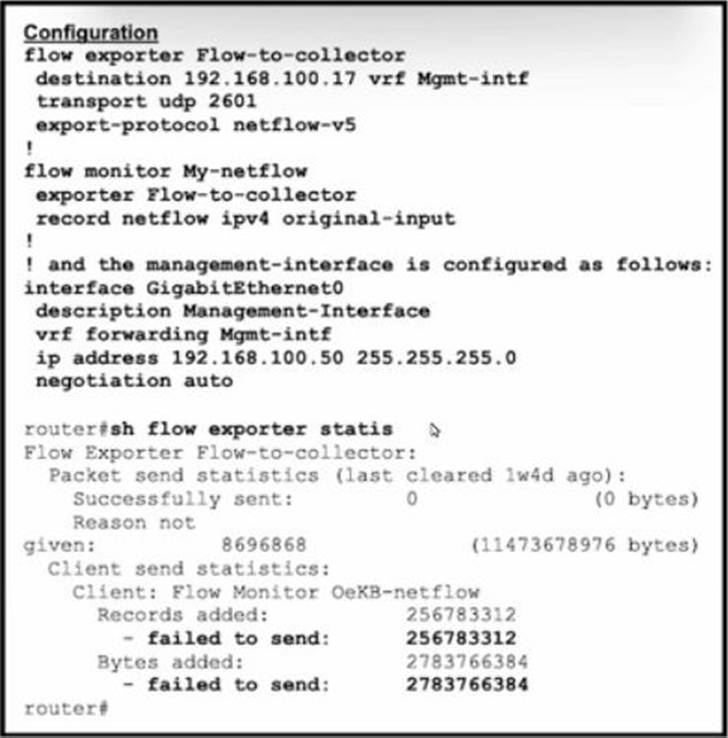
A network administrator configured NetFlow data, but the data is not visible at the NetFlow collector.
Which configuration allows the router to send the records?
- A . Configure the management interface in the global routing table to send the records.
- B . Configure a different interface to send the records.
- C . Configure the NetFlow collector to listen at export-protocol netflow-v5.
- D . Rectify NetFlow collector reachability from the management interface.
Refer to the exhibit.
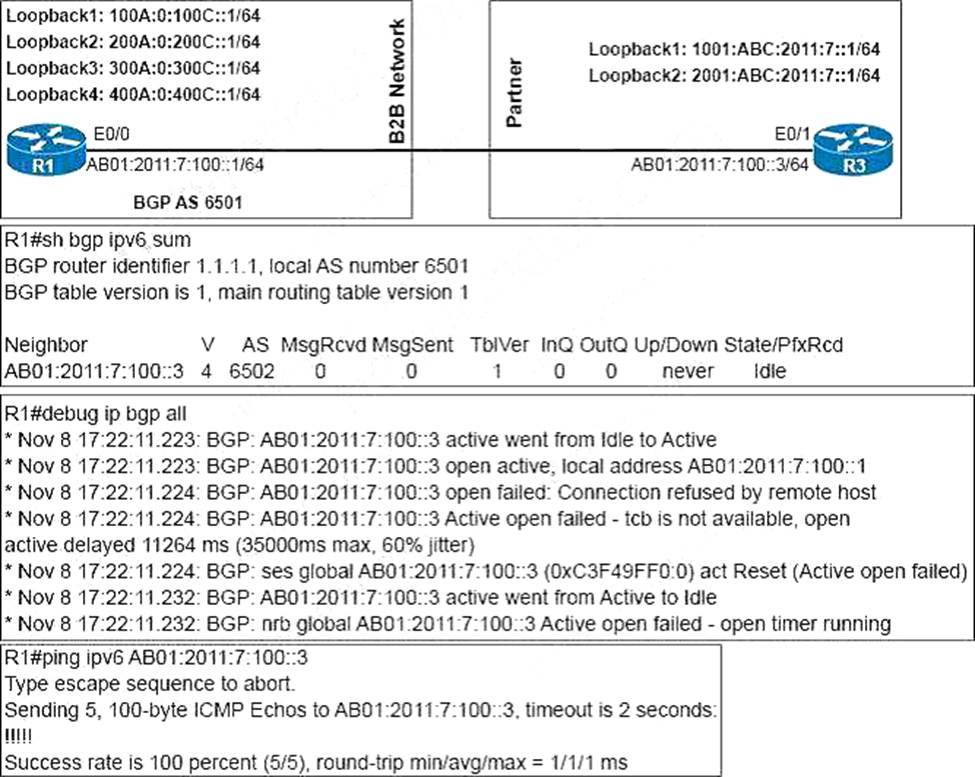
An engineer configured BGP between routers R1 and R3 The BOP peers cannot establish neighbor adjacency to be able to exchange routes.
Which configuration resolves this issue?
- A . R3router bgp 6502address-family ipv6neighbor AB01:2011:7:100::1 activate
- B . R1router bgp 6501address-family ipv6neighbor AB01:2011:7:100;:3 activate
- C . R3router bgp 6502neighbor AB01:2011:7:100::1 ebgp-muttlhop 255
- D . R1router bgp 6501 neighborAB01:2011:7:100::3ebgp-multihop255
A
Explanation:
From the output, we learned that R1 was trying to establish BGP neighbor relationship with R3 but failed. Both of them were using physical interface to establish neighbor relationship so we don’t need the “… ebgp-multihop” command here. The only reasonable answer is R3 has not been configured to activate BGP neighbor relationship with R1.
Which statement about IPv6 RA Guard is true?
- A . It does not offer protection in environments where IPv6 traffic is tunneled.
- B . It cannot be configured on a switch port interface in the ingress direction.
- C . Packets that are dropped by IPv6 RA Guard cannot be spanned.
- D . It is not supported in hardware when TCAM is programmed.
A
Explanation:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/xe-3s/ip6f-xe-3s-book/ip6-ra-guard.html#GUID-589AF00C-7499-439F-AD23-51005D61CAB7
The IPv6 RA Guard feature does not offer protection in environments where IPv6 traffic is tunneled.
Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/xe-16/ip6f-xe-16-book/ip6-ra-guard.pdf
Refer to the exhibit.
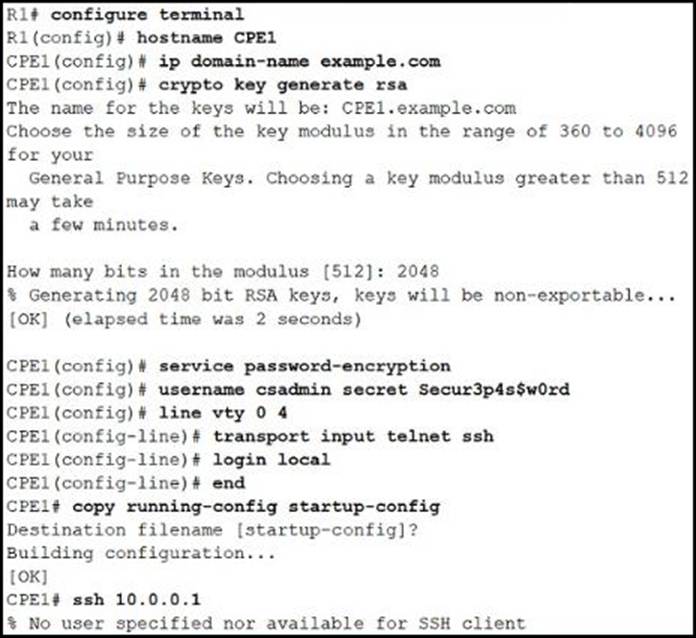
An administrator must harden a router, but the administrator failed to test the SSH access successfully to the router.
Which action resolves the issue?
- A . Configure SSH on the remote device to log m using SSH
- B . SSH syntax must be ssh -I user ip to log in to the remote device
- C . Configure enable secret to log in to the device
- D . SSH must be allowed with the transport output ssh command
Refer to the exhibit.
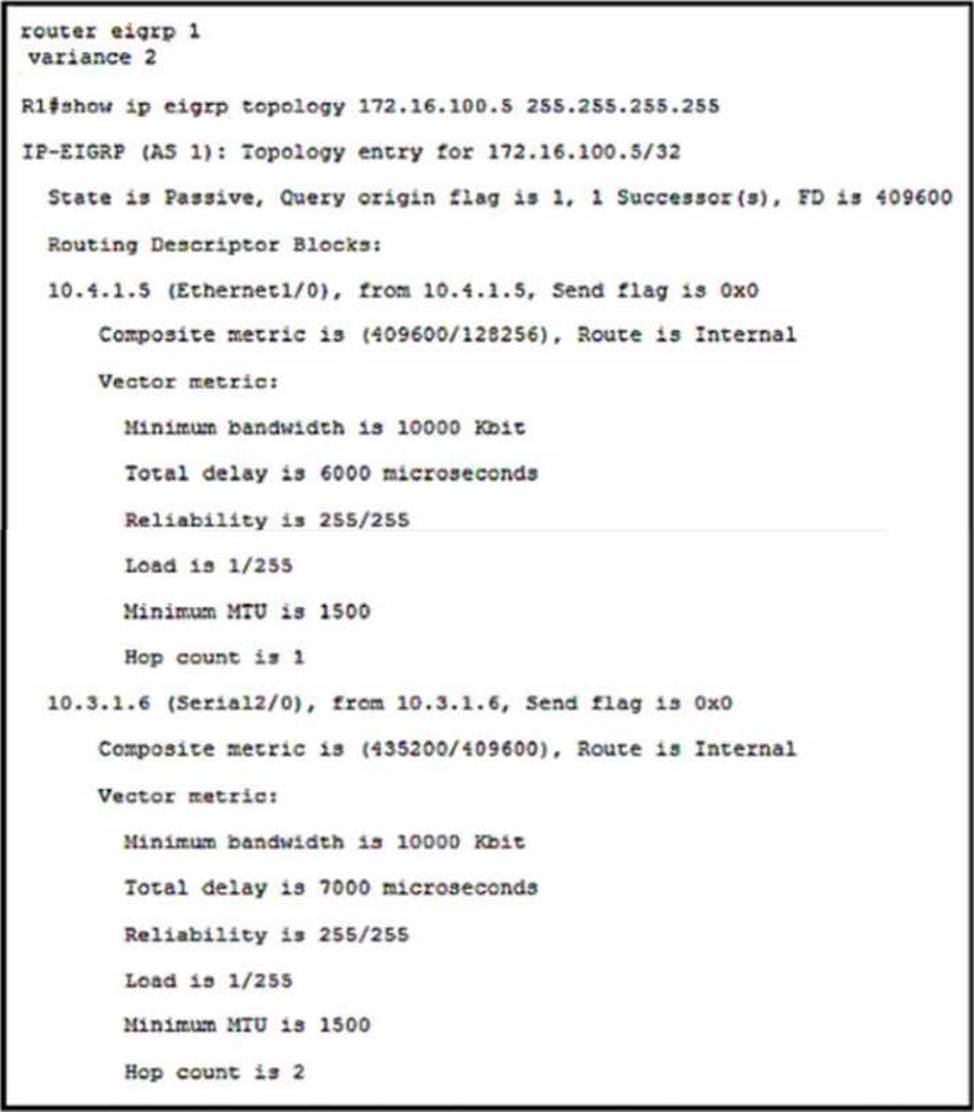
A network engineer troubleshooting a packet drop problem for the host 172.16.100.5 notices that only one link is used and installed on the routing table, which saturates the bandwidth.
Which action must the engineer take to resolve the high bandwidth utilization problem and share the traffic toward this host between the two available links?
- A . Set the eigrp variance equal to 4 to install a second route with a metric not larger than 4 times of the best metric.
- B . Change the EIGRP delay metric to meet the feasibility condition.
- C . Set the eigrp variance equal to 3 to install a second route with a metric not larger than 3 times of the best metric.
- D . Disable the eigrp split horizon loop protection mechanism.
Refer to the exhibit.
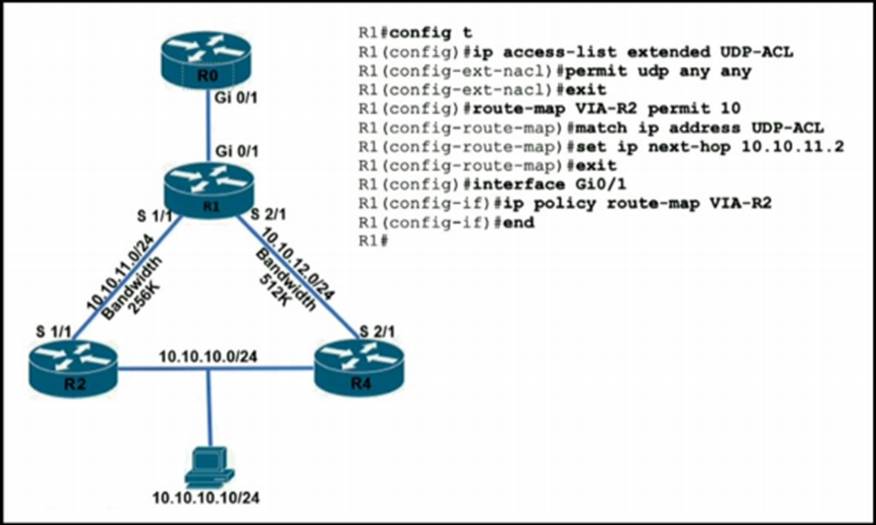
TCP traffic should be reaching host 10.10.10.10/24 via R2.
Which action resolves the issue?
- A . TCP traffic will reach the destination via R2 without any changes
- B . Add a permit 20 statement in the route map to allow TCP traffic
- C . Allow TCP in the access list with no changes to the route map
- D . Set IP next-hop to 10.10.12.2 under the route-map permit 10 to allow TCP traffic.
Refer to the exhibit.
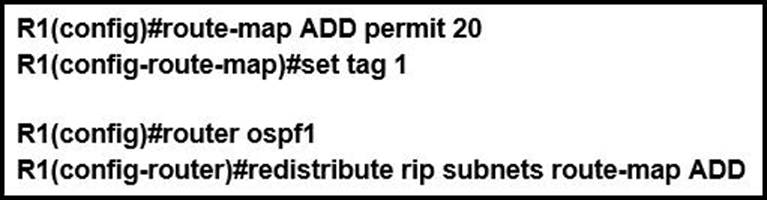
Which statement about R1 is true?
- A . OSPF redistributes RIP routes only if they have a tag of one.
- B . RIP learned routes are distributed to OSPF with a tag value of one.
- C . R1 adds one to the metric for RIP learned routes before redistributing to OSPF.
- D . RIP routes are redistributed to OSPF without any changes.